






Each time an application extracts weather data, displays a map, processes a payment, there is a quiet handshake going on in the background. This handshake often involves a small string of characters that confirms that the request is legit. This is precisely where the overall concept of an API key proves to be crucial. Understanding it fully is crucial for anyone who is working with today’s web applications. So, this blog is relevant to you irrespective of whether you are a website owner, a developer, or just curious about how software communicates to other software.
In this detailed guide, let us break down what is actually an API key, how it operates, why it is important, and how it compares to other methods of authentication.
It is a combination of unique letters and numbers, which the service provider issues to recognize a user or application making a request to API (Application Programming Interface). You can consider it as a digital ID card. When a single program wishes to interact with another, it provides this key as an authorization proof.
An API key generally appears like a random and long string. For instance, something like AIzaSyD4rTk9X8L2vN0p. It is created by the API provider and associated with a particular project or account, which essentially means that the provider can always find the source of the request.
A few key traits of an API key are as follows:
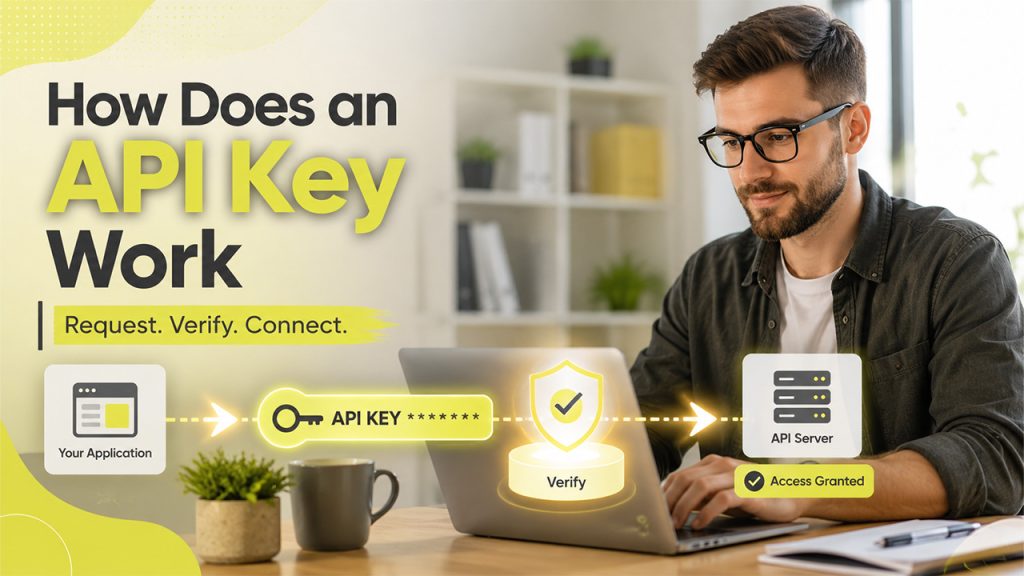
The working of the API key is extremely simple, and everything gets completed in milliseconds. Let us look at the general flow:
This system enables organizations to monitor usage, apply rate limits, and avoid unauthorized access, all without needing a complete login process for each single request. For website owners handling WordPress websites, this same logic is applied when you are connecting to third-party services such as Google Analytics, where a tracking code or generated key verifies the connection between your external platform and the website.
An API key is not just a technical obligation. It plays a crucial role in how services remain efficient, secure, and accountable. Here is why they are important:
Having said that, an API key alone is not a comprehensive security solution. Since it is basically a static string, it can get exposed if carelessly shared or embedded in source code. This is why so many developers combine API keys with additional protection layers, which is similar to how securing a WordPress site pertains to integrating numerous safeguards instead of depending on a single measure.
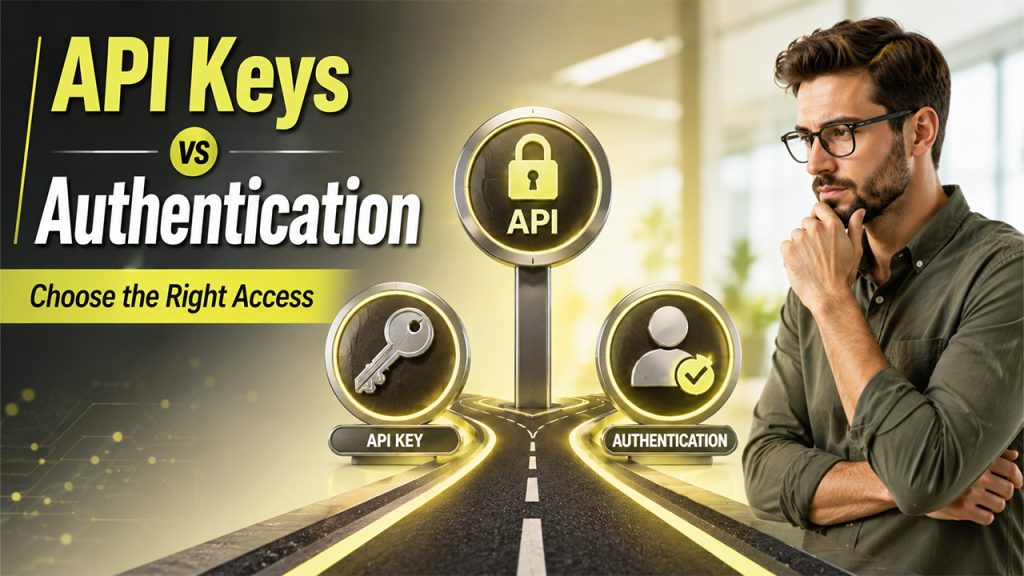
It is helpful to know where an API key aligns as compared to other approaches in common authentication:
For developers developing integrations, like the ones exploring developer-friendly APIs for tasks such as automation or captions, the choice between a more advanced method and an API key often comes down to how confidential the data is and how much control over access is required.
Since an API key can be a vulnerability point if mishandled, a few practices can go a long way:
Following such steps minimizes the risk of a leaked key being utilized for unexpected changes or unauthorized access.
At the core of it, there is an API key which is a simple but vital tool that allows applications to recognize themselves and securely communicate with APIs. It provides usage tracking, access control, and rate limiting, making it a practical first layer of authentication for countless service people use daily. While this is not the most sophisticated security method available nowadays, comprehending what an API key is and how to handle one responsible is a key skill for anyone working with connected apps, ranging from solo developers to teams handling numerous integrations.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。