





Unstructured data — documents, emails, shared drives, collaboration tools, recordings — has always been hard to govern. It doesn't fit neatly into databases. It moves across platforms. It accumulates in corners no one remembers creating. And now AI tools are surfacing more of it.
"AI is the most efficient ingestion engine ever built," said Jason Gowans, chief digital and technology officer at Levi Strauss. "Every internal RAG system, every copilot, every meeting transcription tool — they're all reading your unstructured data, and most of them weren't designed to respect data boundaries."
According to recent Cloud Security Alliance research commissioned by Thales, 68% of 210 organizations surveyed have significant unprotected unstructured data, yet 75% describe themselves as moderately or highly confident in their security posture. The disconnect often comes down to a deceptively simple question: Who owns this?
Related:Ask the Experts: The cloud cost reckoning
The two technology leaders interviewed here take different approaches — one built on shared accountability among security, data and privacy leaders, the other on pragmatic guardrails designed to preserve speed and flexibility.
Both say AI is forcing organizations to take a harder look at unstructured data governance.
We asked them how they've approached unstructured data security at their companies and what they'd tell peers still struggling to answer the ownership question.

Jason Gowans: Ownership is not a single name on an org chart; it's a contract between functions. At Levi's, the CISO owns the control framework and risk posture. The CDTO — my role — owns the data platforms, integration layer and the policies that govern how data flows. The chief privacy officer (CPO) is the third voice, particularly where customer or employee data is involved.
We landed on this model because no single function has complete visibility. Security can set controls, but they don't always know what data exists or how it's being used. Data teams know where things live but may not understand the threat landscape. Privacy knows the regulatory stakes, but not the technical architecture. Shared accountability forces alignment.
Gowans: AI was the forcing function. When we started deploying agentic search — AI that could retrieve and reason over internal documents — we discovered that a lot of data was underpermissioned. It wasn't exposed externally, but it was accessible to more people internally than it should have been. That's a manageable risk when humans are searching manually. It's a different risk when AI can surface and connect information instantly.
Related:Ask the Experts: Validate, don't just migrate
That's when we formalized the partnership. The CISO, CDTO and CPO now meet regularly, specifically on AI governance. Every AI deployment is treated as an unstructured data security event.
Gowans: What's working is the partnership at the top. When the CISO and I are aligned, escalations are rare. Teams know who to call and what the expectations are.
What's still evolving is the legacy footprint: Twenty-plus years of file shares, mailboxes, SharePoint sites and tools we acquired, deprecated or half-decommissioned. None of it lined up with the modern data model. None of it has clean ownership. Most of the unstructured data security problem in any large enterprise lives in that long tail, and the cost of working through it is real. We're working through it. But it's the kind of program measured in years, not quarters.
Gowans: Stop trying to name one owner. Name the accountabilities — who sets policy, who enforces controls, who owns the platforms, who handles incidents — and make those people talk to each other regularly. Classify before you control. And treat every AI deployment as an unstructured data event, because that's exactly what it is.
Related:Ask the Experts: When ransomware strikes, who takes the lead -- the CIO or CISO?
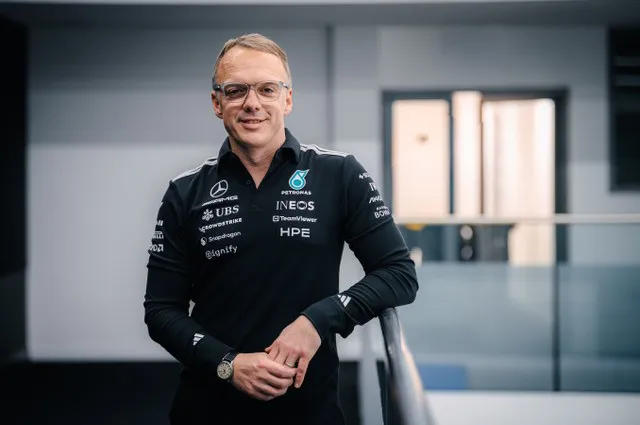
Michael Taylor: We have a relatively relaxed data ownership model throughout the organization. Where are we in terms of maturity? We do enough to enable the org to work and operate successfully. There are potential areas where we could slow things down to the point of diminishing returns.
It's an engineering-permissive, empowered culture. We trust and rely on our people.
We landed on "enough" by moving the conversation away from perfect to pragmatic. Enough is when we have visibility into our data, confidence that access is appropriate, controls that are proportionate to the risk, and a user experience that means people can still operate at pace.
Taylor: The gray areas are handled through ownership and context. In an engineering-permissive culture, you cannot secure collaboration by simply saying no. You have to understand what the data is, who genuinely needs it, what the consequence of exposure would be, and then apply controls that are proportionate.
Shared drives and collaboration tools are not the problem in themselves; the problem is unmanaged access, unclear ownership and data that outlives its purpose. So, the goal is to put sensible guardrails around the ways people already work, rather than forcing them into a model they will inevitably find ways to circumvent.
Taylor: AI has definitely moved the goalposts. It has not made "good enough" obsolete, but it has changed what "good enough" means.
In the past, we could tolerate a certain amount of mess in unstructured data because the effort required to find and connect information was high. With internal AI assistants, that effort is minimal. So now "good enough" has to include stronger visibility, cleaner permissions, clearer ownership, better labeling and a more deliberate approach to what data AI is allowed to index, retrieve or reason over.
Contributing Writer
Stephanie Overby is an award-winning journalist who has covered business and technology for nearly three decades. Her work focuses on the intersection of people, technology, and change -- with particular attention to IT leadership and digital transformation. She is a regular contributor to CIO.com and has written for The New York Times, CMO.com, Good Housekeeping, The Christian Science Monitor, and Inc.com, among others. Her reporting has been recognized by the American Society of Business Publication Editors, the Jesse H. Neal Awards, and the National Magazine Awards.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。