




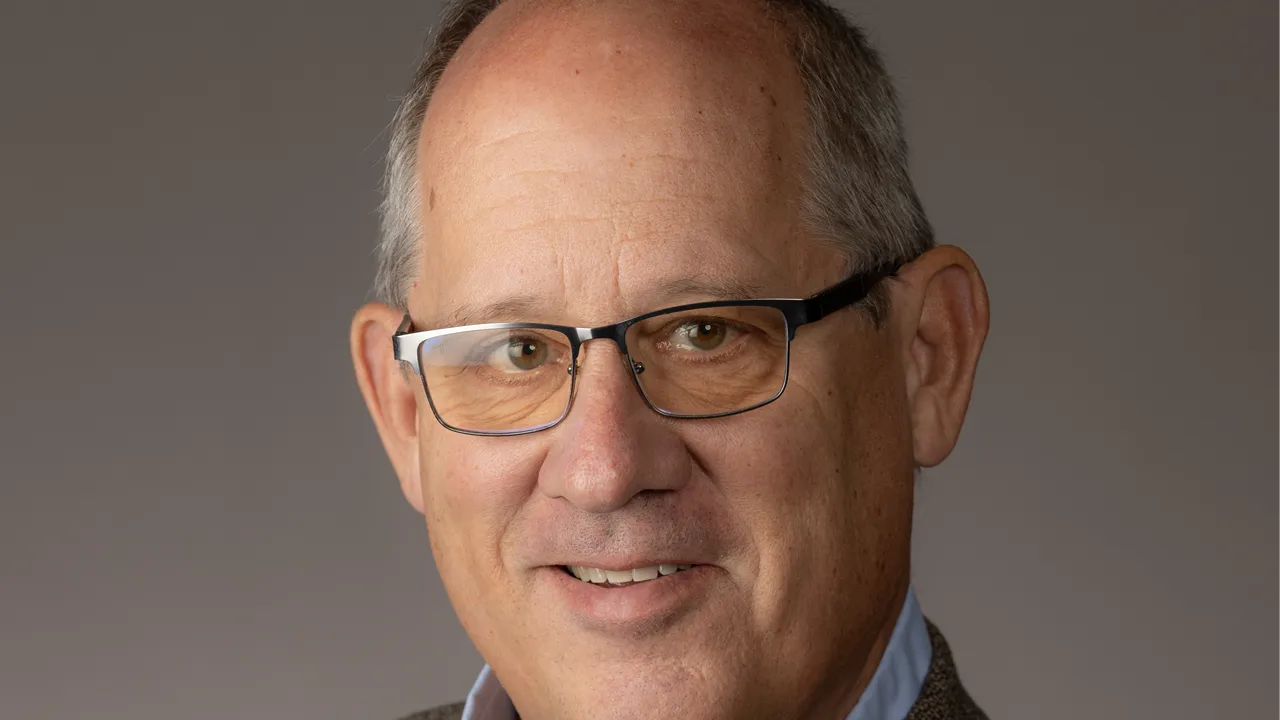
Courtesy Texas A&M University System
As users face a growing number of authentication prompts, security checks and compliance requirements, organizations need to pay more attention to the friction — and security risks — those safeguards can create.
That's the view of Texas A&M University System CIO Vince Kellen, who argues that implementing high-security protocols at the expense of usability and user experience no longer serves as an effective cybersecurity strategy.
The challenge, he explained, is protecting users without creating so much friction that they look for ways around security controls.
"Unless the [user] experience is wonderful, you can't have high security," Kellen said, in an interview with InformationWeek during the recent Cisco Live event in Las Vegas.
Without achieving both high security and high visibility into the network, together with a seamless user experience, "the user will invent ways around you," he added.
Related:How AI is changing the breadth of cybersecurity roles
Kellen pointed to multifactor authentication as one area where users are becoming frustrated with the hoops they have to jump through to access their accounts.
"You go to sites, and it's not just two-factor authentication — in some cases, it's four or five," he said. Layering multiple security technologies without considering the user experience can complicate cybersecurity programs and diminish their effectiveness.
That concern also affects how Kellen views zero-trust architectures, which he described as a critical part of his security strategy for Texas A&M University System. The network he oversees includes 12 universities and eight state agencies — each with its own CIO.
The key components of zero trust security are access and action — who has access to applications, and what is happening on the network (the action), he explained. For example, by using real-time packet inspection for threat detection and software-defined networking, an organization could flag an instance in which a user is attempting to share private data. This approach also speeds up response time to potential security threats.
"The network will say, 'OK, Vince, it looks like you're transmitting HIPAA data. We're going to immediately start to deploy real-time policy around your flows and your computer to redirect and change this,'" Kellen said.
The goal is to move more of the enforcement into the technology itself, he said — rather than depend on users to recognize every risk or make the correct security decision.
Kellen applies a similar view to securing agentic AI. He said he doesn't "fret about agents" but views them in the same way as securing human users.
Related:Cisco's Jeetu Patel on overcoming the 'AI trust deficit'
"I try not to get terribly freaked out just because the thing is called an agent," Kellen said.
For Kellen, securing agentic AI builds on many of the same principles CIOs already apply to users and devices. Agents still need identity, visibility, behavioral monitoring, and policy enforcement.
He added that he does worry about "semantic drift" — models that gradually diverge from their intended behavior — and what he called "semantic malfeasance," agents that act contrary to their intended purpose.
Behavioral monitoring offers one way to identify agent or model drift, Kellen said, noting that organizations have historically applied such monitoring to users and devices.
When it comes to encouraging behavioral changes in humans, Kellen said that cybersecurity trainings are useful for nudging users to comply with security policies, but training cannot carry the full burden of cybersecurity.
"The technical controls have to win," Kellen said.
Users might chastise themselves for falling for a phishing attempt, but humans are naturally trusting by nature, he pointed out. As a result, strong cybersecurity policy and technologies are needed to compensate for human error.
Related:Anthropic's Mythos forces a rethink of vulnerability management
Technical controls also perform better when they're "as invisible to the user as possible," so measures like biometrics can increase usability.
But, Kellen added, "we're still many years away from a real seamless [security] experience."
Senior Editor, InformationWeek
Kelsey Ziser is a senior editor at InformationWeek, where she covers C-suite dynamics, data strategies and the evolving cybersecurity threat landscape.
Kelsey also oversees the publication's IT Leaders Fast-5 column, which brings peer insights to IT professionals, and the tech layoffs tracker. She has been with InformationWeek since September 2025.
Before joining InformationWeek, she spent nine years at sister publication Light Reading, reporting on a broad range of topics including smartphones and devices, AI, satellite connectivity and enterprise networking. Kelsey has a Bronze Regional Azbee Award in the Technical Article category. Outside of work, she enjoys reading four (or 12) books at once, watching movies about space travel, crafting and tending to an ever-growing collection of houseplants. Kelsey has a bachelor's degree in journalism and mass communication from UNC-Chapel Hill and is based in Raleigh, N.C. She can be reached at [email protected] or on LinkedIn.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。