





Financial institutions in Hong Kong face a defining moment in how they deliver technology-driven banking: the Hong Kong Monetary Authority (HKMA) launched Fintech 2030 on November 3, 2025, introducing the DART framework with named initiatives and clear supervisory expectations.
DART represents four foundational pillars:
- Data: Building unified data infrastructure and governance
- AI: Deploying artificial intelligence responsibly and at scale
- Resilience: Ensuring operational continuity and cyber security
- Tokenisation: Enabling digital asset innovation and blockchain adoption
For Hong Kong banks, DART moves beyond the groundwork of Fintech 2025 into concrete programs with supervisory weight. It sets regulatory standards across the pillars, creates competitive differentiation for early adopters, introduces risk management frameworks for AI governance and post-quantum cryptography (PQC), and requires participation in ecosystem initiatives like the Commercial Data Interchange (CDI) and GenAI Sandbox++. DART signals clear supervisory direction. Banks that move early will be better positioned to meet both regulatory expectations and market demands.
AWS provides deployed, proven capabilities across the DART pillars today. Customer stories from NatWest, Commonwealth Bank of Australia (CBA), Visa, Prudential, Capital One, Vanguard, and Coinbase, demonstrate these capabilities at production scale. In this post, you will learn how AWS capabilities map each DART pillar through production customer examples, and find resources to begin building in your own environment.
“D”ata – Creating next-generation data infrastructure
HKMA’s Data pillar requires banks to share trade-finance and anti-money laundering (AML) data across institutions under strict governance, with each party controlling what it shares, with whom, and for how long:
- Consolidating fragmented data into a single layer serving analytics, machine learning, and regulatory reporting from one copy of the truth
- A unified architecture on open standards with scalability for petabyte-scale workloads, real-time ingestion, and resilience patterns across failure domains
- Consent-governed sharing workflows for cross-institutional access with time-bound entitlements and automated approval chains
- Confidential compute environments that process sensitive financial data without exposing raw records between institutions
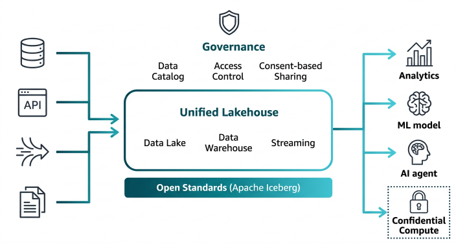
Figure 1: AWS unified data strategy—data sources converge into a single lakehouse with governed sharing and confidential compute.
Unified Data Infrastructure
To address these requirements, you can consolidate fragmented data silos with a lakehouse architecture built on open standards. Amazon SageMaker Unified Studio provides a single development environment for data engineers, analysts, and data scientists. Teams build SQL queries, notebooks, and visual ETL pipelines without switching tools. It unifies analytics on Apache Iceberg with a single-copy architecture. Zero-ETL integrations connect operational databases directly, eliminating data movement. AWS Lake Formation enforces fine-grained access controls at the table, column, and cell level. Teams query data in place with no movement, no duplication, and no drift between copies.
Using Apache Iceberg as the open table format supports portability across engines and reduces vendor lock-in. Amazon S3 Tables manages these Iceberg tables at scale as first-class Amazon Simple Storage Service (Amazon S3) resources. It delivers higher transactions per second (TPS) and automated compaction and snapshot management. As data grows to a significant scale, banks need purpose-built warehousing for complex analytics and regulatory reporting. Amazon Redshift provides data warehousing at petabyte-scale with zero-ETL integration, streaming ingestion, and cross-account data sharing without copying. Before data reaches analytics or models, it must be discovered, cataloged, and quality checked. AWS Glue handles serverless data integration, crawling, cataloging, and transforming data across sources. Built-in PII detection and data-quality rules flag anomalies before they reach downstream consumers.
Data and AI Governance
Cross-institutional data sharing demands consent-based access control. Amazon DataZone provides consent-governed cataloging, discovery, and sharing. Data producers publish assets with metadata, lineage, and quality scores. Consumers request access through governed workflows with automated approval chains. Subscription grants enforce time-bound access that expires automatically. AWS Key Management Service (AWS KMS) encrypts data assets at rest and AWS CloudTrail provides audit trails of all access and sharing activity for regulatory evidence.
When institutions must derive shared insights without any party seeing another’s raw records, AWS Nitro Enclaves provides isolated compute environments with no persistent storage, no interactive access, and no operator access. Cryptographic attestation verifies the enclave’s code before any data enters it. This allows multi-party computation while maintaining strict data boundaries. For field-level data protection, the AWS Serverless Tokenization solution replaces sensitive values with random tokens, simplifying regulatory compliance by reducing the components that handle sensitive data directly.
Customer References
NatWest is consolidating nearly 30 fragmented customer master databases to three or fewer on a lakehouse built with SageMaker Unified Studio, establishing a single governed copy of customer data across retail, wealth, and commercial banking. Amazon DataZone allows each line of business to publish and discover data assets through consent-governed workflows, directly addressing the cross-institutional sharing requirements.
Commonwealth Bank of Australia migrated 61,000 pipelines (10 PB) in nine months to a unified lakehouse on Apache Iceberg, with AWS Glue for cataloging and Lake Formation for fine-grained access control. Their CommBank.data marketplace on SageMaker Unified Studio and DataZone serves 40 lines of business from a single governed data layer without duplication.
Visa built Protect A2A, scoring non-card payment fraud in under 250 ms at 99.99% uptime. Sensitive PII is encrypted and processed exclusively inside AWS Nitro Enclaves where no operator can access it, demonstrating the confidential compute pattern for multi-party data collaboration without exposing raw records.
“A”rtificial Intelligence – A new holistic artificial intelligence strategy
HKMA’s AI pillar expects banks to move generative AI from sandbox pilots to production-scale deployment, with supervisory frameworks for responsible adoption and AI-enhanced regulatory oversight.
- Access to diverse foundation models without provider lock-in, with the flexibility to select the right model for each use case
- Responsible AI guardrails enforced at the infrastructure layer, with content policies, topic restrictions, and automated reasoning checks applied centrally
- An agentic deployment runtime with session isolation, identity management, real-time policy enforcement, and comprehensive observability for auditability
- Resilient training infrastructure for fine-tuning domain-specific models on sensitive financial data that cannot leave the bank’s environment
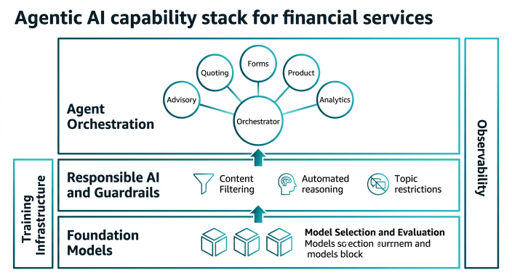
Figure 2: The agentic AI stack—foundation models, guardrails, and agent orchestration with observability.
Scalable AI Infrastructure and Responsible Guardrails
Banks need access to many foundation models without committing to a single provider. Amazon Bedrock serves both proprietary and open source models, giving banks the flexibility to use closed models for general-purpose tasks and self-hosted open source models for workloads with stricter compliance requirements. Bedrock provides access to hundreds of foundation models and serves more than 100,000 organizations. Intelligent Prompt Routing and model distillation optimize for cost and latency across FSI workloads. To ground model responses in institutional knowledge rather than general training data, Amazon Bedrock Knowledge Bases connects models to bank-specific policies, product catalogues, and regulatory documents through retrieval-augmented generation (RAG). Amazon Bedrock maintains ISO, SOC, and CSA STAR certifications, FedRAMP High authorization, and HIPAA eligibility.
Responsible deployment requires controls that compliance teams can set centrally and audit independently of application code. Two complementary capabilities address this. Amazon Bedrock Guardrails provides content filtering with configurable topic-level restrictions, preventing models from discussing competitors, revealing internal policies, or generating non-compliant advice. Guardrails apply consistently across models and agents, creating a centralized governance boundary. Automated Reasoning checks adds a separate layer of logical verification, using formal reasoning to validate that model outputs are factually consistent with source policies and do not contain hallucinated claims. Together, these two features deliver the responsible AI governance that supervisory expectations require.
Agentic AI and Production Deployment
Moving from chatbot prototypes to production agents requires a platform that enforces security boundaries on every action an agent takes. Amazon Bedrock AgentCore is an agentic platform for building, deploying, and operating agents securely at scale using supported frameworks and foundation models. AgentCore works with open source frameworks including CrewAI, LangGraph, LlamaIndex, Google ADK, OpenAI Agents SDK, and Strands Agents, and with foundation models in or outside of Amazon Bedrock.
For deployment and connectivity, AgentCore Runtime provides a secure, serverless environment with true session isolation in Firecracker microVMs. Gateway converts existing APIs and services into Model Context Protocol (MCP) compatible tools for enterprise data access. Identity manages agent authentication against existing identity providers with OAuth 2.0. This eliminates hardcoded credentials across agent deployments.
For governance and quality assurance, Policy uses Cedar (AWS’s open source policy language) to intercept tool calls before execution. Observability traces every step in OpenTelemetry-compatible format for audit and debugging. Evaluations provides automated agent assessment, measuring task execution quality before and after deployment.
Domain-Specific Model Training
Banks fine-tuning models for AML or credit decisioning need resilient training infrastructure for sensitive data that cannot leave their environment. Amazon SageMaker HyperPod provides distributed training with automatic fault detection and recovery across hundreds of accelerators. If a node fails mid-training, HyperPod replaces it and resumes without manual intervention. Checkpointless training reduces training time by removing periodic state saves, allowing banks to iterate faster on proprietary FSI models at production scale.
Customer Reference
Prudential deploys more than 100,000 advisors on a microagent platform built on Amazon Bedrock. An orchestration agent coordinates five specialized sub-agents through MCP and A2A gateways, with Cedar policies enforcing action-level permissions and Bedrock Guardrails applying responsible AI controls. Deployment cycles dropped from 6–8 weeks to 3–4 weeks.
“R”esilience – Enhancing business, technology, and quantum resilience
HKMA’s Resilience pillar requires banks to prove operational continuity and prepare for future cryptographic threats. Supervisory expectations cover both present-day cyber resilience and long-term quantum risk through a post-quantum cryptography (PQC) transition plan. This creates four technical requirements:
- Physically isolated failure domains with defined RTO and RPO targets that regulators can audit
- Automated remediation and chaos-engineering evidence that demonstrates resilience posture without relying on manual intervention
- Compliance certifications and audit-ready documentation aligned with supervisory cloud governance standards
- Cryptographic agility to adopt quantum-resistant algorithms for data in transit and at rest, protecting against harvest-now-decrypt-later threats
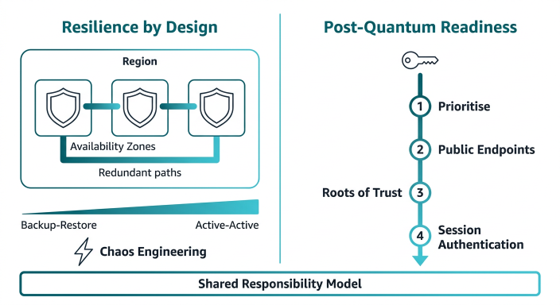
Figure 3: Resilience by design and post-quantum readiness—multi-AZ redundancy with a four-step PQC migration roadmap.
Resilience by Design
Banks need infrastructure where a failure in one facility does not cascade to others. When you build on AWS, each Region comprises three or more physically separate Availability Zones (AZs) with independent power, cooling, and networking, connected by redundant low-latency links. Gray failure detection identifies degraded components before they cause visible outages, and automated remediation replaces failed infrastructure without manual intervention, keeping recovery within defined RTO targets.
Regulators expect banks to demonstrate their resilience posture with evidence, not just documentation. AWS Fault Injection Service (FIS) runs controlled chaos experiments, simulating AZ failures, network latency, and resource exhaustion, and produces audit-ready reports that demonstrate resilience posture to regulators. Banks can validate that their architectures meet RTO and RPO targets under realistic failure conditions before an actual incident occurs.
Under the shared responsibility model, AWS secures the underlying infrastructure to the highest standards, meaning banks building on AWS already inherit the compliance certifications and resilience capabilities that supervisory cloud governance frameworks require. AWS holds certifications and attestations across major frameworks including ISO 27001, SOC 1/2/3, CSA STAR, PCI DSS, and others (refer to AWS Compliance Programs). AWS Artifact provides on-demand access to these compliance reports and security documentation, supporting banks in satisfying audit requirements without manual evidence collection. This shared model means banks can focus their engineering effort on application-level resilience rather than rebuilding infrastructure-level controls from scratch.
Post-Quantum Cryptography Readiness
Financial data with long confidentiality horizons is vulnerable to harvest-now-decrypt-later threats, where threat actors capture encrypted traffic today and decrypt it once quantum computers mature. Banks need to adopt quantum-resistant algorithms now. AWS delivers post-quantum cryptography that’s deployable today. AWS-LC and s2n-tls provide a FIPS 140-3 validated open source cryptographic library with ML-KEM support, allowing hybrid PQC TLS connections now. Hybrid mode means applications negotiate quantum-resistant key exchange alongside classical algorithms, maintaining backward compatibility while gaining forward secrecy.
For digital signatures and roots of trust, ML-DSA in AWS KMS and AWS Private Certificate Authority (Private CA) provides quantum-resistant algorithms. PQC protection extends across AWS services covering both data in transit and at rest, and banks can activate it through configuration changes rather than application rewrites.
Customer References
Capital One engineers for five nines using shuffle sharding, assigning each customer to a unique combination of infrastructure cells. During the US-East-1 outage, services failed over within a 500 ms SLA with automatic failover to the secondary region. AWS FIS drives chaos engineering with audit-ready evidence, directly addressing the requirement for demonstrated resilience posture.
Vanguard established a Cryptography Center of Excellence and uses AWS KMS at 30 billion operations per hour. A discovery framework built on AWS Config, Amazon CloudFront logs, and Amazon Athena inventories cryptographic usage across inbound and outbound connections, targeting ML-KEM adoption by late 2029, addressing the cryptographic agility requirement.
“T”okenisation – Infrastructure for the future of money
HKMA’s Tokenisation pillar aims to build a vibrant ecosystem for tokenised assets and digital money, accelerating the tokenisation of real-world assets (RWAs) and settling them with new forms of digital currency. For banks, this translates into four infrastructure requirements that differ sharply from consumer crypto:
- Blockchain nodes running 24/7 with institutional-grade availability for government bond and digital currency settlement
- Key management where private keys never exist in plaintext outside hardware security boundaries
- Inter-institutional connectivity that keeps settlement traffic off the public internet
- Auditable transaction governance with compliance checks, allowlisting, and multi-signature approval before execution
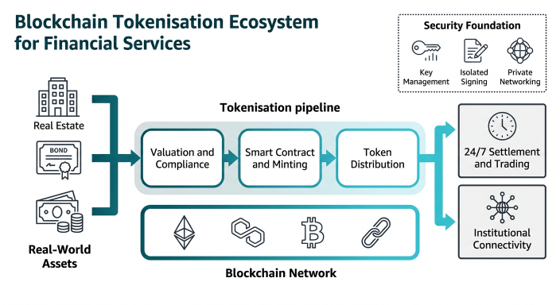
Figure 4: The tokenisation ecosystem—real-world assets flow through a tokenisation pipeline to blockchain networks with secure key management.
Blockchain and Distributed Ledger Infrastructure
Banks need the flexibility to adopt different protocols and networks for different tokenisation use cases, from government bond settlement to stablecoin issuance. AWS approaches blockchain infrastructure as composable building blocks rather than a single managed service. AWS Blockchain Node Runners provides vetted deployment blueprints for self-managed blockchain nodes, covering major protocols including Hyperledger Besu, Ethereum, and others. Institutions can deploy node infrastructure with pre-validated configurations for high availability and secure RPC access. Amazon Elastic Kubernetes Service (EKS) runs blockchain nodes with orchestration and Auto Scaling, and AWS PrivateLink keeps settlement traffic off the public internet, addressing the private connectivity requirement.
Institutional-Grade Key Management and Transaction Signing
Tokenised finance demands that private keys never leave hardware security boundaries. AWS KMS supports the ECC_SECG_P256K1 (secp256k1) key spec used by Ethereum and Bitcoin for transaction signing, with keys protected inside FIPS 140-3 Security Level 3 validated HSMs. For institutions that require full custody with single-tenant hardware, AWS CloudHSM provides dedicated HSM instances in the customer’s VPC with secp256k1 support and PKCS#11/JCE/OpenSSL interfaces, giving banks exclusive control over key material.
For transaction signing that requires additional isolation, Nitro Enclaves adds an air-gapped signing layer: unsigned transactions enter the enclave through a local socket, the enclave retrieves the encrypted key from KMS (verified through cryptographic attestation), signs in memory, and returns only the signature. The private key never touches the host.
Real-World Asset Tokenisation
Beyond infrastructure primitives, banks need an end-to-end issuance pipeline for tokenising real-world assets. The AWS and Fireblocks reference architecture delivers this: multi-party computation (MPC) based key management that removes single points of compromise, a policy engine for transaction governance and compliance checks (allowlist policies, velocity limits, multi-signature approval), smart contract deployment, and token minting. This architecture addresses the end-to-end lifecycle from asset valuation through on-chain issuance and secondary settlement.
Customer Reference
Coinbase scaled 10x in 18 months on AWS EKS, achieving 68% resource reduction and sub-minute scale-out across 3,500 service configurations. This demonstrates the infrastructure economics required for 24/7 digital asset operations with institutional-grade availability.
Conclusion and Next Steps
Each DART pillar creates specific technical requirements that Hong Kong banks must address. This post demonstrated how AWS capabilities map directly to those requirements, from unified data architectures and consent-governed sharing, through responsible AI with agentic deployment at scale, to infrastructure-level resilience with post-quantum readiness, and composable blockchain infrastructure for tokenised asset settlement. The customer evidence throughout this post confirms these capabilities operate at production scale today.
Explore the following resources to begin building DART-aligned workloads in your AWS environment:
- Amazon Bedrock AgentCore Developer Guide for deploying responsible AI agents with guardrails and observability
- AWS Post-Quantum Cryptography guidance for inventorying cryptographic dependencies and enabling hybrid PQC TLS
- RWA tokenisation reference architecture with Fireblocks for an end-to-end issuance pipeline
- s2n-tls on GitHub for open source TLS implementation with ML-KEM support
- AWS Well-Architected FSI Lens for assessing resilience posture
Disclaimer
The content in this post doesn’t constitute legal, compliance, or regulatory advice. Customers are responsible for making their own independent assessment of the information in this post, including any determination of compliance with applicable laws and regulations, and for any use of the AWS services mentioned. AWS services and customer examples described in this post are provided for informational purposes and don’t guarantee regulatory compliance with HKMA requirements or any other regulatory framework.