


When the FBI puts out a public service announcement that deliberately appears to avoid naming the company at the centre of the story, you can usually work out which one it is...
On 15 May 2026, the FBI's Internet Crime Complaint Center (IC3) issued an advisory about the ShinyHunters extortion gang that recently breached "an online Learning Management System" used by educational institutions across the United States.
The advisory doesn't say the platform that was hacked was Canvas, and that the company concerned was Instructure.
Frankly, it didn't need to. The security breach was not just big news on cybersecurity blogs, it made headlines worldwide.
On 12 May, Instructure quietly confirmed it had reached "an agreement" with the attackers, who apparently had helpfully provided "digital confirmation of data destruction (shred logs)."
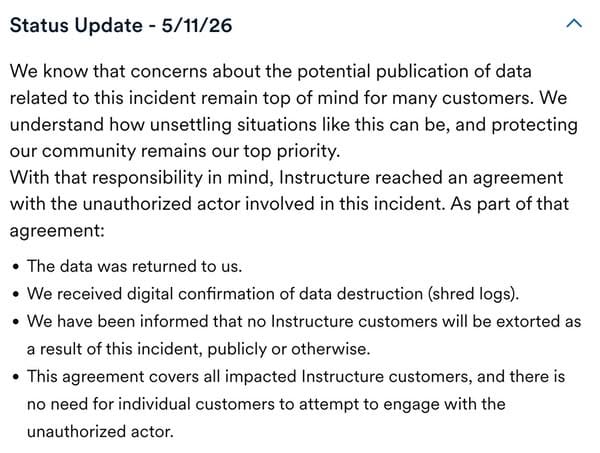
In short, Instructure paid the ransom.
There are a few possible problems with paying an extortion gang and trusting that they will honour the deal. One of the big problems is that it requires you to trust an extortion gang.
And I supposed that's why the FBI wrote its PSA. It's a polite reminder to everyone (whether they be students, parents, or staff) that their data may still be out there - and that it might be sensible to be braced to the possibility that criminals could prove not to be trustworthy - and start putting the stolen information to work.
For instance, ShinyHunters or their cybercriminal counterparts could use the potentially sensitive personal information to harras innocent parties caught up in the breach through no fault of their own.
As the FBI warns, in an attempt to extort money ShinyHunters "commonly use harassment strategies, sending threatening text messages and phone calls to victims and their family members, and in some cases, swatting."
Furthermore, extortionists might falsely claim to have access to compromising information, such as embarrassing photographs or videos of victims.
And then there is always the possibility of spearphishing campaigns, where hackers can disguise their poisoned messages through the use of stolen student IDs, professors' names, or snippets of private messages that were stolen in the breach.
The FBI advises that victims do not engage with anyone claiming to hold their data for ransom, and wait for official guidance from their educational establishment to learn what details may have been compromised.
Furthermore, users are advised to not click on suspicious links or unsolicited attachments, and to enable multi-factor authentication where possible to harden the security of their accounts.
Every successful ransom payment writes a sales pitch for the next attack, and ShinyHunters — already linked to incidents at Ticketmaster, the University of Pennsylvania, Princeton, Harvard, Infinite Campus, and McGraw Hill — will not be stopping any time soon.
For students caught in the middle: assume your data is out there, treat every unexpected message with suspicion, and don't let anyone panic you into paying, clicking, or replying. The criminals are counting on your fear. Don't give it to them.
There is, of course, no certainty that ShinyHunters (or any other criminal) will attempt to exploit the information seized by hackers during the Canvas/Instructure breach - but it would it would be wise to consider the possibility, and ensure that defensive measures are properly adopted.
And that advice also goes to other "online learning management systems" and educational establishments. Having receive a ransom payment for its attack on Canvas, ShinyHunters and other extortion gangs are only likely to be further incentivised to launch similar attacks in future.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。