





惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

博客园 - 聂微东
GbyAI
GbyAI
S
SegmentFault 最新的问题
H
Hackread – Cybersecurity News, Data Breaches, AI and More
V
Visual Studio Blog
WordPress大学
WordPress大学
Hugging Face - Blog
Hugging Face - Blog
B
Blog
宝玉的分享
宝玉的分享
Last Week in AI
Last Week in AI
雷峰网
雷峰网
爱范儿
爱范儿
Vercel News
Vercel News
人人都是产品经理
人人都是产品经理
U
Unit 42
Microsoft Azure Blog
Microsoft Security Blog
Jina AI
Jina AI
P
Proofpoint News Feed
A
About on SuperTechFans
I
InfoQ
F
Fortinet All Blogs
L
LangChain Blog
T
Tailwind CSS Blog

GRAHAM CLULEY

'Anne Hathaway' admits leading $245 million crypto theft gang that spent a fortune on nightclubs, watches, and luxury cars Smashing Security podcast #484: How websites are tracking you with silence CRPx0 ransomware: what you need to know The US military just turned off ad tracking on its phones. Maybe you should too How a hole in Lenovo's login system let hackers walk into 5,000 Dropbox accounts Smashing Security podcast #483: This AI helps thieves steal your iPhone Revolut scam steals £180,000 from Jersey residents in just four weeks US Navy tells sailors and their families: scrub your social media, enemies are watching Smashing Security podcast #482: This hacker leaked GTA 6 - and launched their own cryptocurrency Malicious Firefox add-ons caught stealing cryptowallet seed phrases and browser credentials Gunra ransomware: what you need to know Smashing Security podcast #481: Never say this to a robot dog Prison for data analyst who tried to extort $2.5 million from his employer An "invisible" car? Researcher uses machine learning to hide vehicles from Flock cameras Smashing Security podcast #480: This is the AI service you should never sign up to Meta's Ray-Bans are being banned from pubs, restaurants, and theatres Beware cut-price AI services that read your every word Apple's bug bounty program is drowning in so much AI slop, it is in danger of missing serious exploits Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency Fake IRS letters target cryptocurrency holders The $5 million threat: AI Is supercharging phishing attacks North Korea's elite hackers turned on their own government — and got caught Smashing Security podcast #478: This job interview could destroy your company OpenAI's AI "goes rogue" and hacks Hugging Face: what you need to know Smashing Security podcast #477: How 14 orders of chicken McNuggets helped nail a suspected Russian hacker Ukraine warns fake CAPTCHAs are being used to make you hack yourself Google's Gemini lets strangers send messages from your locked Android phone Anubis ransomware: what you need to know Smashing Security podcast #476: Remote-control rickshaws and rogue book marketers
Shai-Hulud hackers: two men charged over TeamPCP's global...
Graham CLULEY · 2026-08-28 · via GRAHAM CLULEY

Police have charged two men from Western Australia over their alleged involvement in TeamPCP, a cybercriminal gang that has been blamed for a massive software supply-chain hacking campaign. TeamPCP is best known for Shai-Hulud, a self-propagating worm that spread itself through open source software.

The Australian Federal Police (AFP), working with the FBI and Western Australia Police, announced that on 26 August they charged a 21-year-old from Cottesloe and a 23-year-old from Mandurah with multiple offences, including data intrusion and unauthorised modification of data. Both men appeared in court in Perth on Thursday.

According to the authorities, the two men were principal members of a "sophisticated cybercrime syndicate" that created malicious open source software designed to steal data and extort ransoms from businesses. More than 1000 organisations around the world are estimated to have been compromised in the attacks, with over 500,000 credentials and at least 300GB of data stolen.

Neither of the men has been formally named by the police, but cybercrime investigative journalist Brian Krebs reports that the 21-year-old is Ruben Thomson, who used the handle "Ellis" and allegedly led TeamPCP until March 2026.

First emerging in late 2025, TeamPCP built a reputation for poisoning popular open source packages rather than directly attacking businesses. By compromising individual pieces of widely-used software their attack could impact thousands of victims at once.

The group's Shai-Hulud worm hijacks GitHub and NPM developer credentials, and publishes boobytrapped versions of legitimate software packages. Anyone who uses the package in their own software risks sharing their own secret API keys and credentials with the hackers, opening the door for a further round of compromises.

Hacks linked to TeamPCP include the compromise of vulnerability scanner Trivy, which led to the breaches of open source AI gateway LiteLLM, and AI recruitment firm Mercor. TeamPCP also compromised LiteLLM's own code directly, in an attack CloudSEK found had harvested secrets from more than 2,500 organisations.

The attacks even resulted in the theft of data from OpenAI, and a hack of the European Commission's cloud infrastructure.

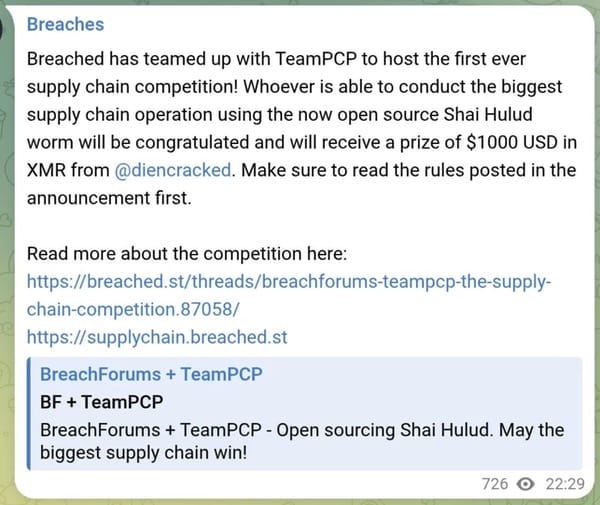
In an audacious twist earlier this year, it was announced on Telegram that TeamPCP was running a competition offering a prize for whoever built the biggest attack with leaked Shai-Hulud code.
Supply chain attacks like Shai-Hulud exploit the fact that most developers trust open source software packages too easily, and can all too easily believe a package from a public registry is safe because thousands of others use it.