

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

WordPress大学
WordPress大学
Jina AI
Jina AI
小众软件
小众软件
GbyAI
GbyAI
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
博客园 - 【当耐特】
D
DataBreaches.Net
腾讯CDC
V
Visual Studio Blog
博客园 - 叶小钗
B
Blog
Apple Machine Learning Research
T
The Blog of Author Tim Ferriss
S
SegmentFault 最新的问题
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
V
V2EX
博客园 - 三生石上(FineUI控件)
云风的 BLOG
云风的 BLOG
The Cloudflare Blog
MongoDB | Blog
MongoDB | Blog
有赞技术团队
有赞技术团队
U
Unit 42
博客园 - 司徒正美
博客园 - 聂微东

Help Net Security

Your work apps are quietly handing 19 data points to someone ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security
ClickFix campaign delivers Mac malware via fake Apple page
Zeljka Zorz · 2026-04-10 · via Help Net Security

Security researchers at Jamf have uncovered a new ClickFix-style attack targeting Mac users via a fake Apple-themed webpage offering instructions on how to “reclaim disk space on your Mac”.
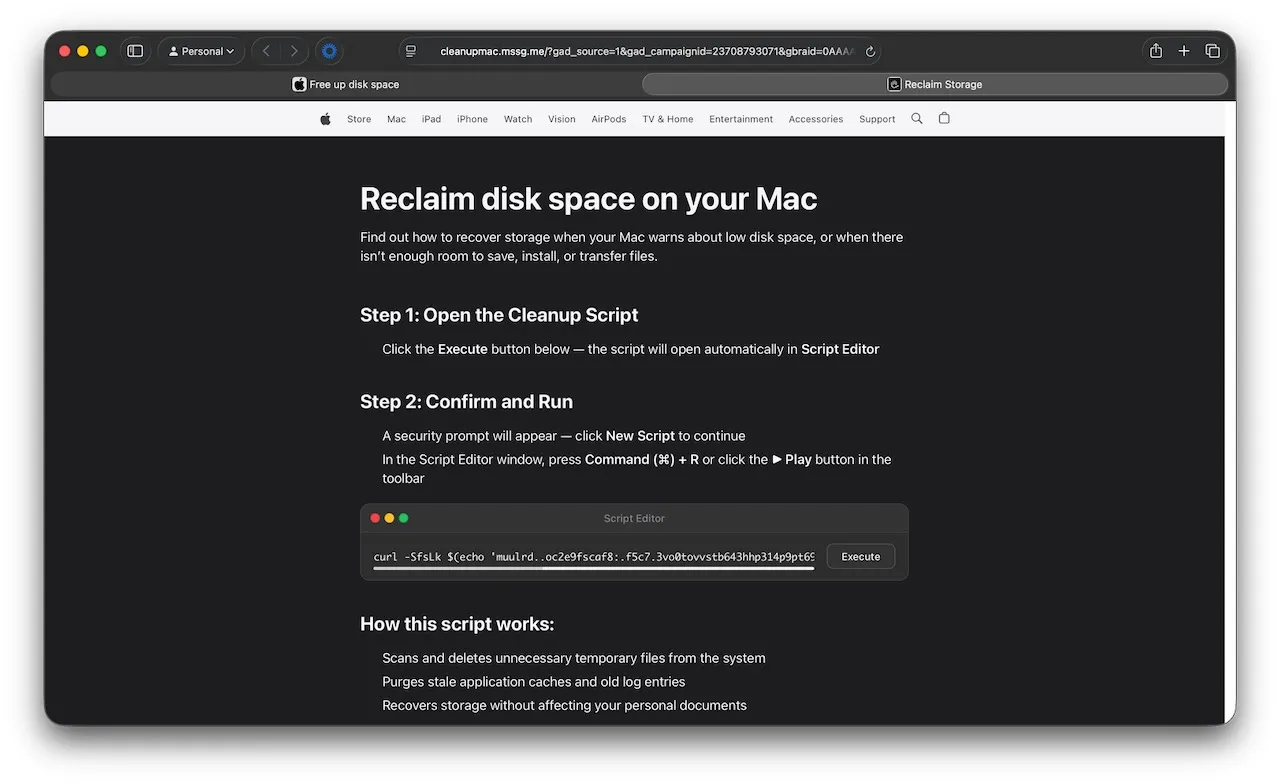
ClickFix Mac Script Editor

The malicious page (Source: Jamf)

ClickFix for everybody

ClickFix is a social engineering technique that cons victims into running malicious commands on their own machine, usually by pretending the commands are needed to fix a problem or perform routine upkeep.

This technique was initially aimed at Windows users, but in time, macOS and Linux users also started getting targeted.

“The go-to approach for ClickFix [macOS] techniques has long been convincing users to copy and paste malicious commands into Terminal under the guise of troubleshooting or routine system maintenance. Apple took direct aim at this in macOS 26.4, introducing a security feature that scans commands pasted into Terminal before they’re executed,” Jamf researchers noted.

For that reason, attackers have switched to using a browser-triggered workflow to launch Script Editor, a code editor for the AppleScript and Javascript for Automation scripting languages. (Both Terminal and Script Editor are installed by default on macOS.)

The lure and the end result

From the victims’ point of view, the attack looks like this:

  • They visit the malicious page and follow the instructions
  • They click the provided “Execute” button
  • The page shows a prompt asking them to allow the website to open Script Editor
  • The Script Editor is opened and is pre-populated with the attackers’ script
  • Depending on the macOS version they use, they may or may not see an additional warning against running the script
  • If they ignore the warning and allow the script to be saved on the disk and executed, the script will covertly download an Atomic Stealer (aka AMOS) variant and execute it.

Atomic Stealer is a subscription product, sold to criminals who then deploy it however they like. It’s capable of collecting system information, stealing data stored in Keychain (Apple’s built-in password management system), autofill data, passwords, cookies, and credit card information from browsers, cryptocurrency wallets, and more.

Jamf researchers have shared indicators of compromise related to this malware delivery campaign.

Subscribe to our breaking news e-mail alert to never miss out on the latest breaches, vulnerabilities and cybersecurity threats. Subscribe here!