

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

G
Google Developers Blog
D
Docker
Stack Overflow Blog
Stack Overflow Blog
GbyAI
GbyAI
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
Google DeepMind News
M
MIT News - Artificial intelligence
H
Help Net Security
T
Tailwind CSS Blog
Engineering at Meta
Engineering at Meta
L
LangChain Blog
MongoDB | Blog
MongoDB | Blog
腾讯CDC
H
Hackread – Cybersecurity News, Data Breaches, AI and More
S
SegmentFault 最新的问题
博客园 - 司徒正美
C
Check Point Blog
B
Blog
Y
Y Combinator Blog
Microsoft Azure Blog
P
Proofpoint News Feed
F
Fortinet All Blogs
美团技术团队
D
DataBreaches.Net

Help Net Security

Your work apps are quietly handing 19 data points to someone ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security Acronis GenAI Protection gives MSPs control over AI usage and data risks - Help Net Security
If cyber espionage via HDMI worries you, NCSC built a dev...
Sinisa Marko · 2026-04-23 · via Help Net Security

A new cybersecurity device developed by the National Cyber Security Centre (NCSC) should be a helpful solution for protecting governments and businesses from malicious activity carried through display connections.
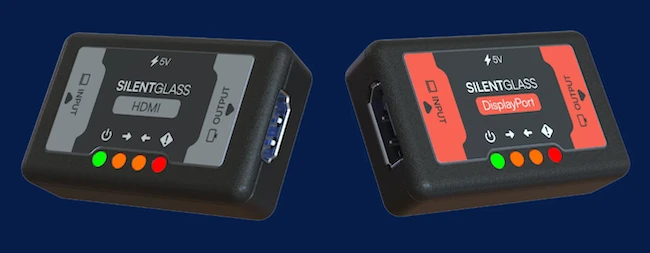
SilentGlass cybersecurity device

Called SilentGlass, the plug-and-play tool is designed to protect HDMI and DisplayPort links from potential cyberattacks.

The NCSC warns that monitors are an attractive target for cyber attackers as they can process and store sensitive data, and are highly likely to be exploited to gain access to networks for espionage, disruption, or financial gain, while existing mitigations are often costly and inefficient.

“Display screens and monitors are everywhere in modern business environments, and the SilentGlass device will help protect previously vulnerable IT infrastructure with unprecedented ease,” said Ollie Whitehouse, CTO at NCSC.

“Its development and commercialisation shows the impact that the NCSC can have, alongside industry partners, with an affordable and effective product now globally available,” added Whitehouse.

The NCSC states that the technology has already been deployed within government systems. It has been approved for use in high-threat environments and is available for commercial purchase.

The device is being manufactured and distributed under licence by Goldilock, in partnership with Sony UK Technology Centre.

“SilentGlass addresses a gap that has been widely overlooked. The hardware interfaces people rely on every day have rarely been treated as security boundaries, despite being exposed to risk through supply chains, third-party servicing, and direct physical access,” noted Stephen Kines, Co-Founder at Goldilock Labs.

“What was once confined to national security environments is now being applied with a low-cost, easy to deploy solution for CNI and businesses where the same risks exist,” concluded Kines.