








Cisco Live AMER 2026 was the perfect place to put the Agentic SOC to work, protecting the attendees and conference infrastructure. We innovated by giving the Agentic SOC access to Endace’s always-on, full packet capture, and asked the agent to assess a potential SharpHound Recon attack that we had seen while threat hunting. Within minutes, the agent returned an accurate and descriptive assessment of the threat, concluding that it was a benign near miss. This saved us many hours of work, giving us confidence that the Agentic SOC will be a massive boost to security and productivity. This blog explores how we built the integrations and how AI helped us with our threat hunt and threat assessment.
At Cisco Live AMER 2026 we deployed always-on, full packet capture as a source of forensic evidence, integrated with Agentic AI, to support the conference SOC directives of Protect, Educate, and Innovate. Always-on, full packet capture provides unique insight into all activity on the network, delivering critical context and evidence for Incident Response and Threat Hunting teams, as well as an unmatched data lake of all network activity for the emergent Agentic SOC.
The challenge when human analysts analyze packet data is whether they have the expertise and experience to interpret and understand what packets are telling them: because not everyone is a packet guru.
To make full use of this rich network data, we decided to integrate Endace full packet capture with the Agentic AI capabilities built into Cisco XDR and Splunk Enterprise Security, along with our custom agentic tool. The goal was to empower our incident responders with powerful evidence and reasoning to expedite the decision-making for suspicious activity. Some of our analysts were spending their first day ever in a SOC, so our goal was to help them be productive quickly using Agentic AI. This was also a great opportunity to understand how Agentic AI helps productivity in the SOC.
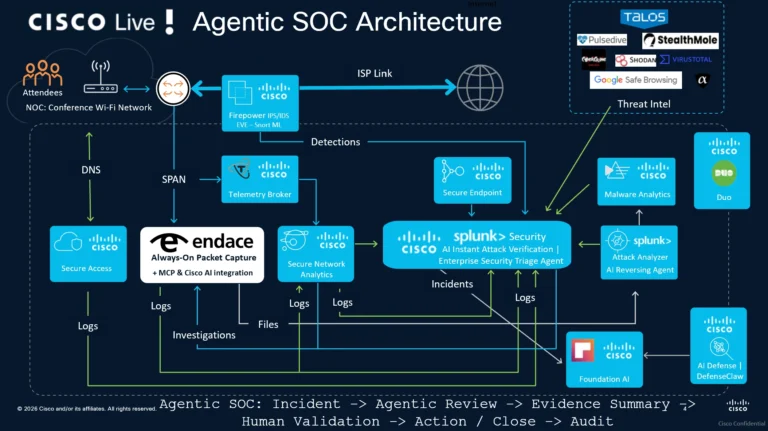
Our Agentic SOC Architecture is a natural evolution of the SOC Architecture we have been deploying for the last several years, heavily leveraging telemetry and insights derived from network data we monitor, analyze and capture throughout each event. We rely on logs generated by Cisco Firepower, Secure Network Analytics, Secure Access, AI Defense, Splunk Attack Analyzer, Secure Malware Analytics, and EndaceProbe (which also generates Zeek logs and reconstructs file content from the packet data it records). Splunk Enterprise Security was the repository for all these logs and data, while EndaceProbe was the repository for full packet data for the entire week of the event.
We implemented a Model Context Protocol (MCP) server for Endace to integrate with Cisco Cloud Control, allowing us to build Agentic AI integrations with Splunk, Cisco XDR and other components of the SOC (see Baz Shaw’s blog for more detail: Cisco Live 2026 – Using LLMs and Endace Full Packet Capture for Incident Response).
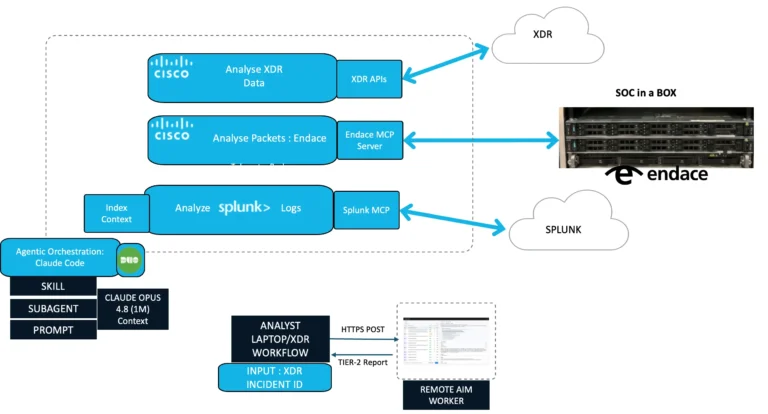
With the Endace MCP server in place, we built a lightweight Agentic Tier-2 SOC analyst that consumes a single XDR incident and investigates it end-to-end. It builds on the agentic capabilities already in our products. Under the hood, it combines the Endace MCP (for packet capture and decode) with a Splunk MCP (for querying the Zeek logs and other indexes) and the Cisco XDR APIs (for incident, asset, and observable context), all orchestrated by a reasoning agent that we tailored with Cisco Live context — the venue’s IP ranges, the Splunk index layout, and the SOC’s rules of engagement. The result is a single entry point: give it an incident ID, and it pulls the XDR context, retrieves the relevant Endace packets, runs targeted Splunk queries, and returns a structured report. (For the full architecture of the tool and how we built it, see the deep-dive: “AIM — Building an Agentic Tier-2 SOC Analyst at Cisco Live AMER 2026.”)
At each SOC event we spend some of our time being curious and threat hunting for suspicious activity. Previously we had seen insecure AD as a serious threat to some attendees at another Cisco Live event, so we decided to take another look, first using humans rather than Agents.
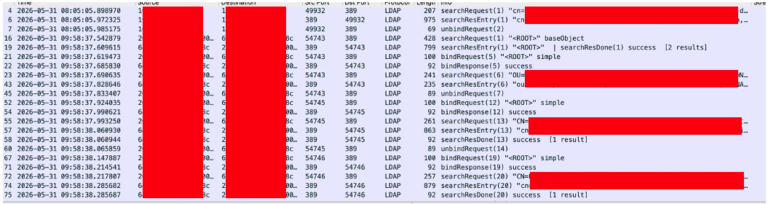
Reviewing the packet data from three days of conference activity, we quickly found several LDAP sessions initiated in the clear by attendee devices. In total, 48 devices were attempting to initiate LDAP binds to external LDAP servers using both IPv4 and IPv6 addresses.
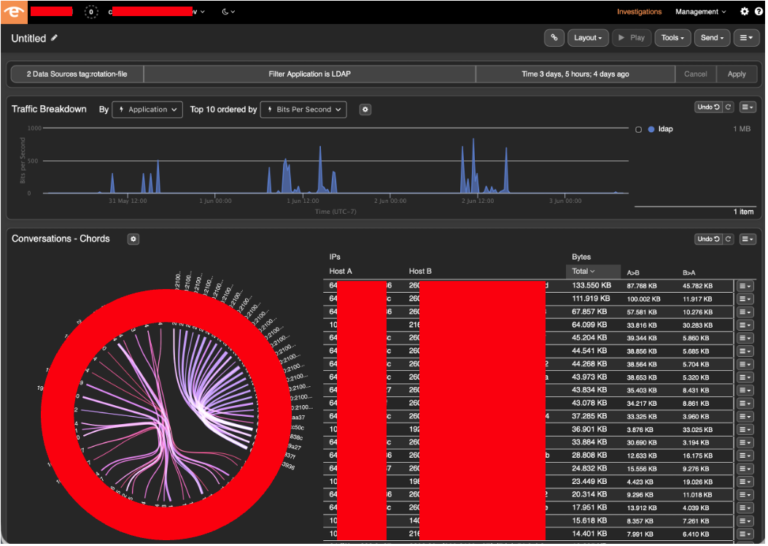
The high-profile organization names found in the LDAP bind requests were particularly concerning. We theorized that the behavior of continuous attempts at anonymous binds may be a sign of SharpHound reconnaissance. This recon, if successful, can result in LDAP enumeration exposing sensitive details that may be used to compromise an organization.
At this point, we decided to use Agentic AI capabilities to investigate and assess this potential threat. Our first step was to create an incident in Cisco XDR. The incident included a description, the incident time, and an IP tuple and port. Then the XDR Attack Storyboard kicked in as the primary agent, delivering an automatic first-pass assessment of the incident. Building on top of that assessment, our Tier-2 agent (AIM) took it further — working the incident in stages and deciding each next step based on what the previous one returned (truly agentic). First, it read the XDR incident context, then pivoted to Endace full packet capture to pull the actual LDAP/389 session (within an analyst-approved 15-minute capture window) and then gathered more supporting evidence from Splunk logs, all autonomously.
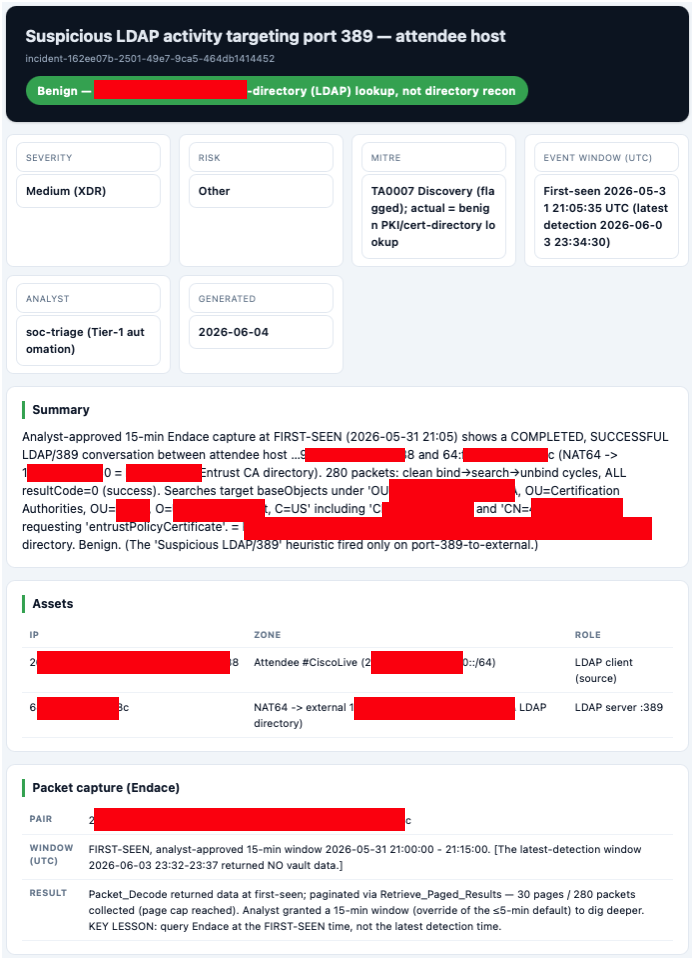
Within a few minutes we were presented with a well-written report that described the incident, data gathered, reasoning, assessment, and disposition along with the next steps. For first-time analysts especially, this was a goldmine — the Agent interpreted the packets on its own, doing the hard part. As SOC analysts, we could review the Agent’s work and take the next steps.
The Agent also produced step-by-step execution logs; every query and decision — so the full reasoning trail can be handed to Tier-3 if escalation is ever needed — showing exactly how it reached its conclusion. It even zoomed out to check other attendees in the later time window: a blast-radius check, done automatically. In this case, the incident was benign, and the recommendation was to close it as a benign/near-miss. Because we provide the Agent with access to Always-On, full packet data, it was able to review all packet data to map out the blast radius entirely and assess all incidents of this threat.
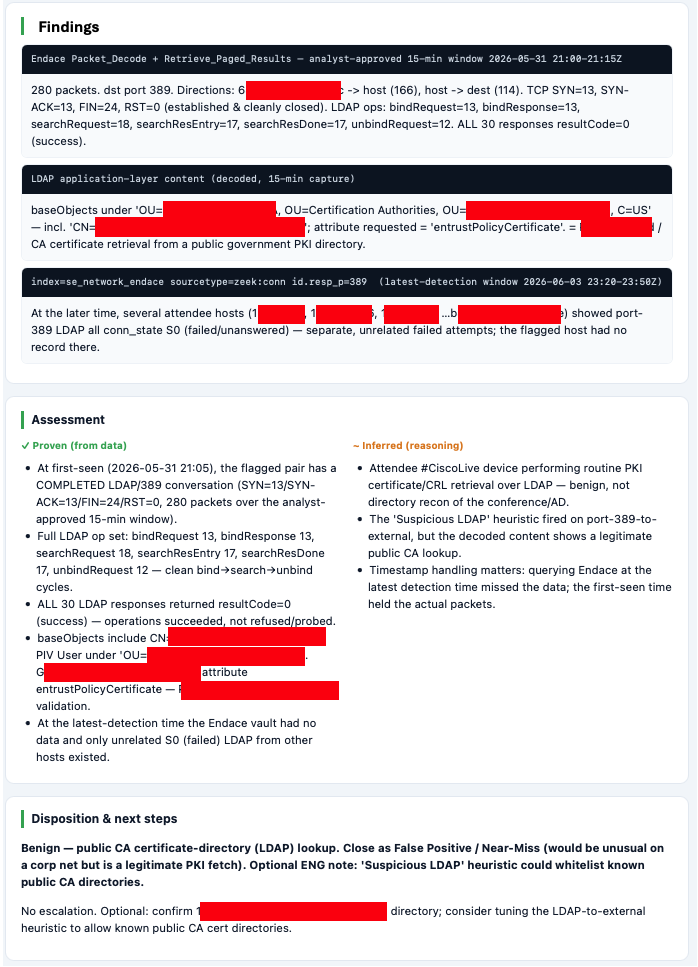
It was particularly encouraging to see the agent first fail, then learn from its mistake. Initially it mixed up “event time” and “first-seen” time. On the first pass, it found no packet evidence because it was searching for the wrong time period. On the second pass, it learned to use the “first-seen” time, found the packet evidence, and wrote that lesson back into its skill file so it would know for next time.
The Agentic SOC, blending Agentic AI built into Endace’s products with custom agentic tools, is a massive boost to productivity and security. The well-reasoned assessments it provides allow us humans to make fast and robust decisions. This, in turn, enables us to focus our precious time on the most serious threats.
Our thanks go to the Cisco SOC team led by @Jessica Oppenheimer and @Ivan Berlinson for the opportunity to integrate EndaceProbes with the Cisco Live Agentic SOC architecture. The SOC team is a collection of Cisco and Splunk experts across many domains who were a pleasure to work and innovate with, and we came away with a great appreciation for the power of the Cisco Security and Splunk tools. The Endace and Cisco teams were able to prove out integration innovations and test them in earnest in a real-world environment in preparation for making them generally available to the market.
Check out the blogs by the engineers who worked inside the SOC at Las Vegas:
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。