


Building on the Cisco Live EMEA SOC, Cisco Live Americas placed the Security Operations Center (SOC) and Network Operations Center (NOC) at the center of the World of Solutions, demonstrating the power of Cisco in bringing Networking, Security and Observability together.
Like any successful SOC, planning starts with a close partnership with the NOC, which deploys a team of engineers to build the network in the weeks ahead of the conference. The Cisco Live Americas Agentic SOC architecture shows how a “One Cisco” approach brings different security tools together to eliminate data silos, in close partnership with the NOC. This directly supported our three missions.
Watch the recording of the live interview at the SOC on Cisco TV.
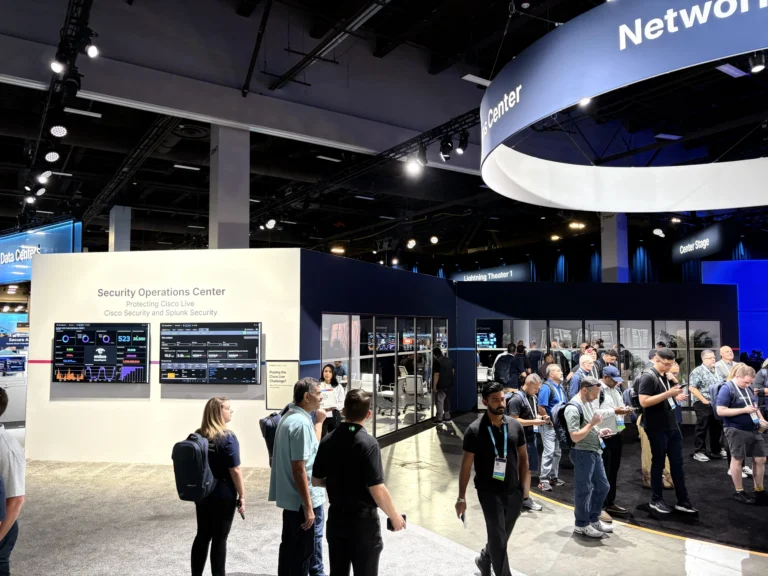
The SOC at Cisco Live was set up in just two days, thanks to lessons learned and continuous evolution. The ‘SOC in a Box’ is on the left.
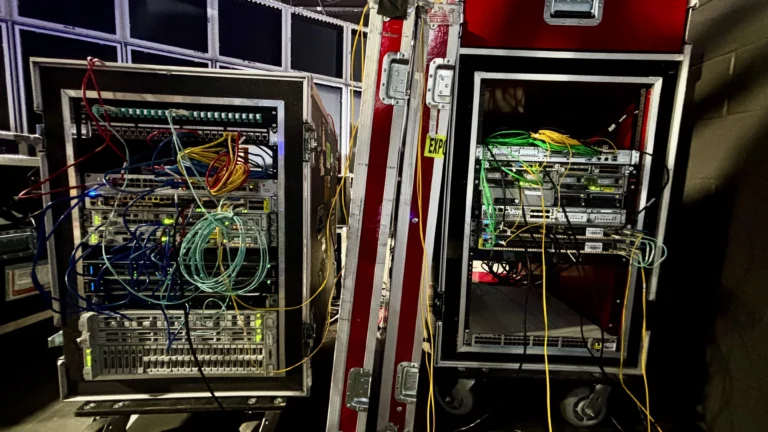
The SOC in a Box also included a UCS M8 with three NVIDIA GPUs, giving the team room to test local and protected AI workflows inside the event environment. That mattered because SOC data can include sensitive details. AI Defense and DefenseClaw provided guardrails and auditability around these workflows, helping the team inspect prompts, responses, and agent actions rather than treating AI as a black box.
We connected developing agentic capabilities into a governed SOC workflow so every incident could be summarized, validated, investigated, and audited with a human still in control.
For Cisco Live AMER, we treated agentic AI as an auditable review layer across the SOC, not as a replacement for analysts. Incidents still started from real telemetry and detections, but agentic workflows helped summarize what happened, identify supporting evidence, recommend next steps, and preserve the reasoning for human review. Analysts remained accountable for closure, escalation, and any action that could affect the event network.
Splunk Enterprise Security served as the evidence and investigation plane. When agentic workflows produced a summary or recommendation, analysts could validate the underlying events, searches, detections, malware analysis, and packet evidence rather than relying on an uncited AI answer. Where possible, agentic workflow activity and guardrail events were made searchable so the team could review not just the conclusion, but how the conclusion was reached.
Cisco XDR provided the incident narrative layer for frontline analysts. Attack Storyboard and Verification helped convert correlated detections into a guided explanation of what happened, which entities were involved, and whether the available evidence supported escalation, closure, or continued monitoring. Every incident could receive agentic review, but agentic review did not mean autonomous response. The workflow was deliberately human-in-the-loop: agents summarized and recommended; analysts validated and decided.
Firepower SnortML and Encrypted Visibility Engine helped answer a critical question in an event SOC: what can the network tell us even when endpoints are unmanaged and much of the traffic is encrypted? These detections gave the SOC high-value signals that could be correlated in XDR and validated in Splunk.
Incidents were investigated in Splunk Security, with threat intelligence provided by Cisco Talos, and licenses donated by alphaMountain, Pulsedive, and StealthMole along with community sources.
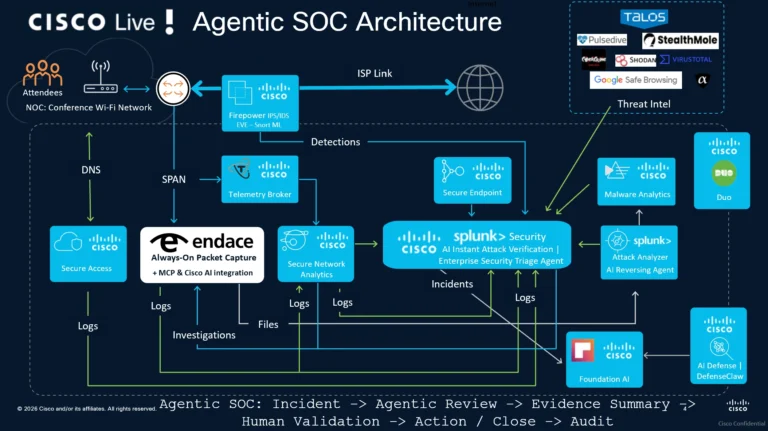
Telemetry creates incidents. Agents accelerate understanding. Splunk grounds the evidence. Cisco XDR guided the incident narrative. AI Defense and DefenseClaw govern the workflow. Humans make the decision. The whole process can be reviewed.
Agentic SOC: Incident -> Agentic Review -> Evidence Summary ->
Human Validation -> Action / Close -> Audit
| Agentic Capability | Question It Helped Answer |
|---|---|
| Firepower SnortML + Encrypted Visibility Engine | What is the network telling us, even through encrypted traffic? |
| XDR Attack Storyboard / Verification | What happened, and does the incident require action? |
| Splunk Enterprise Security Triage Agent | What does the evidence say? |
| AI Studio + Endace | What packet evidence proves or disproves the hypothesis? |
| Splunk Attack Analyzer AI Reversing Agent | What does this file or URL do? |
| Foundation AI with Cisco XDR workflows | How do we summarize and document the investigation? |
| AI Defense + DefenseClaw | How do we inspect, guardrail, and audit agentic workflows? |
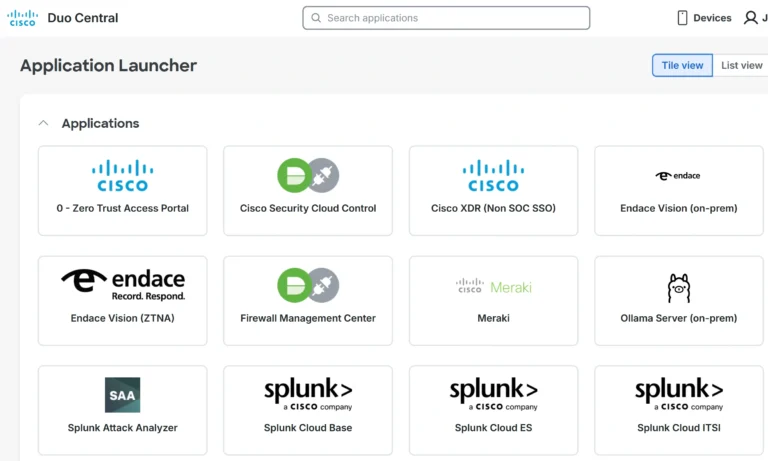
The SOC team used Duo Central for Single Sign-On access to the tools, both on-premises and in the cloud, executing from the first customer experience at Black Hat.
By leveraging cloud-based solutions like XDR and Splunk Cloud, this also minimized the amount of work that was needed in a very tight setup window. Configurations and other data were already ready to go from previous events as well, including dashboards in Splunk. The SOC manager dashboard was used to track status of Agentic AI assisted incident investigations and escalations.
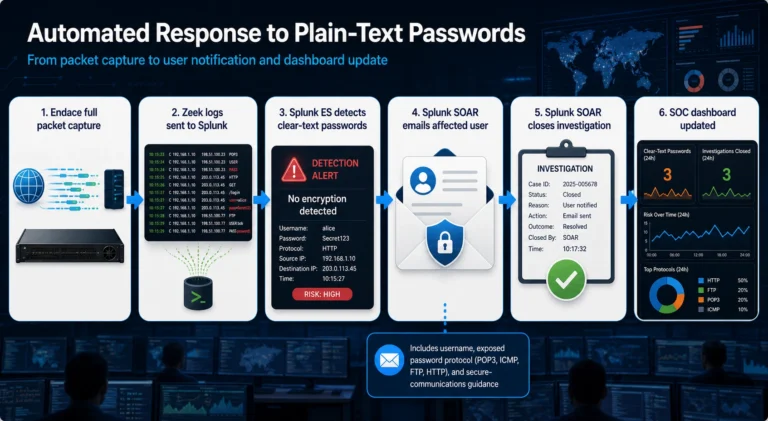
There were some use cases where no human involvement was necessary, such as when an attendee’s device or accounts were found to be compromised or unsecure, the SOC team used automation to notify the attendee with Endace and Splunk SOAR, resolving the Incident without human intervention.
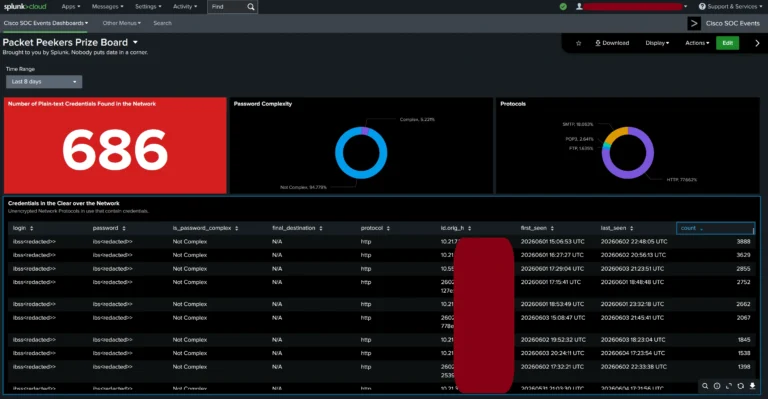
The Splunk Packet Peekers Prize Board was the most popular for attendees to view (and hope their account was not one of the redacted on the dashboard).
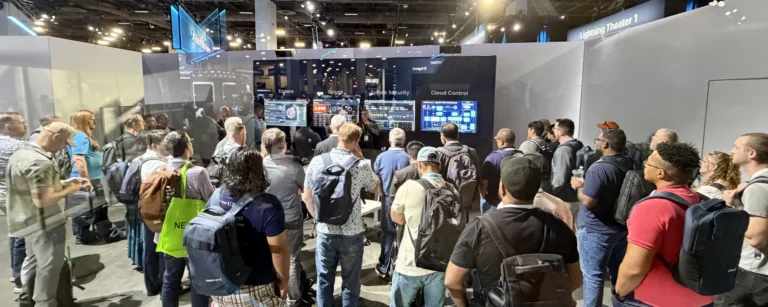
Statistics are always a popular part of the SOC Tours. Below are the stats from this year’s event. In addition, the perimeter firewalls of the NOC blocked over 10 million external attempts to attack the network, with those logs added to the SOC Splunk Enterprise Security platform.
| Year | 2026 | 2025 |
|---|---|---|
| Attendees (Cisco Live) | 20,000+ | 22,000+ |
| Total packets captured (Endace) | 202.9 billion | 99.5 billion |
| Total logs captured (Splunk) | 5.6 billion | 4.5 billion |
| Total sessions (Endace) | 1.74 billion | 1.49 billion |
| Total unique devices | 62,790 (DHCP) | 37,052 (DNS) |
| Total packets written to disk (Endace) | 199 TB – 100 TB IPv6 – 89 TB IPv4 – 4 GB non IP |
78.9 TB (IPv4 only) |
| Total logs written to cloud (Splunk) | 7.4 terabytes (added perimeter firewall logs) | 1.99 terabytes |
| Peak bandwidth utilization (Endace) | 10 Gbps (saturated) | 4.85 Gbps |
| DNS Requests (Cisco) | 270.4 million / 60.1k blocked | 261.3 million / 28.3k blocked |
| Total clear text username/passwords (Endace) | 43,322 | 2,256 |
| Unique devices / accounts with clear text usernames / passwords (Endace) | 686 | 97 |
| Files sent for malware analysis (Endace) | 2.392 million 740,172 file objects reconstructed by Endace – 23,368 sent to Splunk Attack Analyzer – Sent to Secure Malware Analytics |
740,172 file objects reconstructed by Endace – 42,813* sent to Splunk Attack Analyzer – 13.05k sent to Secure Malware Analytics * De-duplication started afternoon of 11 June 2025, as part of tuning |
Check out the blogs by the engineers who worked inside the SOC at Las Vegas:
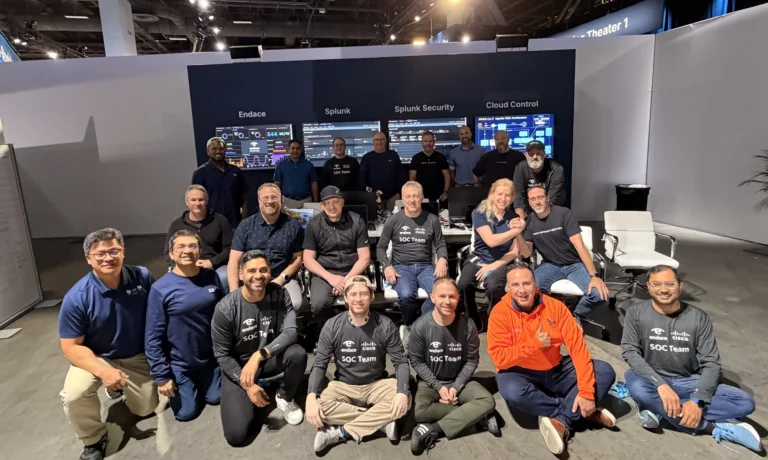
Our thanks to the engineers who made the first Agentic SOC at Cisco Live a success, by protecting the network and educating attendees (and you).
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。