


DNS continues to provide one of the clearest windows into activity across the Black Hat network. Since 2017, Cisco has helped secure Black Hat through DNS-layer visibility and protection, providing the Network Operations Center (NOC) / Security Operations Center (SOC) team with an early vantage point into where devices are attempting to connect.
At Black Hat, however, the value of DNS goes well beyond traditional threat blocking. The conference creates a uniquely noisy environment where security research, demos, pen-testing tools, malware analysis and thousands of attendee devices all generate activity that might look suspicious on a typical enterprise network. DNS telemetry gives analysts an important starting point for separating this expected activity from events that deserve further investigation, while also revealing broader trends in how the network is being used.
Building on the encrypted DNS controls introduced at Black Hat USA 2025, this visibility remains particularly important as encrypted protocols and privacy technologies increasingly obscure traditional network telemetry.
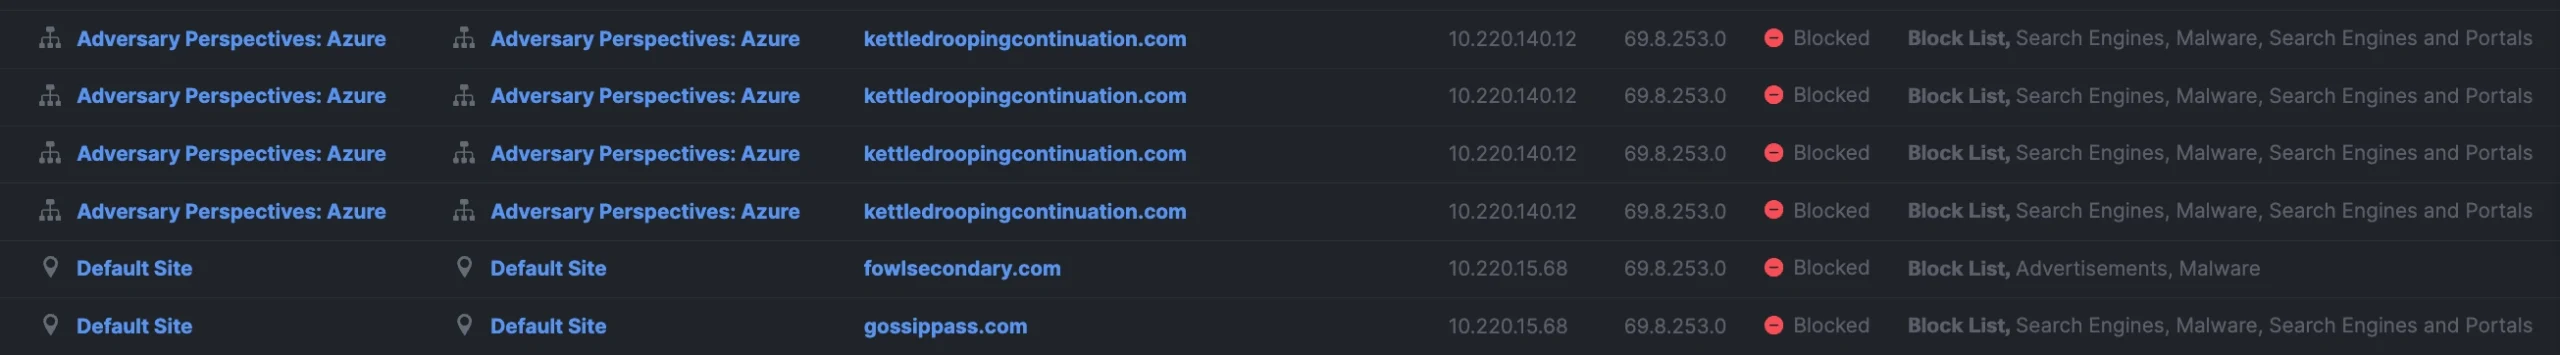
Continuing from last year’s priorities to monitor and block resolutions for domains related to the ApateWeb Potentially Unwanted Program (PUP) delivery and phishing campaign, which uses ‘two/three-name’ domain pattern, we did see some of these destinations blocked to protect attendees.
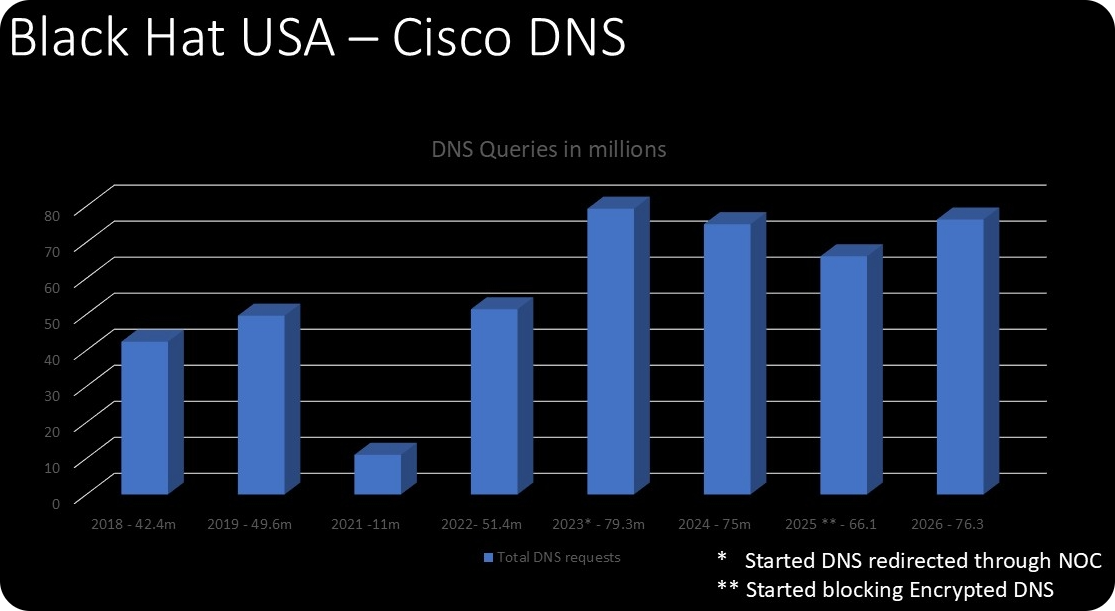
This year, we identified 76,331,133 DNS requests across 1.02 million domains and 1,268 identities, as more attendees connected to the conference network vs recent years. With the increase in DNS requests, we also identified an increase in number of apps:
| 2019: ~3,600 | 2023: ~7,500 | 2026: ~10,800 |
| 2021: ~2,600 | 2024: ~9,300 | |
| 2022: ~6,300 | 2025: ~9,300 |
Secure Access was not merely resolving DNS—it was preventing devices from bypassing organizational DNS inspection through unapproved encrypted resolvers
Cisco classified 8,695 DNS requests as “Hacking.”
A focused set of penetration-testing and research domains generated approximately 5,137 requests, including:
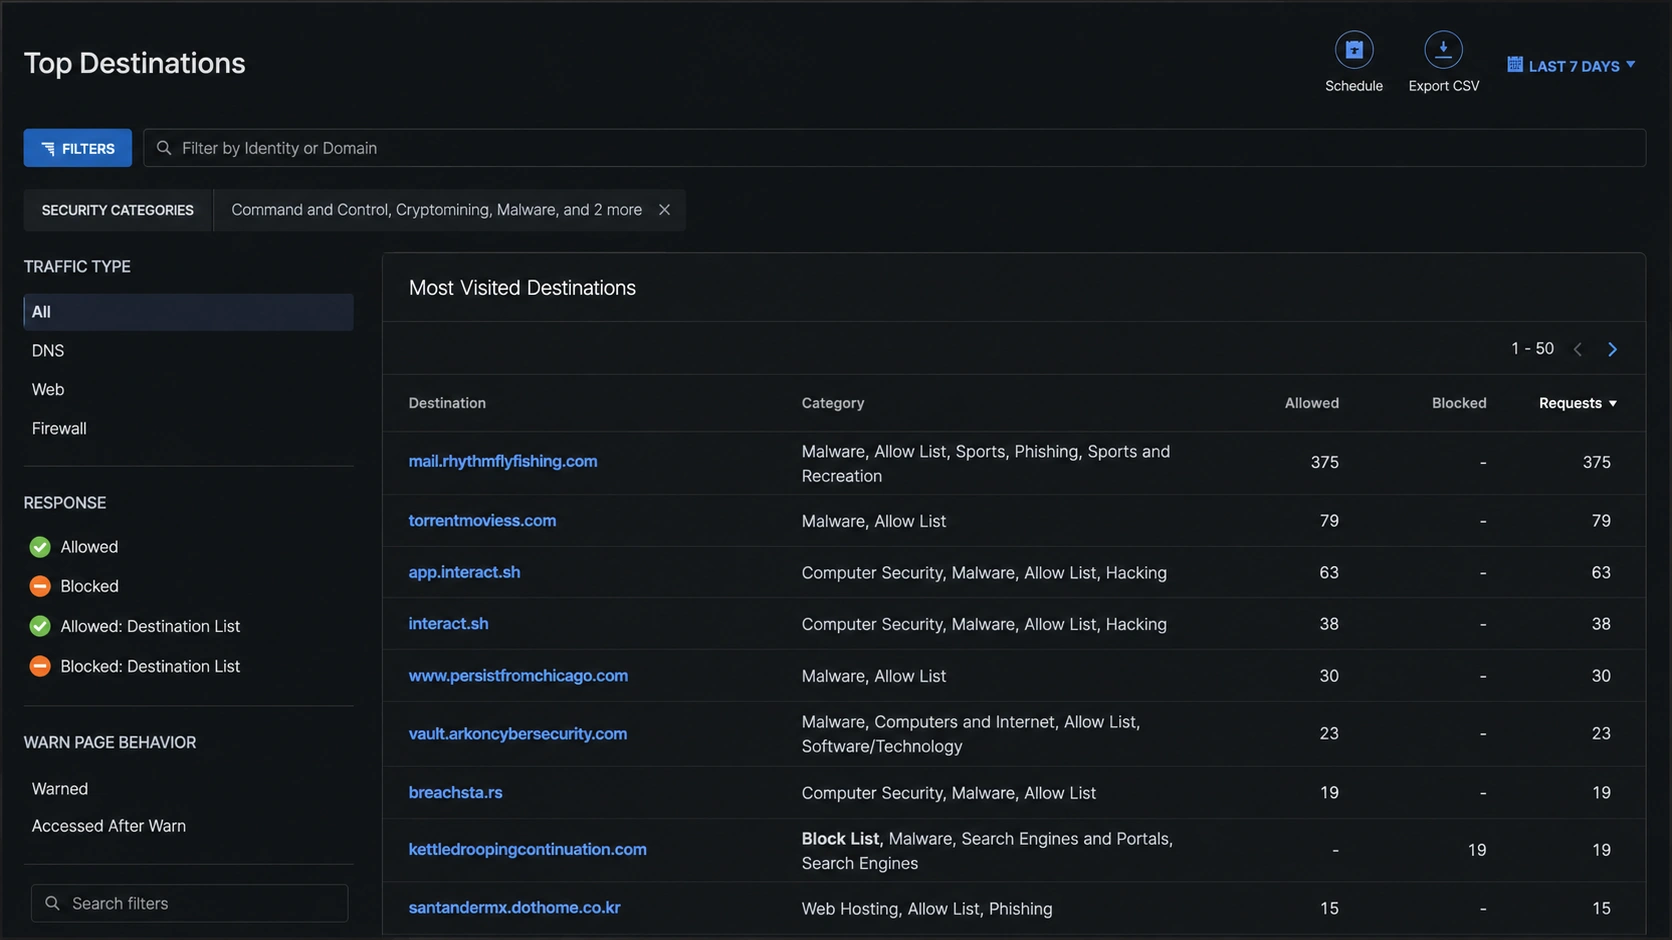
This view highlights the most visited destinations observed through Cisco Secure Access that were classified under security-related categories, including Command & Control (C2C), Cryptomining, Malware, Phishing, and Potentially Harmful content.
Given the security research, demos, training and testing taking place at Black Hat, traffic to many of these destinations was expected and not necessarily indicative of malicious activity.
The growth of Generative AI was clearly visible on the Black Hat network, with Cisco Secure Access identifying nearly twice as many GenAI applications compared to last year. This increase highlights how quickly AI-powered tools are becoming part of the everyday application landscape and reinforces the growing need for visibility and governance around their use.
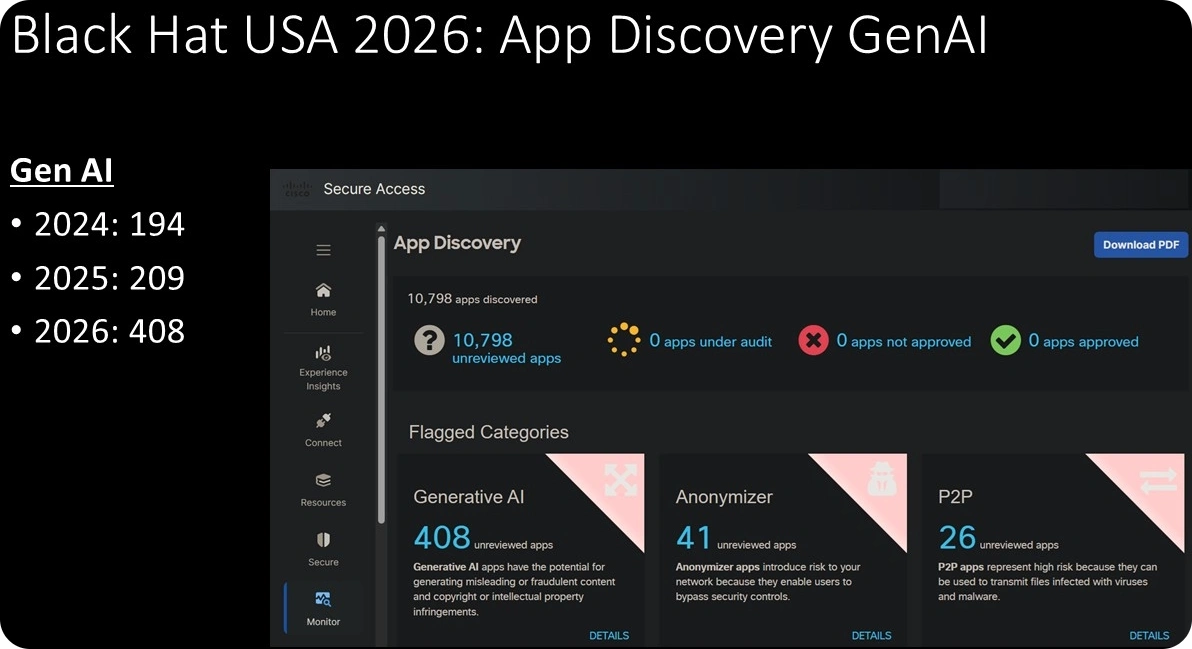
With so many talks incorporating AI subjects, the real-world usage of attendees serves as a metric to measure the increase of adoption and the proliferation of AI tools.
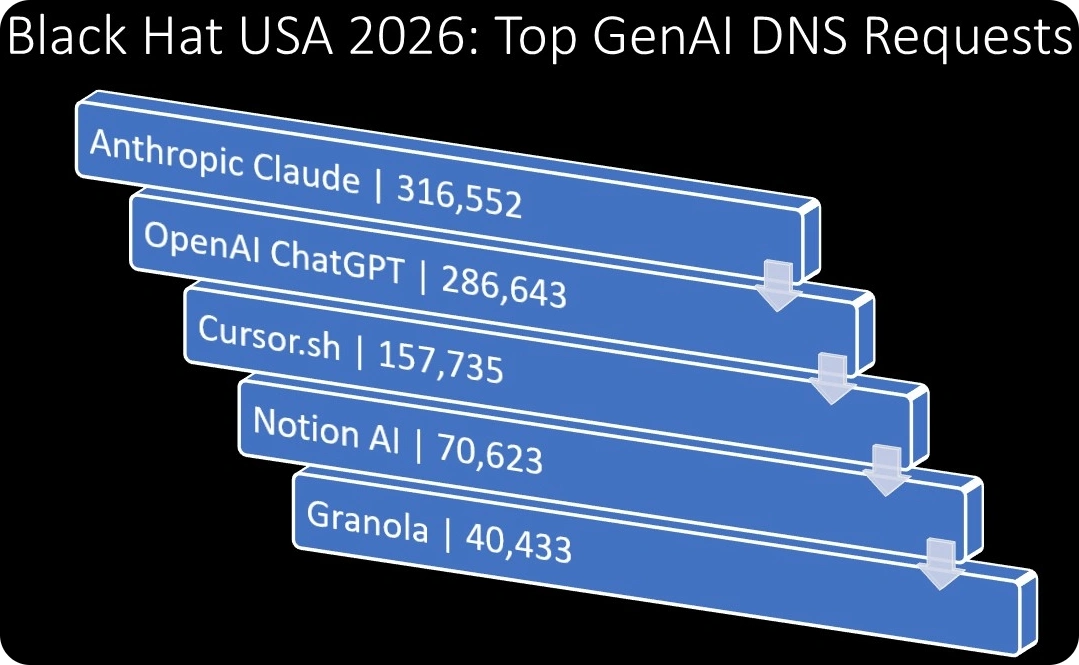
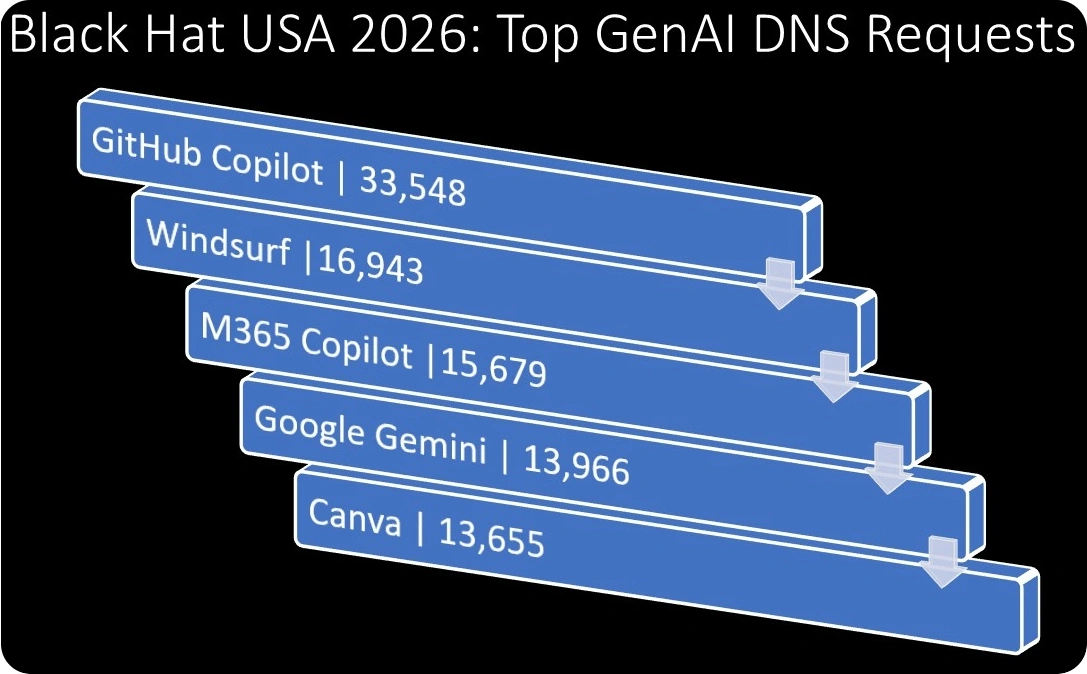
Notable observations:
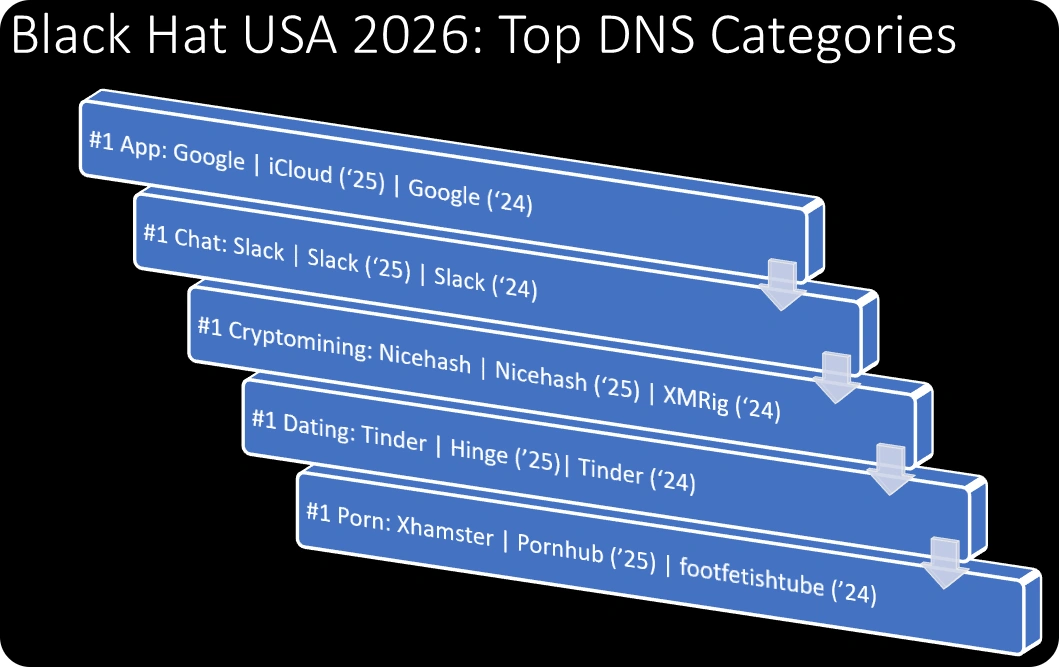
Each year, the NOC leaders give awards for the top requested websites by category. In 2026 we saw Slack hold serve for the top chat app, along with clashes of big names like Apple vs. Google and Tinder vs. Hinge. We’ll present the last matchup with no comment.
DNS is one of the clearest signals a SOC has, especially in an event environment where endpoints are transient, unmanaged, or only briefly connected. Every device needs DNS to find services, reach applications, and communicate outward, which makes DNS visibility a powerful way to identify suspicious domains, command-and-control patterns, newly observed infrastructure, phishing activity, malware callbacks, and policy violations before they become larger incidents.
For the Black Hat NOC/SOC, Secure Access DNS telemetry gives analysts a high-value control point and an investigative starting point. It helps the team protect attendees while preserving the open nature of the network, enrich detections, and support faster human validation with evidence that is easy to correlate across firewall, Zeek, packet capture, malware analysis, and identity context. In modern Security Operations, DNS is not just a network service. It is a security sensor, an enforcement layer, and one of the fastest paths from “something looks suspicious” to “we understand what happened.”
Check out the other blogs from our team at Black Hat USA 2026.
Black Hat is the cybersecurity industry’s most established and in-depth security event series. Founded in 1997, these annual, multi-day events provide attendees with the latest in cybersecurity research, development, and trends. Driven by the needs of the community, Black Hat events showcase content directly from the community through Briefings presentations, Trainings courses, Summits, and more. As the event series where all career levels and academic disciplines convene to collaborate, network, and discuss the cybersecurity topics that matter most to them, attendees can find Black Hat events in the United States, Canada, Europe, Middle East and Africa, and Asia. For more information, please visit www.BlackHat.com.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。