






Crypto agility is the ability to update cryptographic algorithms, protocols, libraries, and implementations while minimizing disruption and avoiding unnecessary replacement of the underlying infrastructure. For networks, that means adopting post-quantum cryptography (PQC) while preserving the ability to accommodate future standards and defenses primarily through software.
This capability matters because networking platforms often take years to develop and may remain deployed for a decade or longer. During that lifetime, algorithms and standards will continue to evolve, while new vulnerabilities and implementation risks may emerge. Infrastructure designed around one point-in-time set of cryptographic requirements can become costly or difficult to update.
The strategic goal, therefore, is not a single cryptographic destination. It is network infrastructure designed to keep evolving.
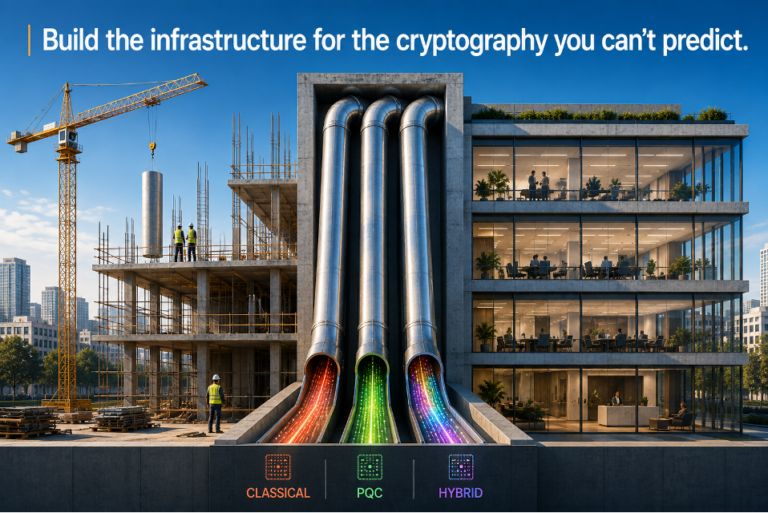
Quantum computing is driving one of the most significant cryptographic transitions in decades. At the same time, artificial intelligence is increasing the speed at which software can be analyzed, vulnerabilities discovered, and attacks developed. Together, they are changing an assumption enterprise infrastructure has relied on for years: that cryptography evolves slowly.
That creates a particular challenge for networking. In our experience at Cisco, developing a new networking platform can take four or more years, while the resulting infrastructure may remain in customers’ networks for a decade or longer. When we started designing our next generation of secure routers, we knew the cryptography they would need throughout their lifetime would continue to evolve.
Designing around a snapshot of cryptography was the wrong objective. We needed to design for continuous change.
For CIOs and CISOs, the implication extends well beyond the current transition to post-quantum cryptography (PQC). Organizations need to adopt new defenses as they become available and keep evolving them as standards, protocols, software, and threats change.
That requires crypto agility.
Think about designing a building before all of its future electrical requirements are known. You cannot predict what equipment its occupants will install ten years from now. But providing sufficient electrical capacity and conduit during construction is far easier than opening the walls every time those requirements change.
Networking platforms face the same challenge.
We cannot predict every cryptographic algorithm or protocol that a router will need throughout its operating life. We can give the platform enough processing capacity and architectural flexibility to accommodate change primarily through software and protocol updates.
PQC readiness addresses the quantum-resistant defenses available at a particular point in time. Crypto agility allows those defenses to keep evolving throughout the life of the infrastructure.
Crypto agility is about adopting the best defenses available today while preserving the ability to adopt better ones tomorrow.
Organizations cannot simply wait for a future “Q-Day.”
Adversaries can capture encrypted traffic today and retain it until a sufficiently capable quantum computer becomes available. For information that must remain confidential for many years, this harvest-now-decrypt-later model makes quantum risk a current exposure.
Consider the WAN. An IPsec VPN generally protects traffic using strong symmetric encryption such as AES, while public-key cryptography is traditionally used to authenticate devices and establish session keys. Those mechanisms also need to become quantum-resistant.
This matters even when applications encrypt their own data. The network still establishes trusted communications between branches, data centers, clouds, partners, and users. Sensitive information continuously crosses infrastructure outside the physical boundaries of the enterprise.
Application encryption protects information within the application context. Quantum-safe networking protects the communications and trust infrastructure connecting that application to everything else.
The WAN is therefore a logical place to begin adopting quantum-resistant defenses progressively as standards, protocols, and software capabilities become available.
NIST standardized ML-KEM for quantum-resistant key establishment and ML-DSA for digital signatures in 2024. That was an important milestone, but standardized algorithms are only one part of the transition.
Those algorithms need to work within protocols and real-world implementations. RFC extensions continue to develop. Interoperability matures. Certification requirements and implementation guidance evolve as PQC moves into production environments.
Infrastructure has to keep pace.
And agility doesn’t stop with the platform. Vendors need to build networking platforms capable of absorbing new algorithms, protocol extensions, and cryptographic implementations without requiring hardware replacement. Customers have to use that agility by adopting new defenses and keeping software current as those capabilities become available.
A crypto-agile platform running software that is years behind does little to improve resilience.
The practical approach is to adopt the protections available now and continue strengthening them as the ecosystem evolves.
AI reinforces the need to move faster.
Increasingly capable models can help researchers analyze large codebases, automate testing, and find software weaknesses faster. The same capabilities can help adversaries scale vulnerability discovery and attack development.
This does not mean AI can suddenly defeat the mathematics behind AES or post-quantum cryptography. The more immediate concern is the software surrounding cryptography: libraries, protocols, implementations, and the systems that depend on them.
AI puts pressure on traditional upgrade cycles by shortening the time between discovering a weakness and developing ways to exploit it.
Quantum is forcing fundamental changes in the cryptography we use. AI is increasing the pressure to respond quickly when implementations and defenses need to change. A networking platform expected to operate for ten years needs to be designed for both.
Customers considering a WAN investment today face a decision similar to the one we faced when designing the platform.
Some organizations will move quickly toward PQC. Others will migrate over several years based on their data, risk profile, regulatory requirements, and the readiness of the broader technology ecosystem. But the network purchased today will likely remain in service through much of that transition—and beyond it.
It should provide the performance needed for PQC, support classical and post-quantum mechanisms during a phased migration, and have the flexibility to absorb new cryptographic requirements primarily through software. That adaptability extends across the platform, from data in transit and device authentication to software integrity and secure boot.
There is an economic reason to think this way as well.
Replacing distributed networking infrastructure involves far more than purchasing another device. It means planning, logistics, testing, maintenance windows, operational disruption, and potentially truck rolls across hundreds or thousands of locations. A platform that costs less at acquisition can become considerably more expensive if changing cryptographic requirements shorten its useful life.
For CIOs, that should change the procurement conversation.
Instead of asking only, “Does this platform support PQC?” ask, “Can this platform keep evolving as cryptography changes?”
Can new algorithms and protocol extensions be introduced primarily through software? Is there enough processing headroom for requirements that were not known when the hardware was designed? Will the vendor continue delivering the software uplifts needed to stay current throughout the expected life of the platform?
Customers should also ask themselves whether their operational model allows them to adopt those uplifts quickly enough to benefit from that agility.
Organizations do not need to predict exactly how cryptography will evolve. Neither did we. And every enterprise does not need to migrate to PQC at the same speed.
But the infrastructure decision comes first.
A network purchased today may still be operating in 2035. During that lifetime, algorithms will evolve, RFCs and protocols will advance, implementation guidance will mature, software weaknesses will emerge, and adversaries will gain new capabilities.
The response cannot be a sequence of forklift upgrades. It has to be continuous: adopt stronger defenses, uplift the software, evolve the protocols, and repeat as the threat changes.
PQC makes that need urgent. AI makes the cycle faster. That is why crypto agility needs to be designed into the network we invest in today.
What is crypto agility?
Crypto agility is the ability to update cryptographic algorithms, protocols, and implementations while minimizing disruption and avoiding unnecessary replacement of infrastructure. In networks, this often means introducing new protections through software and protocol updates.
How does crypto agility differ from PQC readiness?
PQC readiness focuses on an organization’s ability to adopt post-quantum defenses. Crypto agility goes further: it enables infrastructure to continue adapting as algorithms, protocols, standards, and cryptographic requirements evolve.
How can organizations prepare their networks for PQC?
Organizations can inventory cryptographic dependencies, prioritize data that requires long-term confidentiality, and assess whether network platforms support software-based cryptographic updates. They should also plan for a phased migration using classical and post-quantum mechanisms.
Why is harvest-now-decrypt-later a current risk?
Adversaries can retain encrypted information today and attempt to decrypt it when more capable quantum systems become available. Data that must remain confidential for years should receive priority in PQC migration planning.
What should CIOs ask when evaluating PQC-ready networks?
CIOs should ask whether new algorithms and protocol extensions can be added primarily through software. They should also assess processing headroom, support for hybrid cryptographic approaches, interoperability, and the vendor’s software-update commitments.
Learn more about Cisco SD-WAN and how we’re powering AI-driven networks for today and tomorrow.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。