




As is tradition at every Black Hat conference, Day 1 winds down with a quick reality check – what’s done, what’s broken, and what absolutely needs to go live by tomorrow.
Despite a rough start with equipment delays, the foundation was solid. Corelight traffic and detections were already flowing into Cisco XDR using OCSF-based ingestion built at Black Hat Europe 2025. Ivan Berlinson was refining those workflows and dashboards, pushing them toward production-grade quality.
That left an open challenge – and an opportunity. Could we bring in detections from Palo Alto Networks Cortex XSIAM?
The NOC leadership enabled Cisco and other partners to introduce additional pre-approved software and hardware solutions, enhancing our internal efficiency and expanding our visibility capabilities; however, Cisco is not the official provider for Extended Detection & Response, Security Event and Incident Management, Firewall, Network Detection & Response or Collaboration.
The goal Ivan set was deceptively simple:
“See if you can query and ingest analytics alerts from XSIAM into XDR.”
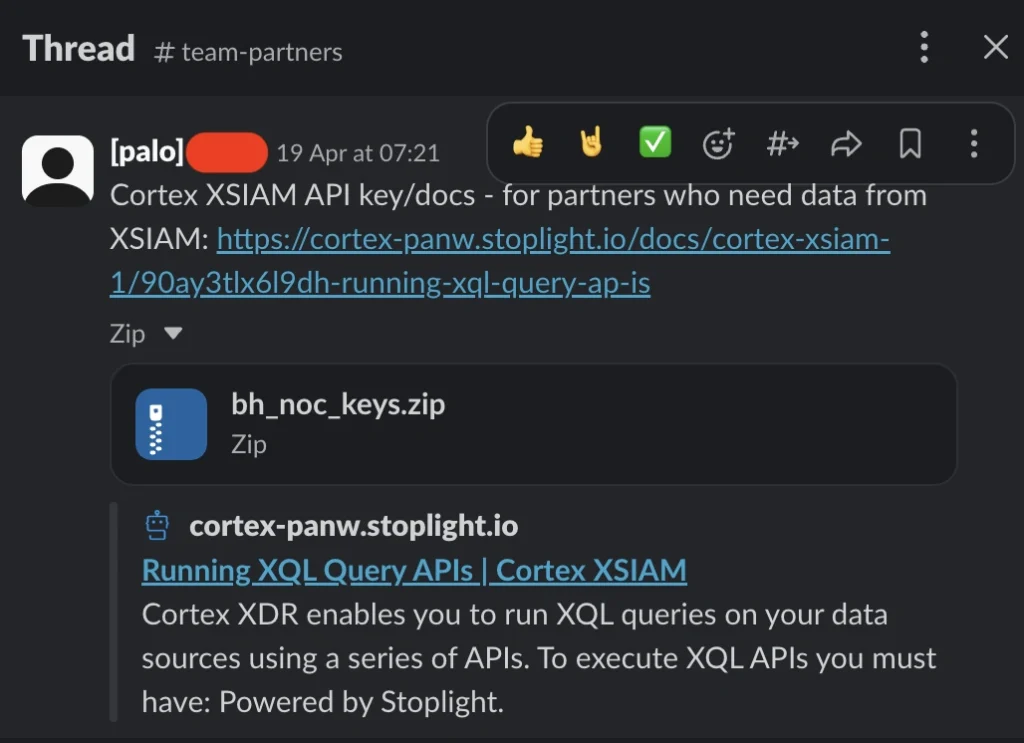
My starting point came from a collaborative Slack post from our friends at Palo Alto Networks, prompted by our SOC leader, who wanted to have visibility into the Endpoint data on critical assets.
I dove into the APIs and started experimenting in Postman. Initial results were…inconsistent. But a quick live discussion with the experts from Palo Alto Networks changed everything – they suggested a more effective query structure, and suddenly we had a way forward.
That’s the lesson Black Hat reinforces every time:
Progress accelerates when you ask the right person the right question.
Once the data started flowing, the next step was building the ingestion pipeline in Cisco XDR Automate. This is where Aditya Sankar stepped in. If APIs got the data, Aditya helped shape the workflow – clean structure, efficient execution, best practices and resolved breaks I would have taken much longer to figure out alone.
Out of the multiple detection types that XSIAM produces, the most relevant datasets at Black Hat were:
We focused on these because they could be ingested as Network-type Custom Security Events. Even this decision was collaborative – balancing feasibility with impact.
Getting alerts was easy. Making them usable turned out to tedious.
Several challenges emerged:
Fortunately, Ivan had already built an atomic action to handle this – taking IPs, zones, and interfaces as input and returning directionality. A perfect example of reusable engineering enabling speed.
By mid-day, I had my first alert flowing into the workflow!
It wasn’t perfect – but it worked.
Ivan’s response was encouraging, but grounded:
“Good start. Now you have to make it ready to be ingested.”
That meant:
And then came the daunting challenge:
“So, I expect a Detection in the Detections page before you go to sleep tonight.”
Guess what, at 10:30 PM, the workflow was complete.
End-to-end. Functional. Producing detections in XDR. No shortcuts, no placeholders.
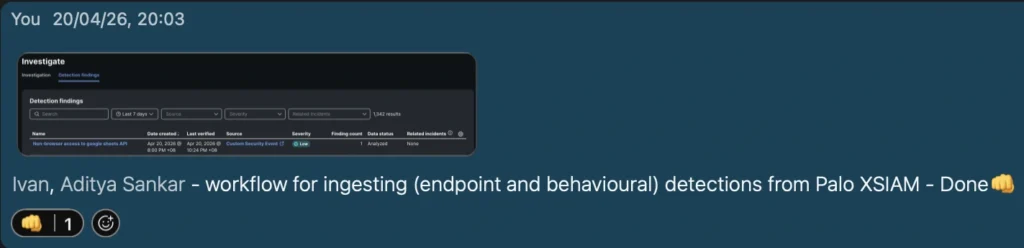
Ivan was right! I didn’t sleep until it was done. And it was absolutely worth it!
The next day, Ivan took the workflow further:
What emerged was a clean, modular, and scalable workflow:
Fetch XSIAM data → Parse → Transform → Ingest into Cisco XDR
The real validation came from the threat hunters.
A correlated incident combining:

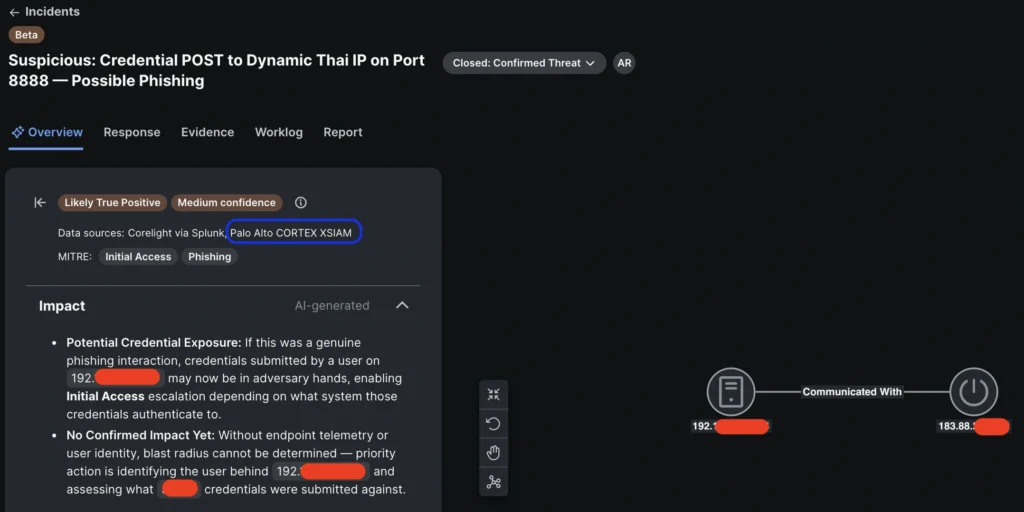
Two different platforms. One unified investigation.
That’s the outcome this entire effort was driving toward. Black Hat isn’t just about tools or technology. It’s about engineers, partners, and ideas coming together – solving problems in real time, under pressure, and learning from each other in the process.
But the best part? Not building it.
Watching someone else use it – and realizing it matters.
US:
https://xdr.us.security.cisco.com/automate/exchange/install/02VOS757W5M8E2FKM02kGVdBT9k8pMqpY0B
EU:
https://xdr.eu.security.cisco.com/automate/exchange/install/02VOS757W5M8E2FKM02kGVdBT9k8pMqpY0B
APJC:
https://xdr.apjc.security.cisco.com/automate/exchange/install/02VOS757W5M8E2FKM02kGVdBT9k8pMqpY0B
Do try it out yourself. Check out the other blogs from our team at Black Hat Asia 2026.
Black Hat is the cybersecurity industry’s most established and in-depth security event series. Founded in 1997, these annual, multi-day events provide attendees with the latest in cybersecurity research, development, and trends. Driven by the needs of the community, Black Hat events showcase content directly from the community through Briefings presentations, Trainings courses, Summits, and more. As the event series where all career levels and academic disciplines convene to collaborate, network, and discuss the cybersecurity topics that matter most to them, attendees can find Black Hat events in the United States, Canada, Europe, Middle East and Africa, and Asia. For more information, please visit www.Black Hat.com.
We’d love to hear what you think! Ask a question and stay connected with Cisco Security on social media.
Cisco Security Social Media
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。