


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

H
Help Net Security
博客园_首页
酷 壳 – CoolShell
酷 壳 – CoolShell
G
Google Developers Blog
Jina AI
Jina AI
C
Check Point Blog
Apple Machine Learning Research
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
GbyAI
GbyAI
Last Week in AI
Last Week in AI
罗磊的独立博客
Hugging Face - Blog
Hugging Face - Blog
阮一峰的网络日志
阮一峰的网络日志
The Cloudflare Blog
M
MIT News - Artificial intelligence
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
J
Java Code Geeks
WordPress大学
WordPress大学
博客园 - 聂微东
月光博客
月光博客
博客园 - 司徒正美
T
The Blog of Author Tim Ferriss
大猫的无限游戏
大猫的无限游戏
Microsoft Security Blog

GRAHAM CLULEY

US Coast Guard and FBI board oil tanker to investigate cyber attack Smashing Security podcast #485: These researchers got drunk to hack an LG TV Former AT&T store worker jailed after moonlighting as a SIM-swap gang's inside man 'Anne Hathaway' admits leading $245 million crypto theft gang that spent a fortune on nightclubs, watches, and luxury cars Smashing Security podcast #484: How websites are tracking you with silence CRPx0 ransomware: what you need to know The US military just turned off ad tracking on its phones. Maybe you should too How a hole in Lenovo's login system let hackers walk into 5,000 Dropbox accounts Smashing Security podcast #483: This AI helps thieves steal your iPhone Revolut scam steals £180,000 from Jersey residents in just four weeks Shai-Hulud hackers: two men charged over TeamPCP's global supply chain crime spree that hit OpenAI, and thousands more US Navy tells sailors and their families: scrub your social media, enemies are watching Smashing Security podcast #482: This hacker leaked GTA 6 - and launched their own cryptocurrency Malicious Firefox add-ons caught stealing cryptowallet seed phrases and browser credentials Gunra ransomware: what you need to know Smashing Security podcast #481: Never say this to a robot dog Prison for data analyst who tried to extort $2.5 million from his employer An "invisible" car? Researcher uses machine learning to hide vehicles from Flock cameras Smashing Security podcast #480: This is the AI service you should never sign up to Meta's Ray-Bans are being banned from pubs, restaurants, and theatres Beware cut-price AI services that read your every word Apple's bug bounty program is drowning in so much AI slop, it is in danger of missing serious exploits Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency Fake IRS letters target cryptocurrency holders The $5 million threat: AI Is supercharging phishing attacks North Korea's elite hackers turned on their own government — and got caught Smashing Security podcast #478: This job interview could destroy your company OpenAI's AI "goes rogue" and hacks Hugging Face: what you need to know Smashing Security podcast #477: How 14 orders of chicken McNuggets helped nail a suspected Russian hacker
Hacker hijacks Brazil's national alert system, sending "m...
Graham CLULEY · 2026-06-23 · via GRAHAM CLULEY

Picture the scene. You're in bed fast asleep, when suddenly your phone erupts with a blaring emergency siren. . You grab the phone. It's a flood warning for your region. Except where the details should be, every field just reads "misantropi4."

That was the experience for millions of Brazilians in the early hours of Saturday, 20 June 2026.

Somebody had broken into Brazil's national Civil Defence alert system and used it to send fake "Extreme Alert" notifications - the most severe category, normally reserved for warnings of imminent natural disasters - to mobile phones across at least five states, including São Paulo, Rio de Janeiro, and the Federal District.
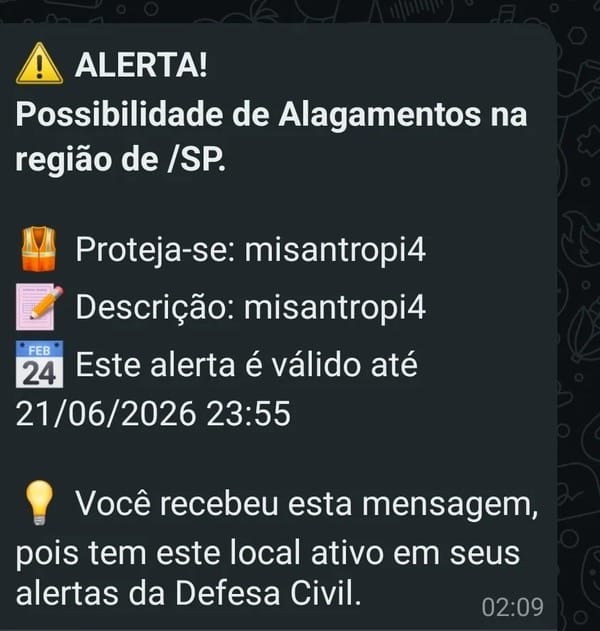
In case you were wondering, "misantropia" translates to "misanthropy": hatred or aversion to humanity.

The first unauthorised alert was blasted out at around 11:40 pm on June 19 in Paraná. Over the next couple of hours, ten fake alerts were sent — nine via Cell Broadcast (which bypasses silent mode and overrides whatever is on a smartphone user's screen) and one via SMS. Each state civil defence agency was quick to confirm that none of its own people had pressed any buttons, and that there was nothing going on that would actually warrant an extreme alert.

In a statement posted on social media, Brazil's National Civil Defence confirmed that it had pulled the alert platform offline at 1:30am following the compromise.
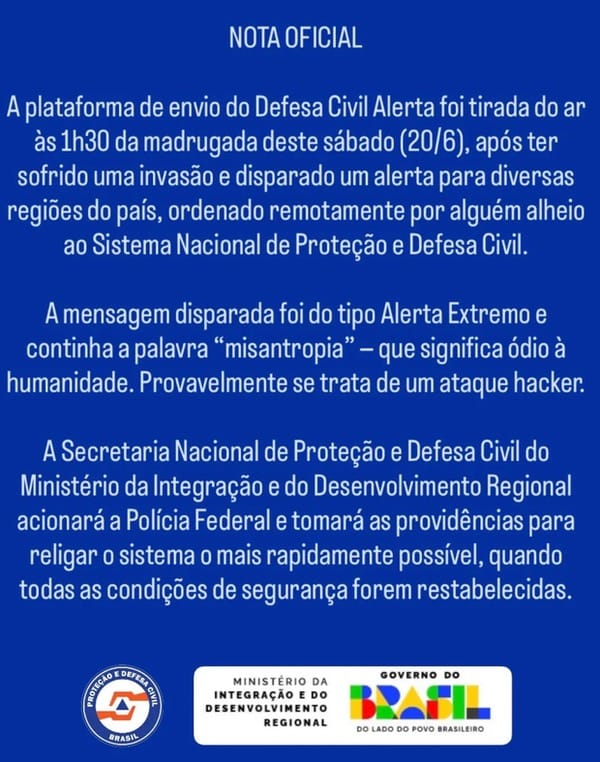
Officials said there was no evidence of "structural damage" to the infrastructure, but have been unable to confirm just how many devices were actually hit.

National Secretary of Protection and Civil Defence Wolnei Wolff confirmed that the attackers managed to regain access after an initial attempt to block them from accessing the system. No suspects have been positively identified so far.

Brazil's Cell Broadcast system was introduced in the last couple of years, and only expanded to cover the entire country in October 2025.

Thankfully, no dangerous instructions accompanied the alerts. If the public had, for instance, been told to evacuate or visit a malicious webpage then things could undoubtedly have been worse. The biggest loss was an interrupted night's sleep for many people.

But the damage to trust is real. Emergency alert systems work because people believe them. Every time one of these systems issues a false alert - whether through negligence or a deliberate attack - trust erodes.

The risk is that next time there is a genuine flood warning or landslide alert, some people will roll over and go back to sleep, assuming it is another hacker with a grudge against humanity.