








Rehub, also known as ReHub or RehubCom, is a Russian-language cybercrime forum founded in August 2025 by a former XSS moderator following its shutdown in the summer of 2025. Rehub dedicates itself to the commercial and marketplace use of ransomware, while its counterpart, DamageLib, serves as a knowledge base archive and exchange.
July 23: XSS is taken down by law enforcement
August 1: XSS moderators launch DamageLib, which completely abandons illicit commerce.
August 10, 2025: Rehub forum is launched by a former XSS moderator, fully embracing illicit commerce.
January 28, 2026: RAMP is seized by law enforcement, with its users migrating to Rehub.
Operating both on Clear Web domains and an onion domain, the forum positions itself as free from state and law enforcement interference, framing existing XSS iterations as compromised. After law enforcement seized the RAMP (RAMP4U) forum in January 2026, Rehub absorbed a significant portion of the displaced cybercriminal community and became one of the primary destinations for ransomware operators.
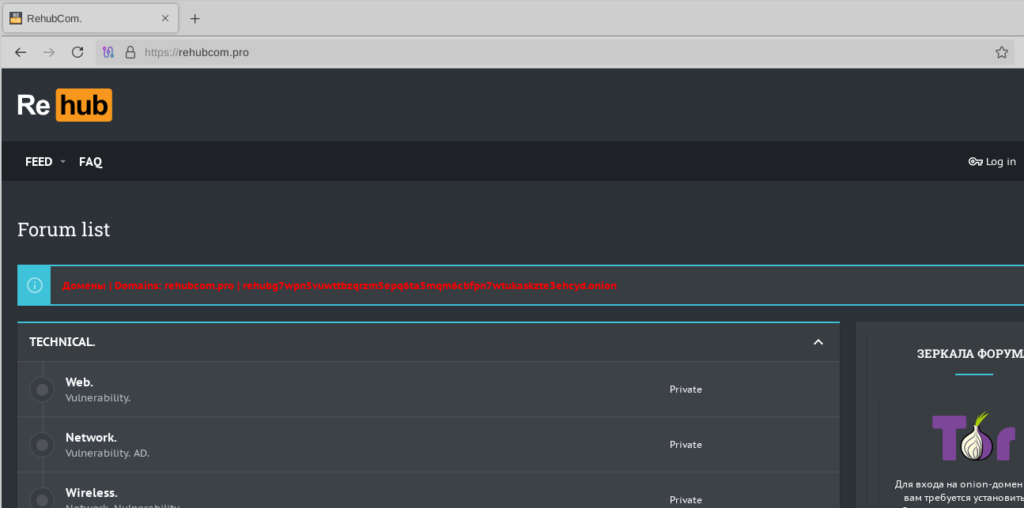
There are many notable threat actors among Rehub moderators and users, including ransomware operators, vendors, and other prominent threat actors active across several illicit communities. Several current or ex-Rehub moderators were also maintainers of other illicit forums such as XSS, DamageLib, and RAMP.
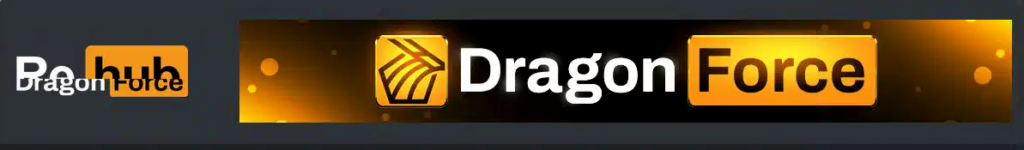
Notably, Ransomware-as-a-Service (RaaS) groups such as DragonForce have maintained an active presence on the platform to market their affiliate programs. Flashpoint assesses that DragonForce is likely the forum’s primary sponsor or partner, as their banner is permanently displayed on the forum’s home page, with both logos merged—similar to its previous placement on RAMP.
Other active RaaS include:
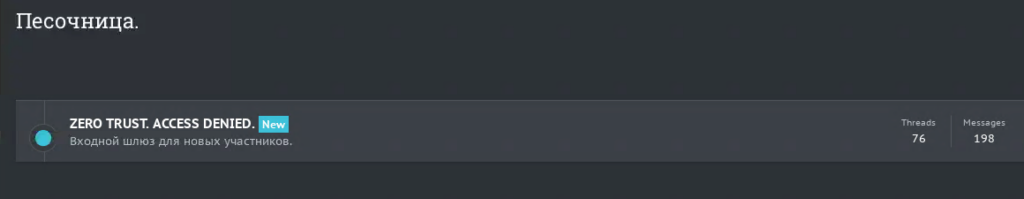
As of July 2026, Flashpoint intelligence observes over 8,300 active users, 15,000 posts, and nearly 3,000 threads. Despite being free to join, Rehub practices a zero trust policy, which was established in mid-April 2026. Under this system, the forum restricts newly registered users from accessing any section other than its Sandbox. Users can also purchase paid upgrades:
Rehub sections, similar to other forums, are grouped by major activities, separating the knowledge base from commerce and from general discussions.
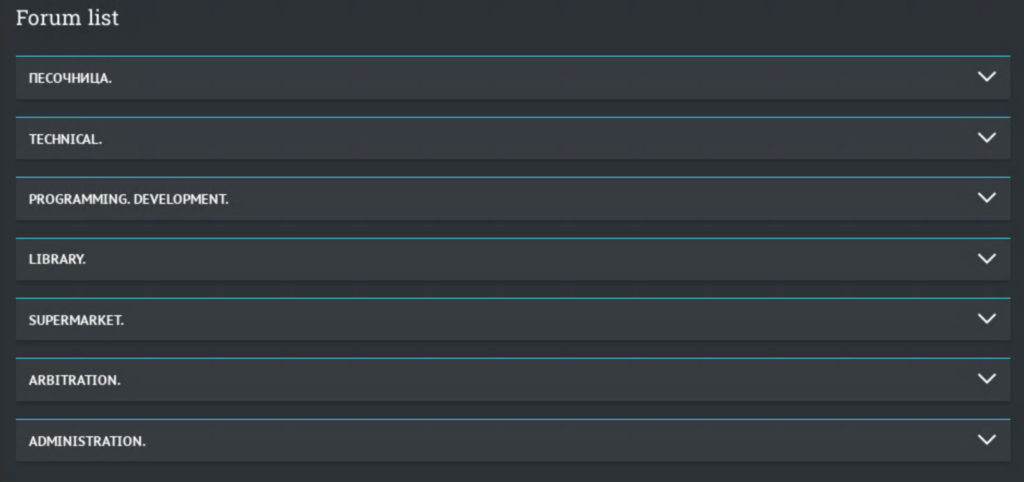
Serves as an entry-level general discussion area and a place for community questions. Main activity consists of queries about operational security, introductory networking, and entry-level fraud or malware logistics.
Covers threads ranging from traditional network infrastructure vulnerabilities to emerging technologies such as AI jailbreaking and deepfake social engineering. Highly active, most communications focus on network vulnerabilities and carding.
This is a dedicated space for discussions on software engineering, system administration, and web optimization within the forum. Primary activities include sharing programming language tutorials, comparing backend technologies, and developing specialized automation tools.
Serves as a repository of resources for the forum, hosting the most threads and community engagement. Users share operational materials, leaked databases, and utility software. Additionally, this section aggregates cybersecurity and tech industry news and articles.
This is a commercial section featuring ransomware affiliate programs, compromised network access, malware tools, stolen financial data, bulk spam infrastructure, forged documents, anonymous hosting, and crypto laundering services.
Serves as the forum’s internal justice system, where members resolve financial disputes and flag scammers. The “Black List” subsection functions as a public record of bad actors and scam sites.
This is where forum staff post announcements, policy updates, and operational notices, including rules, official domains, forum news, moderator applications, and 2FA requirements. Members use it to ask questions, request escrow services, propose features, and raise concerns about the forum’s public image.
Flashpoint will continue to monitor Rehub’s marketplace activity and infrastructure updates. Rehub’s rapid evolution from a post-XSS refuge to a heavily sponsored ransomware marketplaces demonstrates the resilience of the cybercrime ecosystem.
Positioning itself as the primary ransomware marketplace, Rehub has built a high-barrier, high-reward environment for sophisticated threat actors. Request a demo to learn how Flashpoint delivers visibility into illicit communities—empowering security teams to track threat actors, identify exposed assets, and mitigate ransomware risks.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。