








Cloud security posture management (CSPM) is being redefined as two forces collide: Cloud environments are becoming more interconnected—spanning workloads, identities, data, APIs, and development pipelines—while security teams must reduce risk faster with fewer tools and less time.
Frost & Sullivan’s 2025 Frost Radar™ for Cloud Security Posture Management points to a structural shift: CSPM is no longer a periodic compliance exercise. It’s a continuous, risk‑based governance layer inside modern cloud native application protection platforms (CNAPPs). Frost & Sullivan projects the CSPM market will grow from $2.82 billion in 2025 to $6.96 billion by 2030 at a 19.8% compound annual growth rate (CAGR)—reflecting the growing shift from standalone posture tools to integrated, platform‑based approaches.
A cloud native application protection platform (CNAPP) brings together posture, workload protection, identity and entitlement management, and related controls to secure applications across the full lifecycle—from development through runtime operations.
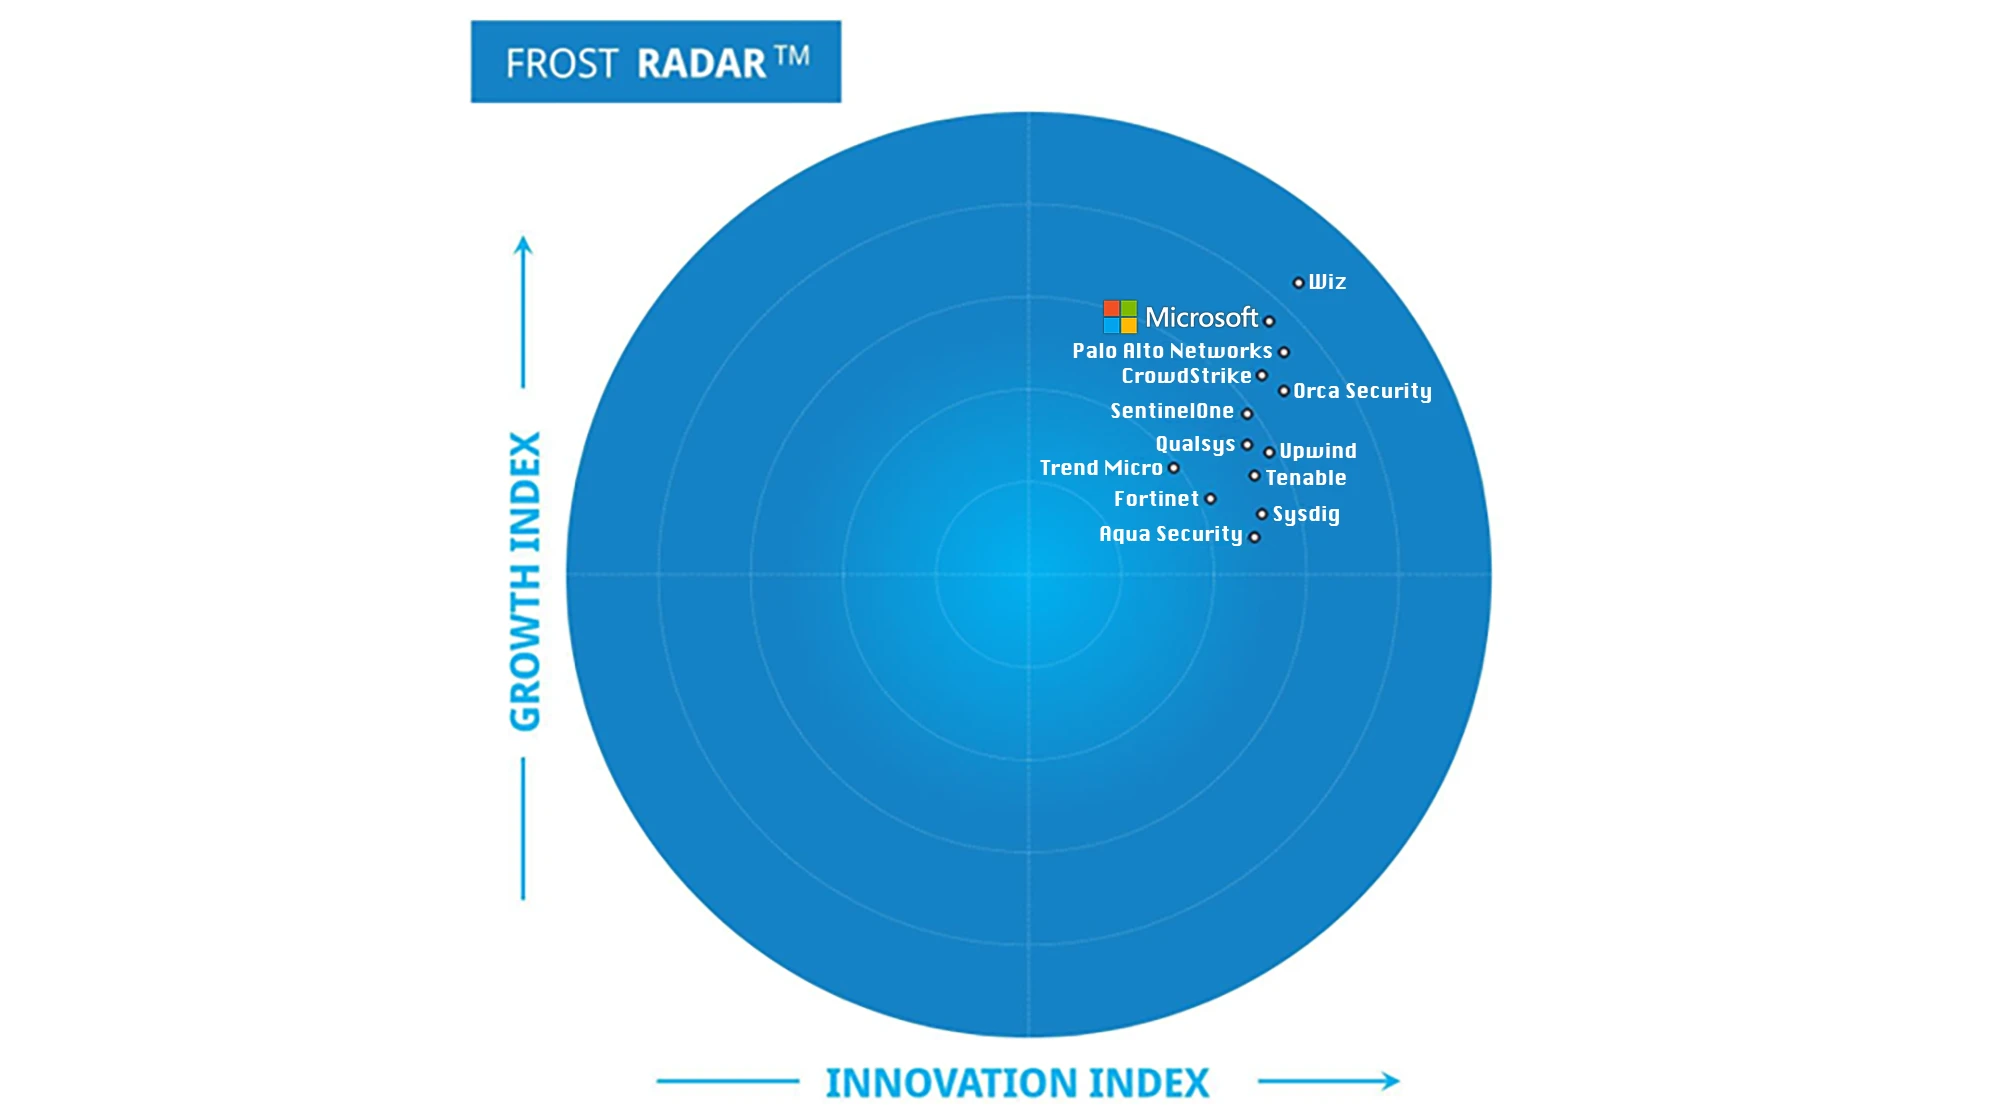
Frost & Sullivan’s analysis also reinforces Microsoft’s position among leading CSPM providers, with strong performance across innovation and growth. This reflects Microsoft’s approach to unifying posture management with workload protection, identity, and data security as part of a broader CNAPP platform—aligning directly with how CSPM is evolving from point-in-time compliance to continuous risk management.
Below are five key insights from the Frost Radar and what they mean for security leaders navigating today’s cloud threat landscape.
Frost & Sullivan research suggests CSPM is evolving beyond a standalone tool focused on configuration hygiene. Instead, it increasingly serves as the entry point and governance backbone for CNAPP—integrating posture signals with workload protection, identity, data security, and security operations center (SOC) workflows.
Modern CSPM solutions are expected to:
Unified visibility that connects posture findings with workload, identity, and data signals—so investigations don’t begin from scratch when posture risk turns into an incident.
Frost notes that by 2030, CSPM is expected to become less a standalone market and more a foundational governance layer inside CNAPP platforms—unifying code‑to‑cloud policy and feeding posture context into runtime and SOC workflows
Compliance coverage is now table stakes. Frost highlights that for organizations to differentiate they need solutions that continuously assess risk, reduce noise, and guide remediation—helping teams focus on the “toxic combinations” that create real exposure.
Leading solutions need to:
Organizations are increasingly using CSPM to drive ongoing risk reduction—with compliance reporting treated as an outcome of stronger controls.
Prioritization that highlights likely cyberattack paths—not just severity scores—so teams can fix what’s exploitable first and minimize false positives.
Security leaders are adjusting how they evaluate CSPM vendors in response to these shifts. Rather than asking how many compliance frameworks a solution supports, they’re looking at whether posture insights can be correlated with identity, workload, and runtime signals to expose exploitable attack paths and guide remediation across developer and SOC workflows. Frost & Sullivan’s evaluation framework reflects this transition—placing greater emphasis on integrated, code to cloud risk management capabilities inside broader CNAPP platforms.
Another major theme in the Frost Radar report is how organizations can embed posture management earlier in the application lifecycle to prevent misconfigurations before deployment—and continuously detect drift as environments change.
The report emphasizes:
By extending posture management into DevSecOps workflows, organizations can reduce remediation costs and prevent risk from reaching production.
Security guardrails embedded in CI/CD pipelines—with clear ownership routing—so remediation happens earlier and doesn’t bounce between teams.
Fragmented tools and siloed data continue to create blind spots across posture, identity, and workload risk—overwhelming SOC teams and reducing operational effectiveness.
As a result, buyers are consolidating point products into integrated CNAPP platforms that correlate posture, workload, identity, and runtime signals.
Platform convergence is reshaping CSPM investment and deployment models:
Consolidation reduces tool sprawl and improves SecOps efficiency.
A platform approach that standardizes policies across clouds and carries posture insights into security operations (SecOps) workflows—improving both signal quality and remediation speed.
Frost highlights AI as both an operational enabler and a new security domain for CSPM.
AI is being used to:
At the same time, CSPM capabilities are expanding into AI workload posture management—covering models, pipelines, and related infrastructure.
AI assisted prioritization and guided remediation—plus posture coverage for AI workloads—so emerging risks such as prompt injection or data leakage are managed alongside traditional cloud risk.
Frost & Sullivan’s analysis underscores that CSPM is no longer about checking compliance boxes—it’s becoming a strategic control layer for managing cloud risk across the entire application lifecycle.
If you’re evaluating CSPM capabilities in 2025–2026, ask:
Frost & Sullivan attributes Microsoft’s leadership in CSPM to its ability to operationalize posture management as part of a broader cloud security platform—aligning with the report’s emphasis on integrating posture with runtime protection, identity, data security, and SecOps workflows across the application lifecycle. These capabilities align with the same governance, prioritization, DevSecOps integration, and lifecycle visibility themes highlighted across the Frost Radar insights above.
Rather than operating as a standalone compliance layer, Microsoft correlates posture data with runtime telemetry and identity signals—integrating findings into developer pipelines and SOC workflows through GitHub, Azure DevOps, and Microsoft Defender XDR. Frost highlights Microsoft’s multicloud visibility across Microsoft Azure, Amazon Web Services (AWS), and Google Cloud Platform (GCP); policy‑as‑code enforcement and CI/CD integration to strengthen shift‑left security; and unified dashboards that carry posture context into investigations and response.
The Frost report also notes Microsoft’s expansion into emerging posture domains—including AI and API posture management—to continuously manage cloud and AI workload risk across the application lifecycle.
To learn more about Microsoft Security solutions, visit our website. Bookmark the Security blog to keep up with our expert coverage on security matters. Also, follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。