





A man has appeared in federal court in Austin, Texas, after being extradited to the United States to face charges related to his alleged role as a key developer of the notorious RedLine malware.
Prosecutors have charged Armenian national Hambardzum Minasyan with conspiring with others to develop and run RedLine, described by the US Department of Justice as "one of the most prevalent infostealing malware variants in the world."
RedLine can steal a wide variety of information from affected computer systems, including account details and passwords saved in browsers, cookies, and payment card information, as well as details about the PCs it has compromised.
The RedLine malware, which has been deployed against systems in more than 150 countries, has been marketed and sold to cybercriminals via subscription on the dark web. It has been commonly used to harvest data from corporations, and is said to have been used by hackers backed by foreign governments to target US critical infrastructure.
Researchers have claimed in the past that a large proportion of stolen credentials sold on the major dark web markets have been obtained through use of RedLine.
RedLine is still in use by cybercriminals, despite the near-fatal blow of "Operation Magnus" - the seizure of infrastructure by international law enforcement in October 2024.
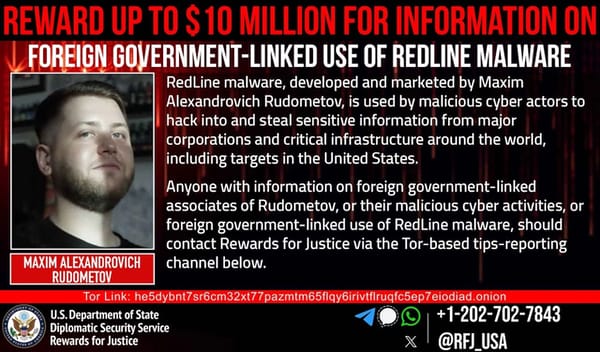
That operation also saw charges filed against Russian national Maxim Rudometov, who is alleged to be another developer and administrator of RedLine, and remains at large.
Last year, the US Department of State offered a reward of up to US $10 million for information about the hackers believed to be behind RedLine malware attacks.
Minasyan is charged by prosecutors with conspiring to commit access device fraud, conspiracy to violate the Computer Fraud and Abuse Act, and conspiracy to commit money laundering. The charges carry a combined potential sentence of up to 30 years in prison.
Specifically, US prosecutors claim that Minasyan registered two virtual private servers and two internet domains, created repositories on an online file-sharing site to distribute RedLine to cybercriminal affiliates, and registered a cryptocurrency account in November 2021 to receive client payments.
He also allegedly offered customer support to the hackers using the malware.
As part of the "Operation Magnus" seizure of RedLine infrastructure in late 2024, investigators recovered a database containing the details of thousands of RedLine clients. This has helped build intelligence about other cybercriminals, and the arrest of Minasyan - almost 18 months later - appears to be a direct result.
As the legal case against Minasyan proceeds, authorities are continuing to urge businesses and individuals to harden their cybersecurity.
The "Operation Magnus" portal remains active at "operation-magnus.com, providing resources for potential victims to check if their credentials were harvested by the RedLine malware.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。