





The volume of vulnerability disclosures is higher than ever, yet most security teams are still struggling to act.
From vulnerability scanners to public sources and AI-accelerated discovery, organizations are often drowning in findings, but lack the context to prioritize what affects their perimeter and is actively being exploited.
Compounding this challenge is the growing issue of unknown and forgotten assets. Up to 95% of a company’s assets change each year, creating critical external blind spots and leaving them vulnerable to attacks on unmonitored infrastructure.
As attack surfaces expand due to cloud adoption, shadow IT, acquisitions, and distributed environments, many organizations struggle to maintain control over what assets they own, what software is running on those assets, and therefore, where exposures exist. You can’t patch what you don’t know is there.
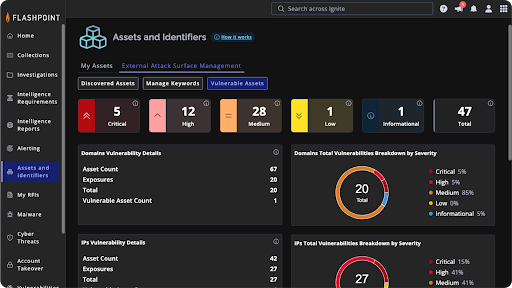
These are the challenges Flashpoint External Attack Surface Management (EASM) is designed to address. With the introduction of EASM in Flashpoint Ignite, organizations can continuously discover internet-facing assets, map them to Flashpoint Vulnerability Intelligence, and prioritize remediation efforts based on actual risk rather than vulnerability volume and severity alone.
“The most effective vulnerability management programs are built on more than vulnerability awareness alone,” said Josh Lefkowitz, Co-Founder and CEO of Flashpoint. “Organizations need to understand where exposure exists within their environment and focus remediation efforts where they will have the greatest impact. Flashpoint EASM helps connect vulnerability intelligence directly to exposed assets, giving security teams a clear path from identification to remediation.”
For many organizations, vulnerability intelligence is no longer the limiting factor.
Security teams have access to more vulnerability data than ever before. They can track newly disclosed vulnerabilities, monitor exploit activity, review KEV catalogs, and identify emerging threats often within hours of disclosure. And Flashpoint customers get the added advantage of learning about vulnerabilities up to 2 weeks faster than NVD, as well as the growing 105K+ vulnerabilities that never make it to public sources.
But understanding whether those vulnerabilities affect assets the organization actually owns remains a challenge. And that challenge exists because asset visibility and vulnerability intelligence often live in separate workflows.
As environments become more dynamic, validating exposure often requires analysts to pivot between scanners, spreadsheets, asset inventories, cloud consoles, and vulnerability intelligence sources.
As a result, organizations must face a growing disconnect between understanding which vulnerabilities are out there vs. whether the organization is actually at risk.
Flashpoint EASM begins by discovering internet-facing assets associated with an organization, giving security teams an attacker’s-eye view of their external perimeter. Using seed domains and IP addresses, it initiates ongoing discovery across the external environment, uncovering infrastructure that often evades internal tracking, including:
Once assets are validated, they are surfaced within Ignite and automatically correlated with Flashpoint Vulnerability Intelligence, including pre-NVD findings, KEV intelligence, and proprietary vulnerability coverage beyond public sources. Teams receive alerts when new assets are discovered and when newly identified vulnerabilities affect monitored assets. For a full walkthrough of the workflow, see the Flashpoint EASM product update.
Not every vulnerability on your attack surface demands the same response. Flashpoint EASM helps teams cut through the noise by combining asset exposure with intelligence on what attackers are actively exploiting, so remediation efforts focus on the vulnerabilities that create meaningful risk.
Rather than focusing on vulnerability severity alone, security teams can now prioritize based on actual exploit activity targeting their attack surface. Flashpoint EASM provides the clarity needed to make that shift.
As attack surfaces continue to evolve, organizations need full attack surface visibility, intelligence on what attackers are exploiting, and an efficient path to remediation.
By connecting Flashpoint Vulnerability Intelligence directly to their exposed assets, organizations can move from reactive investigation to having confidence that their external perimeter is continuously monitored and de-risked.
Learn more about Flashpoint External Attack Surface Management and request a demo.
What is External Attack Surface Management (EASM)?
External Attack Surface Management (EASM) helps organizations discover, monitor, and assess internet-facing assets that could be exposed to attackers.
This includes domains, subdomains, IP addresses, cloud infrastructure, internet-accessible services, and other externally exposed assets that may introduce security risk.
By continuously monitoring these assets, organizations can better understand their external attack surface and identify exposures that require remediation.
How is Flashpoint EASM different from traditional asset inventories?
Traditional asset inventories, CMDBs, and internal scanners often depend on manual updates and may not reflect the full scope of an organization’s internet-facing environment.
Flashpoint EASM continuously discovers external assets and maps them to Flashpoint Vulnerability Intelligence, helping organizations identify exposures that may otherwise remain difficult to track through static inventories alone.
Why is attack surface visibility important?
As organizations adopt cloud services, acquire new businesses, deploy new applications, and support distributed environments, external attack surfaces change constantly.
Without continuous visibility, security teams may struggle to identify unknown assets, shadow IT, forgotten infrastructure, or newly exposed services that increase organizational risk.
How does Flashpoint EASM help prioritize remediation?
Knowing a vulnerability is severe is only half the picture. Flashpoint EASM correlates discovered assets with our proprietary vulnerability intelligence, including KEV data and pre-NVD findings, so teams can prioritize based on the severity of vulnerabilities present on their actual attack surface.
What vulnerability intelligence is included?
Flashpoint EASM integrates directly with Flashpoint Vulnerability Intelligence, including:
This allows organizations to understand both exposure and vulnerability relevance within a single workflow.
Does Flashpoint EASM support continuous monitoring?
Yes. Once assets are discovered and validated, Flashpoint EASM continuously monitors the external attack surface for newly identified assets, vulnerable software, exposed services, and relevant vulnerability findings.
Teams can receive alerts when new exposure risks are identified.
How does Flashpoint EASM reduce alert fatigue?
Traditional vulnerability programs generate large volumes of findings without clarity on whether those assets are actually owned or exposed. Flashpoint EASM’s triage inbox lets teams accept true assets and reject noise, ensuring alerts are scoped only to infrastructure the organization actually owns.
Who should use Flashpoint EASM?
Flashpoint EASM is designed for security teams responsible for:
It is particularly valuable for organizations seeking to connect vulnerability intelligence to real-world asset exposure and remediation priorities.
How does Flashpoint EASM work with Flashpoint Vulnerability Intelligence?
Flashpoint EASM extends the value of Flashpoint Vulnerability Intelligence by helping organizations understand where vulnerable assets exist within their external environment.
Rather than viewing vulnerability intelligence and attack surface visibility separately, organizations can use both capabilities together to identify exposure, prioritize remediation, and reduce risk more effectively.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。