











We are excited to share that Microsoft has been named a Leader in The Forrester Wave™: Extended Detection and Response Platforms, Q2 2026. Microsoft ranked the highest of any vendor evaluated in the Strategy category and is the only vendor to receive the highest score in Vision. Microsoft also received the highest possible scores across the current offering criteria of identity detection, cloud detection, SIEM replacement, Threat Intelligence, Threat hunting, Administrative controls, and Training.
In the report, Forrester writes that “Microsoft articulates a compelling vision to build a Frontier approach to security, bringing people and AI together while the platform continuously shields against and disrupts attacks.”
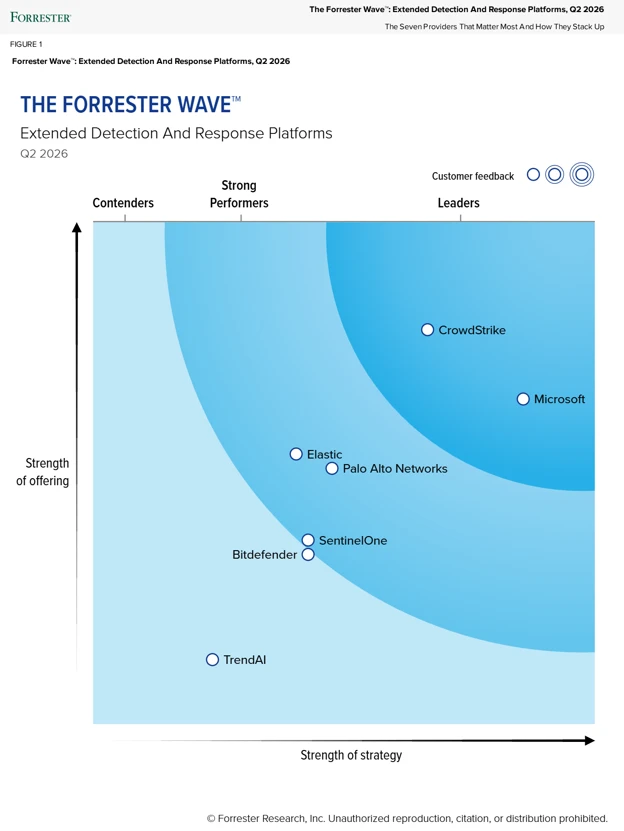
That recognition reflects how Microsoft sees the next phase of XDR evolution. As cyberattackers use AI to scale and accelerate their campaigns, defenders need more than correlated signals. They need a system that brings together data, people, and workflows so security can operate with the same speed and coordination.
At Microsoft, XDR is that foundation. It connects signals across identities, endpoints, email, software as a service (SaaS) apps, and cloud workloads into a shared layer of context bringing together the signals, workflows, and actions security runs on.
That foundation extends directly into how protection and operations are delivered. Microsoft Defender’s native capabilities continuously shield against attacks with built-in, system-level defenses, while embedded agents help triage alerts, hunt for threats, and deliver intelligence in the flow of work. The result is a shift from fragmented response to coordinated, system-level defense—where decisions, actions, and protection move together by default.
Attack disruption is one of the clearest expressions of that vision today. It uses cross-domain signals and AI to stop multi-stage cyberattacks like ransomware and adversary-in-the-middle attacks while they are active and unfolding.
Forrester specifically notes attack disruption in the report, “As well as its roadmap, it (Microsoft) has built unique features, like automatic attack disruption, to help deliver on its vision.”
Threat intelligence is a brand-new evaluation criterion in this Wave and Microsoft earned the highest possible score. This reflects a broader shift: intelligence is no longer a bolt-on, but fundamental to how modern XDR platforms detect, prioritize, and disrupt cyberattacks.
Microsoft Threat Intelligence is built on a broad vantage point, analyzing 100 trillion signals each day. That intelligence is delivered directly into the analyst experience, which provides context on threat actors: their motivations and tactics appear inside incidents, alongside affected assets, and tied to response actions.
The intelligence is built into detections, attack disruption, hunting, and AI that helps analysts make sense of what they’re seeing. It’s also continuously informed by Microsoft’s global security research teams tracking nation-state actors, ransomware groups, and emerging cyberthreats, which brings frontline insight directly to defenders.
We believe Microsoft’s ranking as a leader in this report is a reflection of the pace of innovation across the Defender portfolio over the past year. Highlights include:
Adaptive defense to contain active attacks: Attack disruption now expands autonomous protection to predict and shield against a threat actor’s next move during active cyberattacks. It acts just in time to defend against common attacker tactics such as group policy objects (GPOs), Safeboot, and identity compromise, with new controls that now include device isolation.
Native protection across cloud, identity, and SIEM: Microsoft delivers differentiated protection across cloud and identity by natively harnessing signals from Azure and Microsoft 365 coverage. Combined with Microsoft Sentinel’s powerful security information and event management (SIEM) and threat hunting capabilities, this foundation goes beyond detection, enabling disruption of attacks directly within the SOC for critical data sources including Amazon Web Services (AWS), Okta, and Proofpoint, fundamentally turning your SIEM into a threat protection solution.
Microsoft Security Copilot alert triage agent: Security Copilot agents in Defender help security operations center (SOC) teams investigate faster, automate response, and prioritize high-risk cyberthreats. Microsoft recently extended the Security Copilot alert triage agent to cloud and identity, extending assistive and autonomous AI to two of the most critical attack surfaces security teams defend every day. By helping analysts triage alerts faster, surface high-value context, and move more quickly from signal to action, these new capabilities strengthen the SOC where speed and precision matter most. That momentum reinforces that Microsoft received the highest possible scores in both identity detection and cloud detection.
Securing local AI agents: Microsoft recently announced endpoint security for local AI agents at Microsoft Build 2026. Defender helps security teams gain visibility into AI agents running on devices, assess exposure across identities and resources, block malicious activity in real time, and investigate agent activity through Advanced Hunting.
Being named a Leader in The Forrester Wave™: Extended Detection and Response Platforms, Q2 2026 reinforces Microsoft’s commitment to helping defenders stay ahead of modern cyberattacks. We believe this recognition reflects the strength of our vision, the breadth of our protection across identities, endpoints, email, cloud, and applications, and our continued investment in bringing people and AI together in the SOC.
As the threat landscape continues to evolve, we remain focused on helping customers investigate faster, respond more effectively, and strengthen their security operations with an integrated platform built for today’s cyberattacks.
To learn more about Microsoft Security solutions, visit our website. Bookmark the Security blog to keep up with our expert coverage on security matters. Also, follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity.
Forrester does not endorse any company, product, brand, or service included in its research publications and does not advise any person to select the products or services of any company or brand based on the ratings included in such publications. Information is based on the best available resources. Opinions reflect judgment at the time and are subject to change. This report is part of a broader collection of Forrester resources, including interactive models, frameworks, tools, data, and access to analyst guidance. For more information, read about Forrester’s objectivity here .
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。