

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

MongoDB | Blog
MongoDB | Blog
B
Blog
Y
Y Combinator Blog
大猫的无限游戏
大猫的无限游戏
aimingoo的专栏
aimingoo的专栏
B
Blog RSS Feed
博客园 - Franky
V
V2EX
IT之家
IT之家
WordPress大学
WordPress大学
博客园 - 三生石上(FineUI控件)
J
Java Code Geeks
F
Fortinet All Blogs
I
InfoQ
云风的 BLOG
云风的 BLOG
腾讯CDC
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
月光博客
月光博客
让小产品的独立变现更简单 - ezindie.com
N
Netflix TechBlog - Medium
宝玉的分享
宝玉的分享
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
P
Proofpoint News Feed
Microsoft Security Blog

Microsoft Security Blog

Microsoft named a Leader in the 2026 IDC MarketScape for MDR/MXDR for the Enterprise  | Microsoft Security Blog DeadLock ransomware: Breaking down a Rust-based encryptor with decentralized recovery infrastructure | Microsoft Security Blog ​​Microsoft named a Leader in the KuppingerCole Leadership Compass for Cloud Native Application Protection Platforms (CNAPP) | Microsoft Security Blog From open lures to cloaked gates: How a macOS ClickFix campaign learned to hide | Microsoft Security Blog ChainDrop supply chain compromise: Anatomy of a self-propagating worm | Microsoft Security Blog Advance Zero Trust for AI: New tools and guidance to secure AI agents and DevSecOps | Microsoft Security Blog 128 Seconds to disruption: Microsoft Defender stops ransomware at QNET  | Microsoft Security Blog CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential theft | Microsoft Security Blog ​​​​What’s new in Microsoft Security: July 2026 | Microsoft Security Blog ​​Better security starts with better questions | Microsoft Security Blog Rethinking security for the age of AI - The Official Microsoft Blog Enhancing AI security through global AI red teaming | Microsoft Security Blog Email threat landscape: Q2 2026 trends and insights | Microsoft Security Blog Real world incident response: Microsoft and AXA XL strengthen cyber resilience | Microsoft Security Blog Microsoft at Black Hat USA 2026: Defending trust in the age of AI and supply chain attacks | Microsoft Security Blog ACR Stealer: Two observed intrusion chains amid increased threat activity | Microsoft Security Blog Least privilege for AI agents: Identity, access, and tool binding | Microsoft Security Blog Unpacking the AsyncAPI npm supply chain compromise and import-time payload delivery | Microsoft Security Blog Turning threat intelligence into decisive action with Defender Experts | Microsoft Security Blog Defending SaaS-based applications against ShinyHunters OAuth abuse | Microsoft Security Blog Microsoft Entra ID security updates: Passkeys are the default authentication method in Entra ID | Microsoft Security Blog Securing our future: July 2026 progress report on Microsoft's Secure Future Initiative | Microsoft Security Blog GigaWiper: Anatomy of a destructive backdoor assembled from multiple malware | Microsoft Security Blog Protecting Microsoft at AI speed: How SFI proactively hardens our cloud   | Microsoft Security Blog 5 insights from Frost & Sullivan’s 2025 Frost Radar™ for Cloud Security Posture Management | Microsoft Security Blog Improving security posture across the Microsoft partner ecosystem | Microsoft Security Blog Microsoft named a leader in the Frost Radar for cloud and application runtime security | Microsoft Security Blog Accelerating the quantum-safe timeline | Microsoft Security Blog ​​What’s new in Microsoft Security: June 2026 | Microsoft Security Blog Securing AI agents: When AI tools move from reading to acting | Microsoft Security Blog
What’s new, updated, or recently released in Microsoft Se...
Alym Rayani · 2026-05-01 · via Microsoft Security Blog

New capabilities in Microsoft Agent 365; new Microsoft Defender and GitHub integration

At Microsoft, security innovations are purpose-built to help every organization protect end-to-end with the speed and scale of AI. Our vision is simple: security should be ambient and autonomous, just like the AI it protects.

In a world where AI agents can act autonomously to take action, access data, and interact across systems, every organization should have the confidence that their security posture can scale and keep pace with their AI investments. Microsoft is focused on helping organizations gain visibility into what their agents are doing, governance over what they’re allowed to do, and protection against emerging threats. With an AI-first, end-to-end security platform grounded in Zero Trust for AI, fueled by more than 100 trillion daily threat signals1, and shaped by the Secure Future Initiative, security and IT teams can harden their security posture with protection that is continuous, intelligent, and built for the agentic era.

In the Loop is a new series from Microsoft Security that delivers timely news and updates to the global security community. Today’s edition spotlights the latest capabilities designed to help security and IT teams secure their AI agents, secure their foundations, and defend against threats in real time with the powerful combination of agents and experts.

New Microsoft Defender capabilities in Agent 365 tooling gateway

Detect, block, and investigate threats to AI agents

Get started ↗

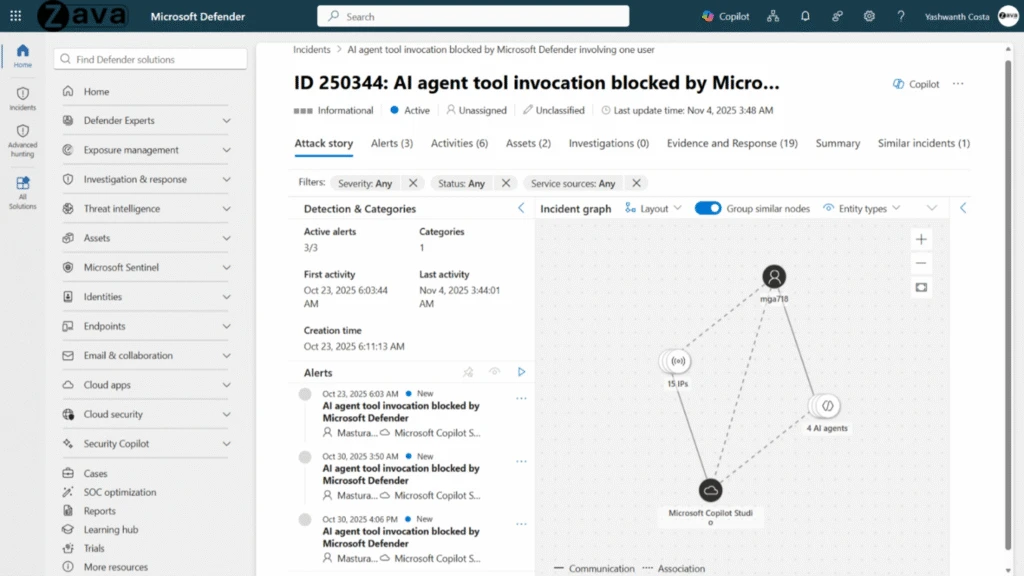
The Agent 365 tooling gateway gives security teams the visibility and control they need to detect and respond to threats that target agentic workflows. New Microsoft Defender capabilities, now available in preview, enable security teams to detect, block and investigate anomalous behavior of their agents. Near real-time protection leverages webhooks to evaluate the actions an AI agent attempts to detect and block malicious or risky activities before they’re executed. Read more and get started.
AI-powered Defender and GitHub solution helps protect from code to runtime

Microsoft Defender for Cloud integration with GitHub Advanced Security, now generally available, provides unified security visibility across the development lifecycle. This integration automatically maps code changes to production environments, prioritizes security alerts based on real runtime context, and enables coordinated remediation workflows between development and security teams. Teams can track vulnerabilities from source code to deployed applications, focus on the security issues that affect production workloads, and take advantage of AI-powered remediation tools to speed resolution.2 Get started today and watch the video.

New demo: Run a data security investigation in Microsoft Purview

Step into the role of a data security analyst and see how Microsoft Purview Data Security Investigations helps you identify investigation‑relevant data, analyze it using AI‑powered deep content analysis, and mitigate sensitive data risks—all within a single, integrated solution. Follow the end‑to‑end investigation journey in this hands‑on demo.

In the demo, you’ll learn how to:

  • Proactively assess data security risk across your data estate.
  • Reactively investigate data involved in security incidents, such as breaches, leaks, fraud, or bribery.
  • Visualize risk using the data risk graph, which shows correlations between sensitive content, users, and activities.

Stay In the Loop

Microsoft Security continually ships meaningful innovations across our portfolio and research-driven insights and reports for the security community. In the Loop posts are your reliable source of what’s new across Microsoft Security and what it means for your security strategy. Check back for the next drop and connect with us at Microsoft Build, June 2-3, 2026 in San Francisco, to hear directly from Microsoft Security experts, learn more about today’s releases, and more.

To learn more about Microsoft Security solutions, visit our website. Bookmark the Security blog to keep up with our expert coverage on security matters. Also, follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity.


1Microsoft Digital Defense Report 2025, Safeguarding Trust in the AI Era

2GitHub Advanced Security Integration with Microsoft Defender for Cloud, Microsoft Defender for Cloud | Microsoft Learn