











As organizations scale AI and agents across environments, security teams need protection that covers every surface. The Microsoft vision is simple: security should be ambient and autonomous, just like the AI it protects. This month’s updates help security and IT teams strengthen identity and multicloud foundations, protect data wherever it lives, and secure the developer workflows powering AI innovation. Here’s what’s new:
Codename MDASH is a multi-model agentic scanning system designed to discover, validate, and help remediate software vulnerabilities across complex environments. MDASH orchestrates a panel of specialized AI agents that reason through proprietary code and systems, helping security teams surface elusive vulnerabilities quickly and systematically. For example, when security teams use MDASH to scan a complex application, it can identify and validate a previously undetected vulnerability in the underlying code and systems, and route it into Microsoft Defender workflows and engineering pipelines for remediation. This closed loop connects discovery, validation, and remediation across the Microsoft stack. Sign up to follow codename MDASH and join the private preview to surface and validate hard-to-find vulnerabilities with multi-model AI.
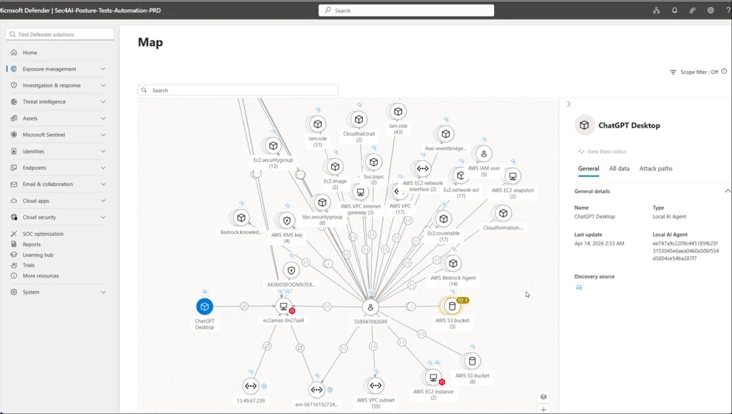
Microsoft Defender now discovers more than 25 types of local AI agents and Model Context Protocol (MCP) servers across managed Windows and macOS devices. Defender also protects at runtime: if a developer using a popular coding agent like GitHub Copilot Command-Line Interface (CLI) or Claude Code is targeted by a prompt injection attempts, Defender detects and blocks it before the malicious action executes. From there, security teams can investigate agent exposure across their environment with Advanced Hunting. These capabilities are now in preview.
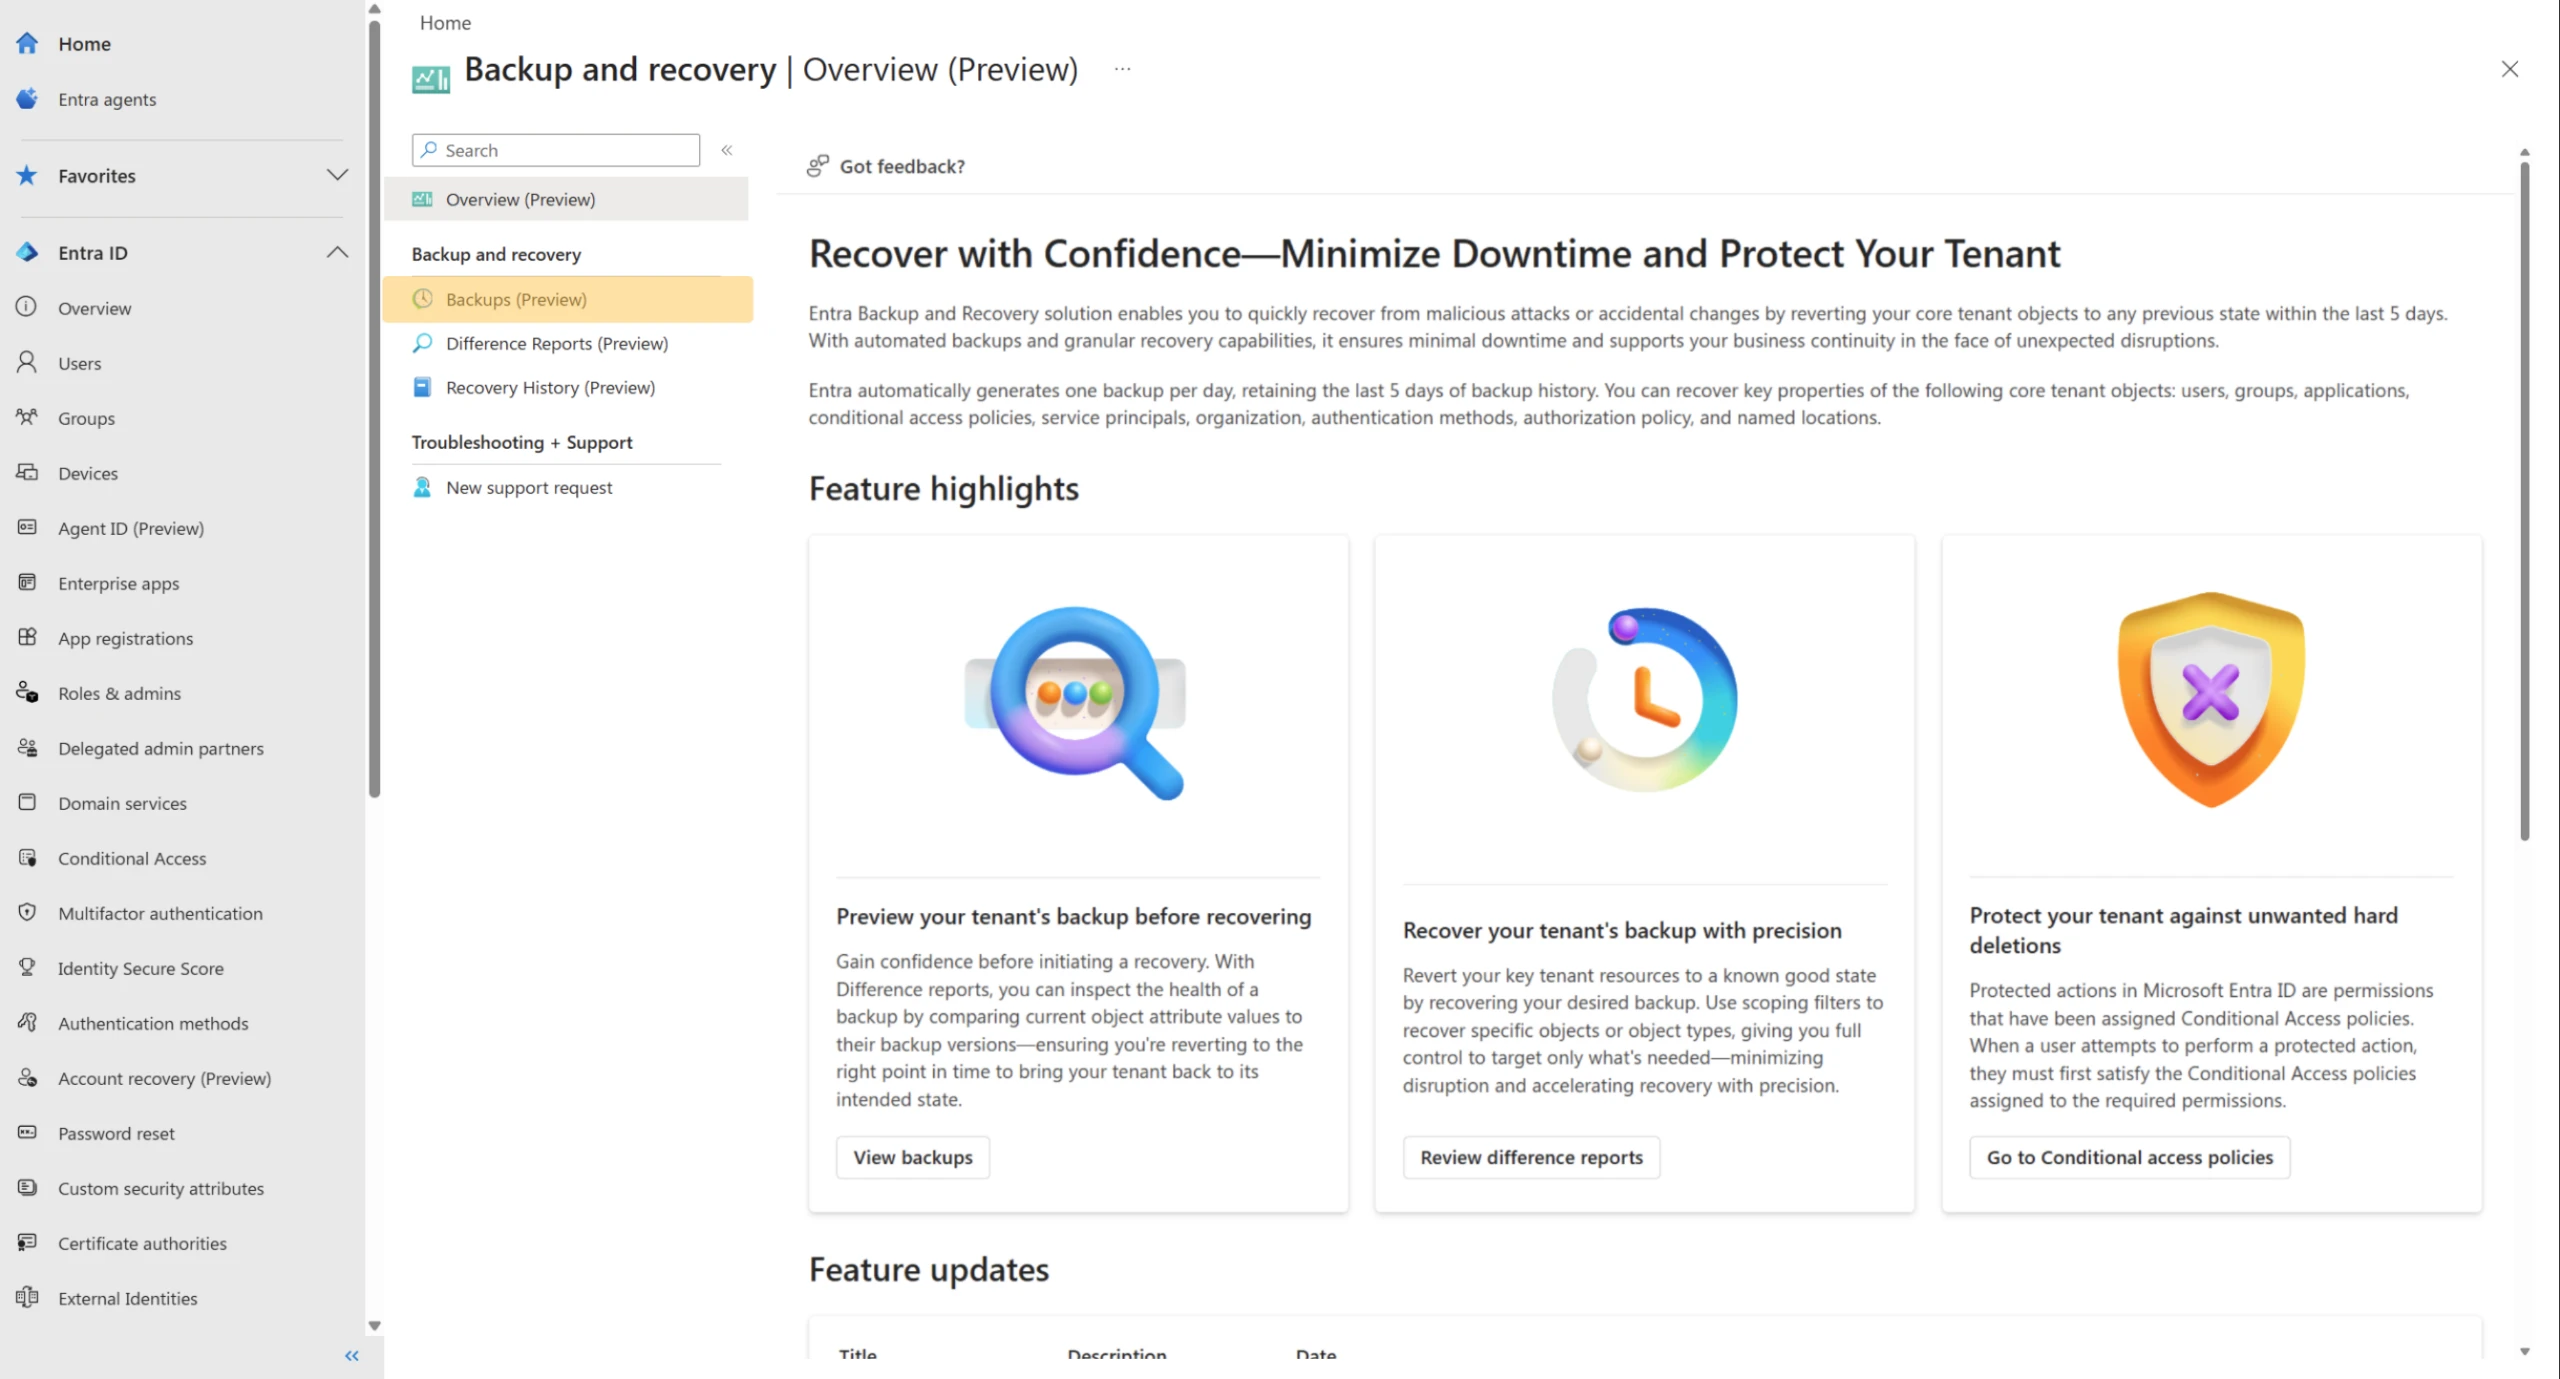
Microsoft Entra Backup and Recovery is now generally available, delivering Microsoft-managed, always-on backups native to your environment that are protected from deletion or modification. Security teams gain clear visibility into what changed across their tenant and can back up core directory objects, compare and restore to previous timestamps, and configure Conditional Access policies to protect against permanent deletion. Together, these capabilities protect your tenant, helping you minimize downtime and recover quickly from accidental changes and security compromises. Strengthen identity resilience with rapid recovery capabilities in Microsoft Entra.
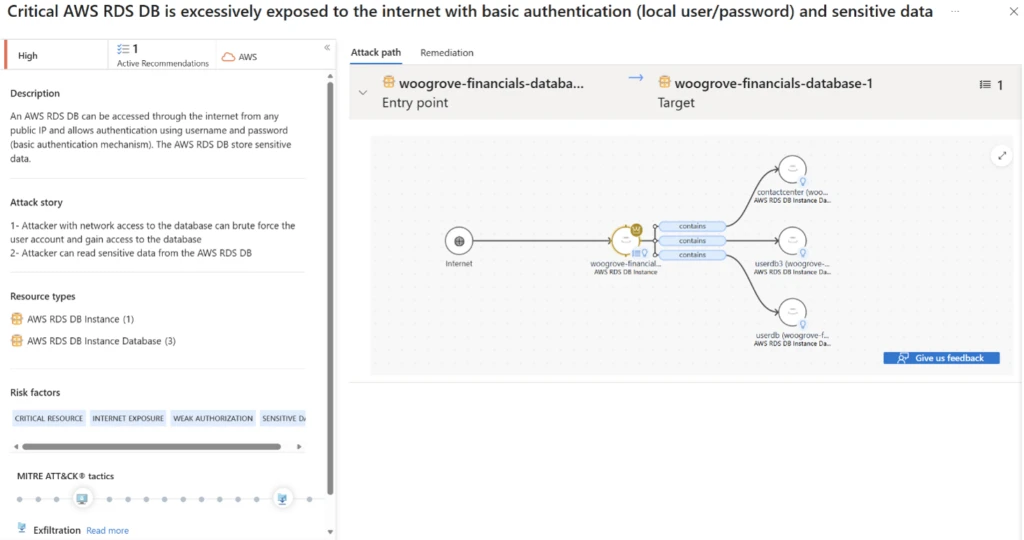
Microsoft Defender for Cloud now extends database threat protection to open-source relational databases on Amazon Web Services (AWS) Relational Database Service (RDS). Now generally available, built-in threat detection identifies anomalous access patterns and brute-force attempts, while automated sensitive data discovery helps teams understand where high-risk data resides. These insights, combined with integrated investigation across Microsoft Defender, help teams prioritize and respond to database risks more effectively. Detect threats and discover sensitive data across Azure and AWS with Microsoft Defender.
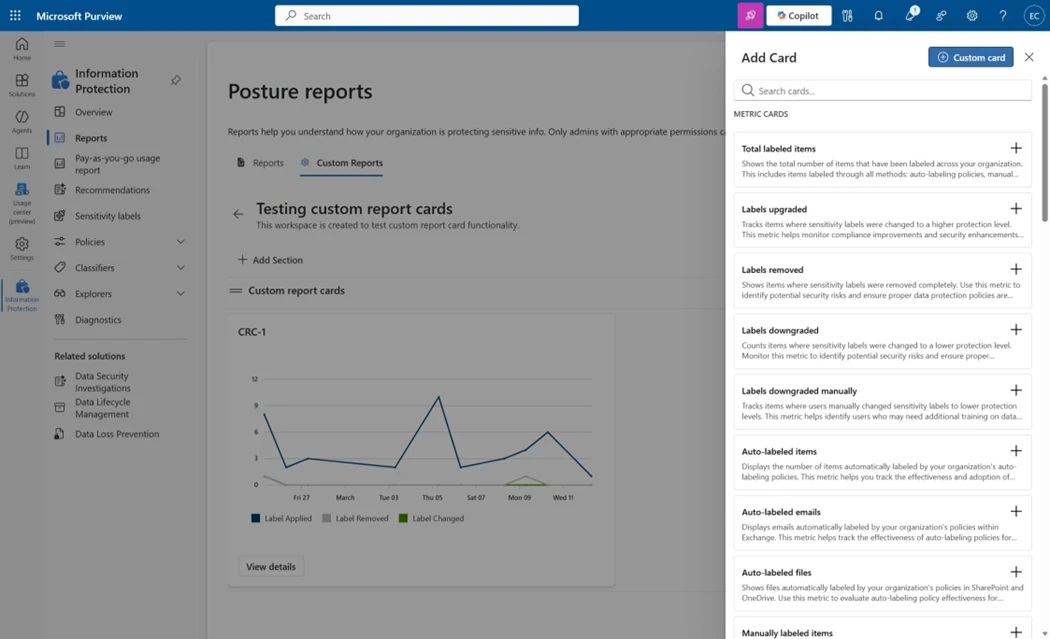
Microsoft Purview customizable reports, now generally available in Data Security Posture Management (DSPM), give teams greater control and flexibility to tailor reporting views, analyze trends, and quickly surface the insights that enable faster, more informed decisions. Choose from out-of-the-box reports or create custom reports tailored to your organization’s specific needs, with easy options to export and share insights across teams and stakeholders. For example, security teams can create role-specific reports that highlight high-risk data exposure trends to guide policy decisions. Learn how to customize reporting experiences to uncover your critical data security insights.
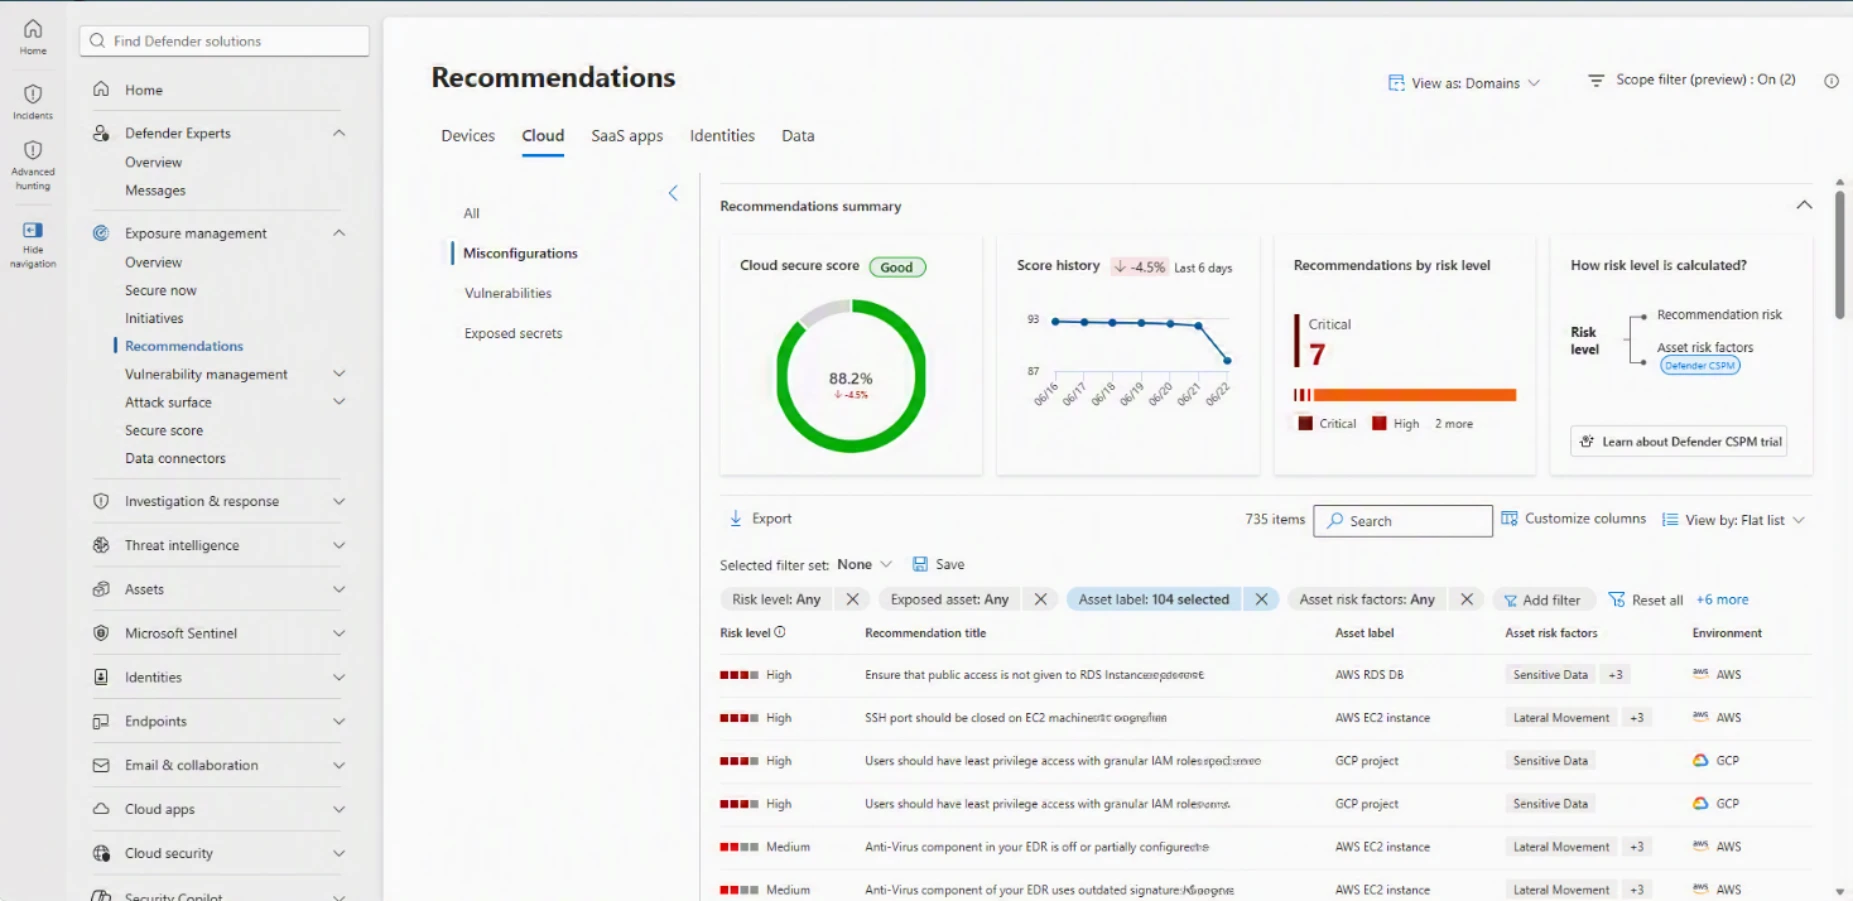
Microsoft Defender for Cloud is expanding multicloud coverage and visibility across AWS and Google Cloud, adding support for approximately 90 additional resource types and more than 200 new security recommendations. Security teams can better understand their attack surface with broader visibility across cloud-native applications, identities, data services, and workloads. Across multicloud environments, teams can better assess security posture and prioritize remediation based on exposure context, compliance posture, and business criticality to reduce risk more effectively. Gain broader visibility and prioritize risk across multicloud environments with Defender for Cloud.
A new unified identity risk score combines signals from across Microsoft Security into a single, explainable measure of an identity’s risk. It brings together behavior, access patterns, and threat intelligence for all related accounts, sessions, and applications to provide a complete view of risk. The moment an identity acts suspiciously, the score helps your team cut through the noise, prioritize what’s urgent, and can automatically trigger Conditional Access policies to enforce protection at the point of access. Prioritize identity risk and enforce protection in real time with the new unified identity risk score.
To help developers secure code, agents, and models while giving security teams consistent visibility and control from development through runtime, Microsoft is integrating security into the tools and platforms developers already use. Organizations can use the new security tools and capabilities announced at Microsoft Build 2026 to innovate faster and scale AI adoption without sacrificing security. Read more about the Build 2026 security announcements.
Microsoft Security continually ships meaningful innovations across our portfolio and research-driven insights and reports for the security community. In the Loop posts are your reliable source of what’s new across Microsoft Security and what it means for your security strategy. Check back for the next drop.
To learn more about Microsoft Security solutions, visit our website. Bookmark the Security blog to keep up with our expert coverage on security matters. Also, follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。