







Anthropic introduced an agent identity model for Claude Tag, its AI assistant designed for team collaboration in shared workspaces. The model gives Claude its own identity, permissions, and tool access, configured by administrators and tied to a workspace or channel. Because Claude does not rely on individual user credentials, access remains separate from employees’ personal accounts, reducing the risk of exposing private documents through shared channels.
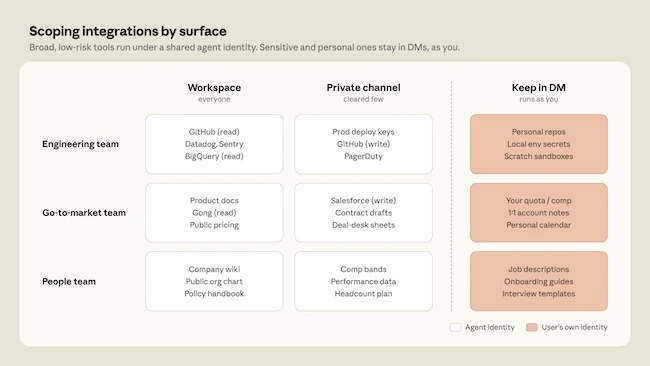
How teams scope Claude’s tool access in Claude Tag: broad, low-risk integrations run in shared channels under an agent identity, while personal or team-specific tools stay in DMs and run as the user. (Source: Anthropic)
Administrators assign Claude a dedicated identity with a default set of permissions, tools, and connections that apply throughout a workspace. These settings can be adjusted for individual channels. For example, Claude can be given access to GitHub and a data warehouse in an engineering channel, while a CRM connection can be limited to a private sales channel.
Administrators control which repositories Claude can access, the tools and API keys it can use, its skills and plugins, and any channel-specific instructions.
Because Claude uses a separate identity, administrators can revoke all of its permissions by disabling that identity instead of managing privileges through multiple user accounts.
“Agent identity replaces the question ‘what can this user do?’ with ‘what can this agent do in this compartment?’ That’s a departure from per-user Access Control Lists: it means that a channel member without direct access to the repo can ask Claude to read that repo if the channel’s profile grants Claude that permission,” Noah Zweben, a member of technical staff on the Claude Code team, explained.
Anthropic describes agent identity as a foundation for access control in environments where AI agents operate alongside teams and interact with multiple systems.
Claude Tag uses separate identities for private channels, while public channels share a workspace-wide identity. Each identity has its own permissions and privileges. For example, Claude in a legal channel cannot access engineering resources, and Claude in an engineering channel cannot view legal documents unless permission has been granted. Information learned in a private channel remains isolated and is not shared elsewhere in the workspace.
A channel’s identity is available to everyone in that channel by default. Administrators can further restrict an identity’s permissions and, on Enterprise plans, use role-based access controls to determine which users can interact with Claude. This allows organizations to control both what Claude can access and who can use it.
Anthropic says Claude Tag becomes more capable as administrators connect additional tools and data sources. It can combine information from connected tools and data sources to answer questions that span multiple systems.
Administrators can start with a baseline set of permissions, review audit logs, and grant additional privileges as needed while maintaining oversight through the agent identity model.
Organizations that need stricter controls can disable Claude Tag in specific channels or use role-based access controls (RBAC) to limit which users can interact with it.
When administrators connect a tool to Claude, the credentials are linked to that channel’s identity and used only when needed. Claude can communicate only with systems that administrators have approved. Connections to unauthorized destinations are blocked.
All actions performed by Claude are logged, including tasks, memory updates, and network requests. Because Claude operates under its own identity, those actions are recorded in the logs of connected services, providing administrators with an audit trail.
In direct messages, Claude operates under the user’s individual claude.ai account and uses that user’s connectors, credentials, and permissions. This allows Claude to work with tasks and tools that should not be available in a shared channel, such as email drafts or software licensed to a single user.
Zweben said Anthropic plans to add security controls that allow users to approve sensitive actions when needed without permanently expanding Claude’s permissions.
The company plans to introduce identity-aware access controls that combine Claude’s permissions with those of the user making the request. Under this model, Claude could perform an action only when both the channel’s permissions and the user’s access rights allow it.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。