









Reco announced Reco Agent Security, which expands the Reco Platform with advanced capabilities that prevent data exposure, unintended use and process disruption caused by AI agents operating across connected applications and workflows.
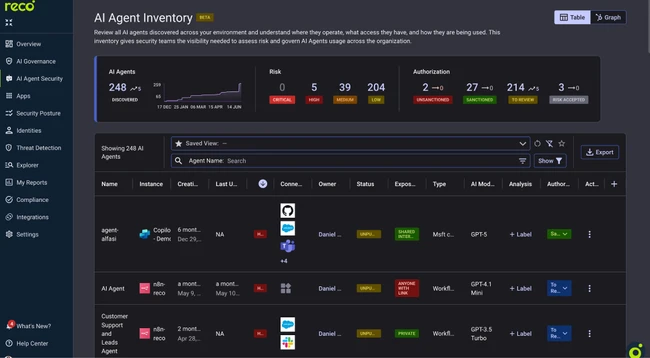
Agents function inside interconnected enterprise ecosystems where they can read sensitive data, invoke tools, trigger workflows, update records, communicate with other systems and take autonomous action. Agent security risks, therefore, are not isolated to the agent itself, but rather extend to the applications that agents connect to, permissions they inherit, identities they use, and data they access.
Reco Agent Security gives security teams visibility and control across the environments where AI agents operate. Built on the Reco Graph, used by Fortune 500 organizations to map and monitor enterprise interactions, Reco discovers every agent, maps what it can reach, prioritizes risk based on real operating context and enables precise remediation before autonomous action can expose data, trigger unintended use or disrupt business operations.
“Agents do not act alone. They operate across apps, identities, workflows and integrations that determine what they can reach and what they can do,” said Ofer Klein, CEO of Reco. “Reco Agent Security provides organizations the context, coverage and control they need to protect their production environments from agent risk without slowing down AI adoption.”
Point solutions exist for individual pieces of the problem: model security focuses on the model, identity security focuses on credentials and access and so on. Yet none of these categories capture the operational context which is where agents introduce real business risk.
Reco maps every agent across identity, permissions, connectivity and activity to show what the agent is, who owns it, how it behaves and what it can reach. This enables security teams to answer not just what an agent “did” do, but what an agent “can” do.
Reco Agent Security helps enterprises govern AI agents across connected applications and environments with the following capabilities:
Agent discovery and inventory: Discovers agents, copilots, AI workflows, service accounts and related non-human identities across the environments where agents operate. Security teams gain a live inventory of known and ungoverned agents, including ownership, connected applications, permission scope and recent activity.
Identity and ownership mapping: Identifies who deployed each agent, which users or teams are associated with it, what identities it uses and who is accountable for its behavior. This helps security teams eliminate orphaned, unmanaged and unowned agents before they create exposure.
Permissions and scope analysis: Maps the OAuth grants, roles, API keys, delegated access and permissions that agents rely on, and identifies excessive access, stale tokens, unapproved connections and permissions that exceed an agent’s intended purpose.
Activity and behavioral monitoring: Establishes baselines for agent activity, including API calls, data access patterns, timing, volume and connected endpoints. Reco flags deviations such as abnormal data movement, off-hours activity, new external connections, unexpected agent-to-agent activity and behavior that appears inconsistent with the agent’s role.
Connectivity and blast-radius mapping: Traces what every agent can reach across applications, APIs, data stores, tools, workflows and connected services. Reco identifies risky combinations where individual connections may appear acceptable in isolation but together create an unauthorized path to sensitive data or critical business systems.
Risk prioritization based on operating context: Scores and prioritizes agent risk based on identity, permissions, connectivity and activity, helping security teams focus on the agents and exposures that create meaningful business risk rather than reviewing raw lists of AI usage.
Context-aware remediation: Recommends precise remediation steps that reduce risk without disrupting business processes. Security teams can reduce permission scope, revoke stale access, disable unauthorized agents, route findings to owners and remediate exposure through existing ticketing and security workflows.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。