






Hackers who once focused on stealing valuable Roblox items are now taking over entire games.
Although Roblox operates the service, users can create and publish their own games on it. Successful games can generate substantial revenue through in-game purchases. Some developers have earned millions of dollars and built dedicated studios around their creations.
Multiple Roblox developers told 404 Media that hackers had taken over their games and said Roblox support did little to help them regain control until a reporter contacted the company for comment.
Ioannis Matziaris said attackers seized control of his family’s Roblox game and stole its Robux, Roblox’s virtual currency, after his son was tricked into running malware disguised as part of a job offer.
He noted that the attackers focused on taking over and republishing games and recruiting developers to continue working on the stolen projects.
Another developer received the same project manager job pitch. The attackers posed as representatives of Cheesy Studios, the Matziaris brothers’ company.
After running the file, the developer lost ownership of his game. The title generated roughly 10,000 Robux per day, reached 1,100 concurrent users, and served as his primary source of income. He spent more than 30 days trying to recover the game through Roblox support before media attention appeared to help move the matter forward.
After 404 Media contacted Roblox for comment, the company restored the game to its owner. In a statement, the company said it was “troubled” by the incident and pointed to security features such as Enhanced Protection and Account Session Protection.
Roblox added that no security measure can completely eliminate the risk of account theft when users are persuaded to run malicious software or execute untrusted code.
One developer described how the attack unfolded. He said attackers contacted him on Discord with a project manager job offer and instructed him to install a Python package called “robase,” which they presented as part of their development tools. Shortly after installing it, he lost access to his Roblox and Discord accounts.
According to the developer, the attackers then changed his security settings and transferred ownership of his Roblox game and group to another user. He said Roblox has not returned the game.
Malware campaigns targeting gamers are not limited to Roblox. A separate investigation uncovered attackers using Steam Workshop to distribute malicious wallpapers.
Kaspersky found that attackers have been using Steam Workshop to distribute malicious wallpapers designed to steal Steam accounts and infect systems with additional malware. Steam Workshop is Steam’s built-in service for sharing user-created content, including wallpapers, mods, and maps.
The campaign has been active since late 2025 and relies on Wallpaper Engine, a popular application that allows users to create and share animated desktop wallpapers.
According to the researchers, attackers hid malicious code inside wallpaper packages and primarily targeted gamers in China and Russia.
“The whole concept of ‘application wallpapers’ essentially allows foreign code to be run directly on your computer. Cybercriminals took note of this feature and started embedding malware right into these types of wallpapers,” they explained.
”Because Wallpaper Engine relies on Steam Workshop for content sharing, anyone can create a wallpaper and publish it for the community to download and install for free. Naturally, this setup is a magnet for bad actors.”
The malicious wallpapers had already been downloaded thousands of times before they were removed, with some reaching tens of thousands of downloads.
The researchers identified two main delivery methods. Some malicious wallpapers included malware directly within wallpaper packages, typically in the form of malicious executables, DLLs, or scripts. Others concealed the payload inside password-protected archives, with passwords either exposed in file names or stored in configuration files.
In most cases, the malware executed automatically when users applied the wallpaper.
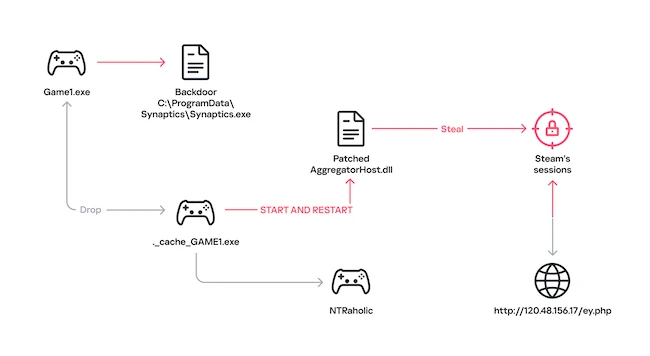
Observed attack flow (Source: Kaspersky)
Kaspersky tested one of the malicious wallpapers disguised as a game called NTRaholic. The game launched as expected, helping avoid suspicion while a DarkKomet backdoor was installed in the background. It also deployed a modified version of a system library called AggregatorHost.dll, which searched the victim’s computer for the Steam application and attempted to obtain account credentials.
Although Steam removed the malicious wallpapers identified during the investigation, the researchers warned that attackers could upload new malicious wallpapers in the future.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。