






A newly discovered Android banking trojan, dubbed Rokarolla, targets 217 banking and cryptocurrency applications and can execute 137 commands on infected devices, according to researchers at Zimperium.
Named after its command-and-control (C2) infrastructure, Rokarolla is primarily distributed through malicious websites that impersonate popular applications such as TikTok and Google Chrome, fooling users into downloading what appears to be a legitimate app.
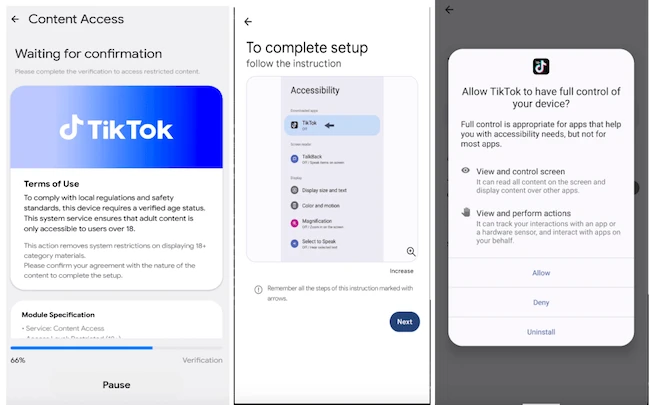
Banker malware impersonating a legitimate app and requesting accessibility service (Source: Zimperium)
Zimperium said Rokarolla is designed to steal financial information while giving attackers broad control over compromised devices.
“Its malicious capabilities include harvesting lock screen credentials, exfiltrating sensitive contact lists and SMS data, and utilizing keyloggers to continuously record user input,” the researchers said.
“Furthermore, the trojan actively conceals its operations and disrupts user intervention by blocking incoming calls, deploying fraudulent screen overlays, suppressing device audio, and deactivating Google Play Protect.”
The attack begins with a dropper that poses as Google Play Protect, Google’s Android security service. Once installed, it delivers a second-stage payload containing the Rokarolla malware.
When launched on the device, Rokarolla requests access to Android Accessibility Services, along with permissions for notifications and SMS messages.
The malware then checks infected devices for any of the 217 banking and cryptocurrency applications on its target list. When it finds one, Rokarolla downloads a phishing page that is displayed as an overlay when the victim opens the legitimate app, allowing attackers to collect credentials, credit card information, and other financial data.
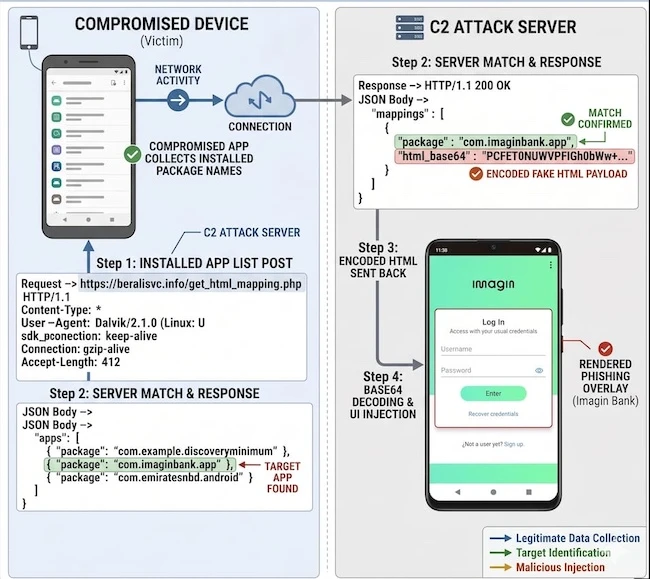
Fake Overlay process of Imagin bank (Source: Zimperium)
Rokarolla exchanges data with its C2 infrastructure, sending details about the device, Android version, locale, battery status, and available storage. According to Zimperium, this information is used to generate a unique botID for each infected device.
The malware can receive commands from its operators and switch to alternative C2 domains through remote configuration. The researchers identified 137 commands used to control infected devices.
“The malware has the capability of exfiltrating all SMS messages from the infected device and can also send SMS on behalf of the victim, which can be used to intercept sensitive information such as bank OTPs,” the researchers said.
Rokarolla can also extract text displayed on the screen and gather information from messaging applications. The researchers found that it can modify clipboard contents without user interaction, a capability that can be used to replace cryptocurrency wallet addresses and other copied data.
Instead of relying on continuous screen streaming, Rokarolla periodically captures screenshots of infected devices and sends them to its operators. This provides visibility into user activity and information displayed on the screen.
Another capability allows Rokarolla to block and intercept phone calls, giving attackers a way to disrupt fraud alerts and other security-related communications from banks.
“Complementing this visual evasion, the malware is capable of muting all device audio and vibrations, ensuring it operates in complete silence during fraudulent activities,” they added.
Zimperium published a list of indicators of compromise (IoCs) on a GitHub page. The company also included a complete list of MITRE ATT&CK tactics and techniques associated with the Rokarolla attack chain.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。