








Researchers built a continuous authentication system called AccLock that identifies a wearer by the tiny vibrations a heartbeat makes inside the ear canal. The signal comes from an accelerometer of the kind already sitting inside many wireless earbuds, so no extra hardware is needed. The point is to keep verifying that the person wearing the device is the legitimate user long after the initial unlock.
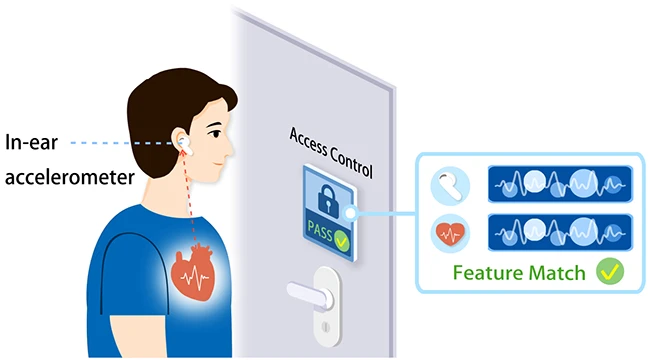
Example of an application scenario for AccLock (Source: Research paper)
Each heartbeat sends a small mechanical pulse through the body. In the ear, that pulse shows up as a ballistocardiogram, or BCG signal, that an accelerometer can pick up. AccLock cleans up the raw motion data, extracts features tied to the wearer’s cardiac pattern, and compares those features to a registered template. If the match is close enough, the session stays trusted. If it drifts, the session gets revoked.
Registration takes about six minutes of sitting still, and the authors show usable accuracy with as little as two minutes of enrollment data. Each authentication decision works on a four-second window, with a sliding step that updates the trust state roughly every half second.
The headline numbers from a 33-person study are decent. Across sitting, lying down, light head movement, and even music playback at high volume, the system kept error rates in the low single digits. Older and younger users, men and women, and even people with several common heart conditions all landed in roughly the same range.
The more interesting test was the one that matters for security: what happens when the legitimate wearer takes the earbud out and someone else picks it up. The system caught the handoff within a few seconds in almost every trial. That is the entire point of continuous authentication, and on this one task the design held up well.
The system held up fine for desk work and casual movement. Walking knocked accuracy down noticeably. Running broke it almost completely. Talking also caused problems, since jaw motion and shifting contact with the ear produce vibrations in the same range as the heartbeat itself. Including some talking samples during enrollment recovered part of that loss.
Long-term drift is another open question. Accuracy held steady for about six weeks and started slipping by week eight, which the authors attribute to gradual changes in fit, posture, and behavior. A background refresh routine using high-confidence samples seems to keep the profile current, but the study only ran for two months. What happens at six months or a year is anyone’s guess.
A small group of users also produced consistently worse results than the rest, likely due to anatomy and how the earbud sits in the ear. Until that gap closes, any deployment would need a fallback for the people the system simply does not read well.
The prototype used a custom 3D-printed earbud with a standard commercial accelerometer running at 100 Hz. That sampling rate matters. Apple AirPods expose only heavily downsampled motion data, around 25 Hz, to third-party developers.
The team did get the system running on AirPods using a lightweight retraining step, but error rates roughly doubled, from around 3% to around 7%. Workable, less accurate, and dependent on vendor cooperation if anyone wanted to ship this at scale.
Most consumer biometrics, including face and voice, have well-documented spoofing problems involving printed photos, deepfake audio, and silicone replicas. A BCG signal is harder to capture from a distance and harder to replay, since it arises from the wearer’s own cardiac mechanics inside the ear canal. The paper leans on that physiological origin as the basis for spoof resistance.
It is worth being honest about what was tested and what was skipped. The 33-user study covered movement, posture, environment, BLE packet loss, music playback, and several cardiac conditions, including bradycardia, tachycardia, coronary heart disease, and premature beats.
The study did not test against an active adversary attempting to inject vibrations, replay a captured BCG stream, or reconstruct a target’s cardiac signature from other sensor data. Continuous biometric streaming over BLE also raises a privacy surface that the paper does not address. Any production deployment would need a hard look at both.
The persistent problem with biometric login is that it usually happens once, at the start of a session, and the trust never expires. An attacker who grabs an unlocked phone, an unlocked workstation, or an unlocked earbud inherits everything. Passive biometrics that run quietly in the background are one of the more credible answers to that problem, since they cost the user nothing and can revoke trust the moment the wearer changes.
AccLock is one of the first published designs to do this from a sensor that already ships in mainstream earbuds, with no speaker output and no required user action. The accuracy numbers are competitive with other passive biometric proposals, the energy overhead is small, and the failure modes are documented.
Whether it ever reaches a shipping product depends largely on whether earbud vendors decide to expose raw accelerometer data to developers, which they currently do not.
For now, treat it as a useful data point on where continuous authentication research is heading: away from explicit gestures and shared secrets, toward signals the body produces on its own.

此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。