






Software teams are pushing code into production faster than security testing can keep up. AI is accelerating development cycles and adding pressure to security programs that rely on periodic validation and manual penetration testing.
The 2026 State of AI Security Testing report from Aikido Security found that 76% of organizations have had to stop, restrict, or roll back AI-driven behavior in the past 12 months. Another 71% said AI or automation made a security issue harder to detect, investigate, or fix.
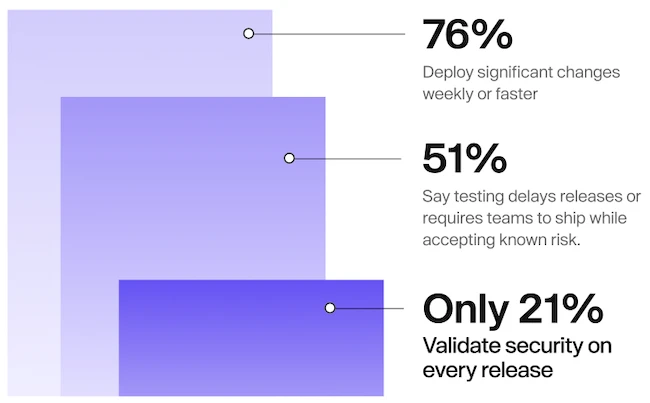
Security testing can’t keep pace with software delivery (Source: Aikido Security)
Security teams are often held accountable for risk despite lacking authority over release decisions. Release owners are not always accountable for the resulting security outcomes. Only a third of security teams have both the authority to stop a release and responsibility for the consequences if something goes wrong.
“Teams are forced to deal with missed issues, uncertainty about what was actually tested, and delays when trying to release,” said Willem Delbare, CEO of Aikido Security.
Most organizations deploy significant changes frequently, but only 21% validate security on every release. Penetration testing remains a point-in-time exercise, even though applications, infrastructure, dependencies, and configurations continue to change after testing is completed.
Security testing timelines affect release decisions by delaying deployments or forcing teams to accept known risks. Teams most constrained by testing benefit the most from faster security validation.
Only 4% of companies have no concerns that their testing will miss vulnerabilities introduced between scheduled assessments. Engineering teams deploy continuously, creating more opportunities for vulnerabilities to be introduced between scheduled assessments.
Nearly half of teams say pentest findings are always or often outdated by the time they receive them. The problem becomes more pronounced as release frequency increases. Of teams that deploy multiple times per day, 84% say pentest findings are often or always outdated when they arrive, compared with 26% of teams that deploy monthly or less frequently.
“We see teams go from idea to production in hours, so when security testing takes weeks to return results, you’re testing a system that no longer exists,” said Anton Osika, CEO of Lovable.
52% of organizations lack visibility into what was tested during a penetration test. That makes it harder to determine whether findings represent isolated issues or broader patterns within an application.
Retesting is another challenge. Only 40% of organizations promptly verify vulnerabilities after fixes are implemented. Delayed or inconsistent retesting leaves teams relying on assumptions that remediation efforts worked as intended.
Respondents reported concerns that manual penetration testing can miss logic flaws and multi-step attack paths that require deeper knowledge of how applications behave in production.
Leaders say AI-driven pentesting needs safeguards such as activity termination controls, data residency guarantees, and human review checkpoints. They want greater confidence in the findings these systems produce.
Teams want to understand a vulnerability’s impact and severity and confirm that findings are legitimate. Triage is where progress most often stalls. Even after a finding is validated, assigning it to the right owner creates additional friction.
Leaders are most concerned about exposure between tests and want more frequent validation. Most prefer quarterly assessments, with others favoring biannual validation. Security leaders are more likely to support frequent validation, and engineering leaders prioritize deployment speed.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。