












Office work in 2026 runs through a stack of mobile apps that sit on the same phones people use for banking, messaging family, and tracking their location.
Ten of the most common workplace apps in use across U.S. companies, including Gmail, Microsoft Teams, Zoom Workplace, Slack, and Notion, account for more than 12.5 billion downloads on Google Play. New research from Incogni, based on data pulled from the Google Play Store on March 20, 2026, finds that these apps collect an average of 19 data points each and share around 2 data types with outside parties.
Source: Incogni
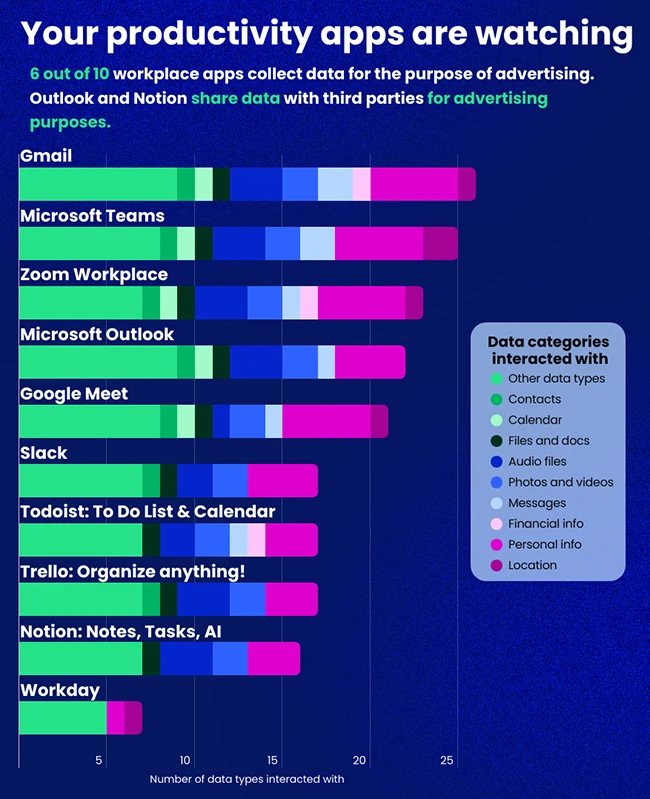
Gmail collects 26 distinct data types, the highest count in the study. The app gathers approximate location, app interactions, and user IDs for advertising and marketing purposes. Microsoft Teams follows with 25 data types, and Zoom Workplace collects 23. Both Teams and Zoom Workplace pull precise location data, the only two apps in the set to do so. Microsoft Outlook collects 22 data types, and Google Meet collects 21. Slack, Trello, and Todoist each collect 17 data types.
Six of the ten apps gather data for advertising or marketing: Gmail, Slack, Notion, Outlook, Todoist, and Zoom Workplace. Three of them, Slack, Todoist, and Notion, collect employee email addresses for marketing purposes.
Notion stands out for outbound data flow, sharing 8 distinct data types with third parties. The shared categories include email addresses, names, user IDs, device or other IDs, and app interactions, and several of these go to advertising partners.
Incogni researchers note that Notion’s privacy policy permits select advertising technology partners to place tracking tools on user browsers to collect behavioral data. Workspace content stored in Notion can include product roadmaps, HR notes, and client records, raising the stakes when that data reaches third parties.
In December 2024, the EU’s Data Protection Board issued an opinion raising the bar for how platforms must justify the use of personal data in AI model training under GDPR. Scrutiny has grown around how Notion AI processes workspace content through third-party model providers.
Workday is the only app in the analysis that does not allow users to request deletion of their data. The platform holds employment records, payroll details, and personal identifiers. In August 2025, Workday confirmed two related security incidents tied to its use of Salesforce as a CRM platform, with attackers obtaining business contact information including names, email addresses, and phone numbers. The breach was part of a broader social engineering campaign linked to the hacker group ShinyHunters.
Most of the apps examined have a documented breach history. In January 2026, a security researcher discovered a publicly accessible 96-gigabyte database containing roughly 149 million login credentials, including 48 million tied to Gmail accounts. Google attributed the exposure to infostealer malware on user devices and denied any internal breach. In November 2025, Japanese media company Nikkei disclosed that attackers used malware-stolen Slack credentials to reach accounts belonging to more than 17,000 employees and business partners, exposing names, email addresses, and internal chat histories. In January 2024, scraped Trello data covering more than 15 million records appeared for sale on a hacking forum.
Zoom, Notion, and Slack have all experienced data breaches. Microsoft and Google, parent companies of several apps in the study, have each had breaches in other products. Todoist is the only app in the set with no known connection to a data breach.
The dataset covers Google Play listings only, leaving open the question of whether iPhone users see the same picture. Asked whether the iOS Privacy Nutrition Labels for the same ten apps would line up with the Google Play disclosures, Bogdan Popescu, Research & Communications Senior Manager at Incogni, told Help Net Security: “Yes, this research focused on Google Play apps solely. In our experience, we have compared iOS and Android apps in the past, and the privacy nutrition tends to be similar, but we haven’t applied this filter here. Independent studies comparing the disclosures for apps available on both platforms revealed notable differences in data practice disclosure in the iOS and Google Play app stores for apps that one would otherwise have expected to be identical.”
Many employees install these apps on personal devices to meet employer requirements. The collected data includes contact details, financial data, and precise location, and much of it feeds into advertising ecosystems or sits within corporate systems with broad administrator access. Slack workspace owners and administrators can reach virtually all communications on the platform, including direct messages and private channels, since the service does not offer end-to-end encryption.
The combination of high-volume collection, advertising-linked use, and recurring breaches across this category gives employers and workers a concrete picture of what installing these apps puts on the line.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。