

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

MongoDB | Blog
MongoDB | Blog
大猫的无限游戏
大猫的无限游戏
H
Help Net Security
V
Visual Studio Blog
G
Google Developers Blog
Blog — PlanetScale
Blog — PlanetScale
Last Week in AI
Last Week in AI
C
Check Point Blog
D
Docker
M
MIT News - Artificial intelligence
P
Proofpoint News Feed
博客园 - 叶小钗
博客园 - 聂微东
The Cloudflare Blog
云风的 BLOG
云风的 BLOG
Martin Fowler
Martin Fowler
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
酷 壳 – CoolShell
酷 壳 – CoolShell
MyScale Blog
MyScale Blog
WordPress大学
WordPress大学
Engineering at Meta
Engineering at Meta
腾讯CDC
S
SegmentFault 最新的问题
博客园 - 【当耐特】

Help Net Security

ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security Acronis GenAI Protection gives MSPs control over AI usage and data risks - Help Net Security
PureLogs infostealer is stealing credentials worldwide
Zeljka Zorz · 2026-05-19 · via Help Net Security

A phishing campaign is smuggling the powerful PureLogs information stealer onto targets’ Windows machines by hiding encrypted malicious payloads inside cat photos, Fortinet researchers discovered.

The attack

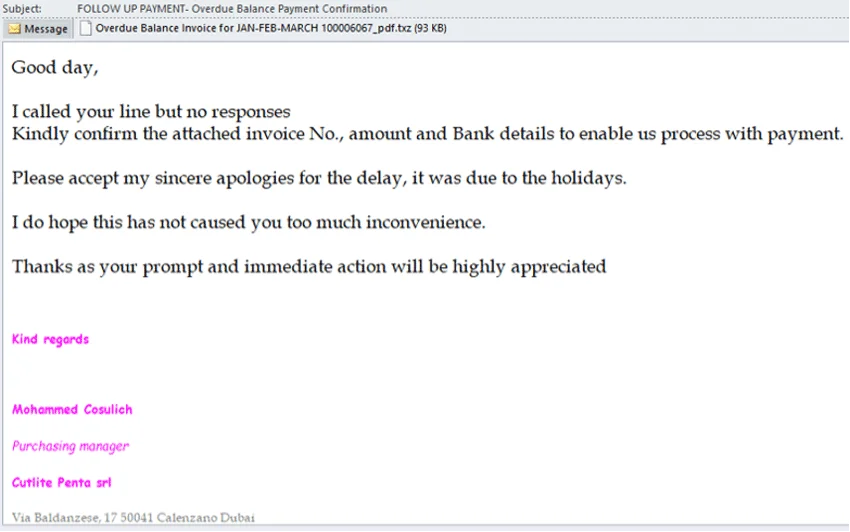
The attack starts with a phishing email containing a TXZ archive and using an invoice-themed lure to pressure the victim into opening it quickly:
PureLogs infostealer steganography

The phishing email carrying the malicious TXZ archive (Source: Fortinet)

The extracted JavaScript stores malicious commands in process environment variables (which are also filled with garbled text and multilingual comments as obfuscation), then launches a hidden PowerShell session to decode, decrypt, and decompress a .NET assembly loader dubbed PawsRunner.

PawsRunner decrypts a download URL using RC4, then tries multiple network APIs to fetch a PNG image. (In a previous campaign flagged by Swiss Post Cybersecurity, the PNG image was retrieved from archive.org.)

It then extracts an encrypted payload hidden withing the image (PNG) file using steganography markers, and bypasses Event Tracing for Windows and Windows 11 security features.

A prodigious infostealer

The final malicious payload is the PureLogs infostealer, which profiles the victim’s system environment and harvests credentials, cookies and session tokens from:

  • An extensive list of popular and lesser known web browsers used around the world
  • Over 100 crypto wallet extensions and desktop wallets
  • Communication apps (Discord, Telegram, Signal, etc.)
  • Password managers (Bitwarden, LastPass, 1Password, etc.)
  • Authenticators (via browser extensions)
  • Other software like Steam, OpenVPN, PhontanVPN, Ngrok, OBS Studio, FileZilla, WinSCP, FoxMail, MailBird, MailMaster, and Outlook.

The stolen data is AES-encrypted and exfiltrated.

“This version of PureLogs uses extensive async/await patterns to improve task efficiency and complicate analysis. Additionally, it uses HTTPS for its Command and Control (C2) communications,” the researchers added.

The stolen data can be used for financial theft or sold on criminal markets, potentially enabling follow-on attacks against victims’ employers, banks, or contacts.

Steganography on the rise

The shift toward hiding payloads inside image files represents a deliberate effort to blend malicious activity into normal-looking network traffic: A PNG file fetched over HTTPS, from what might appear to be a legitimate host, raises far fewer alarms than a direct download of an executable.

According to Fortinet, the technique is increasingly used by attackers.

Users are advised to treat unexpected emails and attachments as suspicious regardless of how urgent or routine they look, and to be wary of opening files in unusual file formats.

Organizations can do more: they can train employees on how to detect invoice-themed lures, block uncommon archive formats at the email gateway, monitor for unusual PowerShell behavior, restrict JavaScript execution from email attachments, and deploy endpoint detection that covers in-memory execution.

Subscribe to our breaking news e-mail alert to never miss out on the latest breaches, vulnerabilities and cybersecurity threats. Subscribe here!