








Chainguard launched Athena, an industry coalition that pools open source vulnerability findings and remediates them under embargo before public disclosure. The group went live with more than two dozen member organizations. Founding members include BNY, Chainguard, Cisco, Cloudflare, Corridor, DepthFirst, Docker, JPMorganChase, Kyndryl, LTIMindtree, and PwC.
Dan Lorenc, CEO of Chainguard, said no single company can get ahead of the threat alone and that orchestrated defense is the answer. In a comment on the launch, he said: “Athena is operational. More than 20,000 findings processed, 2,000 patches across 500 projects, first coordinated disclosures in about a month. Will it be perfect? No, and no one should pretend otherwise. But fragmentation is worse, standing still isn’t survivable, and the more of the industry that’s in, the less any attacker has left to find.”
Athena targets a problem created by frontier AI models. These systems read code, reason across dependencies, and surface novel, chained zero-day vulnerabilities at machine speed, including flaws that survived decades of expert review.
In one case, a critical bug sat in media-processing code used by many applications that automated fuzzers had run more than five million times without catching it. The gap between a vulnerability being discovered and being exploited has collapsed from years to hours, and a growing share of exploits are weaponized before the bug becomes public. The code underneath much of this software is often maintained by one or two volunteers already buried in low-quality scanner noise.
Many of the coalition’s submitting members surface these vulnerabilities through frontier AI programs including Anthropic’s Project Glasswing and OpenAI’s Daybreak, and bring the resulting findings to Athena.
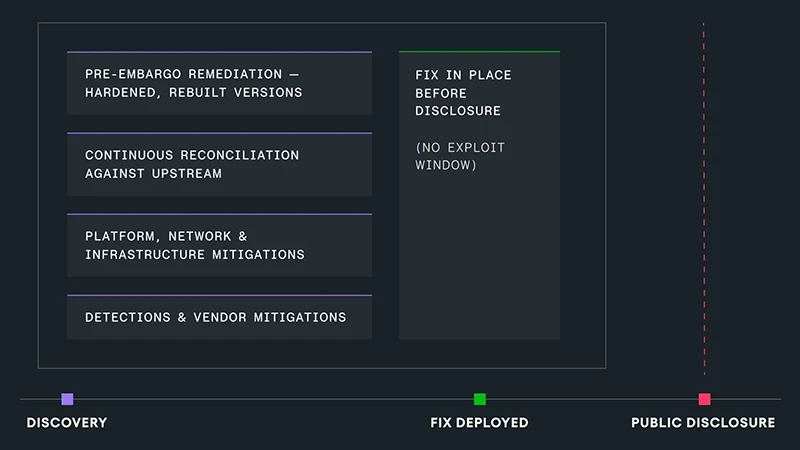
Athena runs a shared platform that carries each vulnerability through its lifecycle from discovery to a durable upstream fix. Organizations submit pre-disclosure findings through an encrypted portal, and each submitter sets what is shared, with whom, and on what embargo timeline. Athena deduplicates and enriches each finding, traces when the flaw was introduced and whether it is already fixed at head, and publishes the metadata as an OSV feed. Members receive anonymized, aggregated intelligence across submitters and access to patched builds ahead of public disclosure.
Before disclosure, private forks and rebuilt, hardened versions reach members through Chainguard Libraries. Findings get addressed in batches across an entire library, hardening it against whole classes of issues. Findings are reconciled against upstream activity throughout the embargo to keep fixes current.
Athena stacks additional layers of protection. Partners that operate infrastructure, platform, network, and security layers push non-patch mitigations ahead of disclosure, including detection signatures, traffic-level rules, and platform-side blocks. Cybersecurity partners add their own detections, signatures, and virtual patching. The coalition drives coordinated disclosure upstream, and Athena acts as a maintainer of last resort for fixes that cannot reach the volunteer maintainers on their own. Chainguard hopes to work with the Linux Foundation on a coordinated Security Incident Response Team for open source.
A large share of Athena’s work stays invisible by design. A patch only protects systems that can apply it, and much of the world’s critical infrastructure cannot patch on an attacker’s timeline. Athena’s platform-level mitigations aim to neutralize a vulnerability across the internet before public disclosure.
The same open source libraries that run inside large technology companies also run inside municipal water systems and regional hospitals with little or no dedicated security staff. Those organizations gain protection without taking any action.
Athena is open to vetted organizations through an application process. Members keep control of their findings, which they can hold private, share with a trusted subset of the coalition, or open to everyone. Organizations that join before the first coordinated disclosure wave next month are covered under embargo ahead of it.

Must read:
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。