









ArmorCode has announced new Cyber Resilience Act (CRA) capabilities within the ArmorCode Agentic AI Platform. The capabilities help manufacturers of products with digital elements (PDEs) prepare for the European Union’s cybersecurity regulation that will impact all sellers of these solutions in the region.
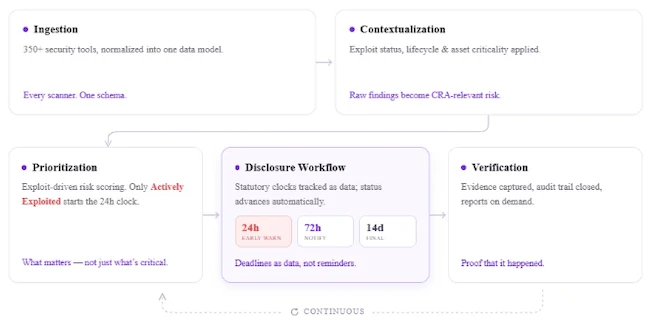
ArmorCode now enables organizations to operationalize CRA requirements through a unified system of record that combines product security data, exploit-aware risk prioritization, disclosure workflow management, software bill of materials (SBOM) and vulnerability exploitability exchange (VEX) support, and continuous compliance reporting.
The EU Cyber Resilience Act is a major regulation that entered into force in December 2024 and establishes cybersecurity requirements for products with digital elements sold in the European Union. The regulation requires manufacturers to remediate vulnerabilities without delay.
Beginning September 11, 2026, manufacturers must meet strict reporting obligations for actively exploited vulnerabilities. These include delivering 24-hour early warning notifications, 72-hour vulnerability notifications, and a final report within 14-days of a corrective or mitigating measure being available. Organizations that fail to comply will face penalties of up to €15 million or 2.5% of global annual turnover, whichever is higher.
Most organizations cannot operationalize these reporting requirements today. They lack a centralized system for managing the data, workflows, and evidence required to meet the obligations. Critical information is also spread across vulnerability scanners, threat intelligence feeds, asset inventories, SBOM repositories, ticketing systems, and compliance platforms, creating operational complexity and increasing the risk of missed deadlines.
“The Cyber Resilience Act is redefining accountability for cybersecurity by extending focus beyond operators to the security capabilities of product suppliers,” said Larry Lowe, Chief Product Security Officer for Wabtec.
“In anticipation, we proactively aligned our development processes with IEC 62443-4-1 and invested in scalable solutions to operationalize security. With ArmorCode, we are achieving the visibility and automation needed to consolidate vulnerability data, streamline disclosure workflows, and track risk in real time, enabling us to meet the pace and scale that the CRA demands while reinforcing customer trust,” Lowe continued.
“The CRA turns product security into a reporting discipline with a deadline attached,” said Mark Lambert, Chief Product Officer at ArmorCode. “The manufacturers who handle it well won’t build a separate compliance program for it, they’ll run it on the platform they already use to manage exposure. And as only actively exploited vulnerabilities start the 24-hour clock, knowing what’s actually being exploited is the difference between a workable process and a fire drill.”
The ArmorCode Agentic AI Platform has been expanded to serve key CRA workflows and requirements, including:
ArmorCode helps organizations focus on the vulnerabilities that matter most for CRA by incorporating exploitability data into risk prioritization workflows. Only vulnerabilities designated as Actively Exploited trigger the 24-hour reporting clock, helping teams reduce noise while maintaining a complete audit trail.
“Cyber resilience is a business requirement,” said Karthik Swarnam, Chief Security and Trust Officer at ArmorCode. “The Cyber Resilience Act raises the stakes for every organization that builds or sells digital products in Europe. Failing to identify and report actively exploited vulnerabilities can result in significant financial penalties, but the greater risk is the loss of customer trust and confidence. Organizations need a way to operationalize security, compliance, and disclosure at scale. ArmorCode helps teams bring together the data, workflows, and evidence needed to respond quickly, demonstrate accountability, and stay ahead of evolving regulatory requirements.2
The CRA capabilities are built on the ArmorCode Agentic AI Platform, which unifies security findings, asset intelligence, software supply chain data, threat intelligence, cloud security signals, and business context into a single source of truth. Through more than 375 integrations, ArmorCode enables organizations to correlate findings, prioritize risk, automate remediation workflows, and generate audit-ready evidence without replacing existing security tools.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。