








145 AI-related laws were enacted by state legislatures in 2025, and more than 1,000 additional bills were introduced or revised, according to DataGrail’s Privacy and AI Trends Report 2026.
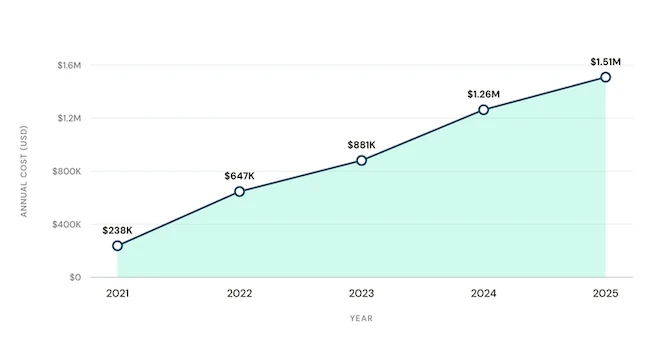
Average cost of manual data subject request management (Source: DataGrail)
Of the 2,400 popular business software providers that advertised AI capabilities, 63.6% did not disclose third-party AI subprocessors in their legal documentation, exposing businesses to shadow AI risks they may not be aware of.
AI risk management requires visibility into how AI is used and what data it processes. DataGrail found that 32.8% of AI systems participate in at least one high-risk activity, including sensitive data processing and automated decision-making.
AI capabilities are not always disclosed in legal documentation, limiting visibility into how personal data is accessed and processed. The flexibility of AI applications can make it difficult to anticipate higher-risk use cases.
During 2025, California publicly reported consent management settlements totaling $4.3 million. This figure does not include non-public settlements.
Investigations by private law firms into tracking pixels and session replay software contributed to more than 1,400 class action lawsuits in 2025. This count excludes the thousands of cases estimated to have been settled out of court, making consent enforcement too costly to treat as an acceptable risk.
Organizations continue to overlook one of the simplest compliance measures: browser opt-out signals. This consent check often provides regulators with an initial view of a company’s privacy compliance posture before they review the privacy policy.
Privacy laws in more than 10 U.S. states require businesses to honor universal opt-out mechanisms, including Global Privacy Control. Despite those requirements, 63% of websites fail to honor opt-out signals.
Fewer than 15% of users make an explicit choice to opt out of some or all non-essential tracking. Users who leave a website without making a selection may be subject to different tracking outcomes depending on the site and jurisdiction, which can influence measurement results.
Regulators are prohibiting dark patterns and other deceptive design practices in cookie consent banners. Enforcement actions include treating a user’s failure to interact with a banner as invalid consent for tracking.
Data subject request volumes increased for the fifth consecutive year, stretching organizational capacity and making it more difficult to ensure requests are completed thoroughly.
For a medium-sized company receiving 5 million unique website visitors annually, the average cost of handling data subject requests manually reaches $1.5 million per year.
“If there’s one word that sums up data privacy in 2026, it’s ‘more’: more regulation, more risk, more pressure. The only thing there isn’t more of is privacy professionals to handle it,” said Daniel Barber, CEO of DataGrail.
“The volume of data subject requests, new AI laws, and enforcement actions isn’t slowing down and privacy teams can’t manage this complexity with traditional approaches anymore. The privacy programs that will thrive in 2026 aren’t the biggest, they are the ones investing in privacy-first AI tools to scale their programs intelligently, stay ahead of regulation, and deliver secure AI to the business,” Barber continued.
Data brokers experienced the largest increase in deletion requests. Compared with 2024, deletion requests rose by 398% in 2025, reaching an average of more than 2,000 requests per month. Since 2021, deletion requests have increased by 567%. Organizations processed more than 900 “do not sell or share” requests per month on average.
Industries handling health, financial, and location data received the highest volume of data subject requests in 2025. Several sectors entered the top five after little activity in previous years. Professional services firms received 4.6 times more data subject access requests than the average organization.
Beginning this year, California made privacy risk assessments a legal requirement. Organizations must conduct them and submit the results for annual audits starting in April 2028. Each review must be personally attested to by a company executive under penalty of perjury.
The CCPA sets some of the strictest privacy assessment requirements in the United States and exceeds GDPR requirements in certain areas. For many U.S. companies, this will be their first experience conducting formal privacy risk assessments.
They are required for any processing activity that may pose privacy risks to consumers. AI initiatives deserve particular attention because of their potential impact on personal data and automated decision-making.
In 2025, 42% of companies abandoned AI projects, with data privacy concerns cited as a leading factor. Early involvement from privacy teams helps identify safeguards, reduce compliance risks, and support product development. An AI risk assessment is often the first step.
Privacy teams have reported headcount reductions of up to 33% while managing expanding compliance obligations. As a result, organizations plan to use AI to support privacy-related tasks.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。