

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

博客园_首页
博客园 - 【当耐特】
博客园 - 叶小钗
阮一峰的网络日志
阮一峰的网络日志
WordPress大学
WordPress大学
D
Docker
T
The Blog of Author Tim Ferriss
Cyber Security Advisories - MS-ISAC
Microsoft Azure Blog
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
月光博客
月光博客
M
MIT News - Artificial intelligence
H
Hackread – Cybersecurity News, Data Breaches, AI and More
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
云风的 BLOG
云风的 BLOG
F
Fortinet All Blogs
罗磊的独立博客
小众软件
小众软件
A
About on SuperTechFans
MyScale Blog
MyScale Blog
D
DataBreaches.Net
The GitHub Blog
The GitHub Blog
C
Check Point Blog
L
LangChain Blog

Help Net Security

ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security Acronis GenAI Protection gives MSPs control over AI usage and data risks - Help Net Security
SimpleHelp RMM flaw could give attackers full access to m...
Zeljka Zorz · 2026-06-16 · via Help Net Security

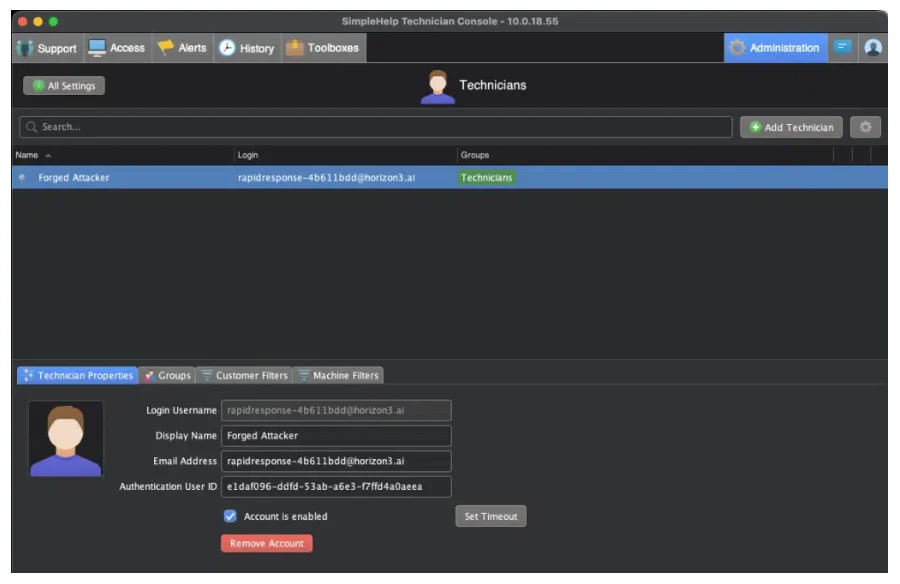
A critical vulnerability (CVE-2026-48558) in SimpleHelp, a popular remote monitoring and management (RMM) tool, can be exploited remotely by unauthenticated attackers to create a new “Technician” account and use it to remote into managed endpoints, execute scripts, and more.
SimpleHelp RMM CVE-2026-48558

Maliciously “forged” Technician account (Source: Horizon3.ai)

The vulnerability

CVE-2026-48558 is an authentication bypass flaw affecting SimpleHelp deployments configured to use OpenID Connect (OIDC) authentication.

“Even when the SimpleHelp server is configured to enforce MFA for technicians, this issue allows the attacker to bypass this mechanism because on first login, technicians can self-register their own MFA method,” Horizon3.ai researchers noted.

Fixes for the vulnerability have been included in SimpleHelp v5.5.16 (stable) and (pre-release) v6.0 RC 2, pushed out in late May 2026.

The vendor said at the time that they were not aware of malicious exploitation of this vulnerability, and urged customers to download and install the appropriate update.

CVE-2026-48558 was discovered by Horizon3.ai researchers with the help of an autonomous vulnerability-hunting AI system, and publicly disclosed last Friday.

Potential for exploitation

Horizon3.ai noted that there are several prerequisites for successful exploitation, namely:

  • At least one OIDC authentication provider is configured on the SimpleHelp server
  • A TechnicianGroup is associated with the OIDC provider
  • The “Allow group authenticated logins” setting is enabled on the TechnicianGroup.

The second of those is expected to be present in any deployment using OIDC authentication, they added, and they found that the latter had been enabled by the clients they assessed.

SimpleHelp noted that an attacker must be able to connect to a server to exploit the vulnerability. “Servers accessible only from local networks or recognised and trusted IP ranges are at much lower risk of exploitation,” they pointed out.

Also, “to log in as a Technician the attacker must be connecting from an IP address permitted by Technician login IP restrictions.”

Horizon3.ai researchers say that the number of SimpleHelp servers exposed on the internet currently reaches nearly 14,000. “A random sampling of these servers indicated that roughly 7.2% of them were configured to use the vulnerable OIDC authentication method,” they added.

Why this matters

SimpleHelp is often used by organizations’ IT help desk and is popular with managed services providers (MSPs).

The three SimpleHelp server vulnerabilities Horizon3.ai reported and disclosed in January 2025 have since been exploited by ransomware attackers.

While the researchers refrained from publishing technical details about CVE-2026-48558, savvy attackers may have enough information to know what to look for and create a working exploit.

SimpleHelp advises admins and security teams to look for evidence of unexpected Technician account creation, logins, sessions, tool runs, especially from unrecognized IP addresses. Evidence of those may be found in the server logs and the Administration settings (under Technicians).

Customers who run an affected SimpleHelp version but cannot immediately upgrade to a fixed version should disconnect their SimpleHelp server from the network (if possible) and make it inaccessible from the internet until they can perform the upgrade.

Subscribe to our breaking news e-mail alert to never miss out on the latest breaches, vulnerabilities and cybersecurity threats. Subscribe here!