






SocGholish, an operation that’s been delivering malware to users via fake software updates, has suffered a major blow: the international law enforcement coalition behind Operation Endgame has taken down 106 of its servers and domains, and cleaned up nearly 15,000 websites compromised to serve their malicious payloads.
The result of this most recent multinational law enforcement action was announced today by the Dutch National Police and on the operation’s website.
More often than not, SocGholish copromises legitimate WordPress sites and injects them with a highly obfuscated JavaScript.
As explained by Proofpoint researchers, the script profiles the potential victim’s browser, makes sure it’s not a developer or site administrator, checks that DevTools aren’t open, and confirms the visitor hasn’t seen the lure before. It also waits for natural mouse movement before acting.
Only once the visitor passes all these checks does the script overwrite the entire page with a fake browser update prompt. If the victim downloads and runs the file, a disguised JavaScript payload silently connects back to attacker-controlled infrastructure, and “delivers” and silently deploys a second-stage payload, usually an infostealer or remote access tool.
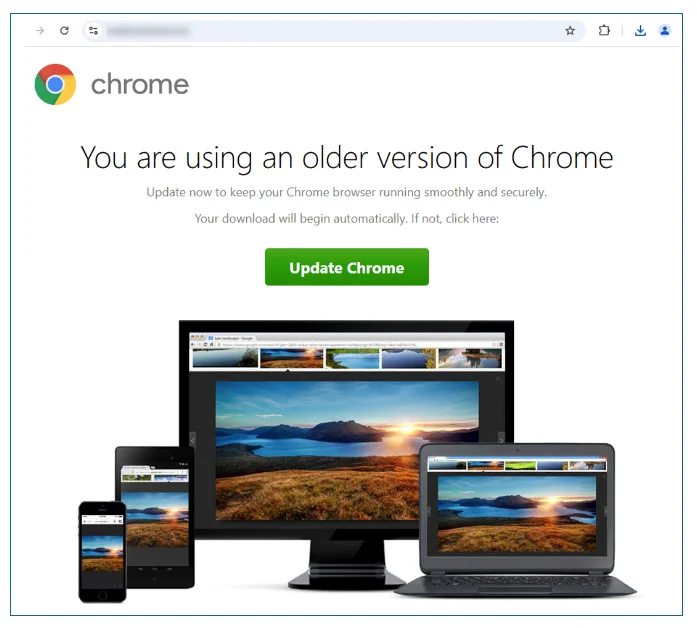
Typical SocGholish fake update lure (Source: Proofpoint)
The SocGholish threat has been around since 2017, and its web inject activity is operated by TA569, which is associated with the Russian cybercriminal group Evil Corp.
“This group has previously been responsible for Zeus and Dridex malware and is also associated with several large‑scale ransomware and money‑laundering operations,” the Dutch Police said.
“For the last nine years, SocGholish, operated by TA569, has posed a major threat to enterprise organizations around the world,” Infoblox’s threat intel team shared.
“As our own analysis shows, nearly 55% of the customer networks in our dataset attempted to reach SocGholish infrastructure during a five-month period. While the overwhelming majority of those attempts did not progress to an active device compromise, we still identified a small number of customer networks potentially impacted by on-device execution of a SocGholish payload.”
The team believes that this law enforcement action will reduce SocGholish activity, but it remains to be seen whether this effect will last.
“The key question now is if and how quickly the actors can adapt: whether they attempt to rebuild the existing ecosystem, shift to alternative infrastructure, or move on to new delivery models,” they commented.
According to Infoblox, TA569 usually compromises websites themselves, but also accepts traffic from affiliates. “Within the research community, it’s believed they could have controlled a million sites during their history,” the researchers noted.
This latest Operation Endgame-related action included notifying the owners of the compromised WordPress sites and helping them clean and secure them.
WordPress site owners are urged to keep their CMS and plugins up-to-date, use strong passwords and enable multi‑factor authentication on their admin accounts, and to delete any unknown additional WordPress accounts they may find.

Subscribe to our breaking news e-mail alert to never miss out on the latest breaches, vulnerabilities and cybersecurity threats. Subscribe here!
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。