






Researchers at Malwarebytes identified dozens of websites claiming to offer free access to FIFA World Cup matches. Instead of streaming games, the sites directed visitors through a chain of advertising pages designed to generate revenue for their operators.
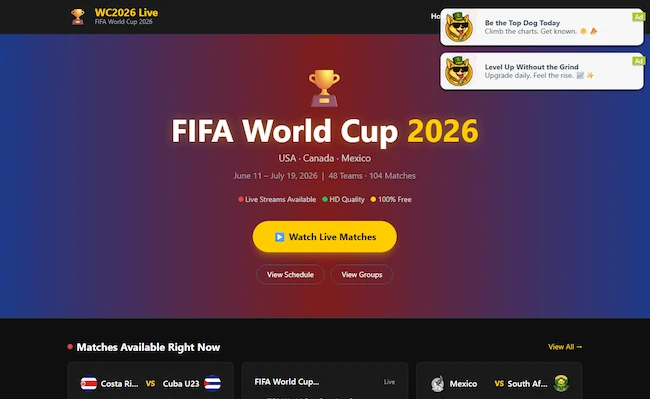
Fake World Cup streaming website (Source: Malwarebytes)
“We’ve identified more than 40 websites that are effectively identical. They use different World Cup-themed names, but behind the scenes they’re running the same page template, the same code, and the same advertising infrastructure,” Malwarebytes wrote.
“This isn’t mainstream, vetted advertising. The kind of ad network we flag as malicious is a common delivery route for the stuff that causes harm: fake virus warnings, bogus software update prompts that install malware, fake prize and verification pages, and forced redirects into subscription traps.”
Researchers found that visitors are pushed through a carefully designed chain of advertising traps before reaching any stream.
The first click is intercepted by a script that opens an advertisement in a new browser tab or window. Users who press the play button are then redirected through a series of prompts and intermediate pages, each generating additional ad impressions.
Some sites also loaded hidden 1×1-pixel advertisements and injected extra ads directly into the video player area. In several cases, the promised stream never appeared, with users instead trapped in loops of “loading” and “retry” messages that encouraged further clicks. By that point, the site’s operators had already generated advertising revenue regardless of whether visitors ever watched a match.
According to Malwarebytes, the advertisements served through the streaming sites generally fall into two categories.
One group consists of fake message notifications designed to resemble legitimate chat alerts. These ads often display profile photos alongside messages intended to create curiosity and encourage users to click.
The second category focuses on cryptocurrency schemes, including so-called play-to-earn platforms that promise daily rewards, token giveaways, airdrops, and unusually high investment returns.
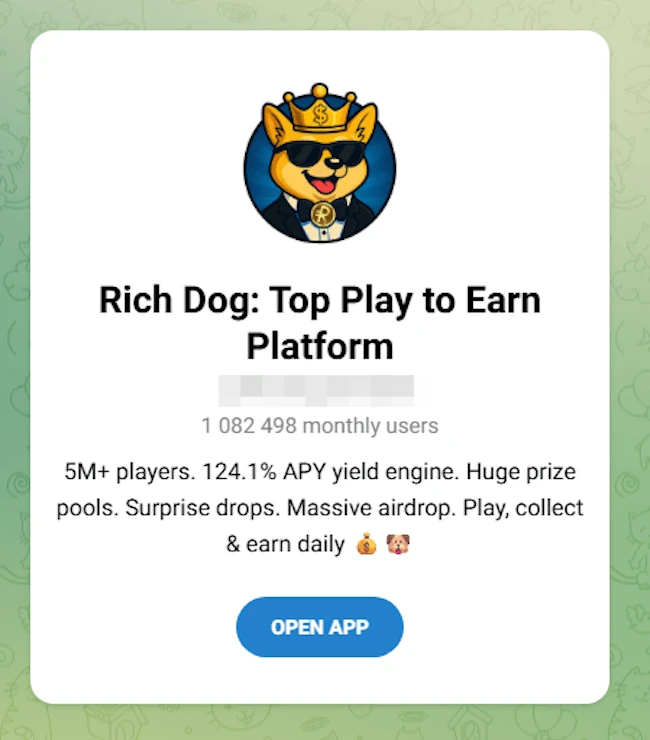
Crypto scheme promoted through a fake streaming site (Source: Malwarebytes)
“One warning sign is the promise of guaranteed triple-digit returns and free money for tapping a button. That’s not how legitimate financial products work,” the researchers added.
Malwarebytes also published indicators of compromise (IoCs) associated with the campaign.
The campaign is far from an isolated case. Earlier this month, Intel 471 reported that roughly 19,000 domains containing references to “FIFA” had been registered since January 2026, with some linked to phishing campaigns targeting fans seeking tickets, merchandise, and other tournament-related content.
Similar concerns have been raised by law enforcement and technology firms. The FBI has warned that cybercriminals are using spoofed FIFA websites, fake ticket sales, and fraudulent hospitality packages to lure victims. Meta, meanwhile, said it worked with Visa to disrupt a scam network that leveraged FIFA World Cup 2026 branding to steer users toward fraudulent gambling websites.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。