



NFC-based payment fraud is expanding geographically and operationally. A campaign active since November 2025 is targeting Android users in Brazil using a new variant of the NGate malware family, this time embedded in a trojanized version of HandyPay, a legitimate NFC relay application available on Google Play since 2021.
ESET Research identified the campaign and attributed two separate NGate samples to the same threat actor. Both samples are distributed from the same domain and use the same modified HandyPay application, indicating a coordinated operation.
The operators behind this campaign could have licensed an existing malware-as-a-service offering to handle the NFC relay function. ESET researcher Lukáš Štefanko, who discovered the new NGate variant in the trojanized NFC payment app, explained the logic directly:
“Why did the operators of this campaign decide to trojanize the HandyPay app instead of going with an established solution for relaying NFC data? The answer is simple: money. The subscription fees for existing MaaS kits run in the hundreds of dollars: NFU Pay advertises its product for almost $400 per month, while TX-NFC goes for around $500 per month. On the other hand, the legitimate HandyPay app is significantly cheaper, only asking for a €9.99 per month donation, if even that. In addition to the price, HandyPay natively does not require any permissions, only to be made the default payment app, helping the threat actors avoid raising suspicion.”
The malicious code injected into HandyPay contains emoji in the log strings, a pattern consistent with output from large language models. ESET assessed that the malware was likely produced with GenAI assistance. Definitive proof of AI involvement remains elusive, per the researchers, though the pattern fits a documented trend of cybercriminals using LLMs to produce working malicious code without deep programming expertise.
The campaign uses two delivery methods. The first is a fake website impersonating Rio de Prêmios, a lottery operated by the Rio de Janeiro state lottery organization. Visitors encounter a scratch card game with a rigged outcome that always produces a win of R$20,000. To claim the prize, users tap a button that opens WhatsApp with a pre-filled message directed to an attacker-controlled number. The associated WhatsApp account uses a profile image impersonating Caixa Econômica Federal, Brazil’s government-owned bank responsible for managing most national lotteries. The victim is subsequently directed to download the trojanized HandyPay APK, which masquerades as the Rio de Prêmios app.
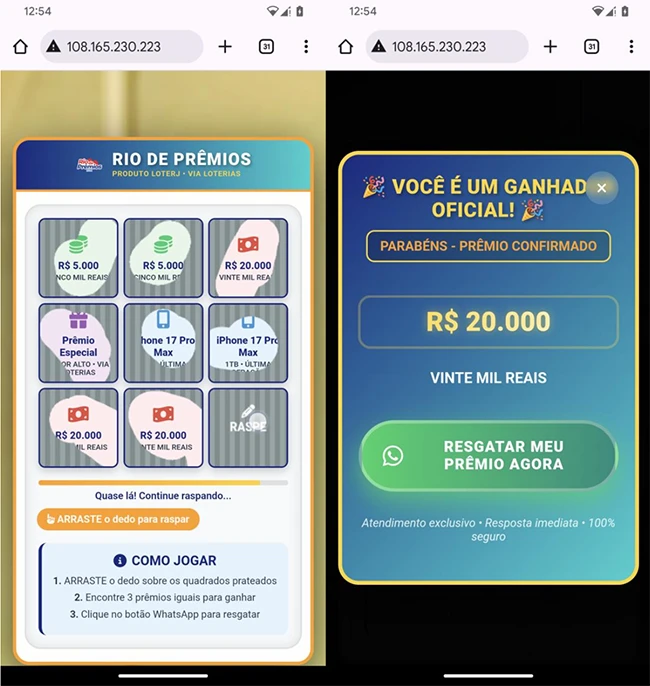
Scratching symbols always results in winning R$20,000 (left), with the victim being invited to launch WhatsApp via a button saying “Redeem my prize now” to claim their prize (right). Source: ESET
The second vector is a fake Google Play webpage distributing the malware under the name Proteção Cartão, which translates to Card Protection. Victims must manually download and install the APK after bypassing Android’s sideloading warning.
Once installed, the app requests to be set as the default NFC payment app, functionality that exists in the legitimate HandyPay application. The app then prompts the victim to enter their payment card PIN and tap their card to the device with NFC enabled. The malware relays NFC card data to an attacker-controlled device, which can then execute contactless transactions and ATM withdrawals using the victim’s card credentials.
The victim’s PIN is exfiltrated separately over HTTP to a dedicated command-and-control server, independent of HandyPay’s infrastructure. That same C&C server also serves as the distribution endpoint for the APK files, centralizing delivery and data collection in a single server.
ESET found logs from four compromised devices on the attacker’s C&C server, all geolocated in Brazil, containing captured PINs, IP addresses, and timestamps.
The trojanized HandyPay application has never appeared on the official Google Play store. ESET notified Google through the App Defense Alliance and also contacted the HandyPay developer directly. The developer confirmed an internal investigation is underway.

此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。