


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

H
Help Net Security
博客园_首页
酷 壳 – CoolShell
酷 壳 – CoolShell
G
Google Developers Blog
Jina AI
Jina AI
C
Check Point Blog
Apple Machine Learning Research
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
GbyAI
GbyAI
Last Week in AI
Last Week in AI
罗磊的独立博客
Hugging Face - Blog
Hugging Face - Blog
阮一峰的网络日志
阮一峰的网络日志
The Cloudflare Blog
M
MIT News - Artificial intelligence
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
J
Java Code Geeks
WordPress大学
WordPress大学
博客园 - 聂微东
月光博客
月光博客
博客园 - 司徒正美
T
The Blog of Author Tim Ferriss
大猫的无限游戏
大猫的无限游戏
Microsoft Security Blog

Help Net Security

ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security Acronis GenAI Protection gives MSPs control over AI usage and data risks - Help Net Security
Apple makes its quantum-resistant encryption open source
Anamarija Pogorelec · 2026-05-27 · via Help Net Security

Apple has published its post-quantum cryptography implementations in corecrypto, together with mathematical proofs and verification tools for independent expert evaluation, allowing external researchers to review the work and reproduce the company’s analysis.

Post-quantum cryptography is designed to protect encrypted data from future quantum computers that could break widely used public-key encryption algorithms.
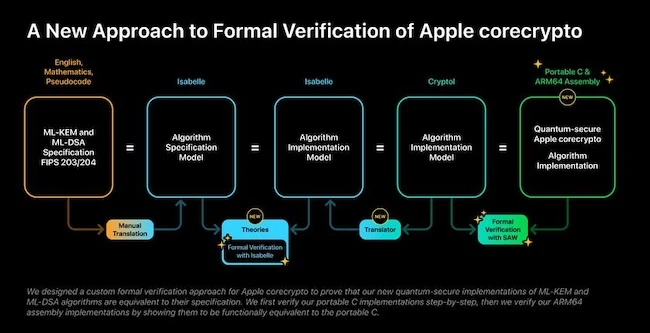
Apple encryption open source

A new approach to formal verification of Apple corecrypto (Source: Apple)

Corecrypto, the cryptography library used throughout Apple operating systems and services, provides encryption, hashing, random number generation, and digital signatures on more than 2.5 billion active devices. The company added post-quantum cryptography support to the library in 2024 for applications that handle encrypted communications and sensitive data, including iMessage, VPNs, and TLS networking.

“A critical bug in corecrypto has the potential to compromise the security and reliability of every app and feature that depends on it, so we are conservative when adding new code to the library and make exceptional efforts to be comprehensive in our testing,” Apple said.

Because the library runs on different Apple devices and chips, Apple writes its cryptographic code in portable C to ensure consistent behavior on all platforms. The company said it applies protections against timing attacks and may randomize some internal computations to make attacks harder.

How the verification system works

Formal verification uses mathematical methods to prove that software behaves as intended under defined conditions.

ML-KEM and ML-DSA, post-quantum algorithms standardized by NIST, were selected for their security, performance, compact key and ciphertext sizes, and functional correctness. The implementations were validated through conventional testing, simulation, independent review, and formal verification.

After evaluating existing verification tools and verified implementations, Apple built a custom system that supports multiple programming languages, codebases, and existing developer workflows.

The framework combines existing and newly developed tools to verify the implementations against official FIPS standards. Galois, a research and engineering company specializing in formal verification, collaborated with Apple to develop a tool that generates Isabelle theories from Cryptol models and connects portable C with Cryptol. Apple also developed Isabelle libraries and hand-optimized ARM64 assembly subroutines.

The Cryptol-to-Isabelle translator allows Cryptol models to be recreated in Isabelle for independent analysis.

The verification process identified issues that conventional testing would likely not have detected. One issue involved a missing step in an early ML-DSA implementation that, in rare cases, could cause inputs to exceed the expected range and produce incorrect output. The flaw was identified and fixed before deployment.

“We believe that the strongest assurance possible comes from combining formal verification with conventional methods and critically evaluating the end-to-end results,” the company added.