


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

C
Check Point Blog
有赞技术团队
有赞技术团队
博客园 - 三生石上(FineUI控件)
博客园_首页
博客园 - 【当耐特】
WordPress大学
WordPress大学
月光博客
月光博客
博客园 - 叶小钗
S
SegmentFault 最新的问题
雷峰网
雷峰网
H
Help Net Security
宝玉的分享
宝玉的分享
A
About on SuperTechFans
IT之家
IT之家
J
Java Code Geeks
Hugging Face - Blog
Hugging Face - Blog
D
DataBreaches.Net
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园 - 聂微东
T
The Blog of Author Tim Ferriss
B
Blog
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
H
Hackread – Cybersecurity News, Data Breaches, AI and More
Y
Y Combinator Blog

Help Net Security

ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security Acronis GenAI Protection gives MSPs control over AI usage and data risks - Help Net Security
Ransomware gangs find Europe's weakest link in third-part...
Anamarija Pogorelec · 2026-06-26 · via Help Net Security

Ransomware attacks against European organizations increased during the first months of 2026, with third-party suppliers becoming a major entry point for attackers. Black Kite examined 2,066 ransomware incidents across 31 countries between January 2025 and April 2026 in its 2026 European Cyber Risk Report.
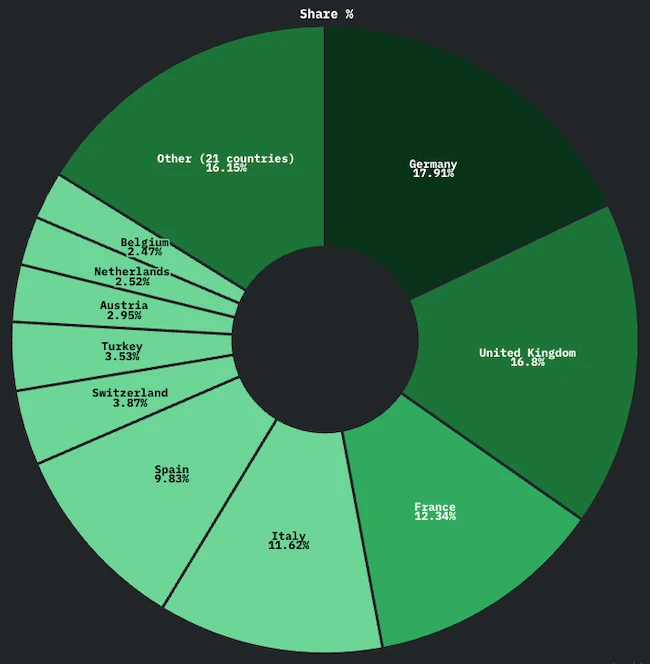
European cyber threats

Country distribution of ransomware attacks (Source: Black Kite)

“Three forces are converging on European organisations at once: ransomware is accelerating, supply chains are becoming a primary attack path, and regulations are placing greater emphasis on third-party risk,” said Dr. Ferhat Dikbiyik, Chief Research and Intelligence Officer, Black Kite.

Publicly disclosed incidents increased 55.1% between January and April 2026 compared with the same period in 2025. The average monthly number of incidents rose from 108 during the first half of 2025 to 171 during the first four months of 2026.

Germany recorded the highest number of incidents. The UK, France, Italy, and Spain followed. These five countries accounted for nearly 70% of all recorded ransomware incidents. Manufacturing was the hardest-hit sector. IT services ranked among the primary targets because attacks on service providers can affect many downstream customers.

The Qilin ransomware group operated in 26 of the 31 countries included in the analysis, giving it the widest geographic reach of the ransomware groups covered by the research.

Manufacturing accounts for the largest share of incidents

Manufacturing accounted for 27.9% of publicly disclosed ransomware incidents, making it the most targeted industry. IT services ranked as the most targeted subindustry because compromising a single provider can give attackers access to multiple downstream customers. Professional services, healthcare, retail, and transportation also remained frequent ransomware targets as cybercriminals increasingly focused on organizations with broad digital connections and high operational impact.

Third-party compromises are becoming a major source of cyber risk across Europe. Instead of attacking organizations directly, cybercriminals target suppliers and service providers to reach multiple victims through a single breach.

The report identified 64 organizations that were compromised through third-party incidents. In one case, a breach at a software provider affected dozens of downstream organizations and exposed the personal data of more than one million people, demonstrating how a single supplier can trigger widespread disruption.

Regulations place greater emphasis on supplier security

European cybersecurity regulations are making organizations more accountable for the cyber risks posed by their suppliers. Frameworks including NIS2 and DORA require organizations to assess, monitor, and manage supplier cyber risk as part of operational resilience programs. Organizations must demonstrate that they understand how supplier vulnerabilities could affect their operations and have processes in place to identify, assess, and reduce those risks

Dikbiyik said some of Europe’s most significant ransomware incidents were defined by their downstream impact across interconnected organizations. He added that NIS2 and DORA were increasing pressure on organizations to better understand cyber risk across their supplier ecosystems and identify where risk is concentrated.