


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

V
Visual Studio Blog
爱范儿
爱范儿
GbyAI
GbyAI
博客园 - 叶小钗
Last Week in AI
Last Week in AI
Jina AI
Jina AI
Microsoft Security Blog
云风的 BLOG
云风的 BLOG
C
Check Point Blog
H
Help Net Security
P
Proofpoint News Feed
酷 壳 – CoolShell
酷 壳 – CoolShell
让小产品的独立变现更简单 - ezindie.com
大猫的无限游戏
大猫的无限游戏
H
Hackread – Cybersecurity News, Data Breaches, AI and More
B
Blog RSS Feed
Y
Y Combinator Blog
U
Unit 42
T
Tailwind CSS Blog
MyScale Blog
MyScale Blog
N
Netflix TechBlog - Medium
S
SegmentFault 最新的问题
J
Java Code Geeks
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知

Help Net Security

Your work apps are quietly handing 19 data points to someone ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security Acronis GenAI Protection gives MSPs control over AI usage and data risks - Help Net Security
Shadow AI risks deepen as 31% of users get no employer tr...
Anamarija Po · 2026-05-01 · via Help Net Security

Between one-fifth and one-third of workers use AI outside the influence and governance of the IT function, according to a global survey of 6,000 full-time employees at enterprise organizations. Researchers found a widening gap between employee AI adoption and the controls organizations have in place to manage it.
shadow AI risks

The Lenovo Work Reborn Research Series 2026 report documents a workforce split into two groups: employees equipped with IT-managed tools, training, and oversight, and those operating independently with consumer AI services.

Training and tooling gaps drive unsanctioned use

Many employees report that their employers fail to supply either AI tools or training, and a sizable share of those who receive training describe it as irregular or ineffective. Half of all employees say better training would help them get more value from AI at work, pointing to a workforce ready to adopt AI faster than its employers can equip it.

Employee enthusiasm for AI continues to climb. Seven in ten use AI tools at least a few times a week, and 80% expect their use of AI to increase over the next year. Lenovo’s research indicates that adoption is outpacing the capacity of enterprises to manage, enable, or align it.

Security implications of unmanaged adoption

The report identifies two security concerns tied to shadow AI. Bypassing compliance controls increases the risk that intellectual property or sensitive data are processed outside governed environments. Fragmented workflows produce inconsistent execution and uneven distribution of productivity gains across teams.

Employee trust in enterprise-provided tools shows measurable cracks. A meaningful share of employees doubt the reliability of information produced by employer-provided AI tools, and a smaller group questions whether their privacy and personal data are safe when using them.

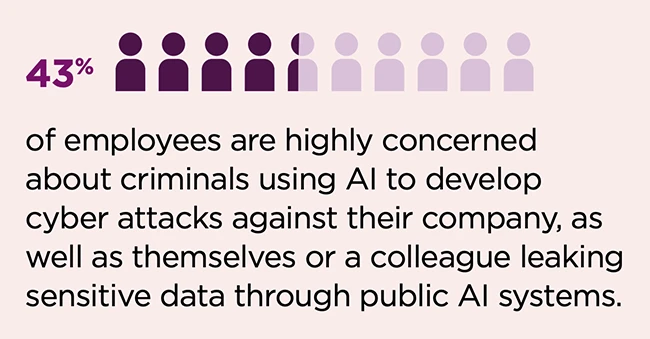
Cybersecurity awareness among employees is uneven. Nearly half of employees are highly concerned about criminals using AI to develop sophisticated cyber attacks against their company, and the same percentage are highly concerned about themselves or a colleague accidentally leaking sensitive company information through public AI systems such as ChatGPT. Forty percent are highly concerned about deepfake videos and AI-generated phishing emails. Only 23% are highly concerned about criminals attacking their company’s AI systems directly, a gap that becomes consequential as organizations deploy AI agents and internal AI infrastructure.

These employee perceptions track with separate findings from Lenovo’s CIO Playbook, which reports that 61% of IT leaders say AI is increasing cybersecurity risks and only 31% are confident in their ability to address those risks.

What employees want from security teams

Seventy-four percent of employees say more or better cybersecurity training on AI-related risks would reassure them that they and their organization are protected. Seventy-three percent say it would be reassuring to know their company’s cybersecurity team is using AI to address these risks. Seventy percent say stricter policies on how employees can use AI would provide reassurance.

The report recommends building governance before scaling AI, embedding security awareness into the flow of work through continuous in-context learning, and standardizing the AI interface across workflows and endpoints.

Webinar: The IT Leader’s Guide to AI Governance