










Visibility across devices, identities, SaaS, and exposures inside Elastic Security

Security teams cannot protect what they cannot see, such as reconciling devices, identities, applications, SaaS, and exposures across hybrid cloud, on-prem, and OT from dozens of tools. Axonius specializes in aggregating and correlating that asset intelligence so that IT, security, and governance, risk, and compliance (GRC) teams get a coherent view of the environment.
Today, we are announcing an integration with Axonius that brings normalized asset context into Elastic, so analysts can search, correlate, and investigate Axonius data alongside endpoint alerts, network telemetry, identity events, and the rest of your Elastic Security data.
Agentless setup
The Axonius integration supports both agent-based and agentless deployments. Agentless ingestion is supported on Elastic Cloud Serverless and Elastic Cloud Hosted, which reduces the operational overhead of maintaining and managing dedicated agents and the underlying infrastructure to support them.
What the integration collects
The Axonius integration periodically queries Axonius APIs and writes normalized documents into Elasticsearch across several data streams. Each stream represents a distinct category of asset intelligence, and together, they fill gaps that traditional agent-based telemetry alone can’t cover.
Application visibility (axonius.application)
This is the richest data stream for security analysts. Rather than a single endpoint, it aggregates across Axonius's full application surface: installed software, SaaS applications, licenses, browser extensions, audit activity, business application metadata, secrets, and URLs spanning both managed and unmanaged territory.
Key fields include audit_activities (actions like login, create, update, delete, reset_password tied to specific users and applications), extension metadata differentiating IT-deployed versus user-installed tooling, and SaaS footprint data across your identity and application landscape.
Users (axonius.user)
User records are normalized to ECS user.* fields. Because Axonius aggregates across HR systems, directories, SaaS platforms, and security tools, these records frequently surface accounts not visible through any single source like orphaned identities, service accounts, or users present in one system but absent in another.
Vulnerabilities and exposures (axonius.exposure)
These vulnerability-oriented events with CVE and CVSS fields are mapped to ECS vulnerability.*. Exposure data reflects what's been correlated across your connected tools, meaning the same CVE can be tied to asset ownership, business criticality, and control coverage in the same record.
Security incidents and findings (axonius.incident, axonius.alert_finding)
Incidents and findings from connected tools, including cloud workload alerts, adapter health failures, and platform-level findings, are enriched with severity, recommendation text, and MITRE-oriented labels where applicable. These records are tagged event.kind: alert, making them compatible with Elastic detection rule workflows.
Infrastructure and operational context (axonius.storage, axonius.ticket, axonius.adapter, axonius.gateway)
Cloud and object storage assets, ITSM tickets with status and priority timelines, adapter connection health, and gateway metadata are also included. The adapter health stream (axonius.adapter) is worth particular attention as it indicates when a data source goes silent, which is often the first signal that coverage has drifted.
From alert to investigation with ES|QL and Workflows
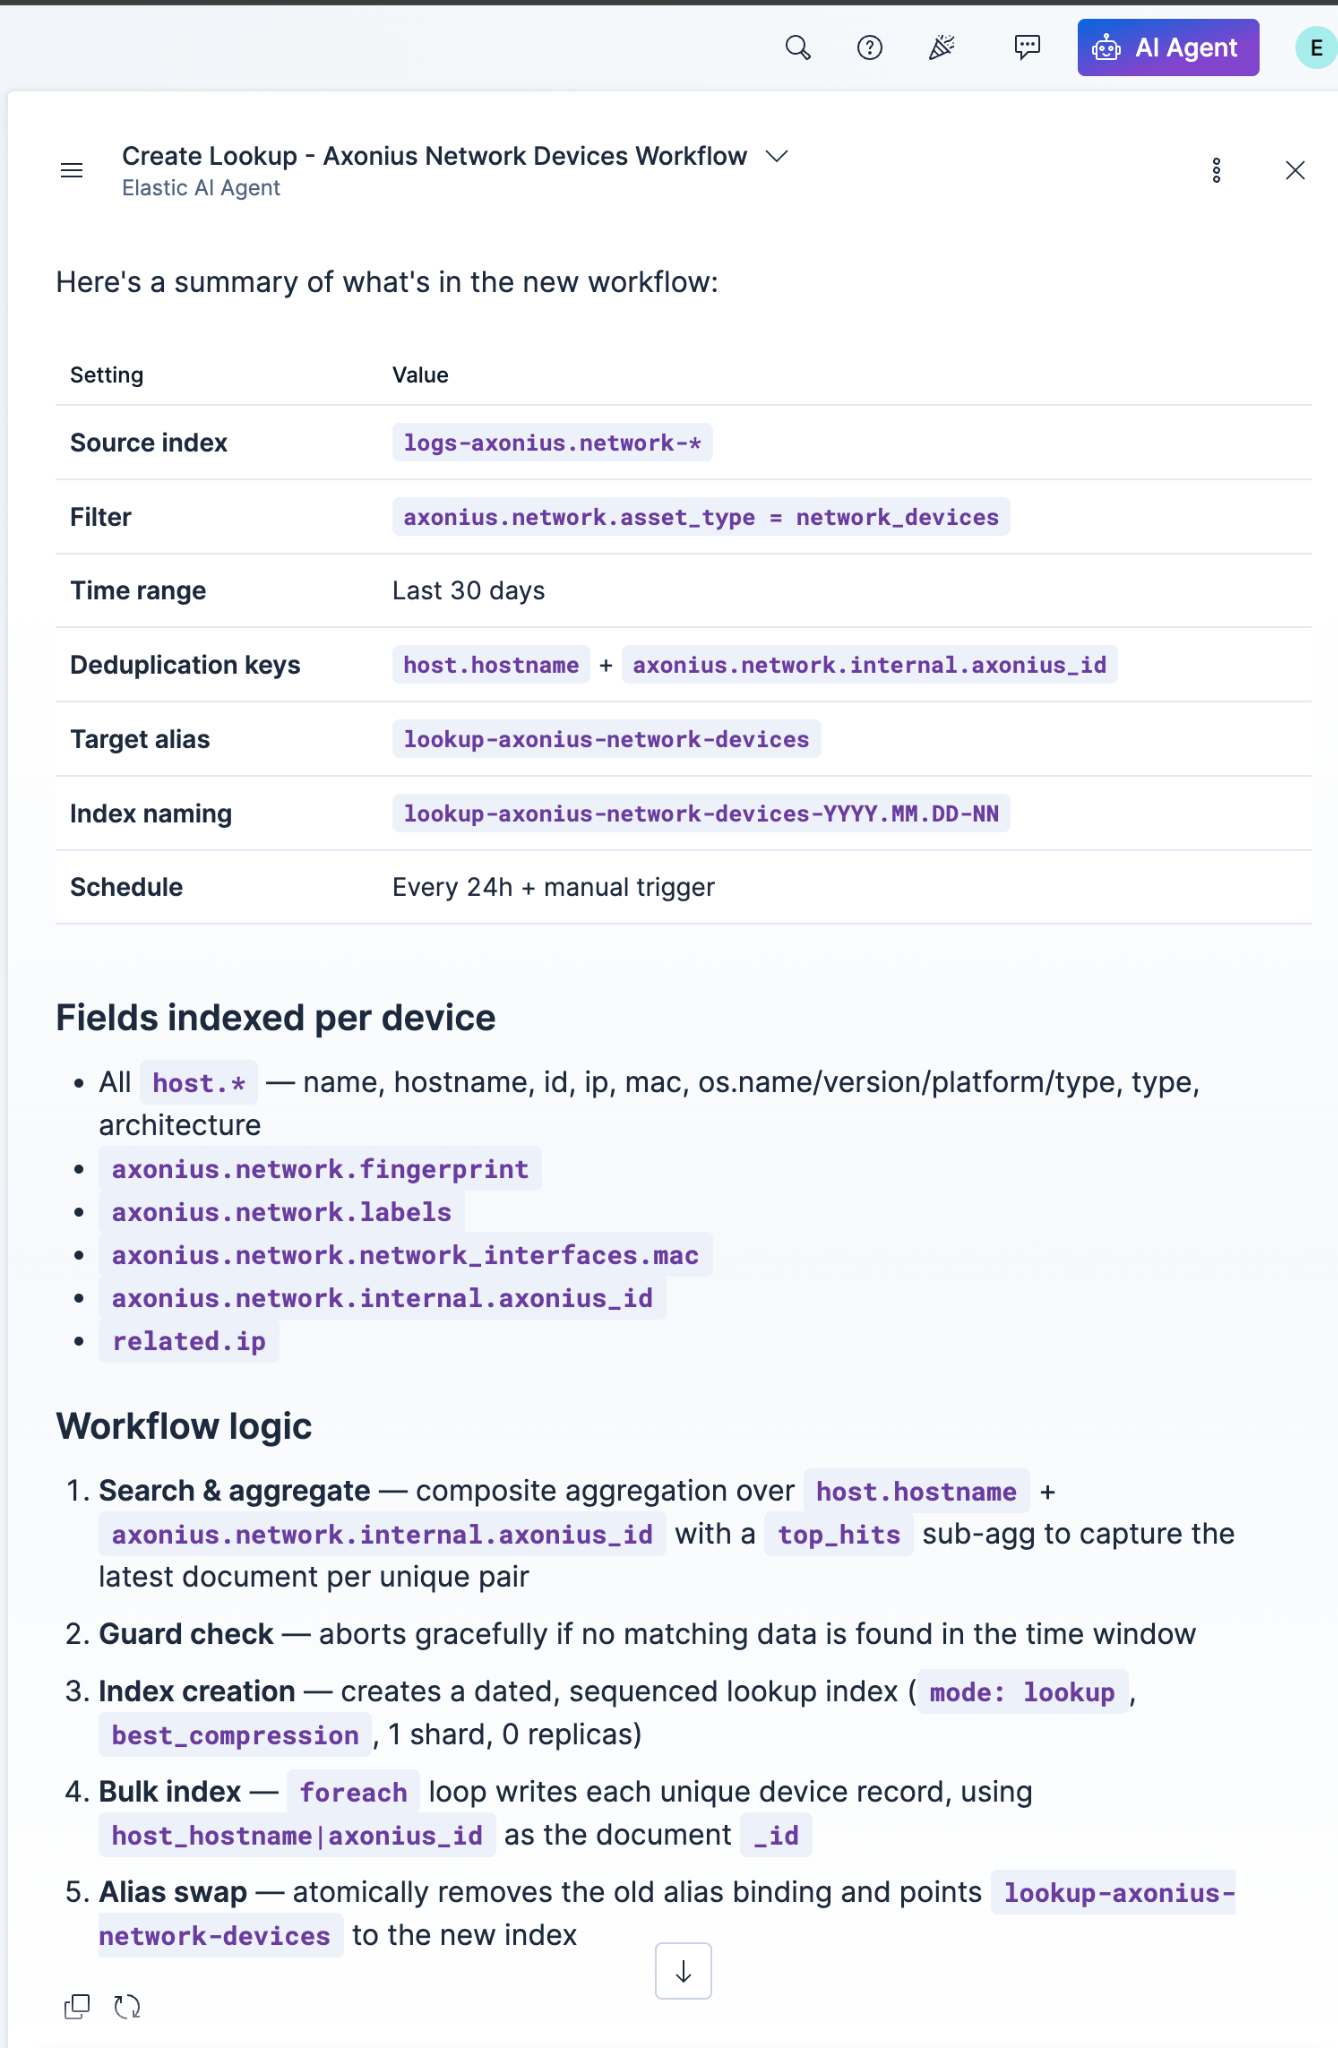
Elastic Workflows can automate asset enrichment so that every Elasticsearch Query Language (ES|QL) query runs against a live, pre-built lookup index, removing manual lookups and tool switching. Workflows periodically searches the Axonius asset data and writes it to a dedicated index set to lookup mode. That lookup index can then be referenced in ES|QL queries to enrich logs and alerts with asset context on the fly, correlating events with attributes like device owner, business unit, or risk score without any manual lookups.
When threat hunting or working an investigation, raw log data can’t tell you who owns a device, what software is running on it, and whether it meets compliance baselines. Axonius supplies that context.
ES|QL LOOKUP JOINS
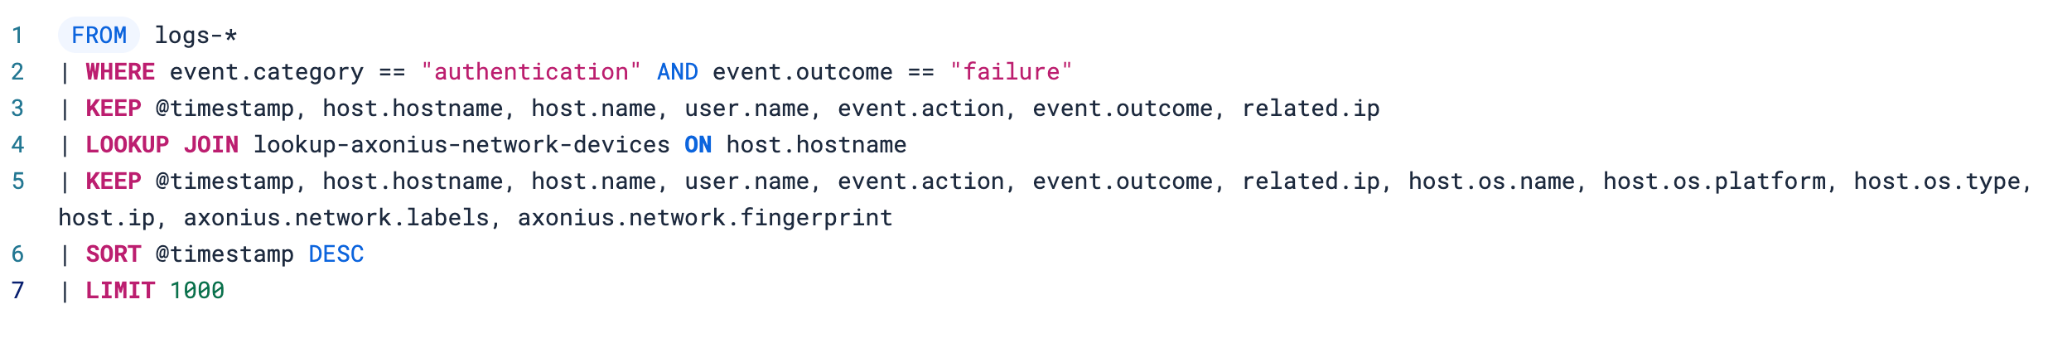
Here’s an example ES|QL query enriching context from Axonius asset data onto failed authentication events using the lookup index created by the workflow.
Elastic Agent Builder
Analysts can also use the Elastic Agent Builder to build workflows through natural language: describing the automation they need, iterating in chat, and skipping the manual configuration entirely.
Operationalize asset intelligence directly inside Elastic Security
Integrating Axonius with Elastic gives security teams a unified view of their environment by bringing normalized asset intelligence, including covering devices, identities, applications, vulnerabilities, and exposures, directly into Elastic Security. With automated lookup index enrichment via Elastic Workflows and ES|QL for on-the-fly correlation, analysts can move faster from alert to investigation with full asset context at their fingertips. The result: analysts spend less time assembling context and more time on the investigations that matter.
Learn more about the Axonius integration and try it out today.
The release and timing of any features or functionality described in this post remain at Elastic's sole discretion. Any features or functionality not currently available may not be delivered on time or at all.
In this blog post, we may have used or referred to third party generative AI tools, which are owned and operated by their respective owners. Elastic does not have any control over the third party tools and we have no responsibility or liability for their content, operation or use, nor for any loss or damage that may arise from your use of such tools. Please exercise caution when using AI tools with personal, sensitive or confidential information. Any data you submit may be used for AI training or other purposes. There is no guarantee that information you provide will be kept secure or confidential. You should familiarize yourself with the privacy practices and terms of use of any generative AI tools prior to use.
Elastic, Elasticsearch, and associated marks are trademarks, logos or registered trademarks of elasticsearch B.V. in the United States and other countries. All other company and product names are trademarks, logos or registered trademarks of their respective owners.