







For organizations in highly regulated industries, any misconfiguration in their cloud environments can be detrimental to customer trust and privacy if overlooked. To mitigate this risk, DevOps and security engineers follow recognized compliance standards to quickly surface issues in their AWS, Azure, or Google Cloud environments. Organizations can take this work a step further by developing detection rules tailored to their unique business or security goals.
Datadog Cloud Security provides more than 250 out-of-the-box rules that are mapped to industry-standard compliance frameworks like SOC 2, PCI-DSS, and ISO. Now, you can clone and modify any of these rules—or create your own—to match your organization’s cloud security practices, regardless of cloud provider. This level of control enables you to enforce customized standards, create security-related alerts on resource configurations, and focus on the findings that matter most to your organization.
In this post, we’ll show you how to:
Write rules for detecting misconfigurations in cloud resources with Rego, an industry-standard query language
Test detection rules on your cloud infrastructure before publishing them
Customize detection alerts and route them to the appropriate teams for remediation
With Datadog Cloud Security, you can build from an existing, comprehensive list of detection rules in order to develop compliance controls that are specific to your environment. This enables you to quickly surface misconfigurations in your cloud resources, like obsolete IP addresses, out-of-date compute instances, open database ports, and more.
To get started, you simply need to click the “New Rule” button at the top-right corner of the Detection Rule page or the three-dot menu next to a rule, as seen in the following screenshot:
On the configuration page, you can customize a rule’s scope, logic, and alert message. Cloning a rule will copy all of its properties and logic, including its name, description, remediation steps, and tags, but you can customize this information to fit your needs.
For a brand-new rule, first select the cloud provider and resource type(s) to define its scope. You can also select multiple resource types by clicking the “Advanced Rule Options” dropdown, as seen in the following screenshot:
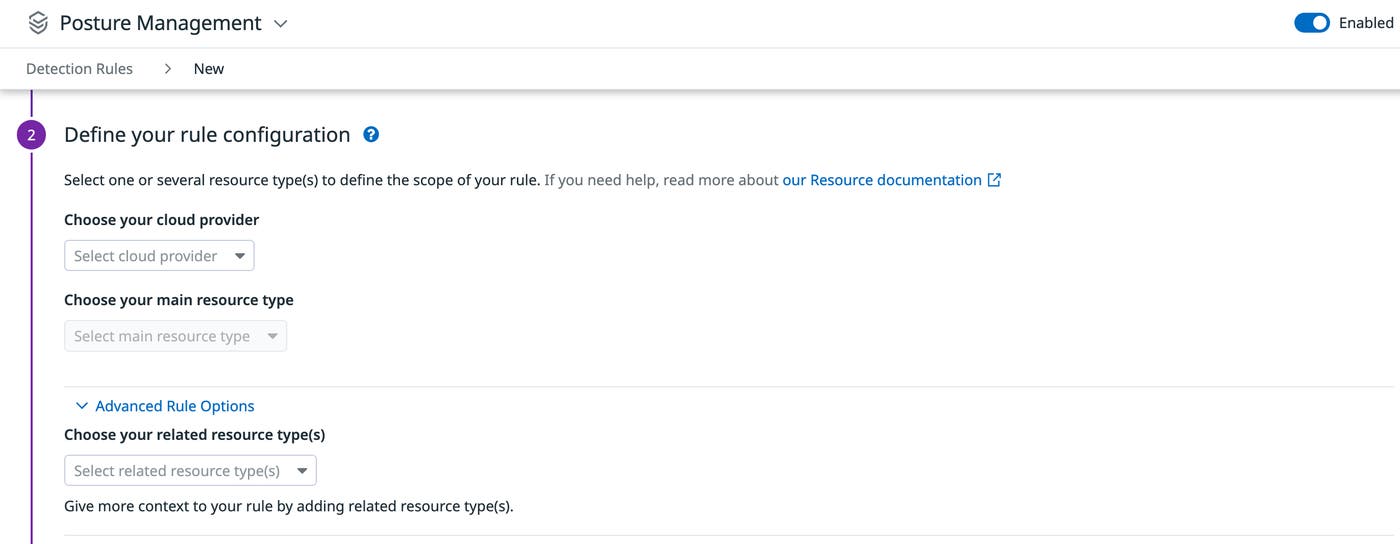
Next, you can customize your rule’s logic using Rego, a query language for developing efficient policy-as-code workflows. Datadog provides boilerplate code to help you get started, but you can check out our documentation to learn more about Rego’s capabilities. The following configuration example checks if access keys are rotated every 60 days or less for all aws_iam_user resources:
package datadog
import data.datadog.output as dd_output
import future.keywords.contains
import future.keywords.if
import future.keywords.in
sixty_days_ms := (((60 * 24) * 60) * 60) * 1000
more_than_sixty(timestamp, resource_seen_at) if {
resource_seen_at - timestamp > sixty_days_ms # Not rotated in last 60 days
}
active_and_rotated_more_than_60(credential_report, resource_seen_at) if {
credential_report.access_key_1_active
more_than_sixty(credential_report.access_key_1_last_rotated, resource_seen_at)
} else if {
credential_report.access_key_2_active
more_than_sixty(credential_report.access_key_2_last_rotated, resource_seen_at)
}
eval(iam_user) = "pass" if {
resource_seen_at := iam_user.resource_seen_at
some credential_report in iam_user.credential_report
not active_and_rotated_more_than_60(credential_report, resource_seen_at)
} else = "fail"
# This part remains unchanged for all rules
results contains result if {
some resource in input.resources[input.main_resource_type]
result := dd_output.format(resource, eval(resource))
}
The rule editor provides a built-in syntax validator, which you can use at any time by clicking the “Check Syntax” button. If there is an issue, the editor will automatically highlight the affected line of code and provide more context to help you find the root cause of the error.
Once you create a rule, it’s important to verify that it works for your targeted cloud resources. Otherwise, you will not be able to reliably surface misconfigurations when they happen. You can test your rule against all relevant cloud resources directly in the editor before publishing it. Using our previous example, the following screenshot illustrates how Datadog Cloud Security tests the rule against all available aws_iam_user resources:
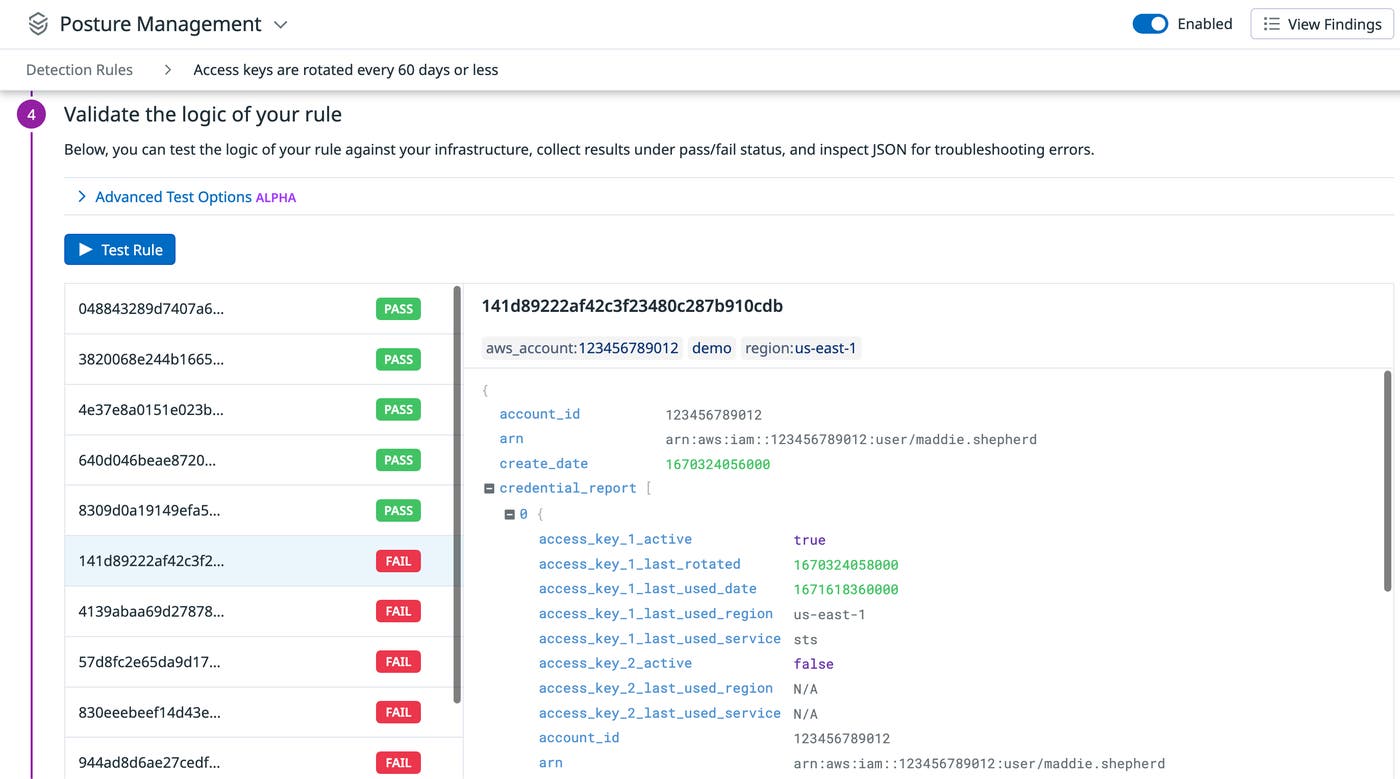
In this example, the rule’s logic calculates if an access key was rotated within the last 60 days by subtracting the ISO 8601-formatted timestamp of when it was created or last changed from when it was last active. With each evaluation, Datadog Cloud Security includes the information you need to quickly verify a rule’s accuracy, such as the resource’s name, its relevant tags, and other configuration data. This data ensures that you can quickly validate your rule’s logic and be confident that it is accurate before publishing it.
A key part of efficiently remediating cloud misconfigurations is providing the right context when they are detected. This means setting the appropriate level of severity for alerts, ensuring that they are routed to the right team, and providing them with enough information to resolve the issue. Datadog Cloud Security enables you to add a severity level to alerts and configure them to automatically notify any team, as seen in the following screenshot:
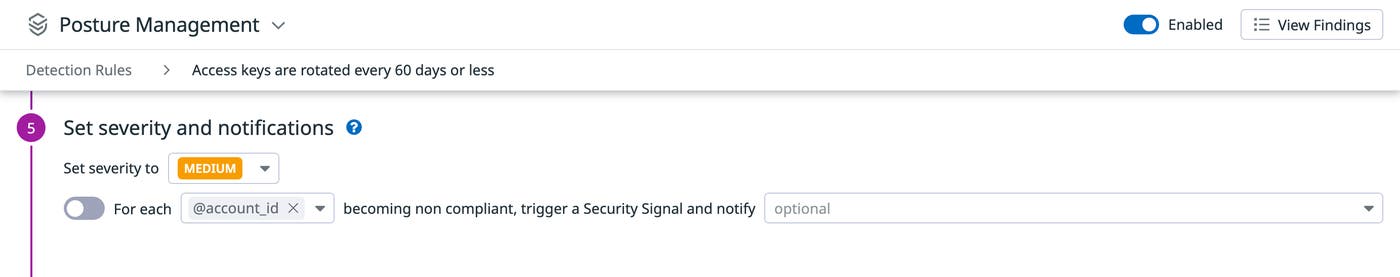
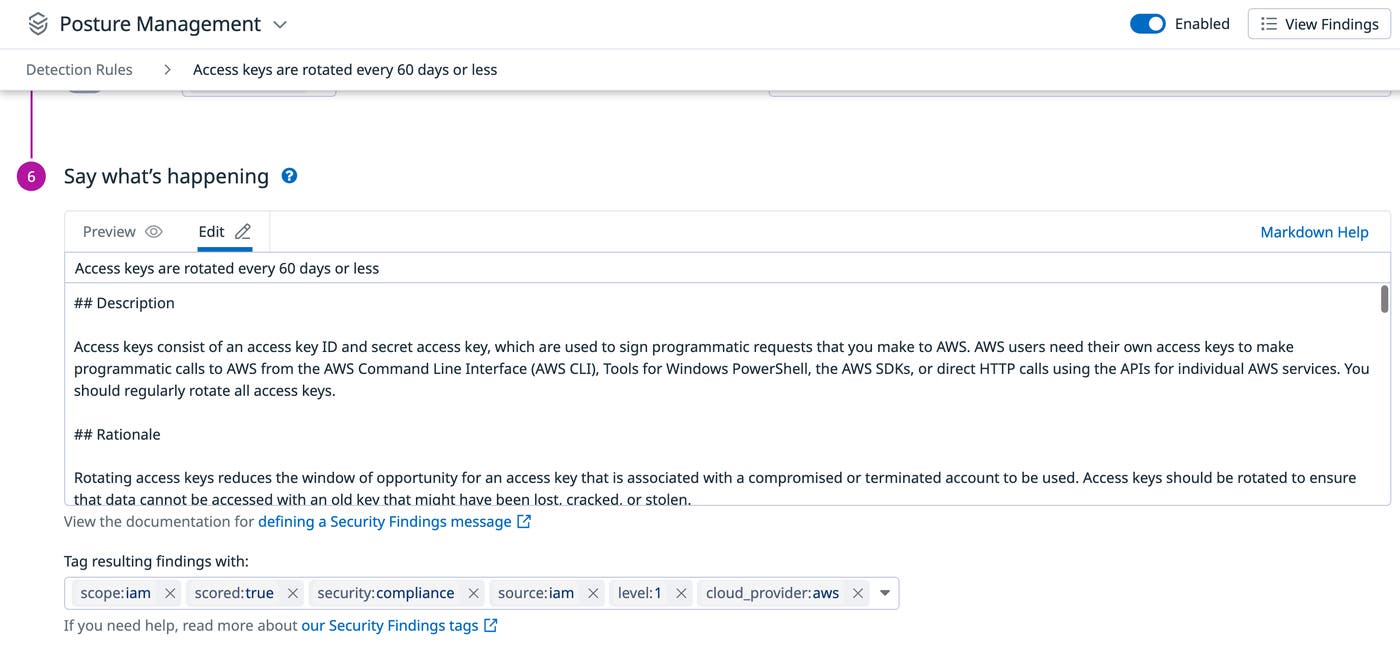
Rules can be configured to send notifications via popular communication channels like Slack and Jira, which ensures that your teams are alerted in a timely and efficient manner. Finally, you can include the exact steps for remediation in the rule’s notification message and tags to generate a context-rich notification for your selected teams, as seen below:
Datadog Cloud Security allows you to easily fine-tune and test the rules for detecting misconfigurations across your AWS, Azure, and Google Cloud environments. Drafting rule logic is quick and simple—Datadog provides you with the ability to customize more than 250 out-of-the-box rules or write rules from scratch using the Rego query language. Datadog Cloud Security takes these capabilities a step further by providing your security and DevOps teams with shared context for quickly identifying the impact of threats on your cloud resources.
Check out our documentation to learn more, or self-enroll to get started—you can publish custom detection rules within minutes of enrolling. If you don’t already have a Datadog account, you can sign up for a free 14-day trial today.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。