





Google Workspace is a popular productivity suite, and its broad collection of apps (such as Gmail, Drive, Calendar, and Docs) can give attackers a central point of entry for accessing sensitive and valuable data if they compromise an account. Learning how to identify malicious activity in your Workspace environment enables you to stop threats before they become more serious. In this post, we’ll look at a few ways attackers gain access to and take advantage of Google Workspace. We’ll also show how Datadog Cloud SIEM provides visibility into their attack paths.
According to our most recent cloud security report, attackers tend to follow predictable patterns when targeting cloud services such as Microsoft 365 and Google Workspace. Compromising credentials, phishing, and deploying malicious OAuth applications are three of the most common types of cloud-based attacks, and each type can escalate to account takeovers, business email compromise, and more. You can look for signs of these attacks in the following key areas of Google Workspace that attackers routinely target:
Gmail: Stores sensitive communications
User accounts: Contain both organizational and personal data
Devices: Increases the number of entry points for unauthorized access
Administrators: Modifies access and permissions for accounts, services, and resources
Attackers can take advantage of Gmail in a few ways. At the start of an attack, for example, they often send emails to users as part of their phishing campaigns, asking them to provide sensitive information or click on malicious links or attachments in order to gain access to their accounts. To make the campaign more believable, an attacker may spoof a legitimate user from the target’s address book to trick them into sharing account credentials.
If an attacker has access to a user account and services, they may attempt to change account settings, elevate privileges, or determine if they can exfiltrate any available data from sources like the user’s inbox. For example, with access to a user’s inbox, an attacker may forward email containing sensitive information to a domain outside of Google Workspace. This kind of activity can initially look like typical behavior, so it’s important to monitor other events from that user, such as logins from new, unusual locations, to determine if the account is compromised.
User accounts give attackers access to sensitive data, and can provide a stepping stone for additional attacks (like privilege escalation). Surfacing malicious activity like this from a user’s day-to-day activity can be difficult, but there are a few signs to look out for. For example, an increase in the number of failed login attempts from a specific user could indicate an attempt to compromise an account. Other indications of suspicious activity include logging in from an atypical location for the user (e.g., impossible travel) or interactions with Tor clients. Attackers may use Tor clients, for example, to hide their identity.
After an account is compromised, an attacker will often change account settings in order to maintain persistence. Activity to look out for in this scenario includes disabling two-step verification and changing recovery settings, which would allow an attacker to easily log back in to an account if needed.
In addition to user activity, it’s important to monitor activity from user devices. Many organizations enable users to connect to Google Workspace apps via their personal devices in addition to their company-issued laptops. This capability creates additional risk because compromised devices, such as those that are rooted or jailbroken, can give an attacker access to linked accounts. A common sign of compromise in these scenarios includes an attacker removing a linked device from Google Workspace’s Advanced Protection Program, which provides security measures for protecting against targeted attacks.
Administrative accounts offer greater control over an environment and its resources, making them another common target for attackers. As a starting point, they may attempt to elevate privileges from user accounts or devices they’ve already compromised in order to execute admin-level activity. Or, they may successfully gain access to an administrator account directly through the same methods used to compromise other accounts, such as phishing.
To detect admin-related activity, it’s important to track changes to app settings—like global Calendar or two-step verification settings—as well as user permissions. For example, you can look out for new admin roles or users who are assigned an existing admin or super admin role.
Attackers may also attempt to use admin permissions to exfiltrate data. An admin requesting a data transfer to another user, for example, could indicate an attempt to move sensitive data to an account that the attacker controls.
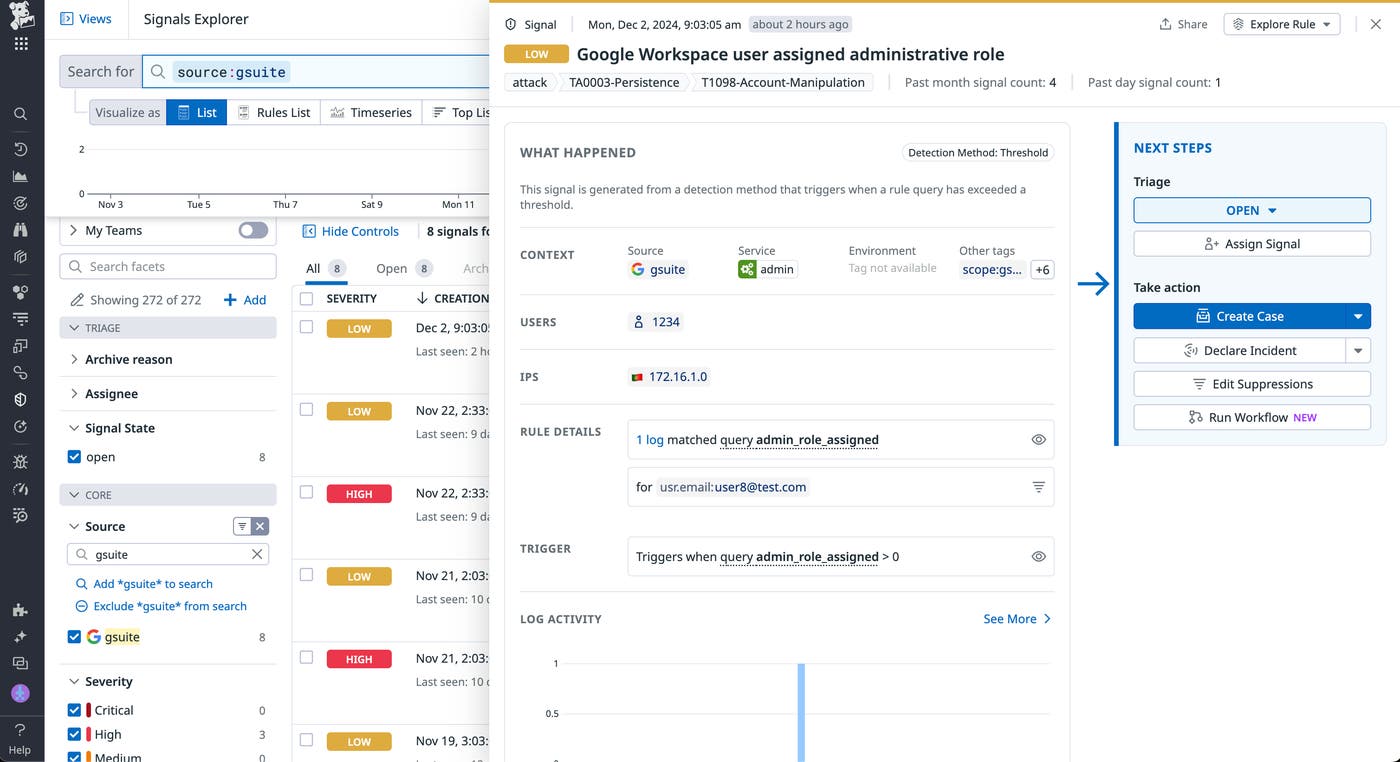
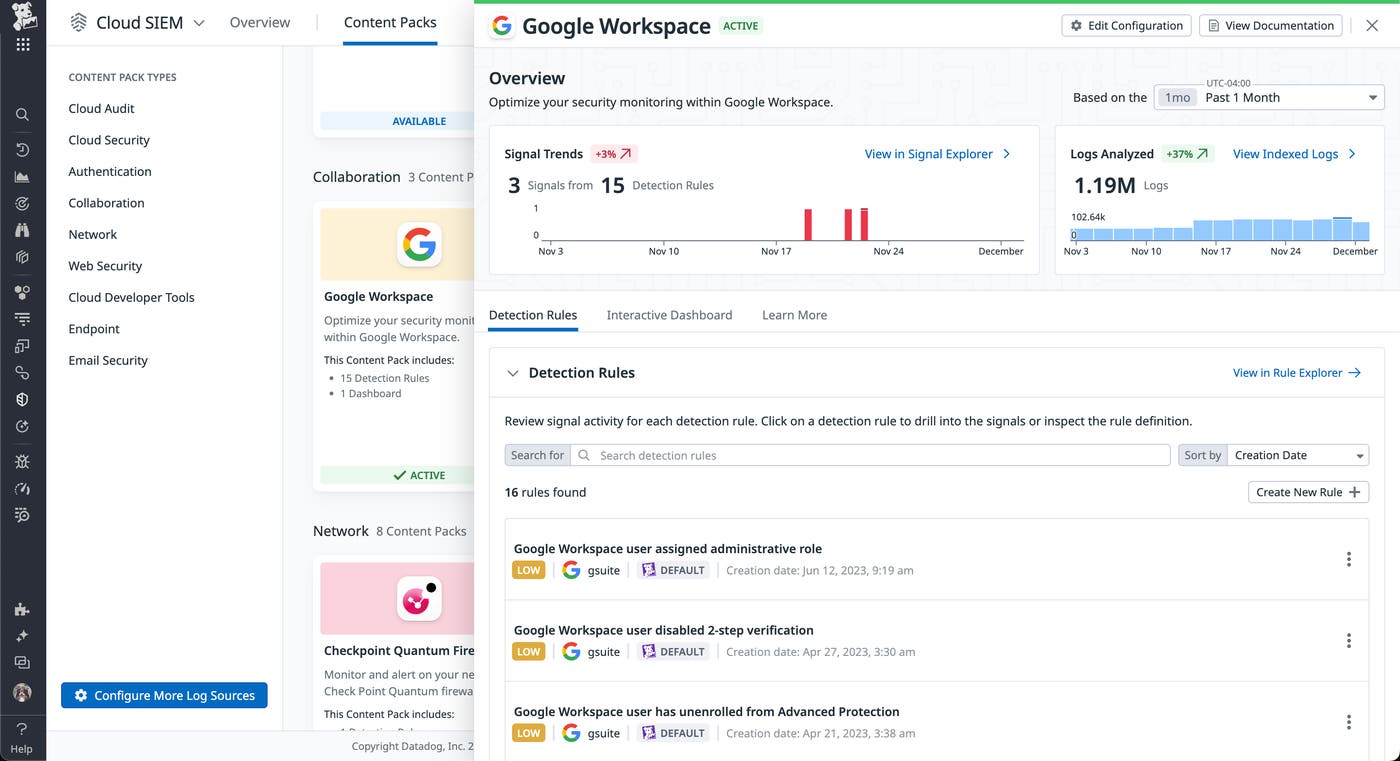
We’ve looked at a few ways attackers target Google Workspace apps and how you can detect their activity. Datadog Cloud SIEM provides a Google Workspace Content Pack that enables your teams to onboard quickly and efficiently identify and surface key trends across apps, devices, and users.
This content pack includes a wide range of built-in Cloud SIEM detections tailored to identify suspicious behavior captured in Google Workspace logs and Alert Center alerts. The pack also includes an interactive dashboard that tracks all log activity and features widgets that help security teams prioritize critical signals, monitor top users and their activity (such as frequent downloads), visualize login trends over time, and oversee administrator actions.
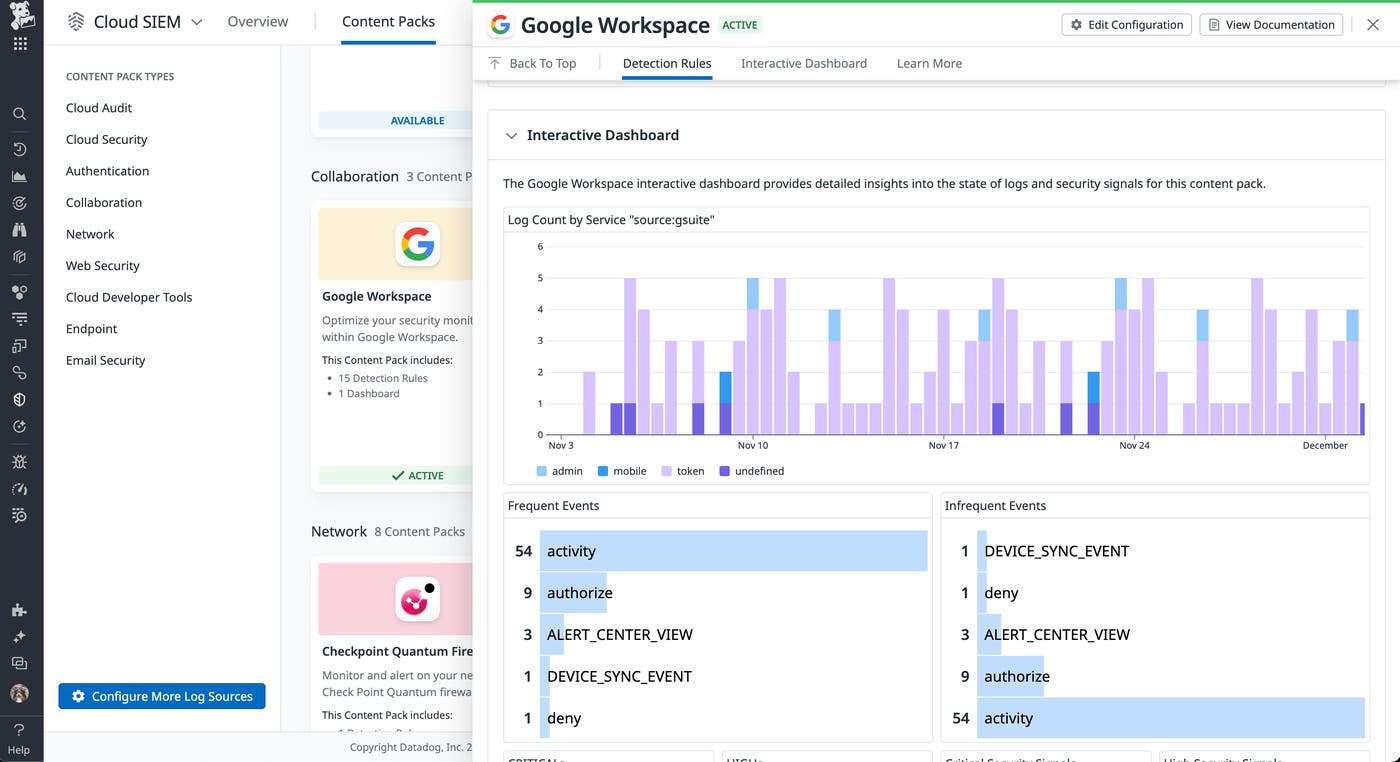
In addition to having the ability to easily analyze your Google Workspace logs, Datadog allows you to retain them for a standard 15 months or variably with Flex Logs. Flex Logs decouples the cost of log storage from the cost of querying, enabling you to keep your logs for the relative long term while still being able to instantly query them for audits and in-depth investigations.
Check out our documentation to learn about Datadog Cloud SIEM and how it provides an efficient onboarding experience for monitoring your Google Workspace environment and more. If you don’t already have a Datadog account, you can sign up for a free 14-day trial.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。