





Organizations are adopting Google Cloud at a growing rate. This growth is partially influenced by both the rise of AI computing and a push towards multi-cloud usage. A recent report found that 85 percent of organizations deploy their applications on multi-cloud architecture. With the shift to AI computing and multi-cloud adoption, organizations are reconsidering their cloud security coverage now more than ever. Google Cloud already offers built-in security monitoring for its environments, and Datadog has expanded its security platform to complement Google Cloud’s capabilities. In this post, we’ll look at how Datadog Security and Google Cloud work together to help you:
Establish visibility into suspicious events or potential attackers in your organization
Ensure continuous compliance with industry-standard frameworks
Protect your application and infrastructure attack surface from threats
Google Security Command Center, Google Cloud’s security monitoring service, enables you to review vulnerabilities and reported threats in your environments. But in order to understand the why and how behind an attack, you need to bring your security and operations teams’ existing monitoring under the same centralized platform. With this shared context, your teams can work together to accurately pinpoint attack attempts or vulnerable areas in your environments, which allows them to respond to incidents more efficiently.
Datadog provides turn-key integrations for both Google Cloud Security Command Center and Google Cloud Armor, enabling you to forward event logs directly to Datadog Cloud SIEM. With these integrations, both security and operations teams can use the same event data to uncover suspicious activity or attackers in their infrastructure.
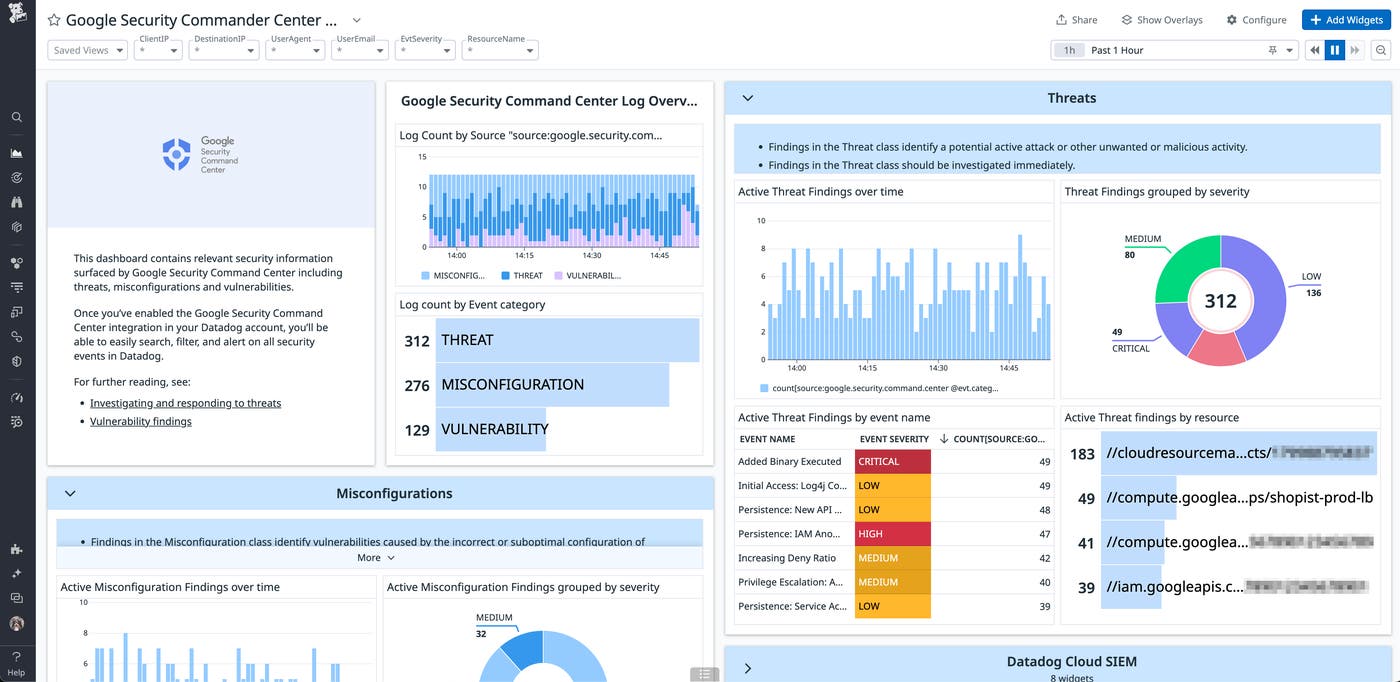
The detail in these logs enables your teams to correlate events and their metadata—such as type, severity, and source—with the existing infrastructure performance data in Datadog. Having this context is crucial for pinpointing which parts of your environment are vulnerable and need to be patched—from application services down to the underlying resources.
A key first step to improving security coverage is expanding visibility into your Google Cloud environment. But once you have a view into your services and resources, you also may need to continuously maintain compliance with certain standards, such as PCI DSS, HIPAA, CIS, and GDPR. Missing any one of these requirements could easily lead to unintentional data exposure or even costly data breaches.
Datadog Cloud Security complements Google Security Command Center by providing compliance and misconfiguration support for CIS GCP Foundations Benchmark v1.3, in addition to other industry-standard frameworks. This ensures that you are able to monitor and continuously maintain and improve your compliance posture while you expand your Google Cloud or multi-cloud environment.
A typical cloud environment is made up of a complex network of APIs, microservices, and web applications, all of which are vulnerable to threats. This is especially true if they access sensitive data, such as a customer’s personal information, credit card information, and more. With this level of risk, you need to ensure that your teams have end-to-end, continuous visibility into their environment’s security posture before and after deploying new features in production. This is in addition to getting insights into applications that are written in popular languages, such Java, Node, Go, and deployed on various compute services, like Google App Engine and Google Cloud Run.
Datadog App and API Protection (AAP) takes advantage of an organization’s instrumented applications in order to identify threats and provide protection capabilities. Datadog AAP also includes support for serverless environments like Google Cloud Run, which many organizations are also adopting at a rapid pace to support their cloud migrations. Once enabled, Datadog AAP will detect common threats, such as OWASP’s Top 10, across APIs, microservices, and applications.
As you migrate to cloud environments, your applications become increasingly more exposed to threats, so it’s critical to identify and mitigate any security and compliance gaps along the way. Datadog Security not only provides a centralized platform for visibility into these gaps, but also helps you keep your cloud environments safe from a rapidly growing threat landscape. Check out our documentation to learn more about integrating with Google Security Command Center, enabling Datadog AAP for Google Cloud Run, and Datadog Cloud Security’s supported frameworks. If you don’t already have a Datadog account, you can sign up for a free 14-day trial.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。