


Etienne Le Blan

Dany Kanes
In recent years, the popularity of Kubernetes deployments has surged—as has the prevalence of security risks associated with the technology. Red Hat’s State of Kubernetes Security for 2023 reveals that 67 percent of organizations have encountered delays in application deployments due to Kubernetes-related security issues. Additionally, 37 percent have experienced significant revenue or customer losses stemming from Kubernetes security incidents. These trends underscore the importance of proactively monitoring your Kubernetes environment for misconfigurations and vulnerabilities to mitigate business risk.
That’s why we are excited to introduce our new Kubernetes Security Posture Management (KSPM) capabilities, which are available within Datadog Cloud Security. KSPM helps you proactively strengthen the security posture of your Kubernetes deployments by benchmarking your environment against established industry best practices, such as those defined by CIS, or your own custom detection policies.
In this post, we’ll show you how KSPM helps you:
Monitor risk across Kubernetes deployments
Assess your Kubernetes security posture against industry-standard frameworks
Create your own Kubernetes security detections
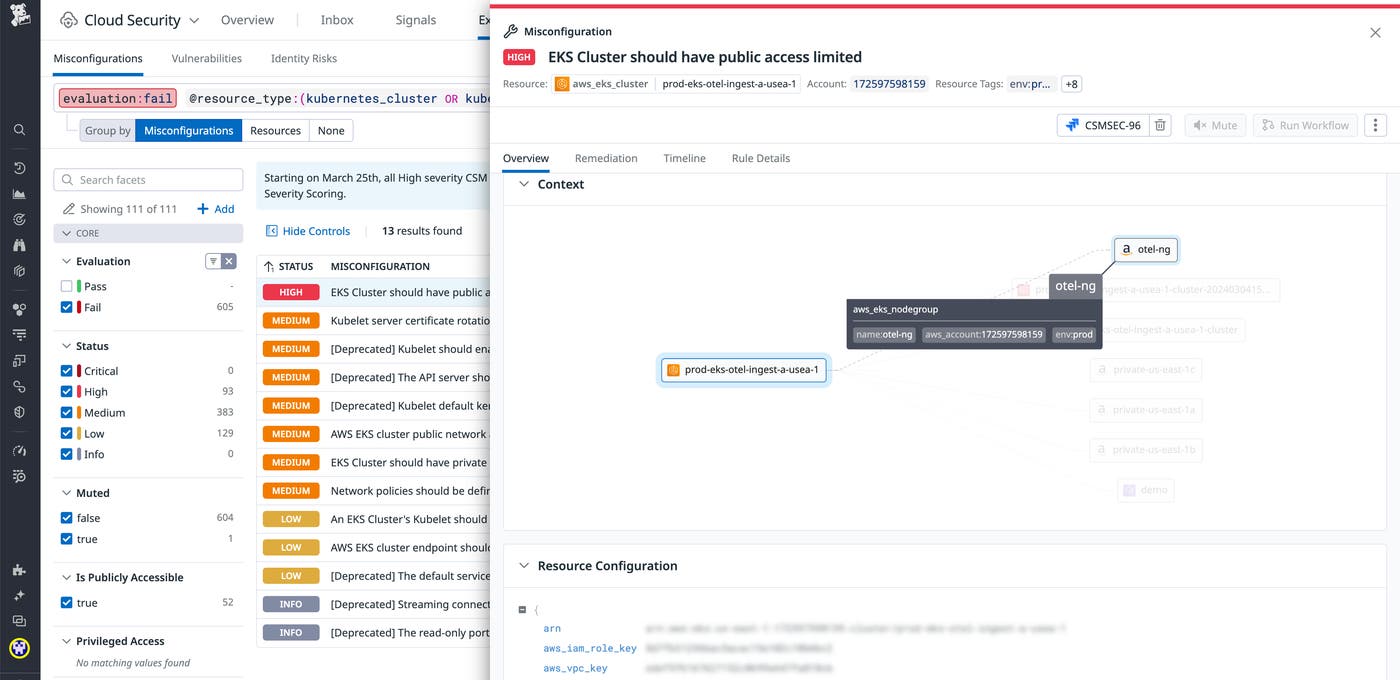
Datadog’s security experts have curated a comprehensive list of 100+ built-in Kubernetes detection rules that are now available in Cloud Security. These rules relieve security teams of the hard work of searching for common Kubernetes security issues and determining how best to solve them—now, Datadog will scan your environment for risks defined by these rules and offer clear descriptions of any issues detected, along with straightforward remediation guidelines.
Each finding contains all the context you need to identify the issue’s impact, such as the full resource configuration, resource-level tags, and a map of the resource’s relationships with other components of your infrastructure. Once you understand the problem and its impact, you can quickly start remediating the issue by creating a Jira ticket from within Cloud Security or executing a Datadog workflow.
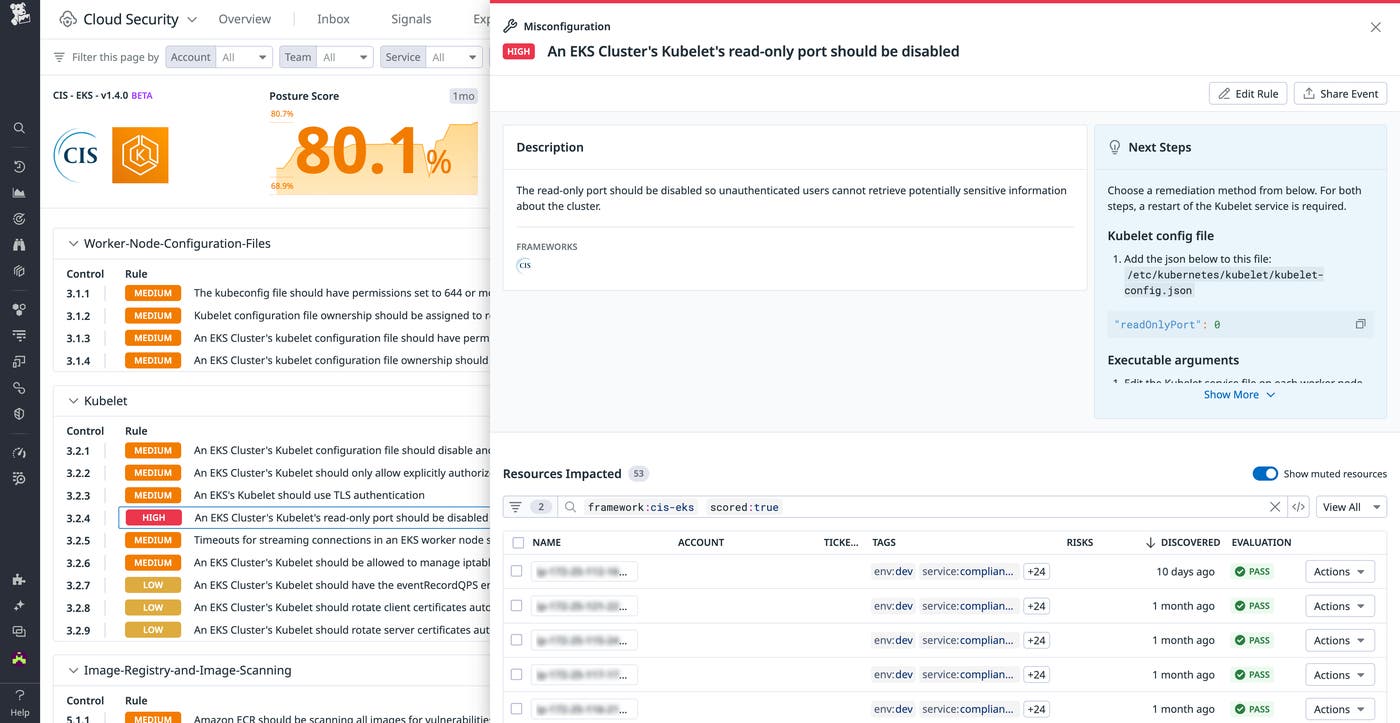
With a wide range of resources and controls for Kubernetes security available online, it can be complicated to clearly understand and evaluate what good security posture means. Datadog Cloud Security lets you evaluate your posture against industry-standard frameworks like CIS in real time and maps out requirements and controls in an easy-to-consume report.
Cloud Security provides a Posture Score that helps you understand your security and compliance status at a glance through a single metric. You can obtain this score for your entire organization or for specific teams, accounts, and environments—including your Kubernetes deployments. From this report page, you can generate detailed PDF or CSV exports to share internally or to auditors, or use our API to programmatically interact with the findings surfaced.
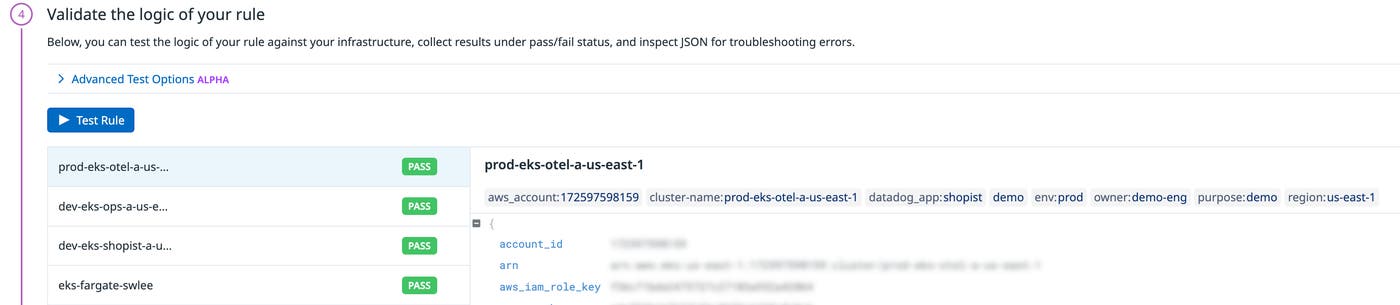
Each organization has unique security needs. Datadog Cloud Security empowers you to create your own detection rules by cloning an existing control or creating one from scratch.
Rules are written in the Rego policy language, a simple but flexible Python-like language that serves as the industry standard for detection rules. As you draft your detection query, you can test it immediately against your existing Kubernetes resources to ensure the rule is accurate and works as expected.
Once your detection is ready, you can customize its severity (Critical, High, Medium, Low, or Info) and set alerts so the right people will be notified immediately of any findings for the rule.
In addition to these KSPM features, Datadog Cloud Security also enables you to:
Identify vulnerabilities in your container images and get advice on how to prioritize remediation efforts, based on whether the affected containers run in production and if attackers are likely to exploit a vulnerability (determined by public exploit availability and Exploit Prediction Scoring System (EPSS) score).
Use out-of-the-box detection rules to catch Kubernetes-native attacks such as unfamiliar processes accessing a pod’s service account token, and use the existing Datadog observability context for 360-degree investigations.
Our new KSPM frameworks are now generally available to all CSM Pro customers for AWS EKS, Azure AKS, and unmanaged Kubernetes deployments, with Google Cloud GKE support coming later this year. Check out our KSPM documentation to get started, or head to the Frameworks page in Datadog Cloud Security. If you don’t already have a Datadog account, you can sign up for a 14-day free trial today.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。