


Millions of enterprise users rely on Slack every day as their primary tool for instant communications and information sharing. Because of its central role in operations, Slack inevitably handles sensitive data and critical business information—which also makes it a high-value target for attackers. For this reason, it’s critically important for security teams to detect and respond to security threats against Slack.
To address this issue and help security teams protect Slack from attacks, Datadog is introducing the Datadog Cloud SIEM Slack content pack, a security feature bundle that allows you to easily monitor and analyze Slack audit logs. The new Cloud SIEM Slack content pack provides a centralized view of out-of-the-box (OOTB) detection rules, automated security alerts, and real-time security dashboards for Slack. Having these security features in one place helps teams proactively monitor Slack activity to protect data, ensure privacy, prevent unauthorized access, and meet compliance standards.
In this blog, we’ll explore how you can use the Datadog Cloud SIEM Slack content pack to:
Centralize Slack audit logs for security monitoring
Detect threats with detection rules
Surface key security information in dashboards
With the Cloud SIEM Slack content pack, security teams can combine the benefits provided by Datadog Log Management and Datadog Cloud SIEM to centralize security monitoring based on Slack audit logs.

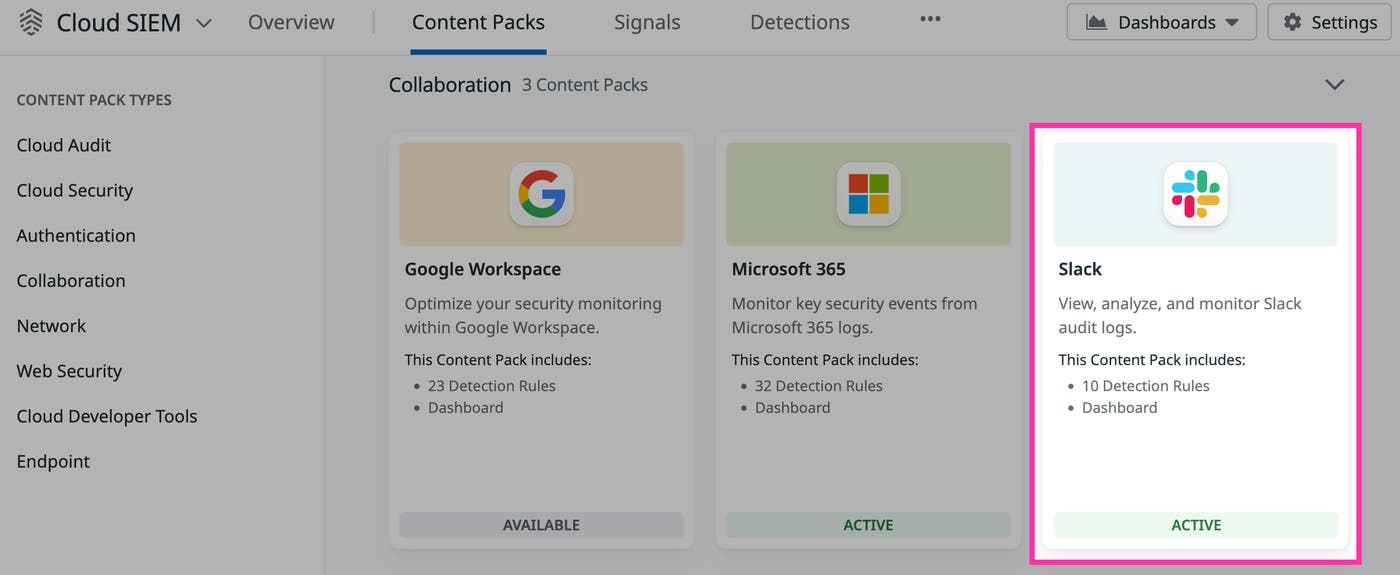
To begin activating the content pack, you first need to install and configure Datadog’s Slack integration. You then need to connect the integration to your Slack Enterprise Grid so that Log Management can start to collect Slack audit logs. At this point, the content pack will be activated and surface various critical Slack activities—including events related to user management, file management, security and compliance, external sharing, and more. See our documentation for more information about the types of events tracked by Slack audit logs.
Once activated, the content pack can also give you access to security features specific to Slack—such as detection rules, dashboards, and the Cloud SIEM Investigator for visual investigation—that enable you to quickly review real-time security signals and begin investigating potential threats.
The following screenshot shows the Cloud SIEM Slack content pack in an activated state and configured to receive audit logs:

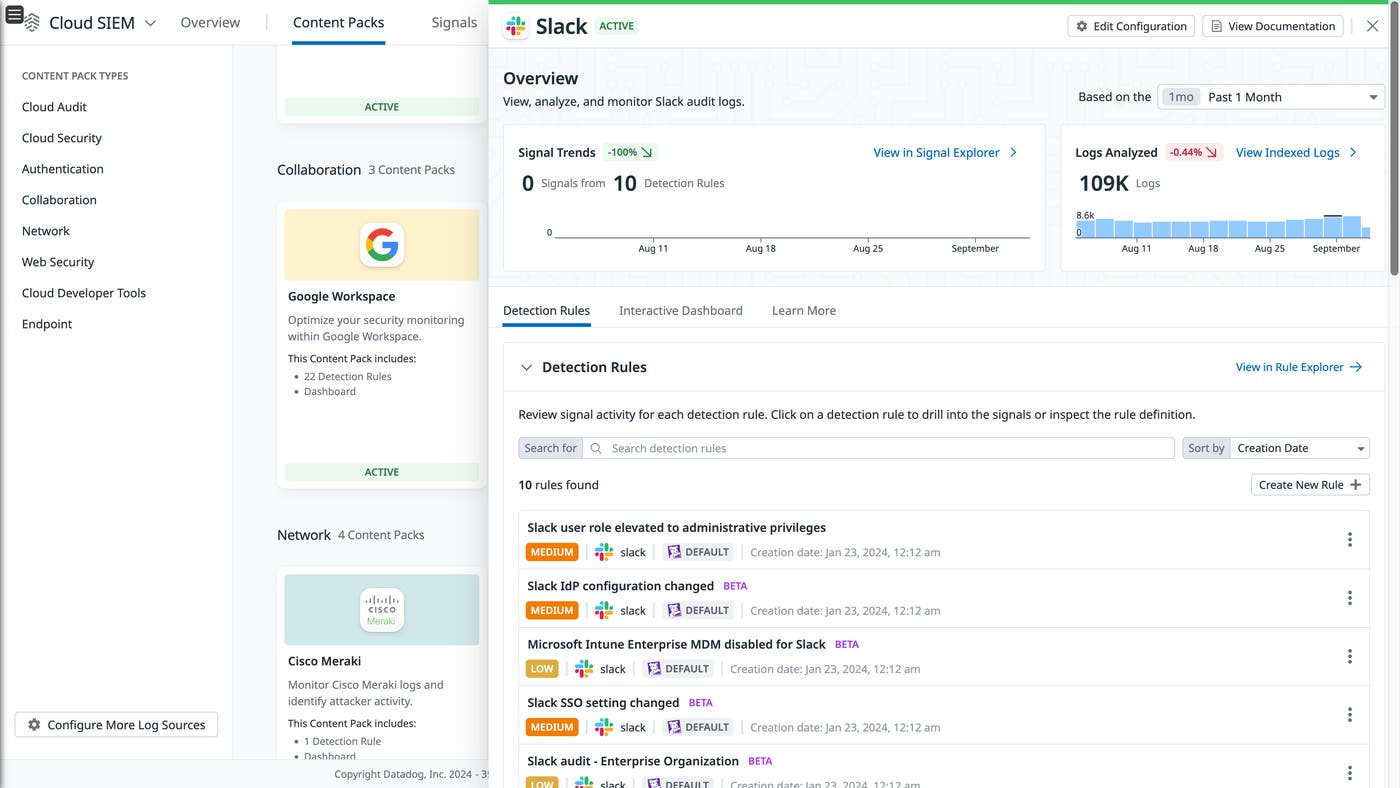
The content pack makes it easy to monitor detection rules for Slack so that you can set alerts and facilitate remediation steps when known suspicious events occur. You can create your own detection rules or use OOTB detection rules. A few examples of OOTB detection rules include the following:
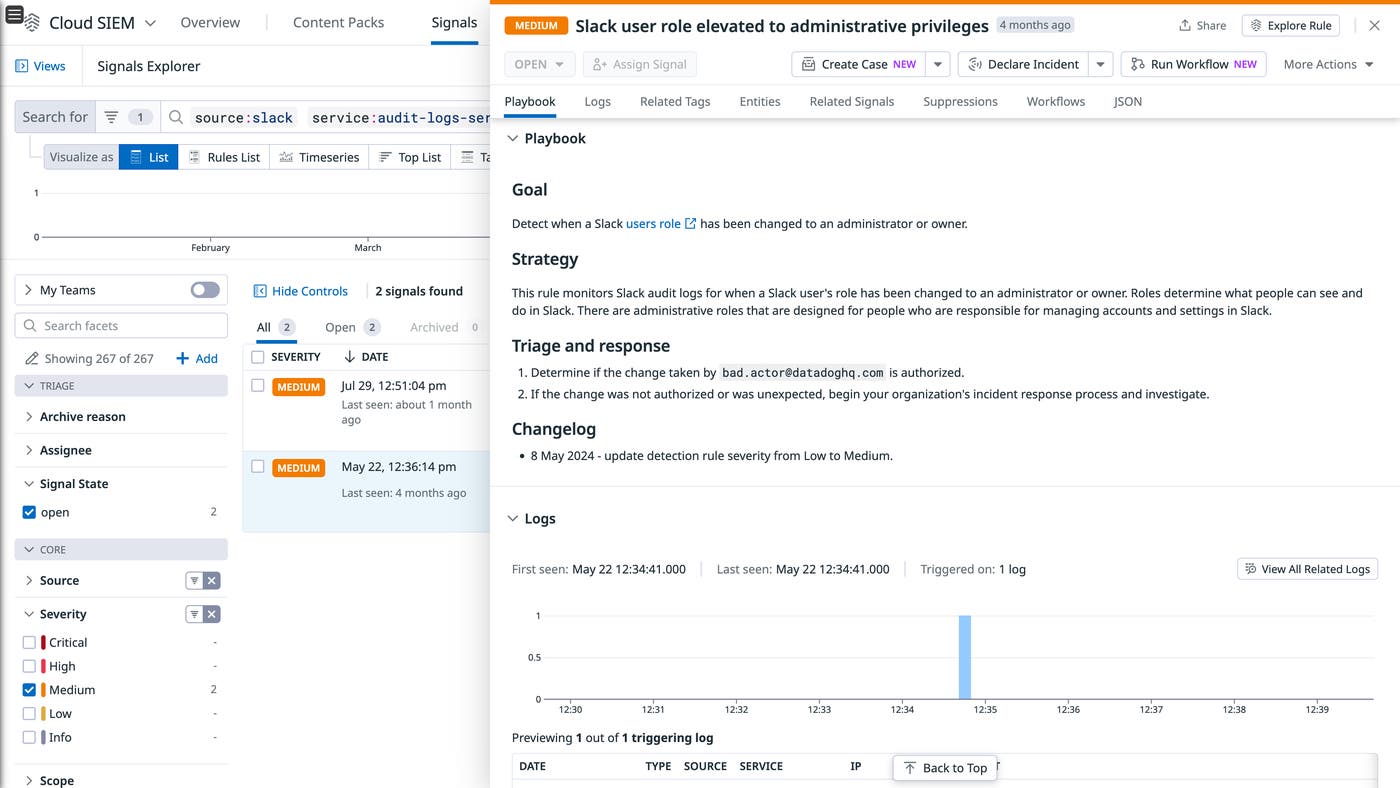
The following screenshot shows two active signals of medium severity generated by OOTB detection rules for Slack. The most recent active signal indicates that a Slack SSO setting has changed, while the other signal has been triggered because a Slack user role has been elevated to that of an administrator or owner.

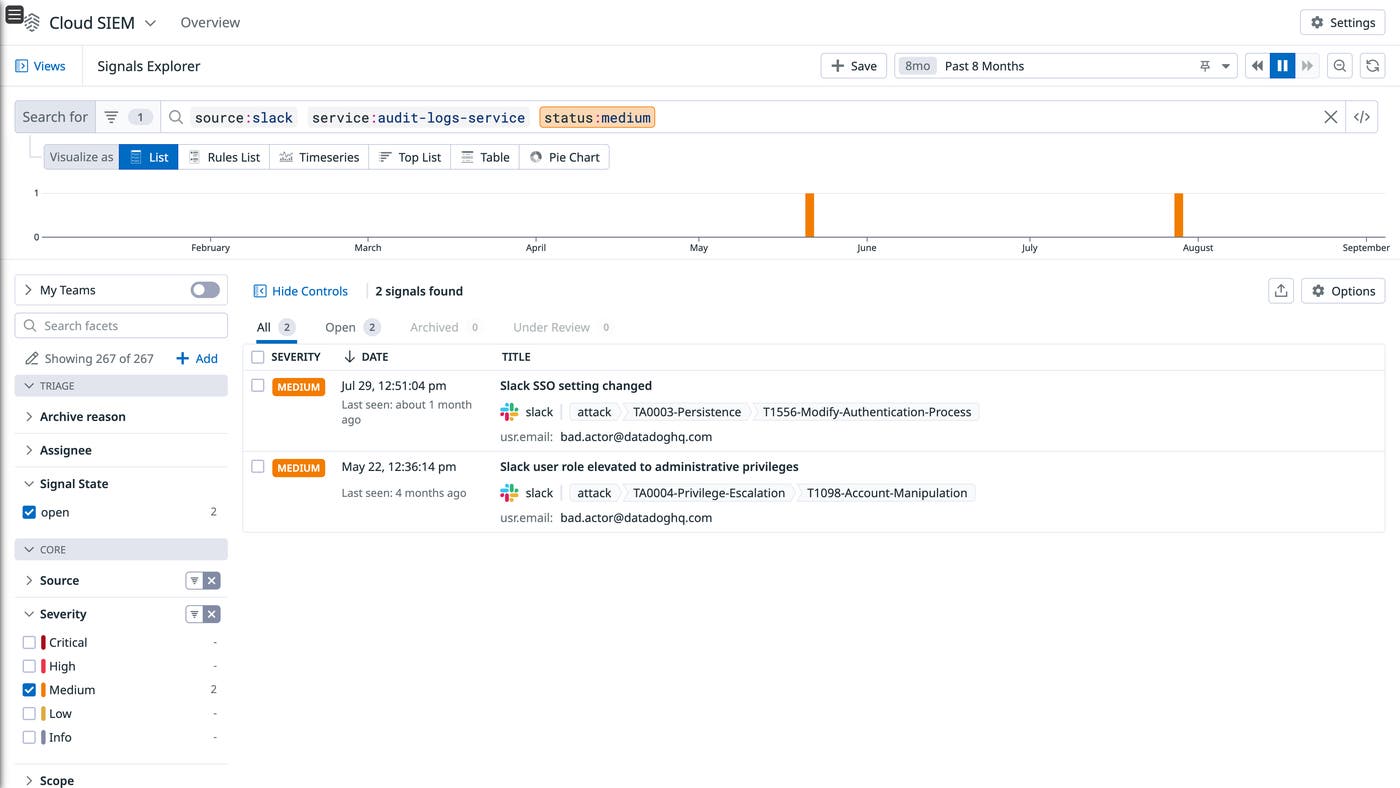
To investigate one of these security signals, you can launch the signal’s side panel to gather more details about associated logs, environment context, attributes, IPs detected, related signals, suppressions, JSON, and more. The side panel also suggests next steps for your investigation, allowing you to open up a case or incident with Datadog Case Management or Datadog Incident Management, respectively—or by using another supported management tool such as ServiceNow or Atlassian Jira.
A signal side panel based on a Slack detection rule is shown below:

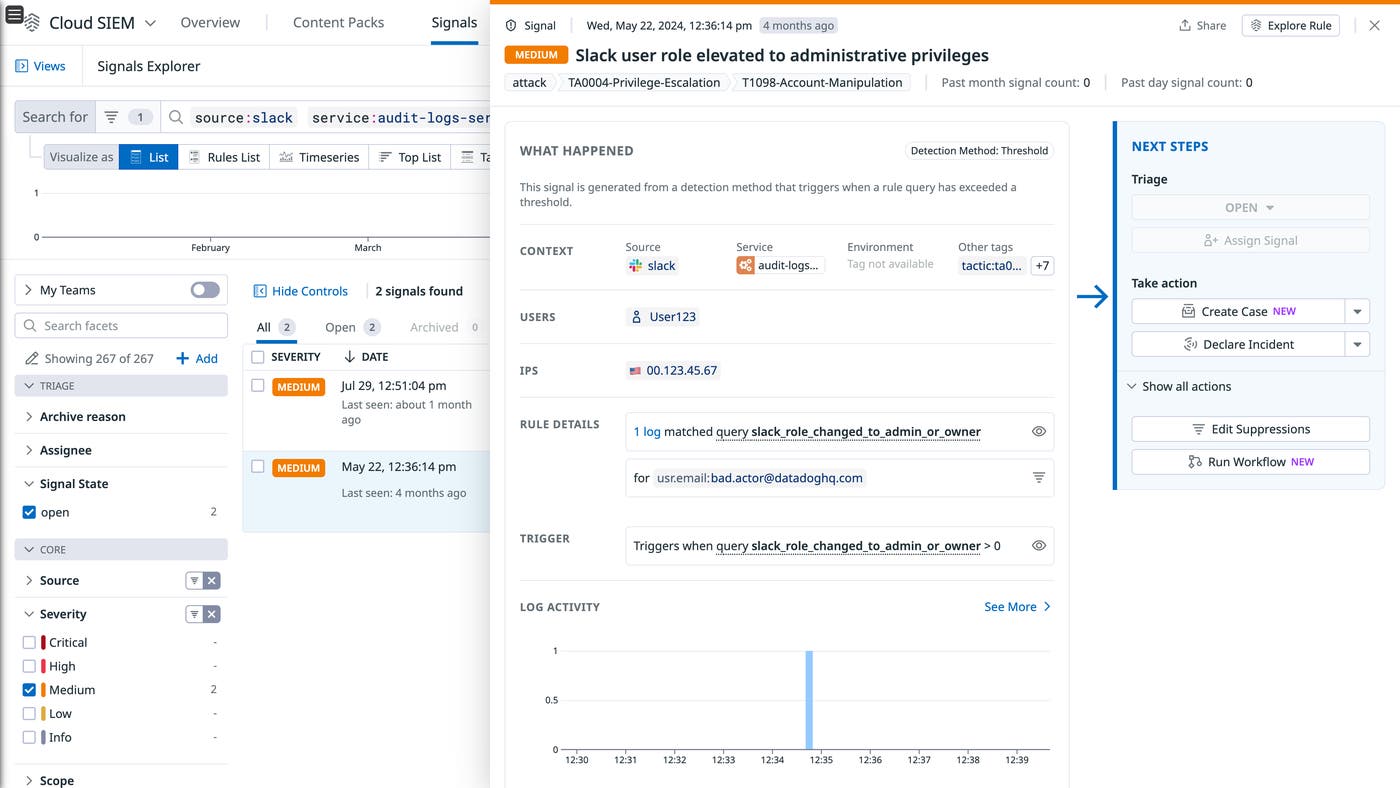
As shown in the image above, the side panel also provides a link to run a workflow. Having this option readily accessible makes it easy to automate a response to a signal, such as by sending an automated update in the form of a Slack message. If you have a Workflow Automation subscription, you can also access over 15 predefined actions for Slack and use them as elements in your own custom workflows built for a signal response.
Further down the signal side panel, Datadog Cloud SIEM signals also equip security teams with playbooks to help them research goals and strategies associated with detection rules. Playbooks also show recommendations to accelerate triage and response, as well as details around what has been changed and when to kickstart investigations.

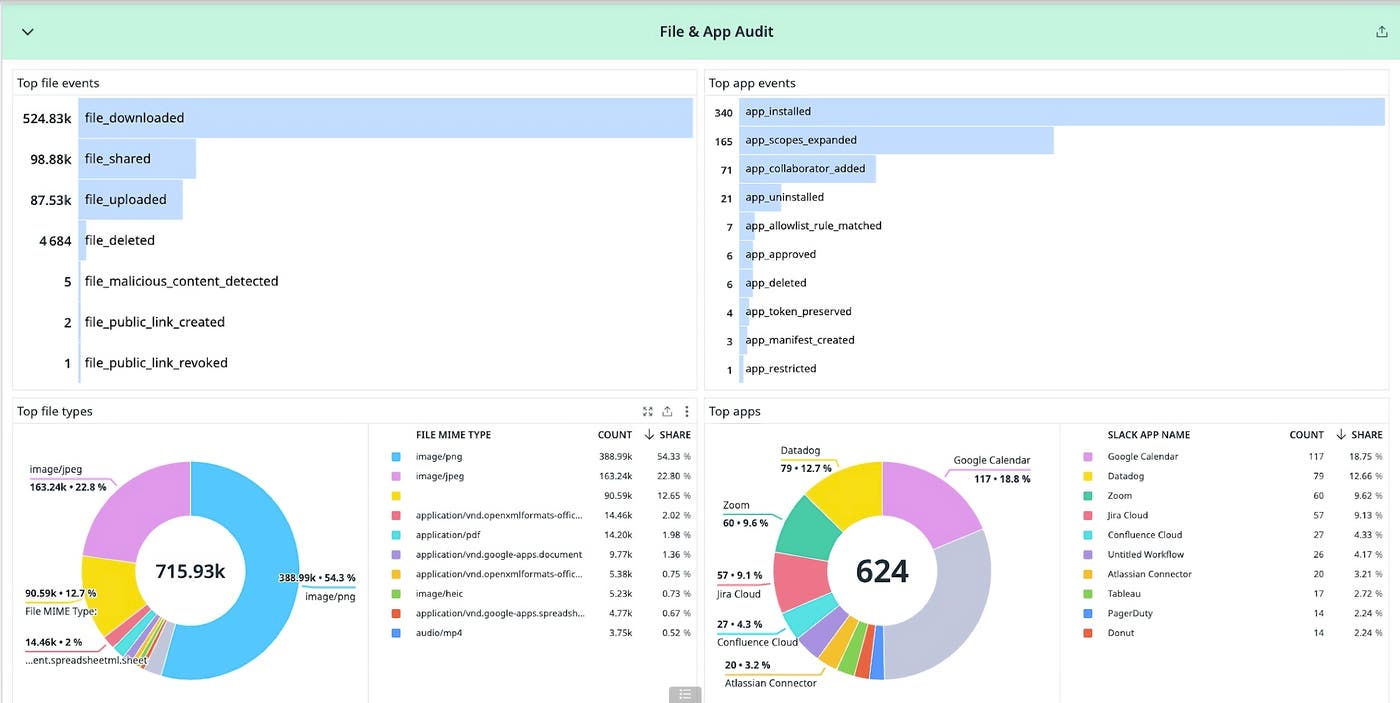
Cloud SIEM enables real-time detection of anomalies in file and app activities, providing security teams with the information needed to investigate and mitigate risks proactively. Within the File & App Audit section (shown below) of the OOTB Slack Audit Log Overview dashboard that comes with the Slack content pack, you can gain full visibility into Slack-related file and app activities across your organization. These activities include monitoring top file actions such as downloads, uploads, deletions, and the creation of public links. By tracking these file interactions, security teams can protect your sensitive data on Slack and quickly identify any suspicious behavior, such as unauthorized file sharing or unexpected deletions, that could signal potential security breaches.
Additionally, the dashboard provides deep insights into app-related events. You can track app installations, approvals, and collaborator additions, while also monitoring app deletions or restrictions. This level of oversight helps ensure that only authorized apps are used within your Slack environment, minimizing the risk of unapproved or malicious applications gaining access to sensitive information.

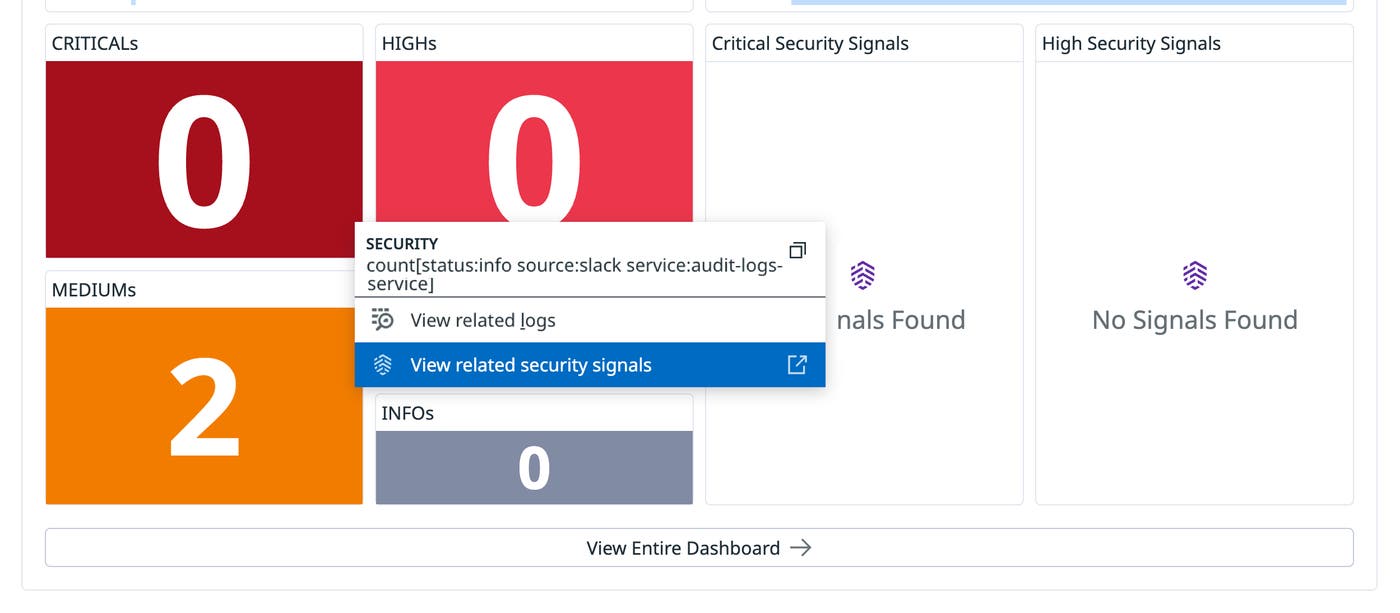
The Cloud SIEM Slack content pack serves as a starting point for Slack security monitoring and for investigations into related security signals. From the Cloud SIEM widget within the dashboard of the content pack, you can easily right-click a tile to switch to other features in Cloud SIEM and continue your research. For example, you can right-click to investigate active signals prioritized by severity in the content pack dashboard of the Cloud SIEM widget. The following image shows the options menu when you right-click the tile for medium-severity signals.
Datadog’s Cloud SIEM Slack content pack consolidates security monitoring for Slack, drawing upon Slack audit logs and features in both Log Management and Cloud SIEM to surface detection rules, workflows, dashboards, and other key security information. Having a central hub for Slack-related security events gives your team a shared starting point for Slack security monitoring, helping engineers quickly detect and remediate these issues to protect your environment against threats. For more information, you can also view the Slack Audit Log API documentation, integration documentation, the blog on how to streamline communication workflows with the Datadog Slack integration, or our guide on the best practices for creating custom rules with Cloud SIEM.
If you’re already a Datadog customer, you can start exploring the new Slack Audit Logs Content Pack now. And if you’re not, get started today with a 14-day free trial.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。