


On March 7, 2022, Max Kellermann publicly disclosed a vulnerability in the Linux kernel, later named Dirty Pipe, which allows underprivileged processes to write to arbitrary readable files, leading to privilege escalation. This vulnerability affects kernel versions starting from 5.8. After its discovery, it was fixed for all currently maintained releases of Linux in versions 5.16.11, 5.15.25, and 5.10.102.
While easier to exploit, it is similar to an older vulnerability disclosed in 2016, Dirty COW, which has been actively exploited by malicious actors since then.
The Dirty Pipe vulnerability is trivial to exploit and affects a wide range of systems, including some versions of the Android OS, which is based on the Linux kernel. Applying kernel patches is typically more challenging than standard software updates. This can be especially true in the case of Android-based systems. As a consequence, we believe that a high number of systems will remain vulnerable in the future.
Datadog was also able to demonstrate that Dirty Pipe can be used to break out from unprivileged containers. Once there has been sufficient time for the community to remediate this vulnerability, we will release full technical details of our container breakout.
This vulnerability exclusively affects Linux-based systems. The easiest way to check whether your system is vulnerable is to see which version of the Linux kernel it uses by running the command uname -r.
A system is likely to be vulnerable if it has a kernel version higher than 5.8, but lower than 5.16.11, 5.15.25, or 5.10.102. For instance:
For more precise instructions on how to check if a system is vulnerable, you can refer to to the advisory specific to your Linux distribution, which we will cover in the next section.
To remediate the vulnerability, ensure your Linux systems are running a kernel version of 5.16.11, 5.15.25, 5.10.102, or more recent.
Major Linux distributions have released dedicated security bulletins to help mitigate the vulnerability, including:
While the situation is still developing, as of this writing Azure and GCP have not yet released a bulletin. AWS issued ALAS-2022-1571 and ALAS2KERNEL-5.4-2022-023 for its Amazon Linux operating system.
This vulnerability lies in the inner workings of the Linux kernel page cache, which handles what bits of memory ("pages") need to be persisted to disk, and what pages can remain in memory only. When exploited, the Dirty Pipe vulnerability allows an underprivileged user to write arbitrary data to any file that user can read on the file system.
There are several ways to exploit this vulnerability for privilege escalation. One of them is by writing to the /etc/passwd file, which contains the list of users along with their privileges. For instance, appending the following line to /etc/passwd creates a new user, "malicious-attacker," with password "datadog" and the same privileges as root:
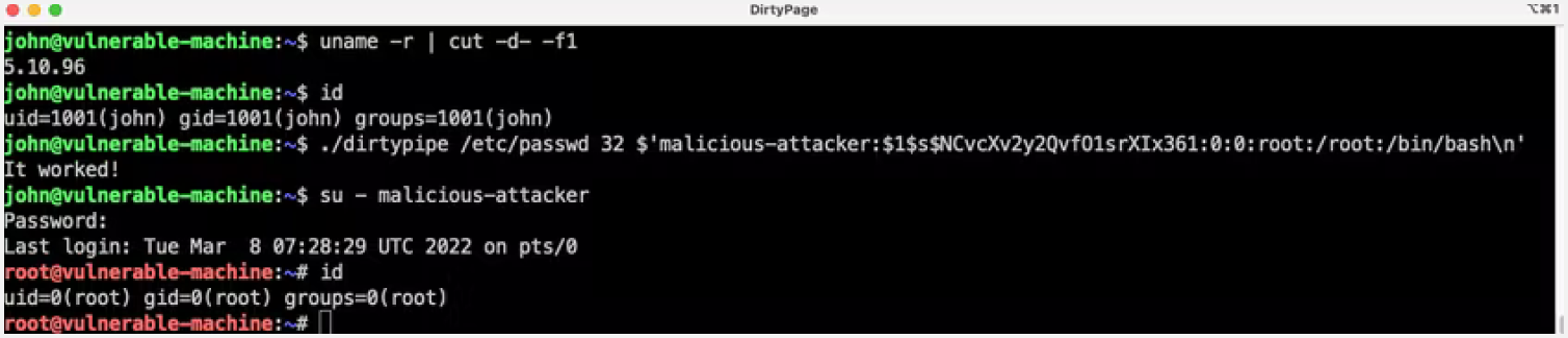
The Dirty Pipe vulnerability can also be used to escape from underprivileged Linux containers. We were able to overwrite the RunC binary from a container running a proof of concept exploit.
RunC is part of many container runtimes used by Docker and Kubernetes, among other container technologies. Its role is to spawn, run, and configure containers on Linux. A specially crafted attack on RunC allows a malicious actor to compromise the host's operating system, leading to a full host compromise.
We will release full details of the PoC in an upcoming blog post, in order to give the community time to update their infrastructure to the latest Linux kernel patches that protect against this attack.
The Datadog Cloud Workload Security team is working to add capabilities to the Datadog Agent in order to reliably detect exploitation of Dirty Pipe. Specifically, we have added splice to the list of system calls that the Agent monitors in real time using eBPF. This feature is expected to be released as part of version 7.35 of the Datadog Agent. Customers of Cloud Workload Security will receive a notification to update their Agent to a version that can detect exploitation of the Dirty Pipe vulnerability.
By enabling Datadog to watch for splice system calls, we are able to create the following detection rule to identify instances of Dirty Pipe exploitation:
tags:audit,dashThis rule identifies when the splicesystem call is performed on a file that isn't world-writable, and includes the PIPE_BUF_FLAG_CAN_MERGEflag to trigger the vulnerability.
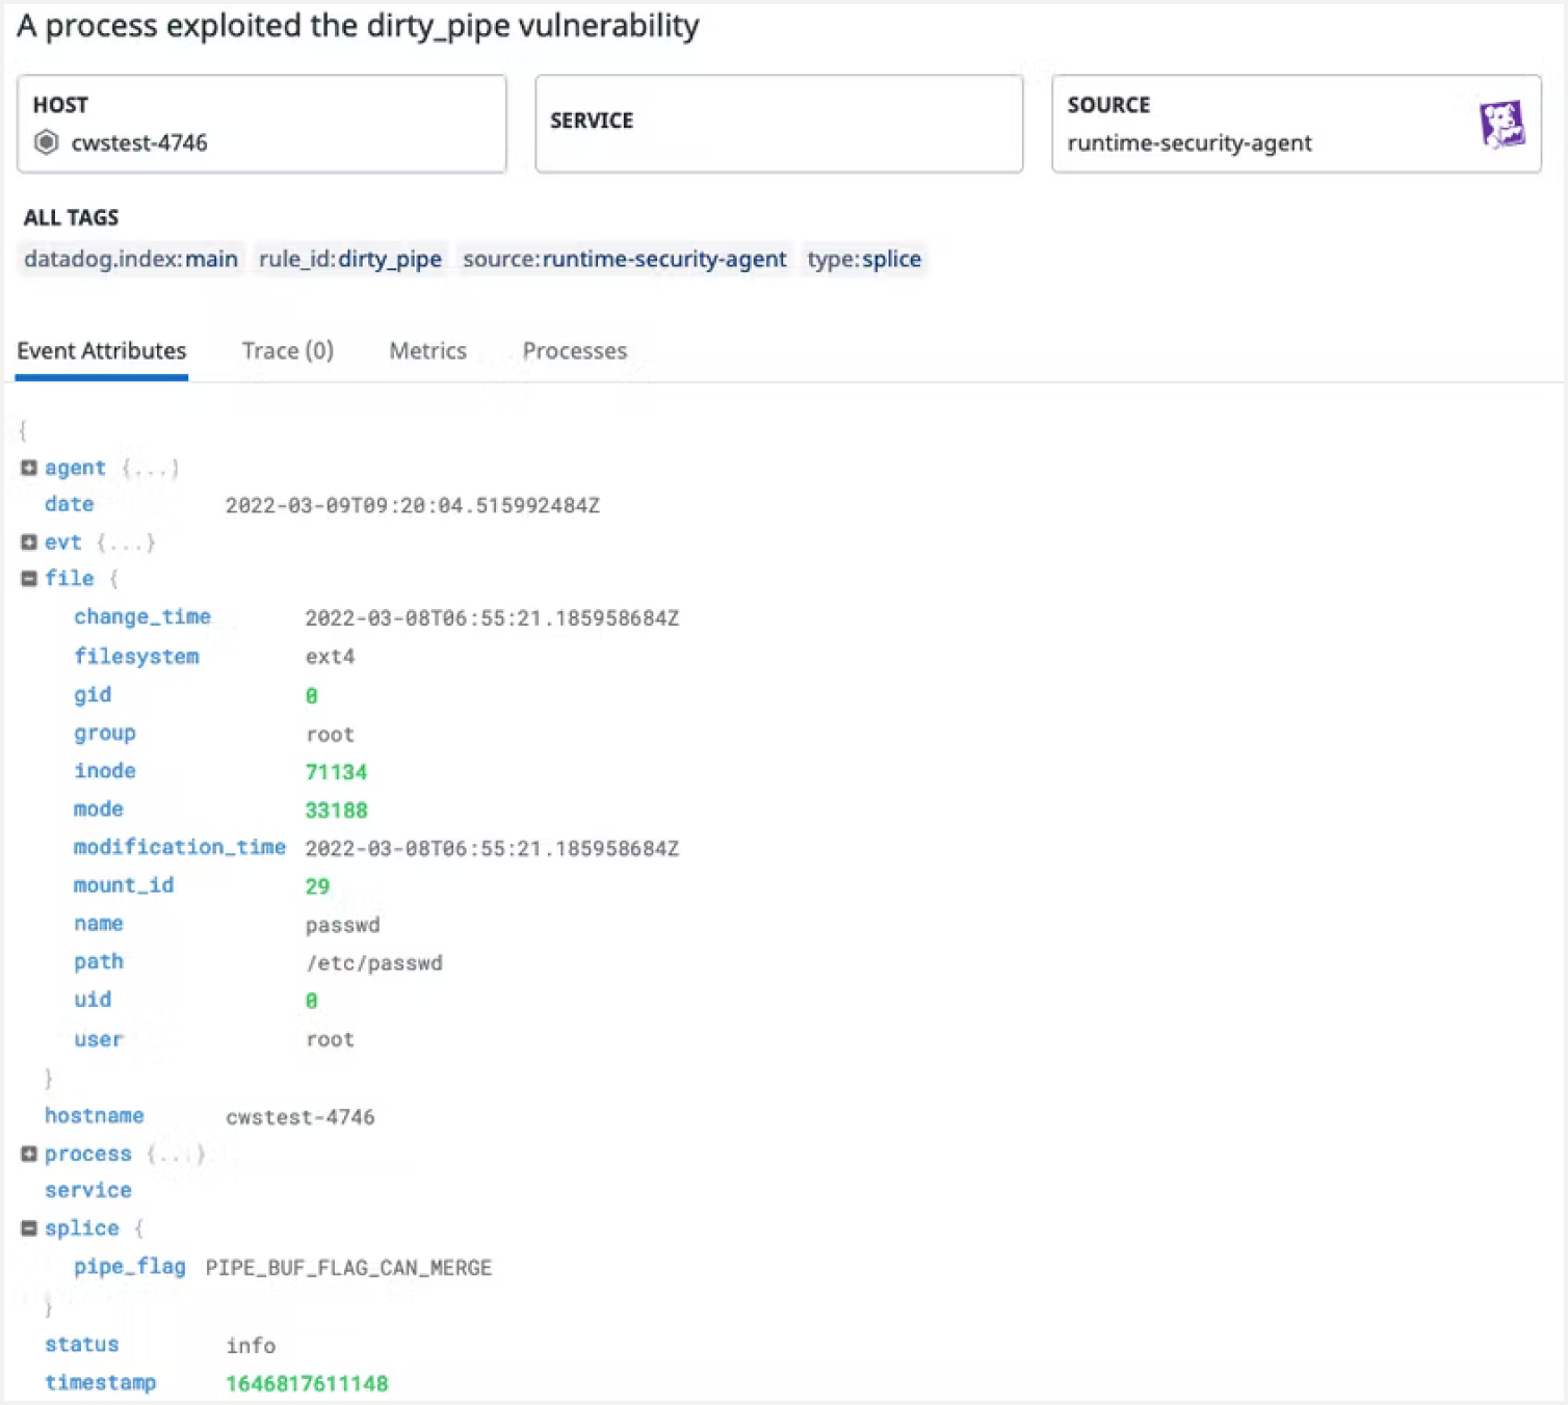
We have also crafted more specific rules to identify several common exploitation cases:
(splice.pipe_exit_flag & PIPE_BUF_FLAG_CAN_MERGE) > 0) &(splice.file.mode & S_IXGRP > 0 || splice.file.mode & S_IXOTH > 0 || splice.file.mode & S_IXUSR > 0)(splice.pipe_exit_flag & PIPE_BUF_FLAG_CAN_MERGE) > 0
&& (splice.file.path in [ ~"/bin/*", ~"/sbin/*", ~"/usr/bin/*", ~"/usr/sbin/*", ~"/usr/local/bin/*", ~"/usr/local/sbin/*", ~"/boot/**" ])Dirty Pipe is a significant vulnerability because it provides attackers an easy-to-use local privilege escalation in Linux and cloud infrastructure. We will continue to update this post as more information about the vulnerability becomes available. However, the risks and disruptions Dirty Pipe makes possible can be mitigated through a defense-in-depth security approach. Datadog customers can enable Cloud Workload Security today to get immediate defense at the runtime level by detecting the exploitation in real time.
Securing your production environment is a continuous journey, and doesn't stop after you've mitigated this newest vulnerability. For a more holistic, unified security approach, you can check out Datadog's Cloud Security Platform and start a 14-day free trial today.
Securing your production environment is a continuous journey, and doesn't stop after you've mitigated this newest vulnerability. For a more holistic, unified security approach, you can check out Datadog's Cloud Security Platform and start a 14-day free trial today.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。