







Gorka Vicente
The modern application landscape is rapidly evolving, creating new tools, technologies, and processes that allow organizations to deploy production code faster. But risks to application security have also changed significantly, requiring the security discipline to evolve in order to adapt to new types of attacks. While solutions like Dynamic Application Security Testing (DAST) have become a widely used approach to detecting vulnerabilities, many organizations are shifting to ones that provide deeper visibility into production code.
In this post, we’ll look at the challenges of using DASTs and how taking an instrumentation-based approach through Interactive Application Security Testing (IAST) solves them. Along the way, we’ll also look at how Datadog Code Security uses the IAST approach to efficiently detect security vulnerabilities in production environments.
Traditional solutions like DASTs work independently of the application being tested, simulating attacks against them by executing a series of HTTP requests and evaluating their responses. This approach requires that organizations launch a scan and then wait for the results, creating a point-in-time snapshot of an application’s security instead of continuous security monitoring. For applications with a large footprint, this type of security testing can take days to complete. Even minor code changes or vulnerability fixes would require another full scan, which can be a significant hurdle for organizations who deploy production code at a high velocity.
Because DASTs operate outside of an application, they lack granular visibility into the interactions between an application’s services, resources, and other components. This limited scope introduces challenges for building complete security coverage. First, while DASTs can detect vulnerabilities from external threats, they end up missing deep-level vulnerabilities that affect an application’s code or architecture. Second, without this internal visibility, DASTs also lack the necessary context for finding the source of a detected vulnerability and acting on it.
With the combined challenges of lack of visibility into the code and the “launch and wait” approach, relying on DASTs alone to assess application security can create significant gaps in an organization’s overall security strategy. To address these gaps, security teams need a solution that not only improves the scope of their vulnerability detection but also their remediation efforts.
IAST models use instrumentation to analyze applications in their running state, monitoring requests and their interactions with each internal layer—operating similarly to application performance monitoring (APM). This instrumentation-based approach plays a key role in helping organizations find and mitigate a broader range of vulnerabilities that traditional solutions like DASTs may miss.
Instrumentation enables IASTs to easily integrate with an organization’s existing infrastructure, continuously monitor all production traffic for vulnerabilities, and provide security insights in real-time. With these advantages, security teams can quickly ramp up security monitoring without disrupting production releases. For example, they can use the Datadog Agent and their application’s existing instrumentation to detect vulnerabilities instead of relying on manually executed attacks, scans, or costly penetration testing.
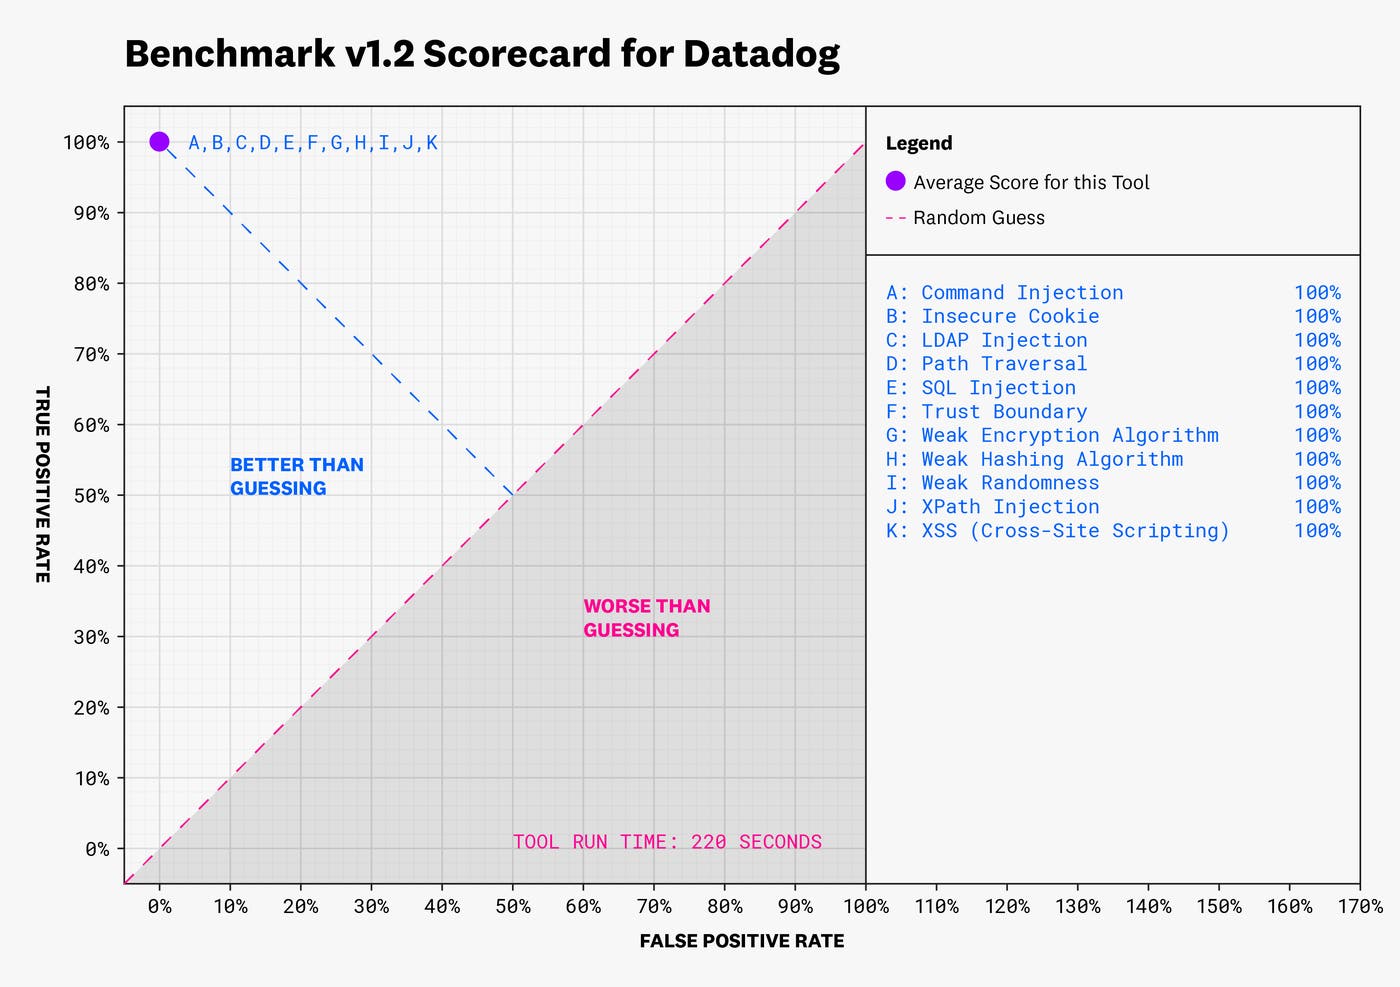
The instrumentation-based approach also enables IASTs to provide greater coverage for a wider range of vulnerabilities than other application security testing solutions. Datadog Code Security offers 100 percent coverage against the OWASP benchmark, which evaluates application security testing solutions like IASTs against common vulnerability types. This scope of coverage ensures that teams can detect vulnerabilities with complete accuracy, regardless of how complex, severe, or widespread those vulnerabilities are.
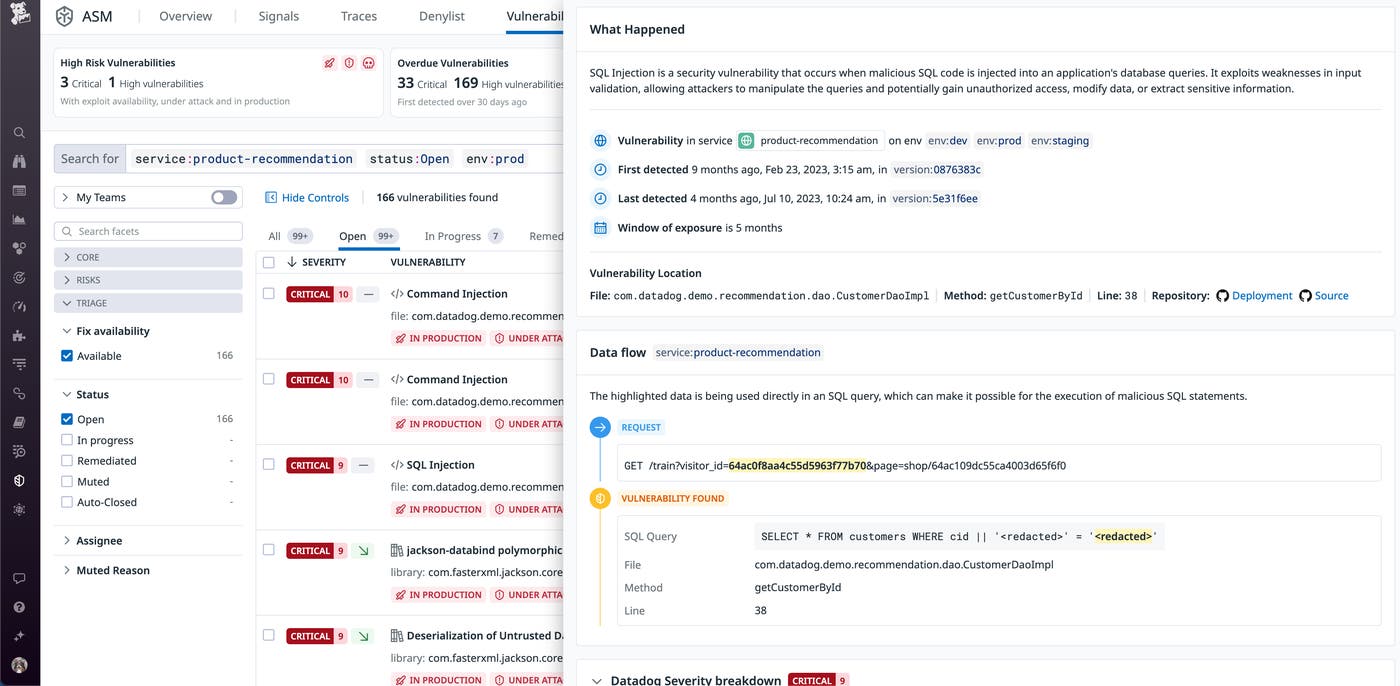
In addition to its ability to integrate with existing infrastructure and create exhaustive coverage, instrumentation plays a key role in offering all of the necessary context for confirming and fixing vulnerabilities. Datadog Code Security automatically provides the information teams need to understand exactly where a vulnerability is in an application—from the affected filename down to the exact method and line number. If they’ve enabled our GitHub integration, Datadog will also show them the first impacted version of a service, the commit that introduced the vulnerability, and a snippet of the vulnerable code. Together, this information gives teams insight into where and when a vulnerability occurred so they can efficiently prioritize their work.
IASTs provide continuous, code-level vulnerability detection for your applications, which is a critical requirement for maintaining secure, reliable production environments. Since this approach works within the application, it enables teams to detect vulnerabilities that other security testing solutions may miss. Datadog Code Security takes advantage of the IAST approach to offer an up-to-date view of your application’s attack surface.
To start detecting code-level vulnerabilities in production, check out our documentation. If you don’t already have a Datadog account, you can sign up for a free 14-day trial.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。