



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

The GitHub Blog
The GitHub Blog
S
SegmentFault 最新的问题
MyScale Blog
MyScale Blog
有赞技术团队
有赞技术团队
V
Visual Studio Blog
T
The Blog of Author Tim Ferriss
爱范儿
爱范儿
Vercel News
Vercel News
让小产品的独立变现更简单 - ezindie.com
Y
Y Combinator Blog
Blog — PlanetScale
Blog — PlanetScale
D
DataBreaches.Net
美团技术团队
Microsoft Security Blog
大猫的无限游戏
大猫的无限游戏
Cyber Security Advisories - MS-ISAC
酷 壳 – CoolShell
酷 壳 – CoolShell
GbyAI
GbyAI
A
About on SuperTechFans
云风的 BLOG
云风的 BLOG
The Cloudflare Blog
宝玉的分享
宝玉的分享
V
V2EX
Microsoft Azure Blog

Datadog | The Monitor blog

Introducing our open source AI-native SAST Instrument and monitor Boomi integration flows with OpenTelemetry and Datadog Not all index scans are equal: How we cut query latency by over 99% Platform engineering metrics: What to measure and what to ignore Integrate Recorded Future threat intelligence with Datadog Cloud SIEM CI/CD security: threat modeling using a MITRE-style threat matrix CI/CD security: How to secure your GitHub ecosystem Ingress NGINX is EOL: A practical guide for migrating to Kubernetes Gateway API Operating agentic AI with Amazon Bedrock AgentCore and Datadog LLM Observability: Lessons from NTT DATA Introducing the Datadog Code Security MCP Capture and analyze custom heatmaps in Session Replay Understand session replays faster with AI summaries and smart chapters Monitor ClickHouse query performance with Datadog Database Monitoring How we designed empathetic alert sounds for on-call engineers Search and act across Datadog to resolve issues faster with Bits Assistant Measure the business impact of every product change with Datadog Experiments Analyzing round trip query latency Configuring JavaScript caches for better performance Introducing Bits AI Dev Agent for Code Security Datadog achieves ISO 42001 certification for responsible AI Monitor Nutanix clusters, hosts, and VMs with Datadog Monitor Juniper Mist in Datadog A new Host Map for modern infrastructure Annotate traces to improve LLM quality with Datadog LLM Observability What’s new in Cloud SIEM: AI-powered investigations, enhanced threat intelligence, and scalable security operations Explore Kubernetes with native OpenTelemetry data Monitor Oracle Fusion Cloud Applications with Datadog Announcing the Datadog Terraform provider v4.0.0 Scaling Kubernetes workloads on custom metrics How to design cloud environments for AI-powered threat analysis
Correlate metrics and logs with Datadog and Splunk
Rudy Bunel · 2014-05-15 · via Datadog | The Monitor blog

Splunk is a tool that lets you search, analyze, and create custom reports on your log data to help identify abnormal behavior in your infrastructure. With the new Datadog and Splunk integration, you can view the log alerts and reports that Splunk creates in the context of the infrastructure metrics and events that Datadog captures. Using Datadog and Splunk together, further increases your visibility into your infrastructure and helps identify the root cause of problems faster and with greater accuracy.

In this blog we’ll discuss how Datadog’s Splunk integration puts the microscope on application monitoring by facilitating team collaboration over Splunk events and providing visualization of Splunk events in the context of your infrastructure’s performance metrics.

Collaborate with your team about Splunk events

Splunk gives you the ability to create a custom log report based on your search criteria. The integration with Datadog allows you to automatically deliver this report to your Datadog Events Stream and to incorporate this data in Datadog dashboards. You can further utilize Datadog’s communication and analysis tools to comment on reports or filter them by specific time frames and priorities.
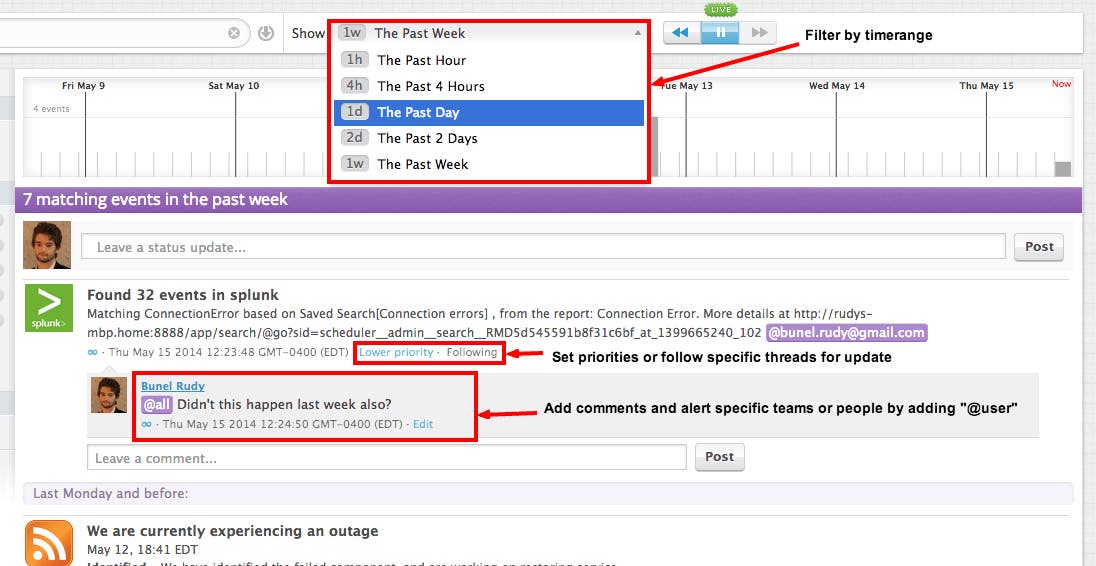
Collaborate about Splunk events

You can also customize Splunk event notifications and alert specific individuals by adding “@user” to the event message. This feature can be used with other integrated alert tools such as PagerDuty and OpsGenie to streamline your communication.
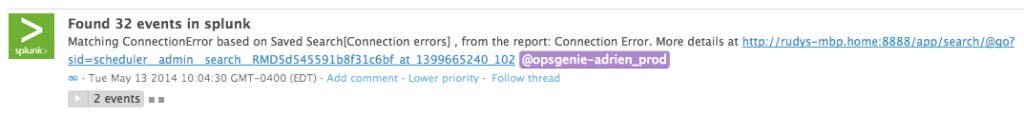
Splunk events

Correlate Splunk events with infrastructure metrics for more efficient root cause analysis

Datadog’s Splunk integration allows events from Splunk reports to be visualized and correlated with metrics drawn from all of Datadog’s integrations. As a result, you can now identify the root cause for performance issues more easily and efficiently.

For example, in the screenshot below we show how we found that I/O and network metrics spikes we were experiencing were due to connection errors that were detailed in our logs.
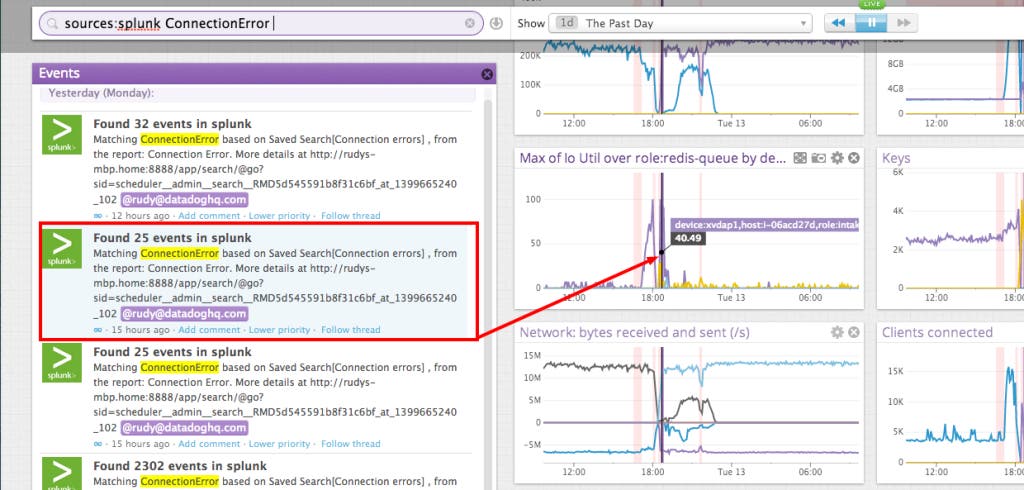
Splunk events

To collaborate with your team about Splunk events and correlate these events with other infrastructure metrics to more easily identify root cause for performance issues, try Datadog free for 14 days.