April 6:The blog has been updated to include that CVE-2026-35616 has been added to the CISA KEV.









Exploitation has been observed for CVE-2026-35616, a critical improper access control zero-day vulnerability affecting Fortinet FortiClientEMS devices.
Update April 6: The blog has been updated to include that CVE-2026-35616 has been added to the CISA KEV.
April 6:The blog has been updated to include that CVE-2026-35616 has been added to the CISA KEV.
On April 4, Fortinet published a security advisory (FG-IR-26-099) for CVE-2026-35616, a critical improper access control vulnerability affecting Fortinet FortiClientEMS.
| CVE | Description | CVSSv3 |
|---|---|---|
| CVE-2026-35616 | Fortinet FortiClientEMS Improper Access Control Vulnerability | 9.1 |
CVE-2026-35616 is a critical improper access control vulnerability affecting Fortinet FortiClientEMS. A remote, unauthenticated attacker can exploit this flaw to execute arbitrary code using specially crafted requests which bypass API authentication.
While no attribution has been provided as of the time this blog was published, the advisory from Fortinet confirms that exploitation has been observed. The advisory credits Simo Kohonen from Defused and Nguyen Duc Anh, who reported the vulnerability to Fortinet. On April 4, Defused released a Linkedin post confirming their observations of zero-day exploitation of this flaw.
At the time this blog was published, Tenable Research has classified this flaw as a Vulnerability of Interest according to our Vulnerability Watch classification system.
Historical Exploitation of Fortinet Devices
Fortinet vulnerabilities have historically been common targets for cyber attackers, with 24 Fortinet CVEs currently on the Cybersecurity and Infrastructure Security Agency’s (CISA) Known Exploited Vulnerabilities (KEV) list, with 13 of those being linked to ransomware campaigns. Targeting of Fortinet flaws have been attributed to a number of threat actors, including Salt Typhoon.
Just over a week ago, Defused reported exploitation in the wild for CVE-2026-21643, SQL injection vulnerability affecting FortiClientEMS. Fortinet’s advisory now reflects that exploitation has been observed but as of April 6, the flaw has not yet been added to the KEV.
🚨 Fortinet Forticlient EMS CVE-2026-21643 - currently marked as not exploited on CISA and other Known Exploited Vulnerabilities (KEV) lists - has seen first exploitation already 4 days ago according to our data
Attackers can smuggle SQL statements through the "Site"-header… pic.twitter.com/pHwl2qMVsj
— Defused (@DefusedCyber) March 28, 2026
At the time this blog was published on April 6, CVE-2026-35616 had not been added to the KEV, however shortly after publication, the KEV was updated to include CVE-2026-35616.
As Fortinet devices have been popular targets for attackers, the Tenable Research Special Operations Team (RSO) has authored several blogs about vulnerabilities affecting these devices. The following table outlines some of the most impactful Fortinet vulnerabilities in recent years.
As of April 6, a public proof-of-concept has been identified on GitHub, however Tenable Research has not yet verified the exploit. Given the past exploitation of Fortinet devices and published exploit code for several past vulnerabilities, we anticipate that exploitation will continue to increase as additional exploits are released.
The following table details the affected and fixed versions of Fortinet FortiClientEMS devices for CVE-2026-35616:
| Product Version | Affected Range | Fixed Version |
|---|---|---|
| FortiClientEMS 7.2 | Not affected | N/A |
| FortiClientEMS 7.4 | 7.4.5 through 7.4.6 | 7.4.7 or above |
As of April 6, Fortinet has provided a hotfix for FortiClient EMS 7.4.5 and 7.4.6 to address this vulnerability. Version 7.4.7 has not yet been released, but will be an upcoming release that addresses this vulnerability. Until that release, the hotfix must be applied to be protected against this vulnerability. We recommend reviewing the security advisory as Fortinet may make future updates to the document.
A list of Tenable plugins for this vulnerability can be found on the individual CVE page for CVE-2026-35616 as they’re released. This link will display all available plugins for this vulnerability, including upcoming plugins in our Plugins Pipeline.
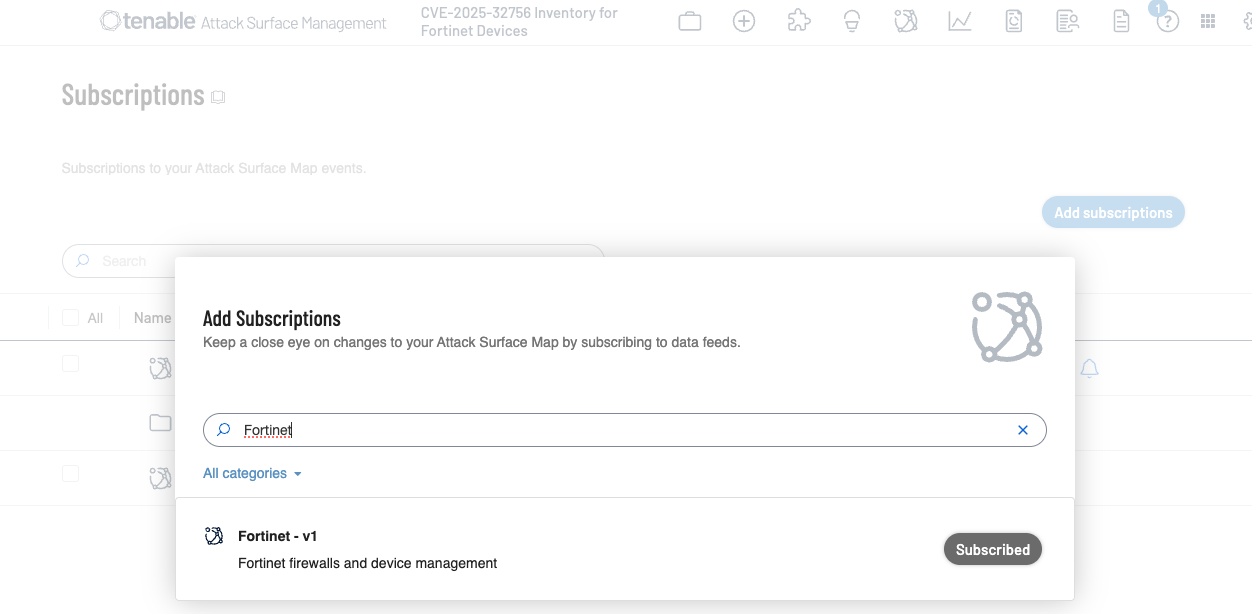
Additionally, customers can utilize Tenable Attack Surface Management to identify public facing assets running Fortinet devices by using the following subscription:
Join Tenable's Research Special Operations (RSO) Team on the Tenable Community.
Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.
Scott joined Tenable in 2012 as a Research Engineer on the Nessus Plugins team. Over the years, he has written hundreds of plugins for Nessus, and reviewed code for even more from his time being a team lead and manager of the Plugins team. Previously leading the Security Response team and the Zero Day Research team, Scott is currently a member of the Research Special Operations team, helping the research organization respond to the latest threats. He has over a decade of experience in the industry with previous work in the Security Operations Center (SOC) for a major domain registrar and web hosting provider. Scott is a current CISSP and actively maintains his GIAC GWAPT Web Application Penetration Tester certification.
Interests outside of work: Scott enjoys spending time with his family, camping, fishing and being outdoors. He also enjoys finding ways to break web applications and home renovation projects.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。